
Archived
pe_tree
 blackberry/pe_tree
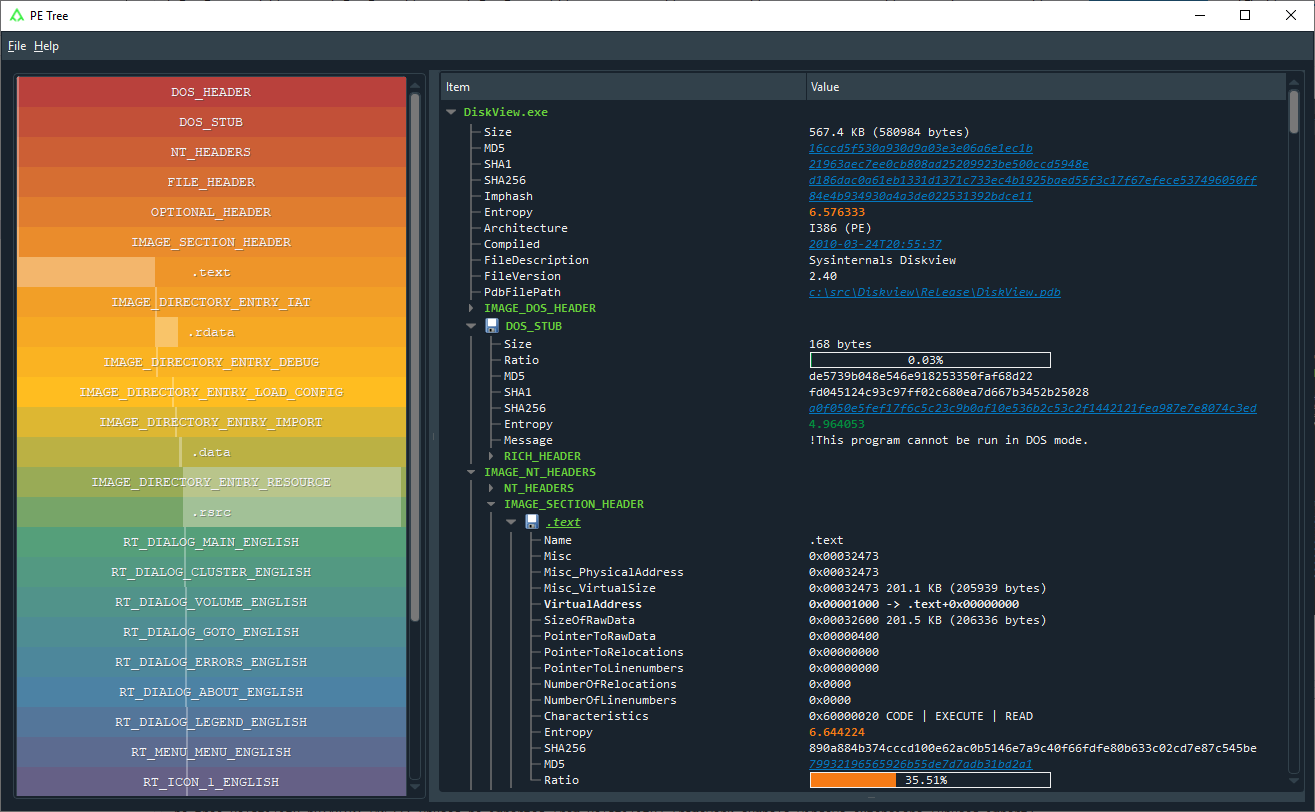
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
binary-analysisdebuggersdigital-forensics+5
blackberry/pe_treePython module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool