
PolyEngine
 longwayhomie/polyengine
PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…
anti-botbinary-analysisctf+6
163
longwayhomie/polyenginePolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…
 mr-un1k0d3r/maliciousmacrogenerator
Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.
 dsnezhkov/elfpack
ELF binary section docking toolkit for stageless payload delivery, enabling in-field payload attachment, signature evasion, and static/dynamic…
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 aaaddress1/pr0cess
some gadgets about windows process and ready to use :)
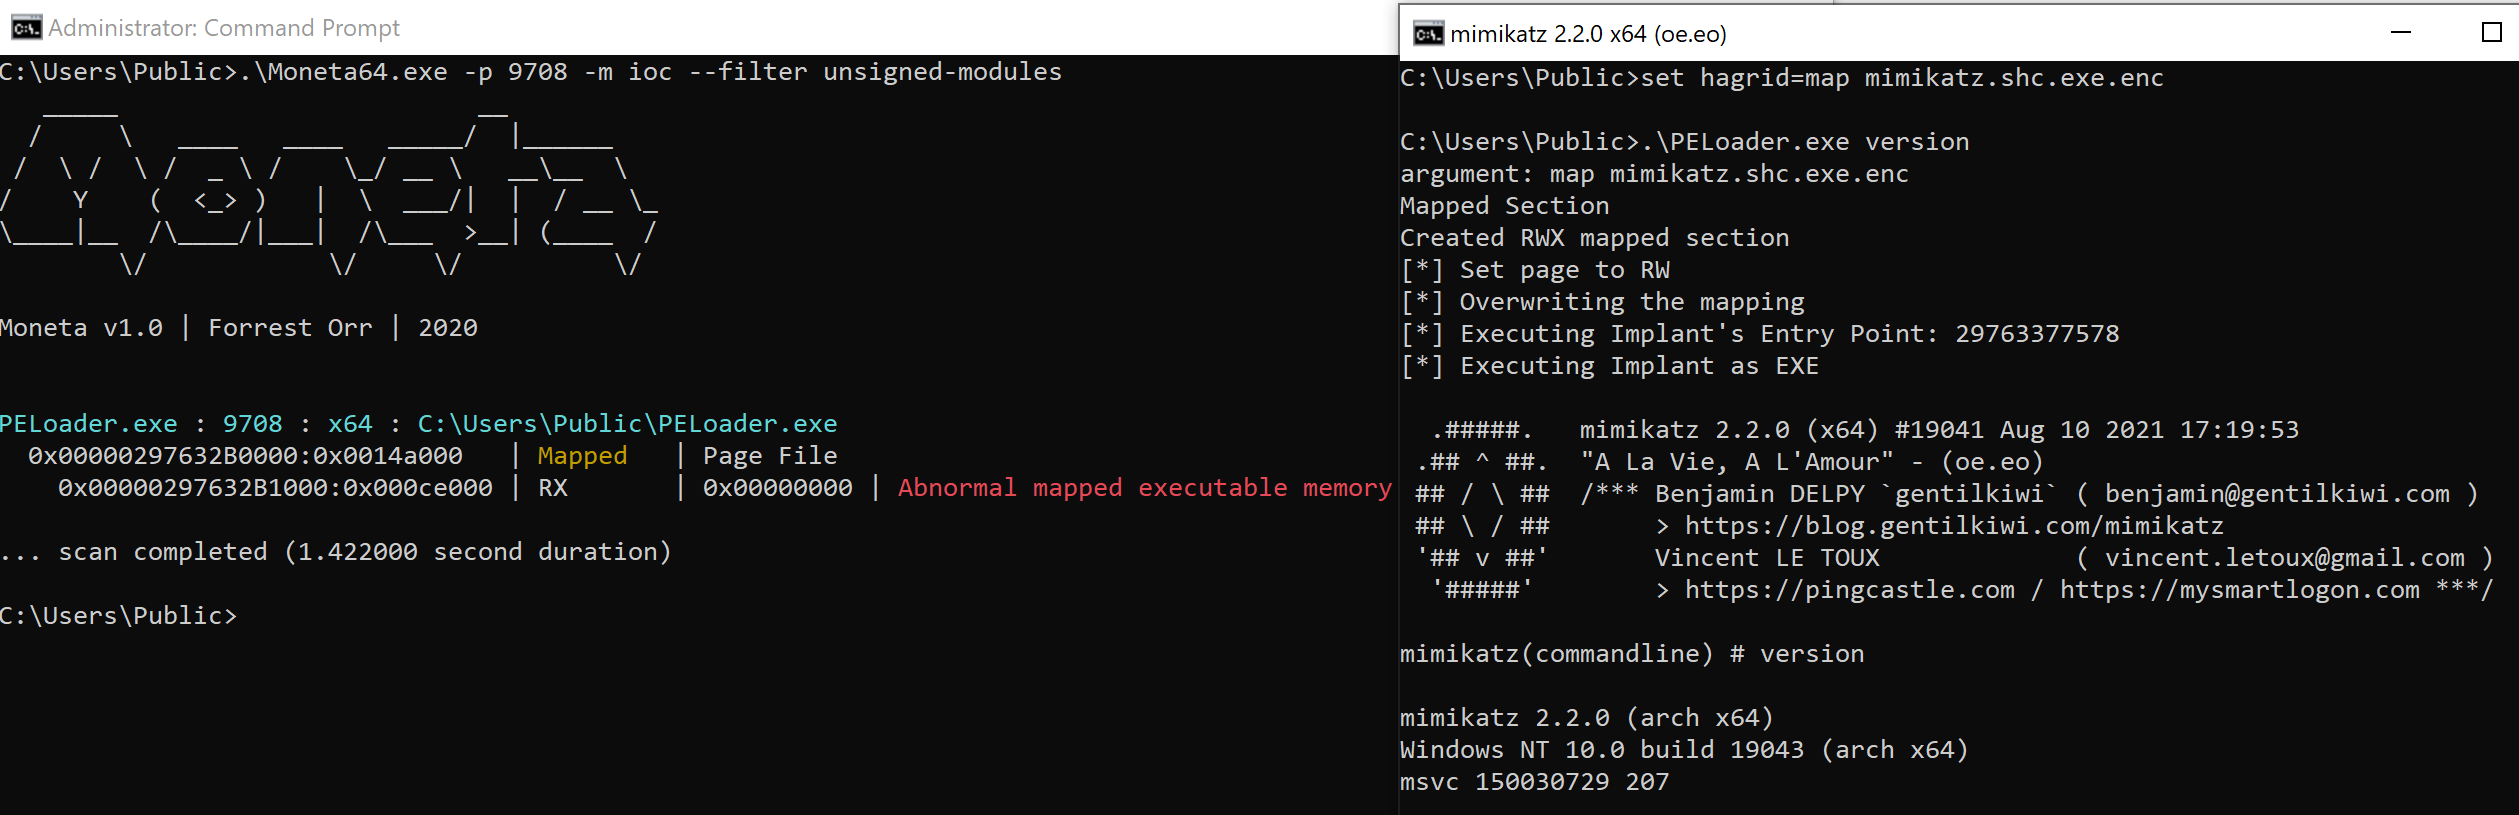 hagrid29/peloader
PE loader with various shellcode injection techniques
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 d4vinci/palsy-virus
Python virus that will make your pc paralyzed once it opened :D
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.