
YARA_Rules
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
curated-resourcesdefensive-toolsincident-response+3
65
malgamy/yara_rulesCurated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
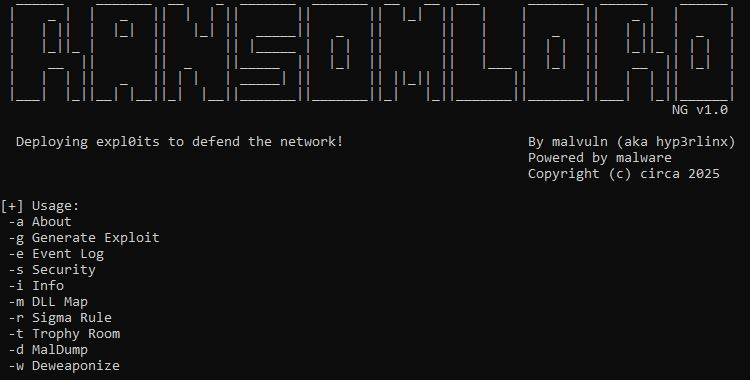 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
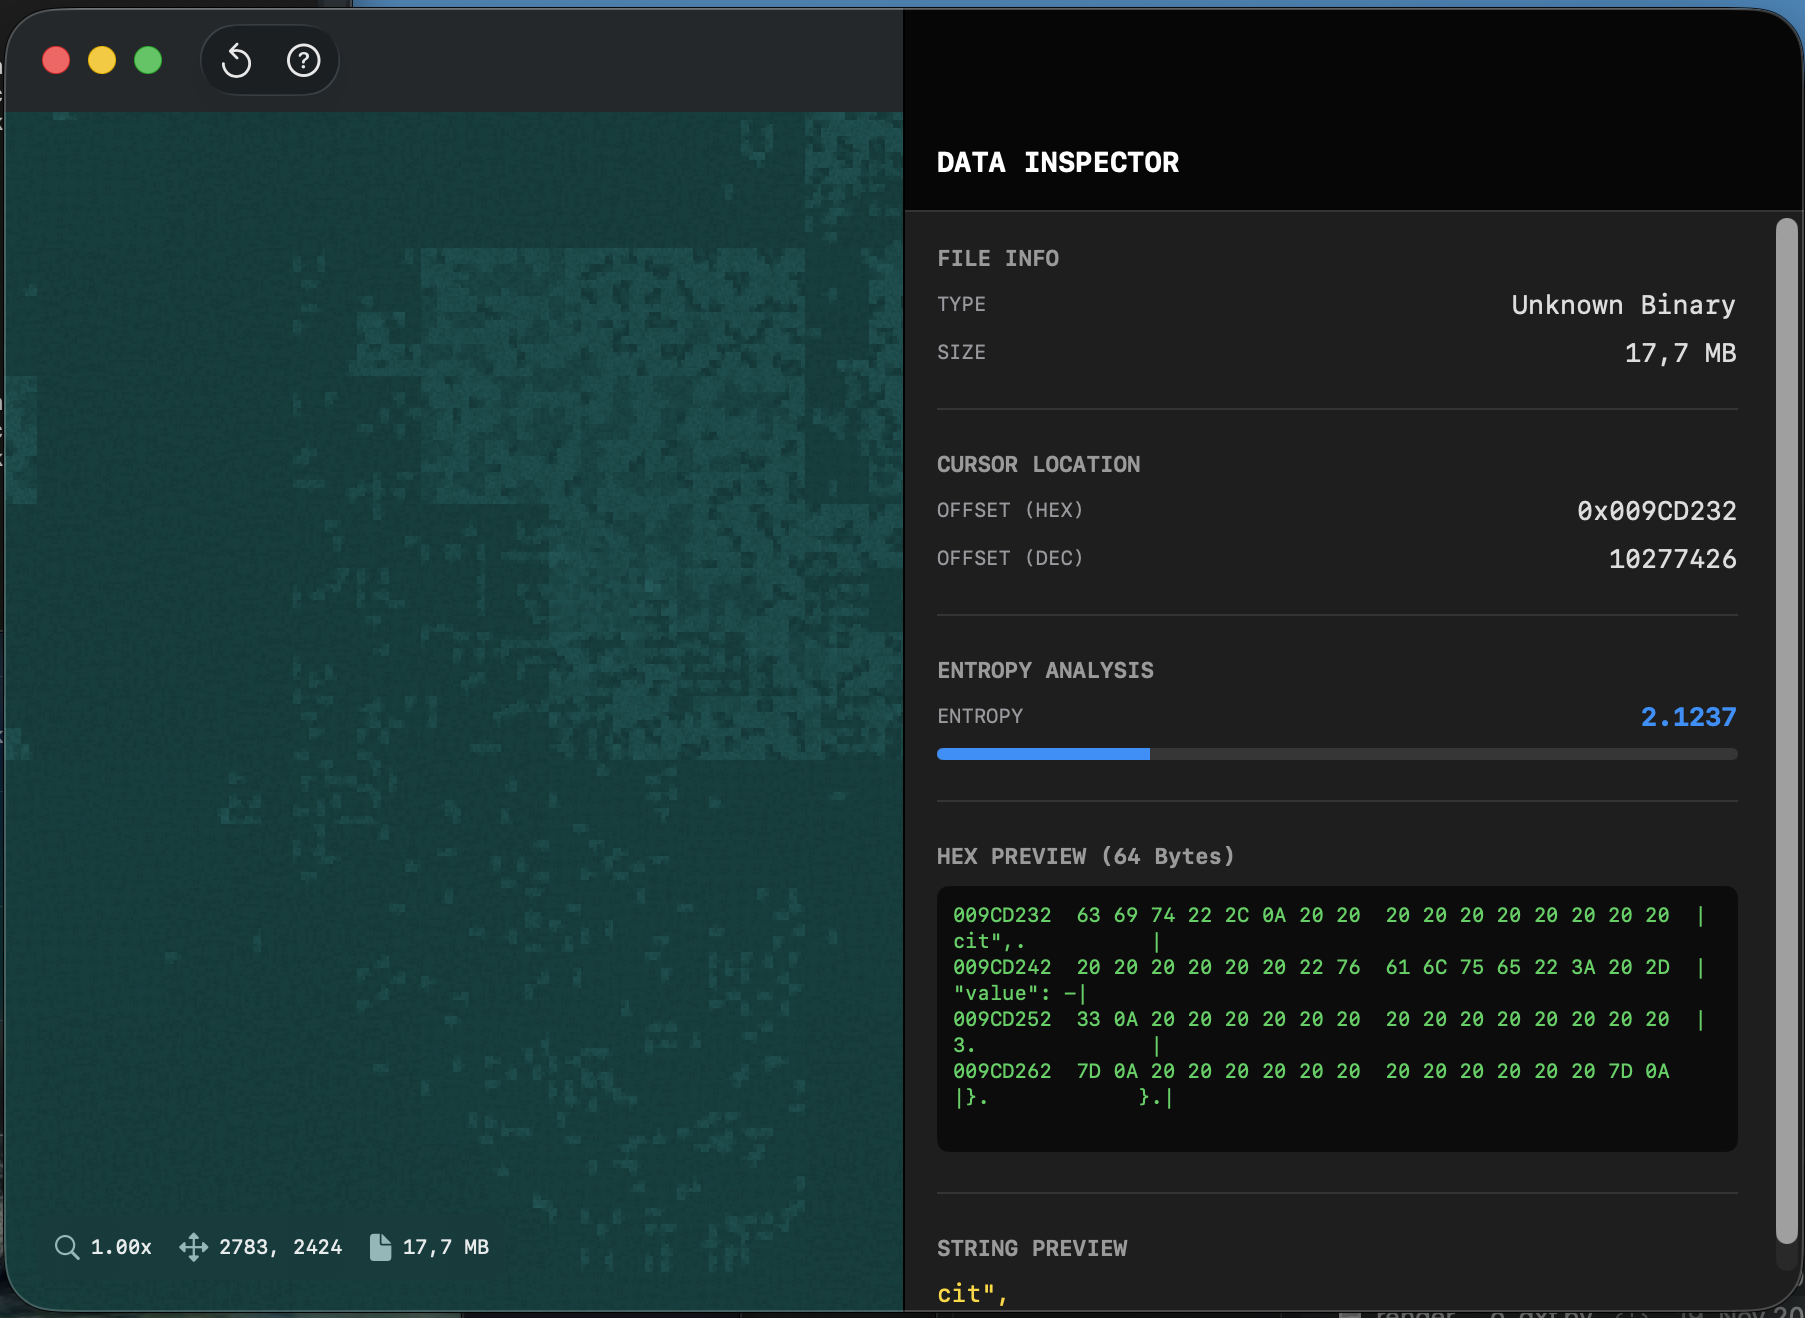 farukalpay/neurocore
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 airbus-cert/cve-2025-24985
Detection of malicious VHD files for CVE-2025-24985
 mikesxrs/cve-2023-21716_yara_results
Results of retrohunt for files matching YARA rules from https://github.com/AmgdGocha/Detection-Rules/blob/main/CVE-2023-21716.yar
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness

 tstillz/webshell-analyzer
Web shell scanner and analyzer.
 matank001/asclepius
Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…
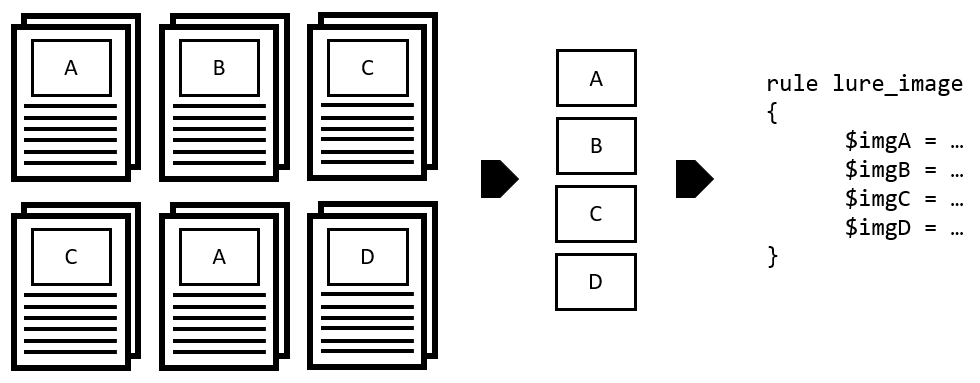 target/halogen
Automatically create YARA rules from malicious documents.
 jfrog/cve-2024-3094-tools
Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…