
aura
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
code-analysiseducationmalware-analysis+4
sourcecode-ai/auraPython source code auditing and static analysis on a large scale
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 indominusrexes/cve-2025-4322-exploit
Critical CVE-2025-4322 exploit for Firefox on Windows enabling sandbox escape and arbitrary code execution. Includes download link and technical…
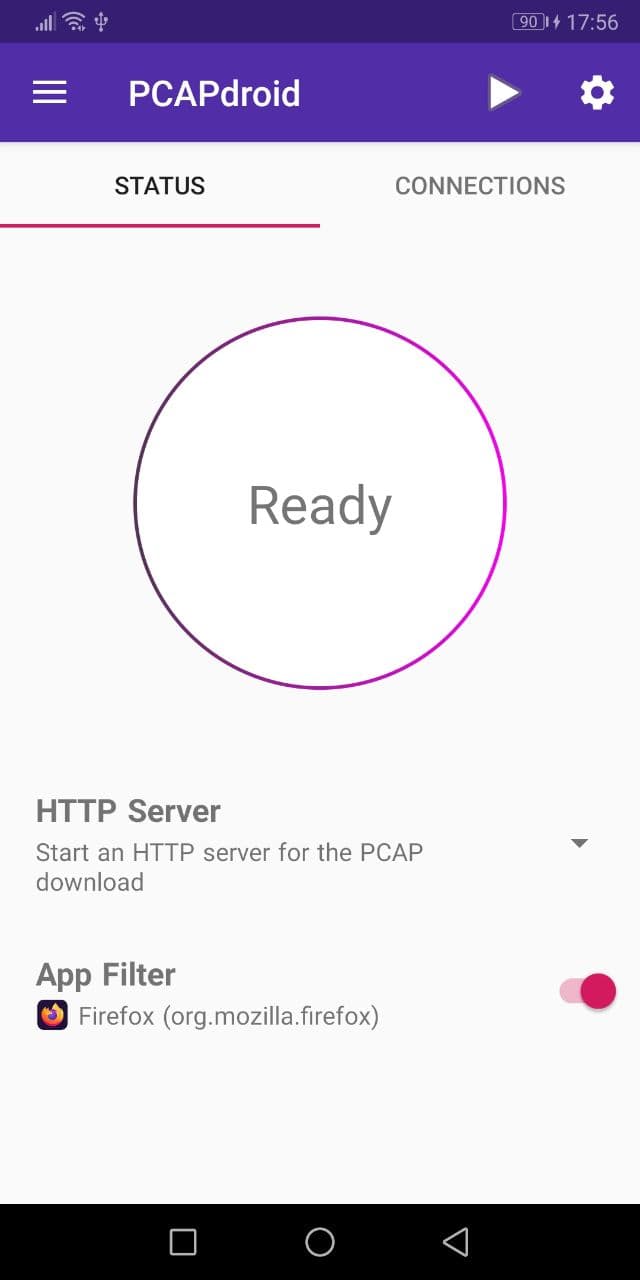 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 theatha/yara_for_config_extraction
Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…
 outflanknl/evilclippy
A cross-platform assistant for creating malicious MS Office documents. Can hide VBA macros, stomp VBA code (via P-Code) and confuse macro analysis…
 basim-ahmad/follina-cve-and-cve-2021-40444
This repository contains scripts and resources for exploiting the Follina CVE and CVE-2021-40444 vulnerabilities in Microsoft Office. The scripts…
 huntandhackett/concealed_code_execution
Tools and technical write-ups describing attacking techniques that rely on concealing code execution on Windows
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
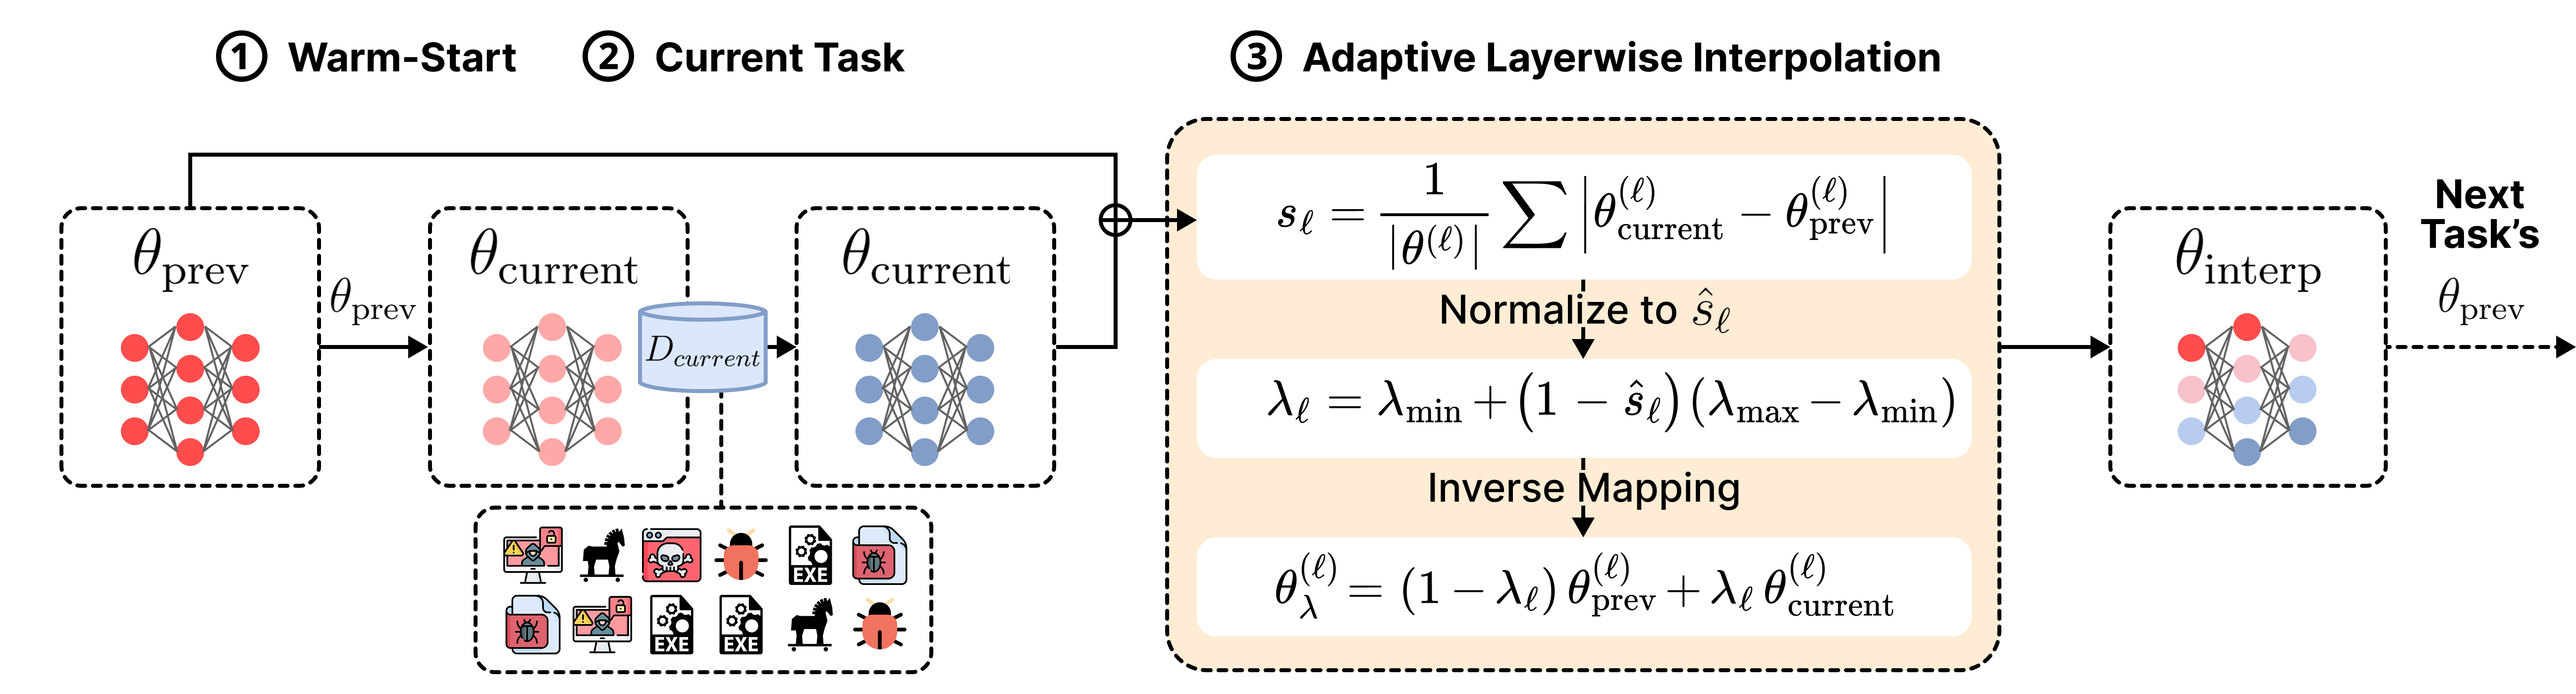 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
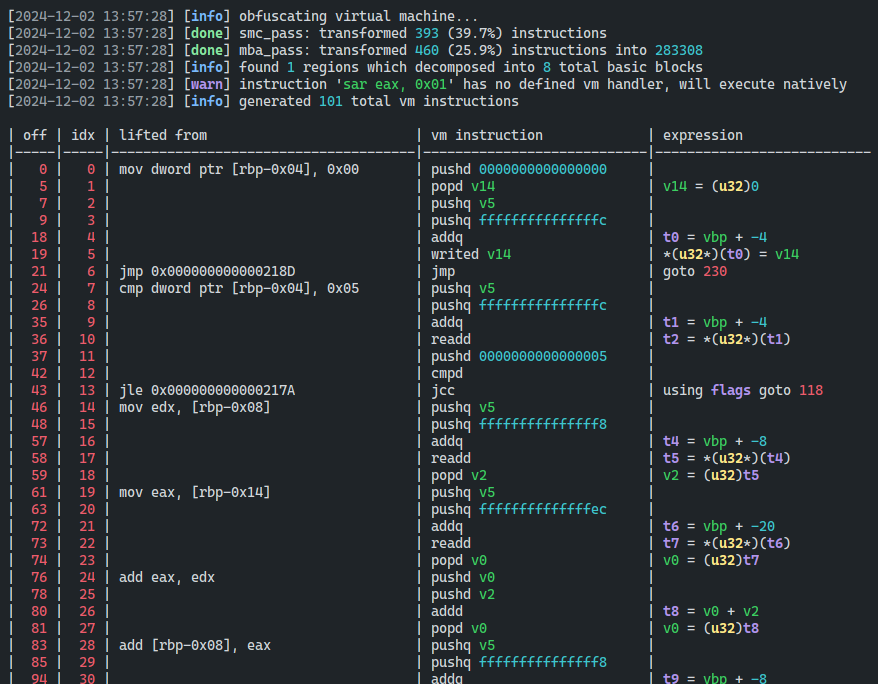 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
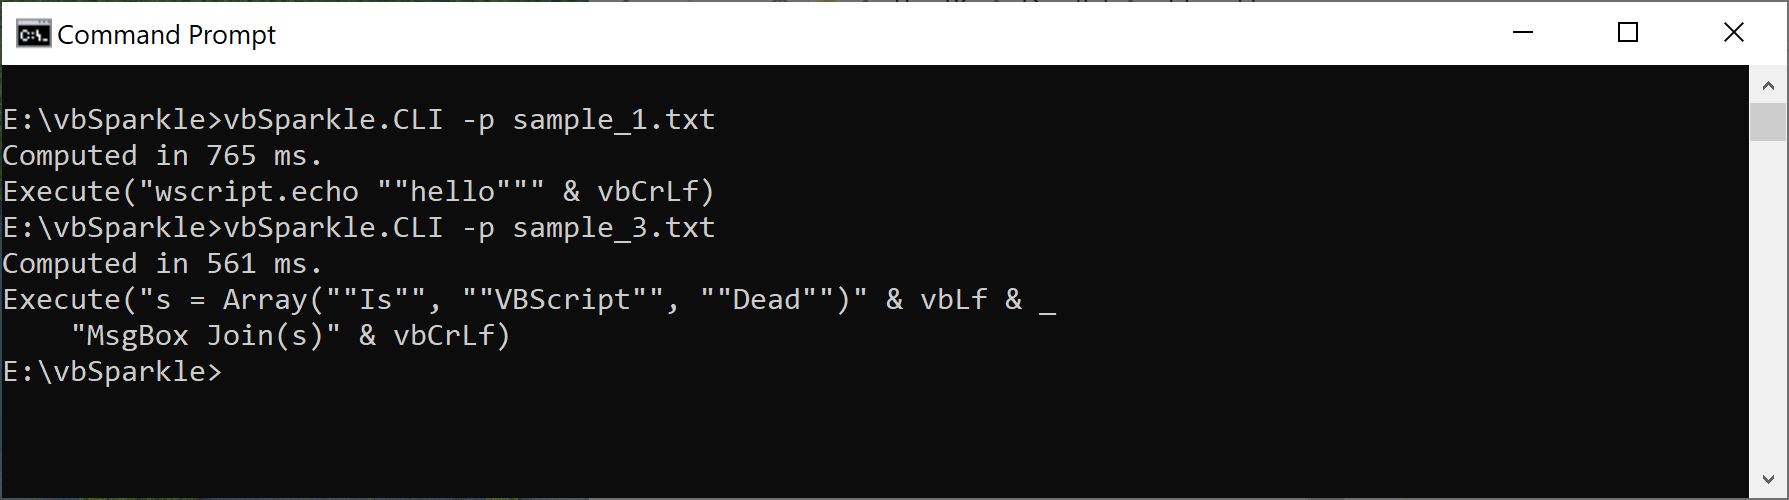 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 olowostandard1/cve-2023-38831-winrar-vulnerability-analysis
This project is a cybersecurity research and analysis project focused on CVE-2023-38831, a critical WinRAR vulnerability that allows attackers to…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…