

ReverseKit
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
binary-analysisdynamic-code-analysismalware-analysis+1
7923 years ago
zer0condition/reversekitx64 Dynamic Reverse Engineering Toolkit
 aetsu/neton
Agent-based tool that collects OS, hardware, file, and hook data from internet-connected sandboxes via HTTPS exfiltration, aiding Red Team artifact…
 renewablehacking/cve-2026-45321-tanstack
Educational lab simulating npm supply chain attacks, CI/CD abuse, and install-time code execution via CVE-2026-45321. Hands-on defensive security…
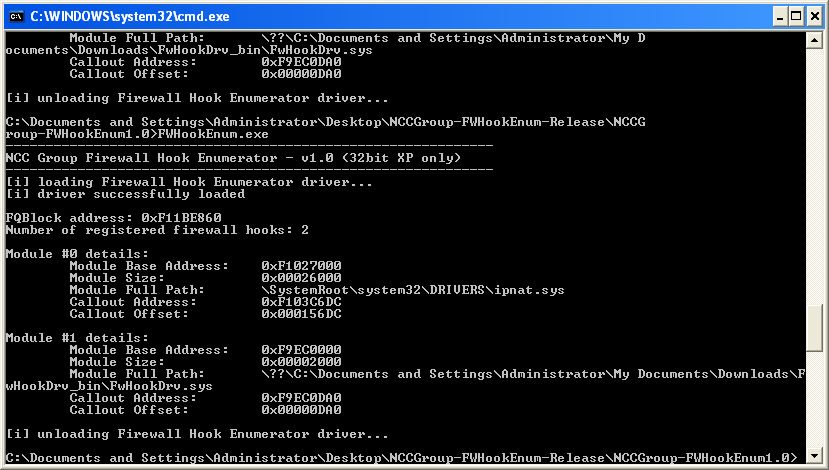 nccgroup/windowsfirewallhookdriverenumeration
Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 mandiant/strace
A DTrace on Windows Reimplementation
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 vignesh21-git/cve-2025-48384-submodule
Test