Get-PDInvokeImports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…

PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.

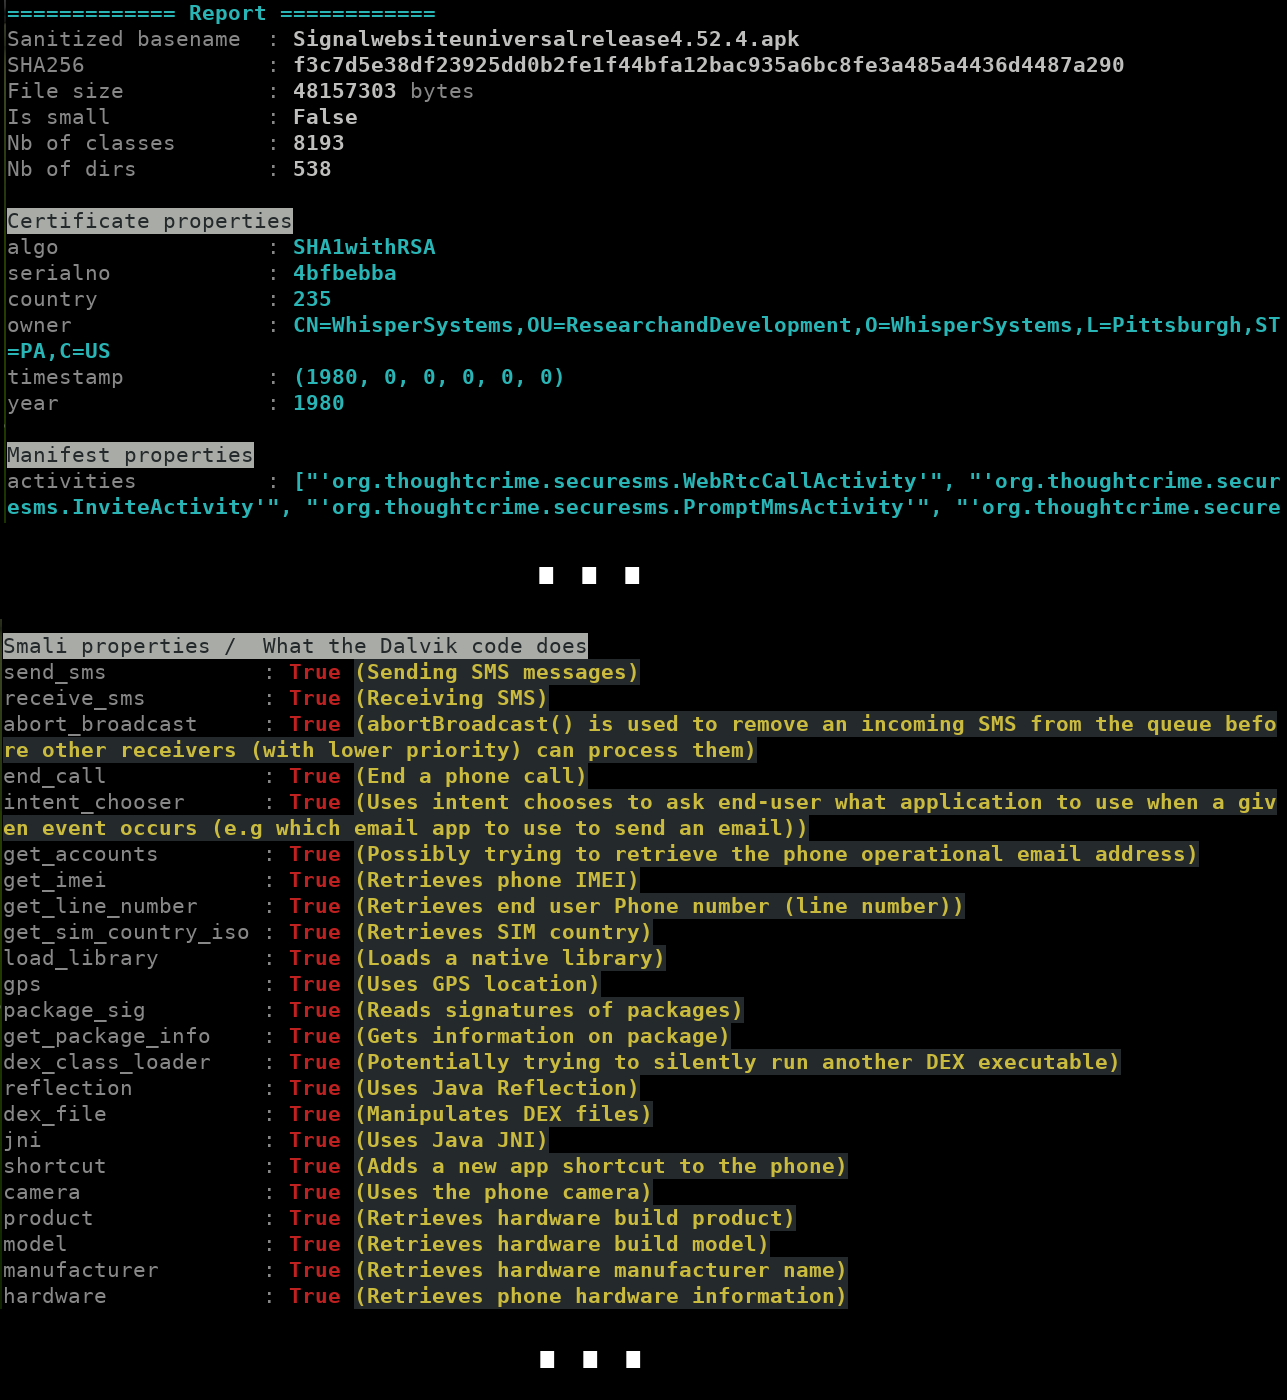
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…

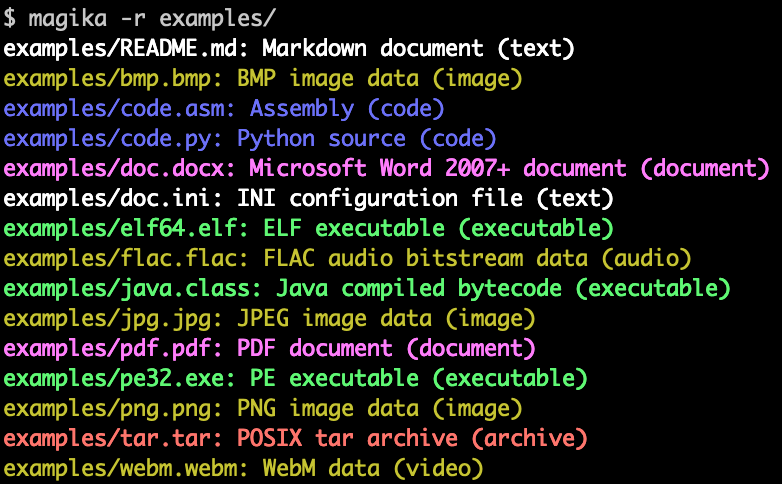
Fast and accurate AI powered file content types detection

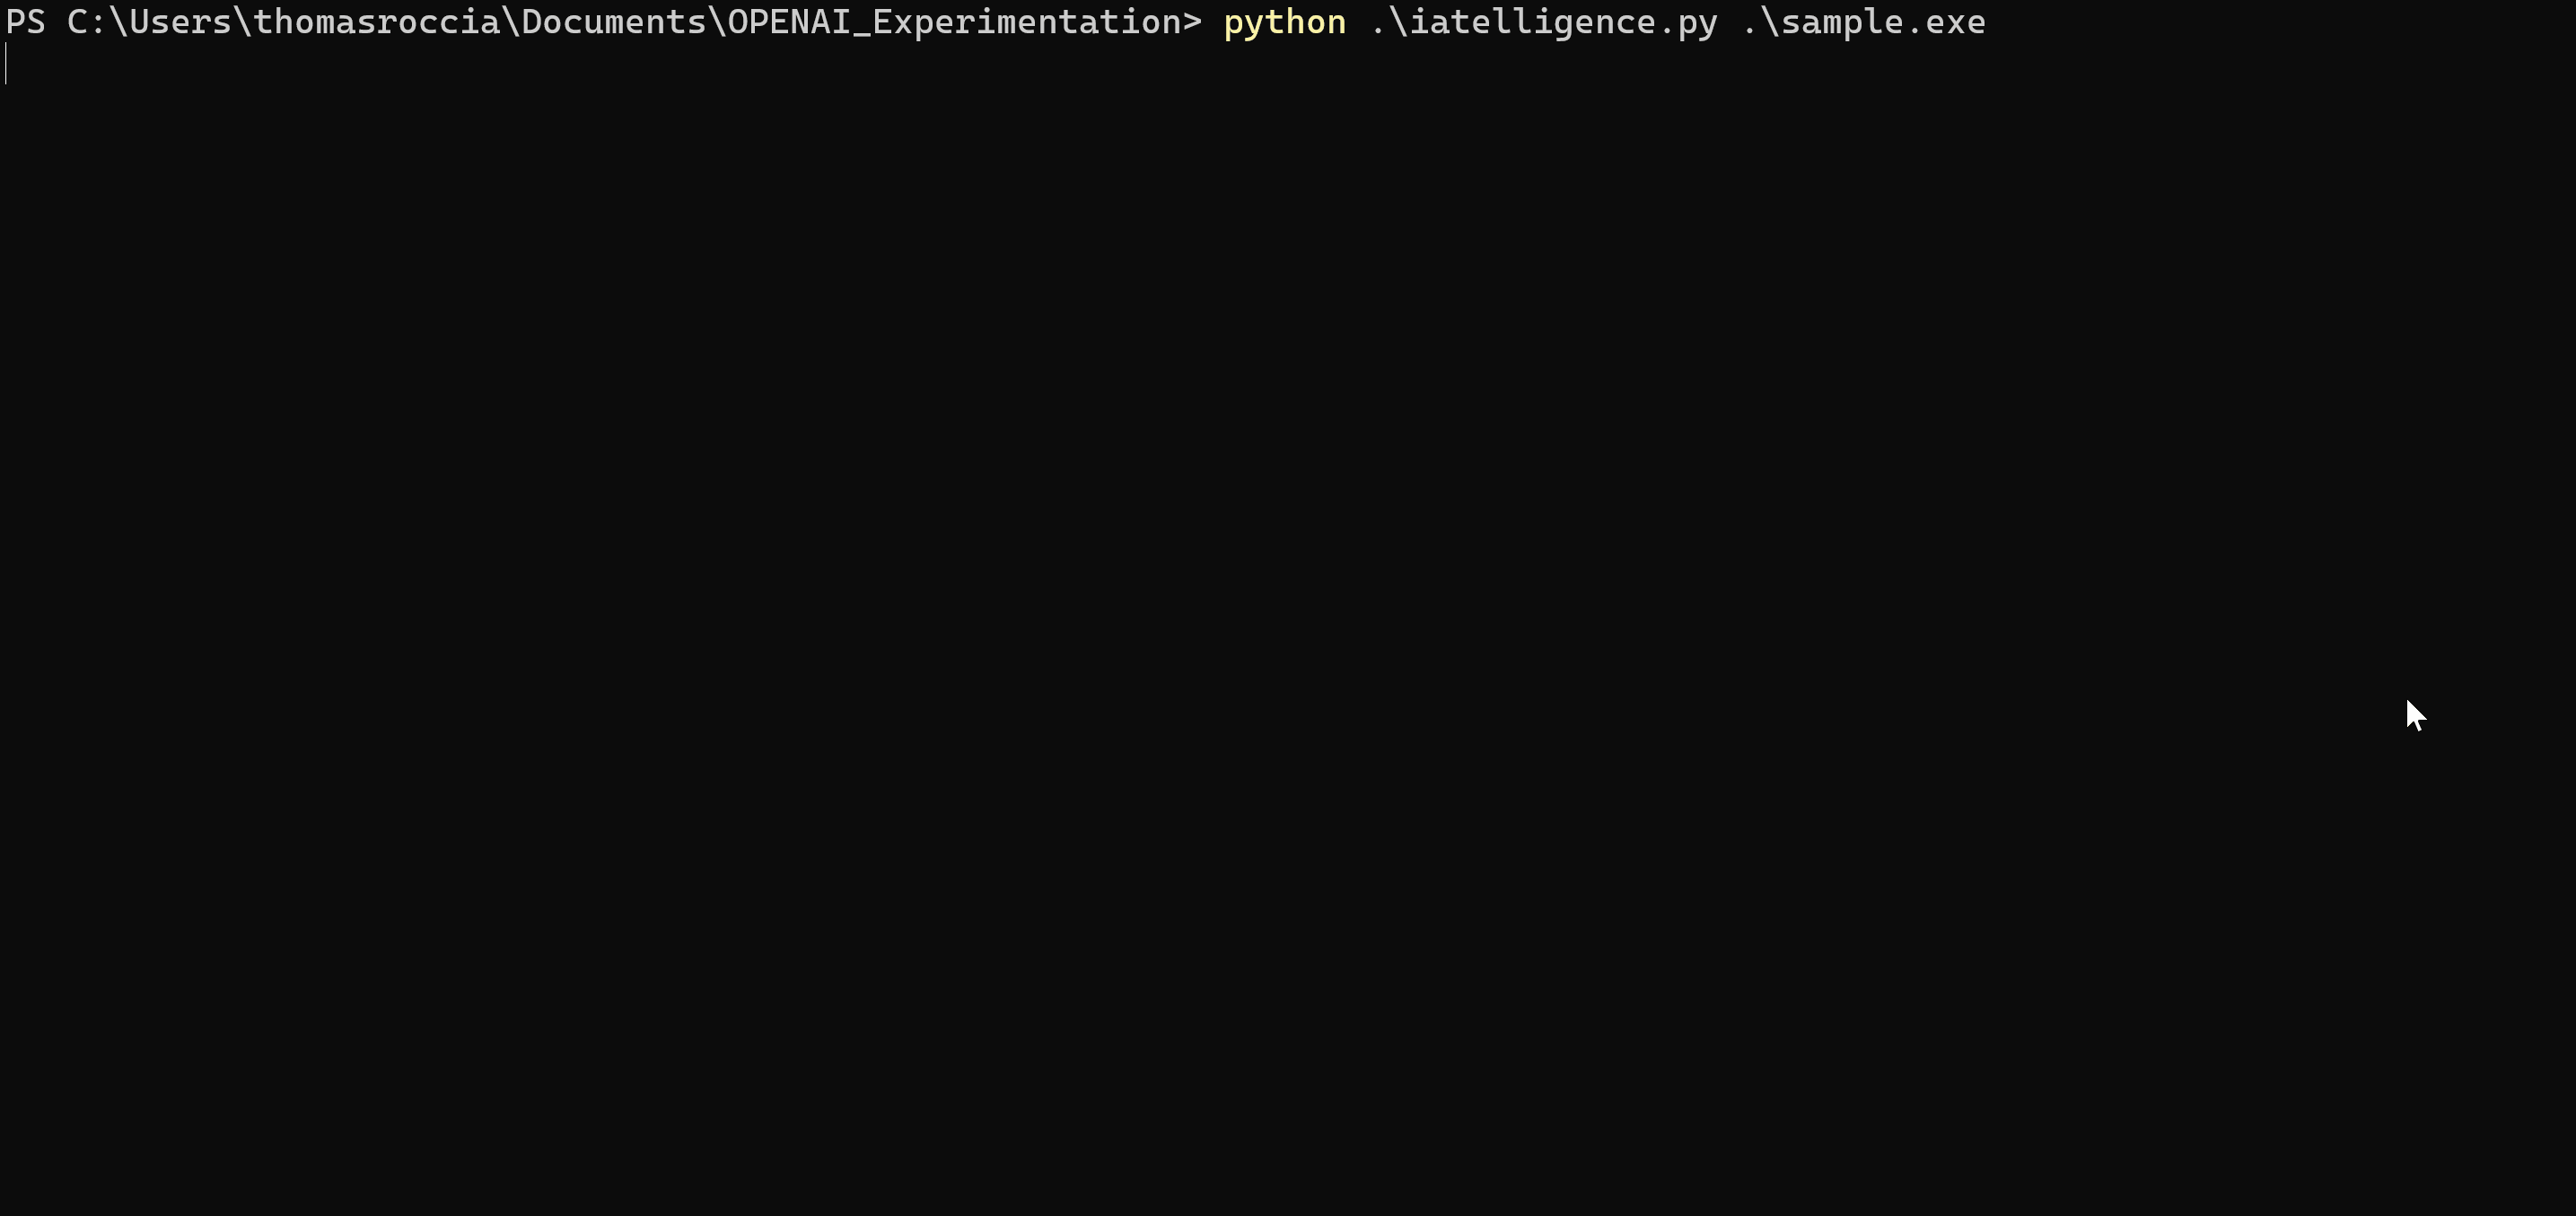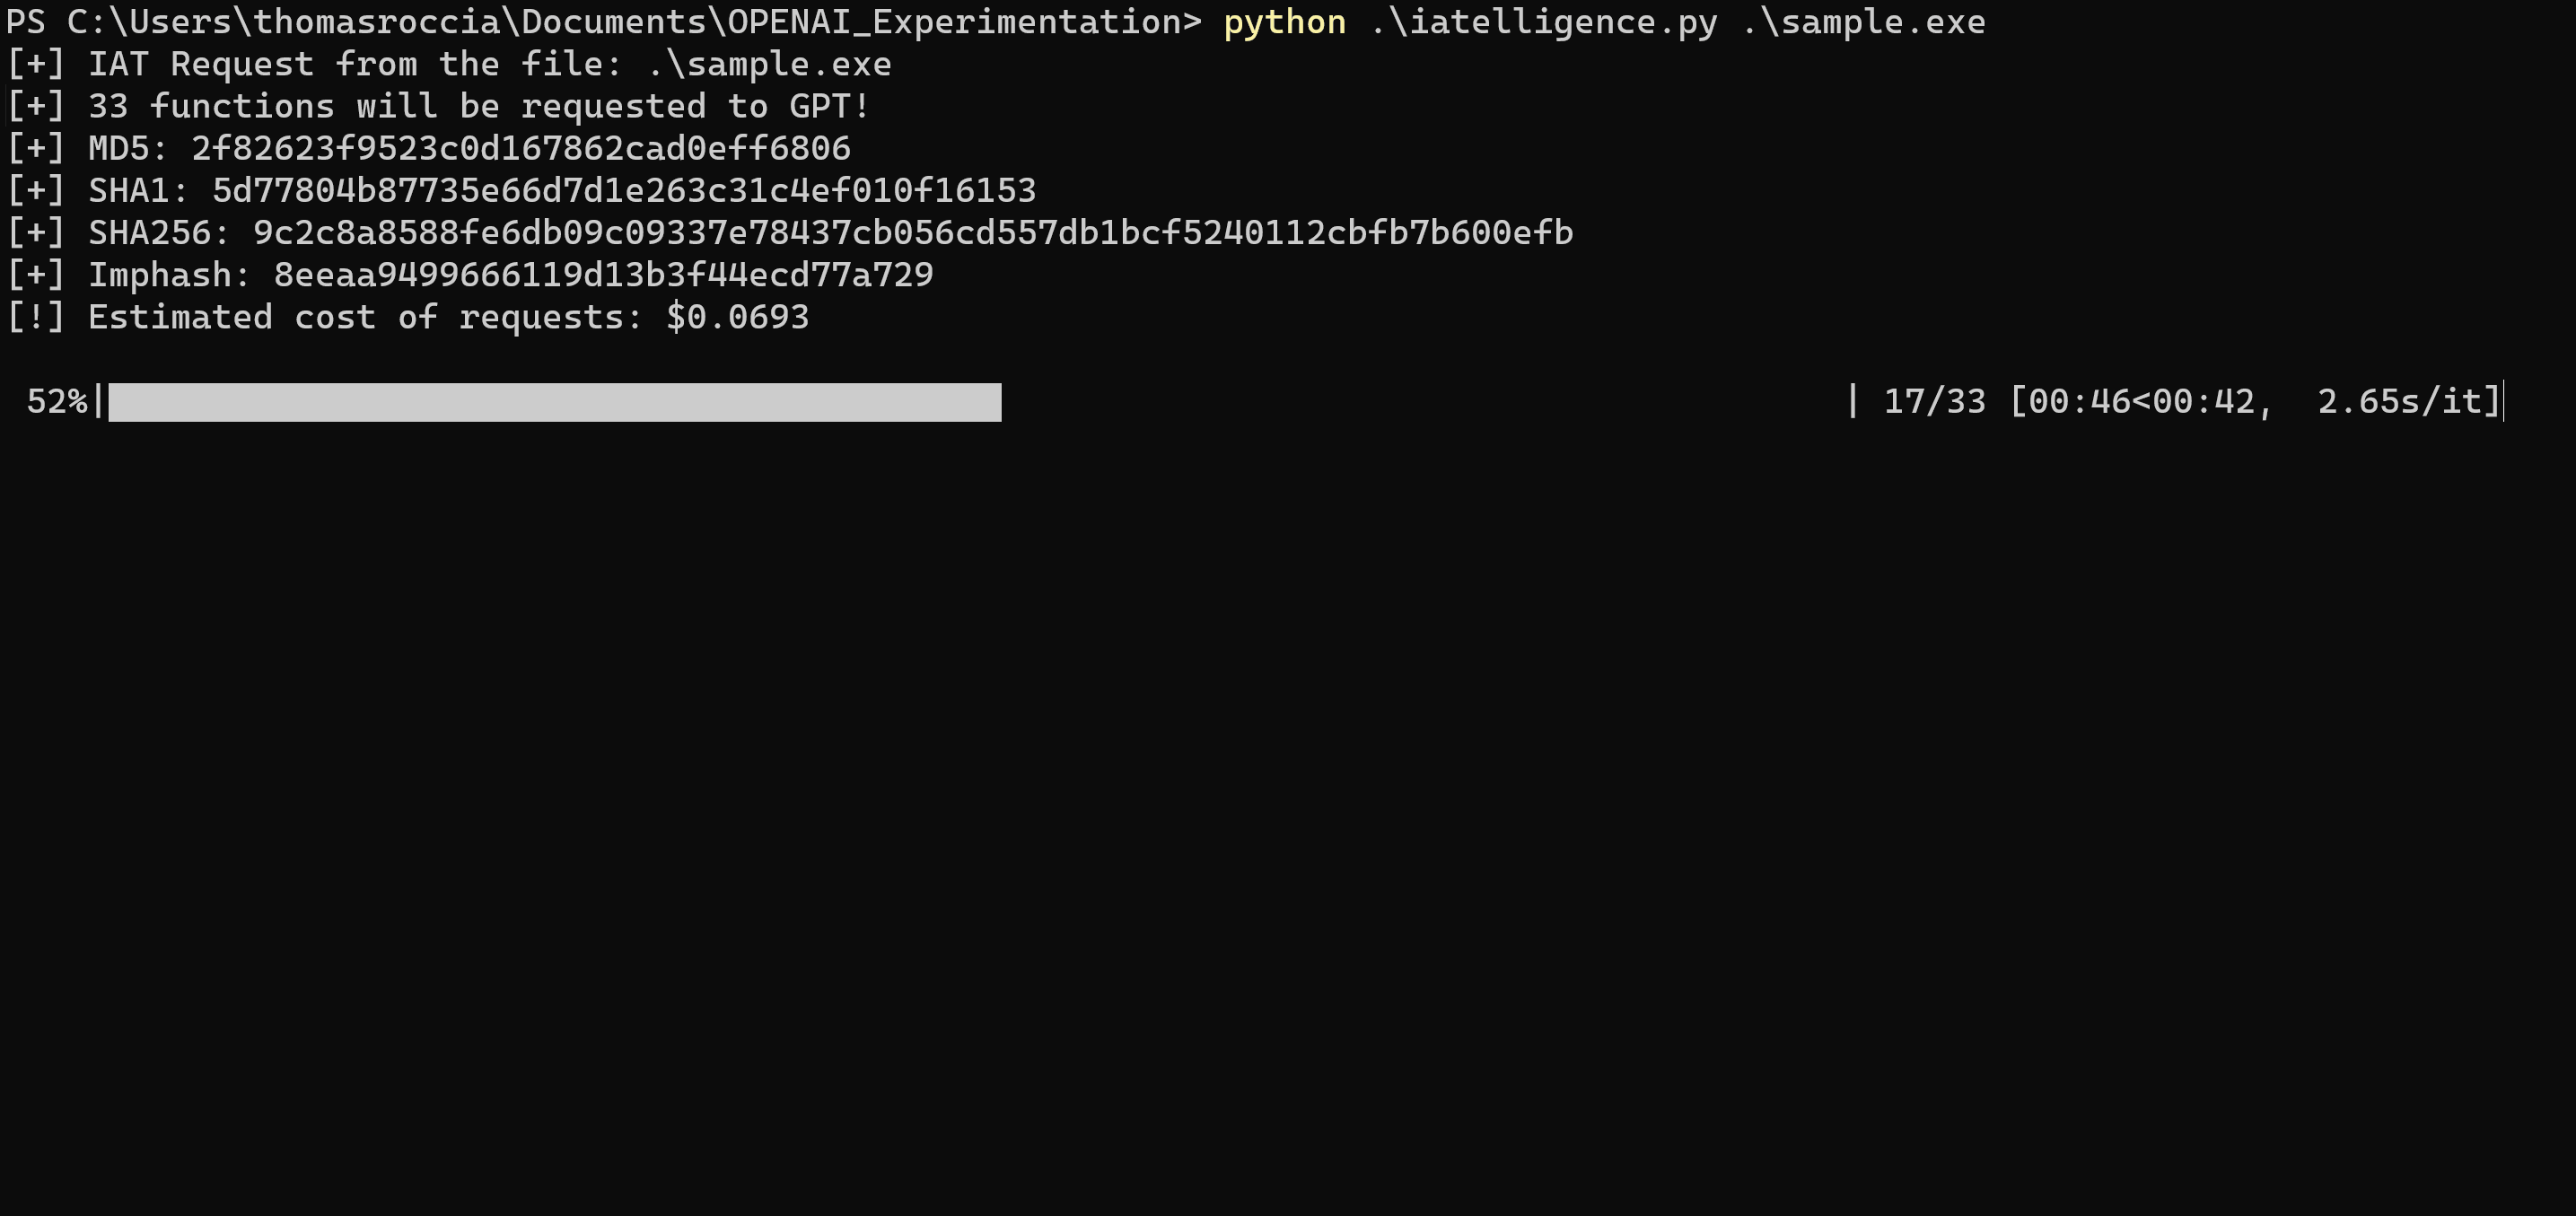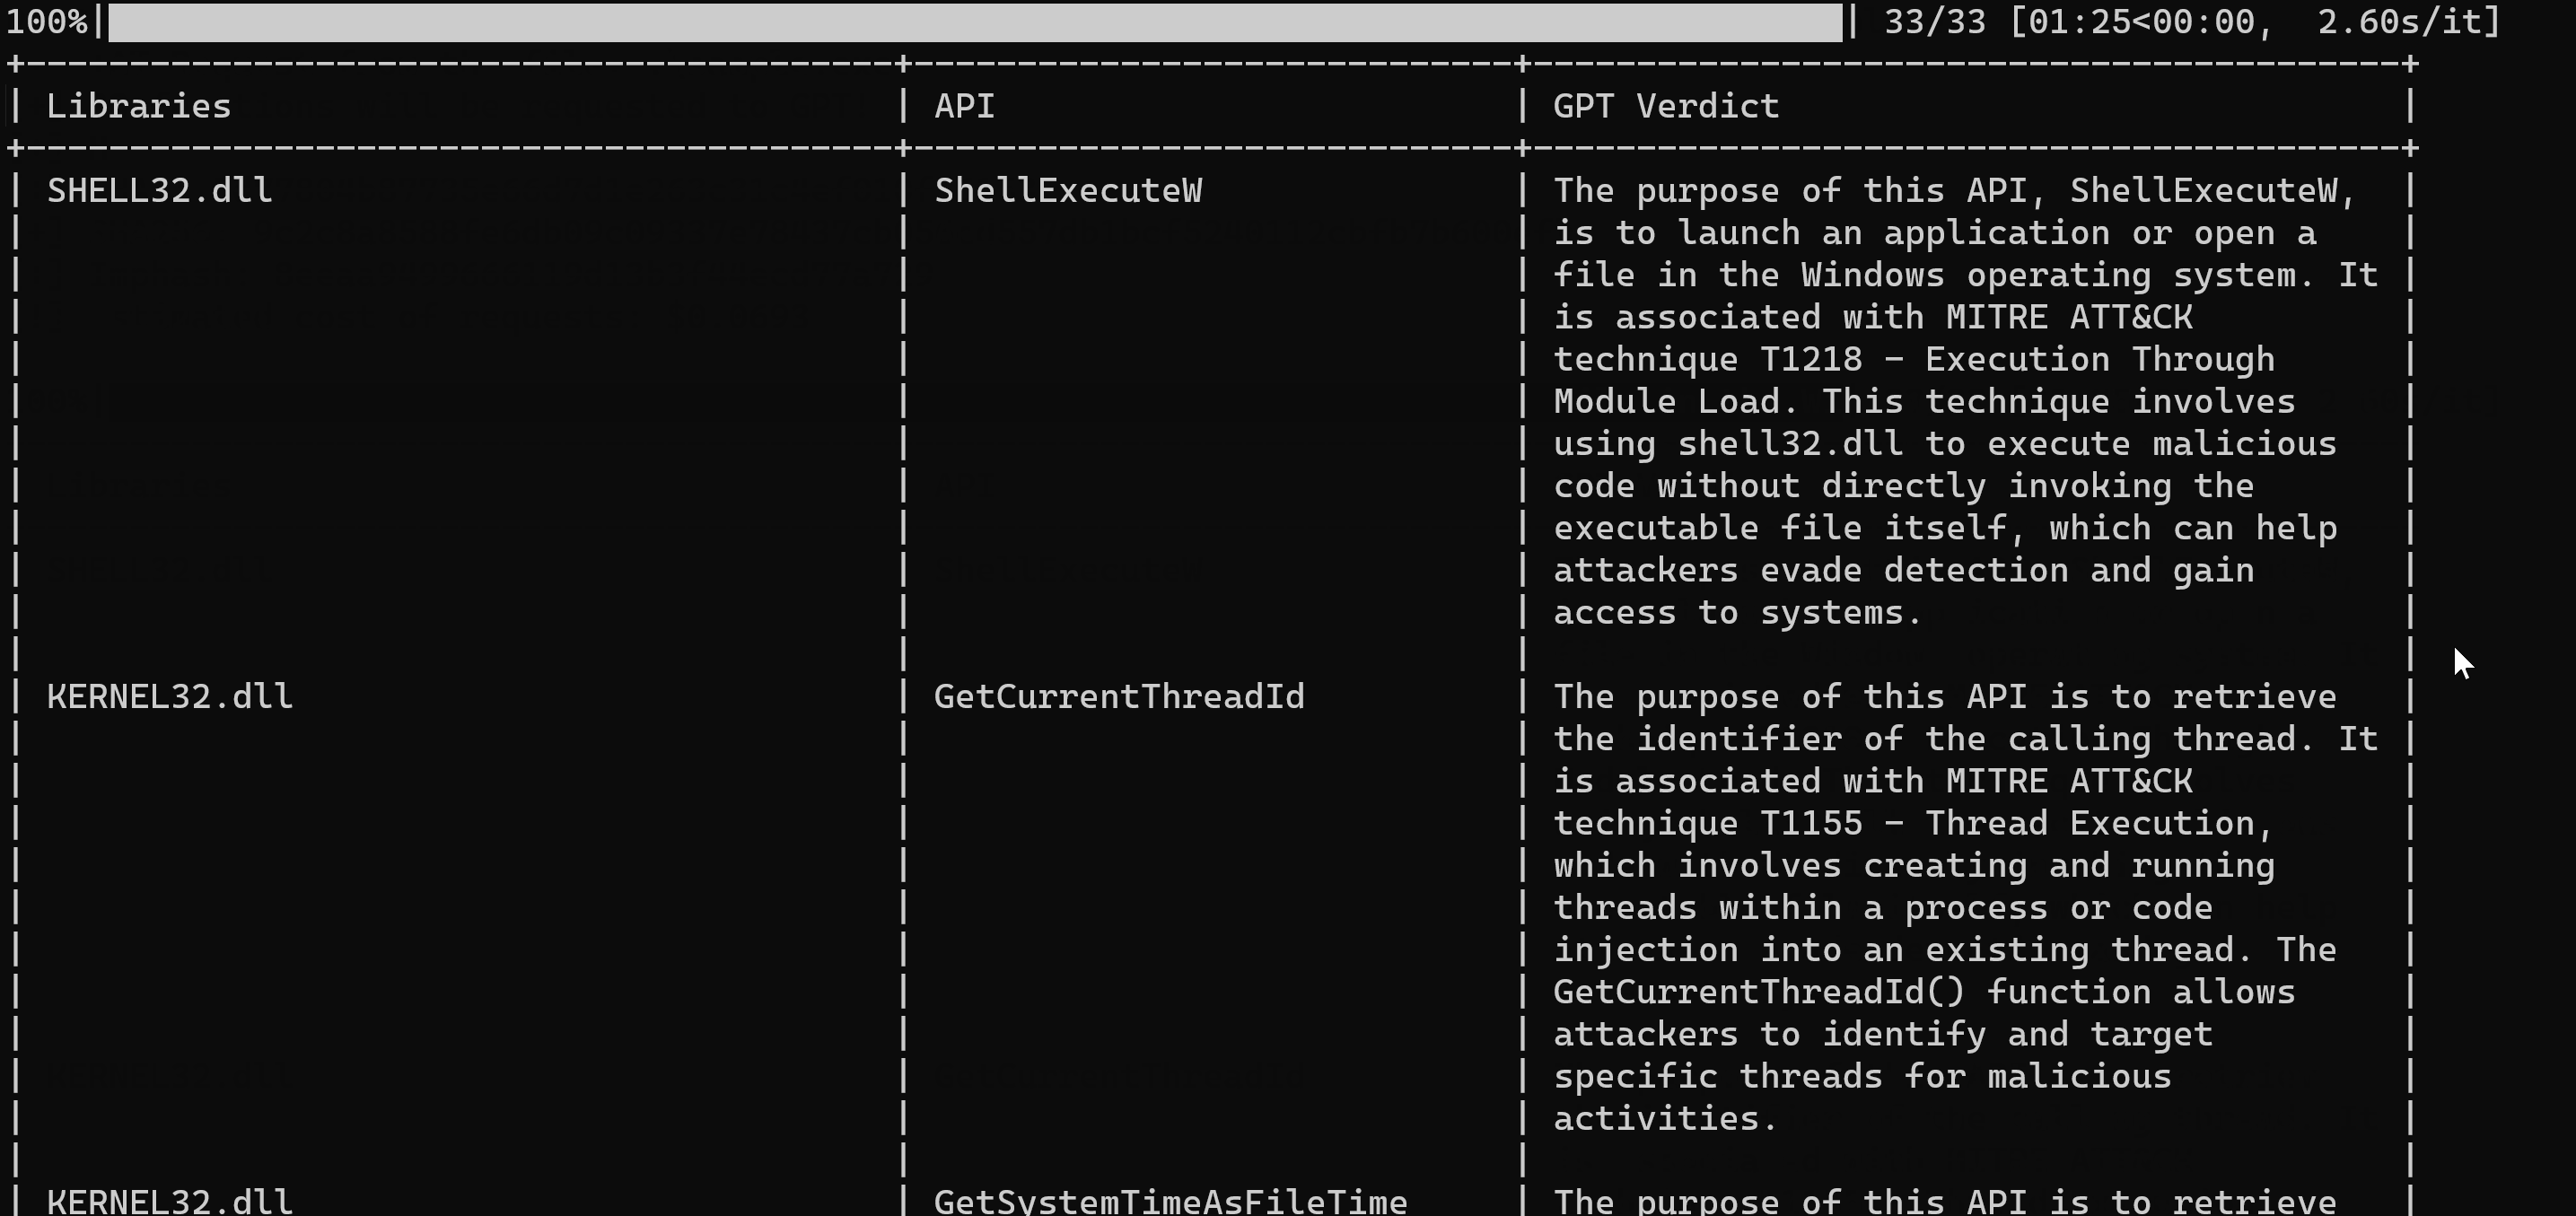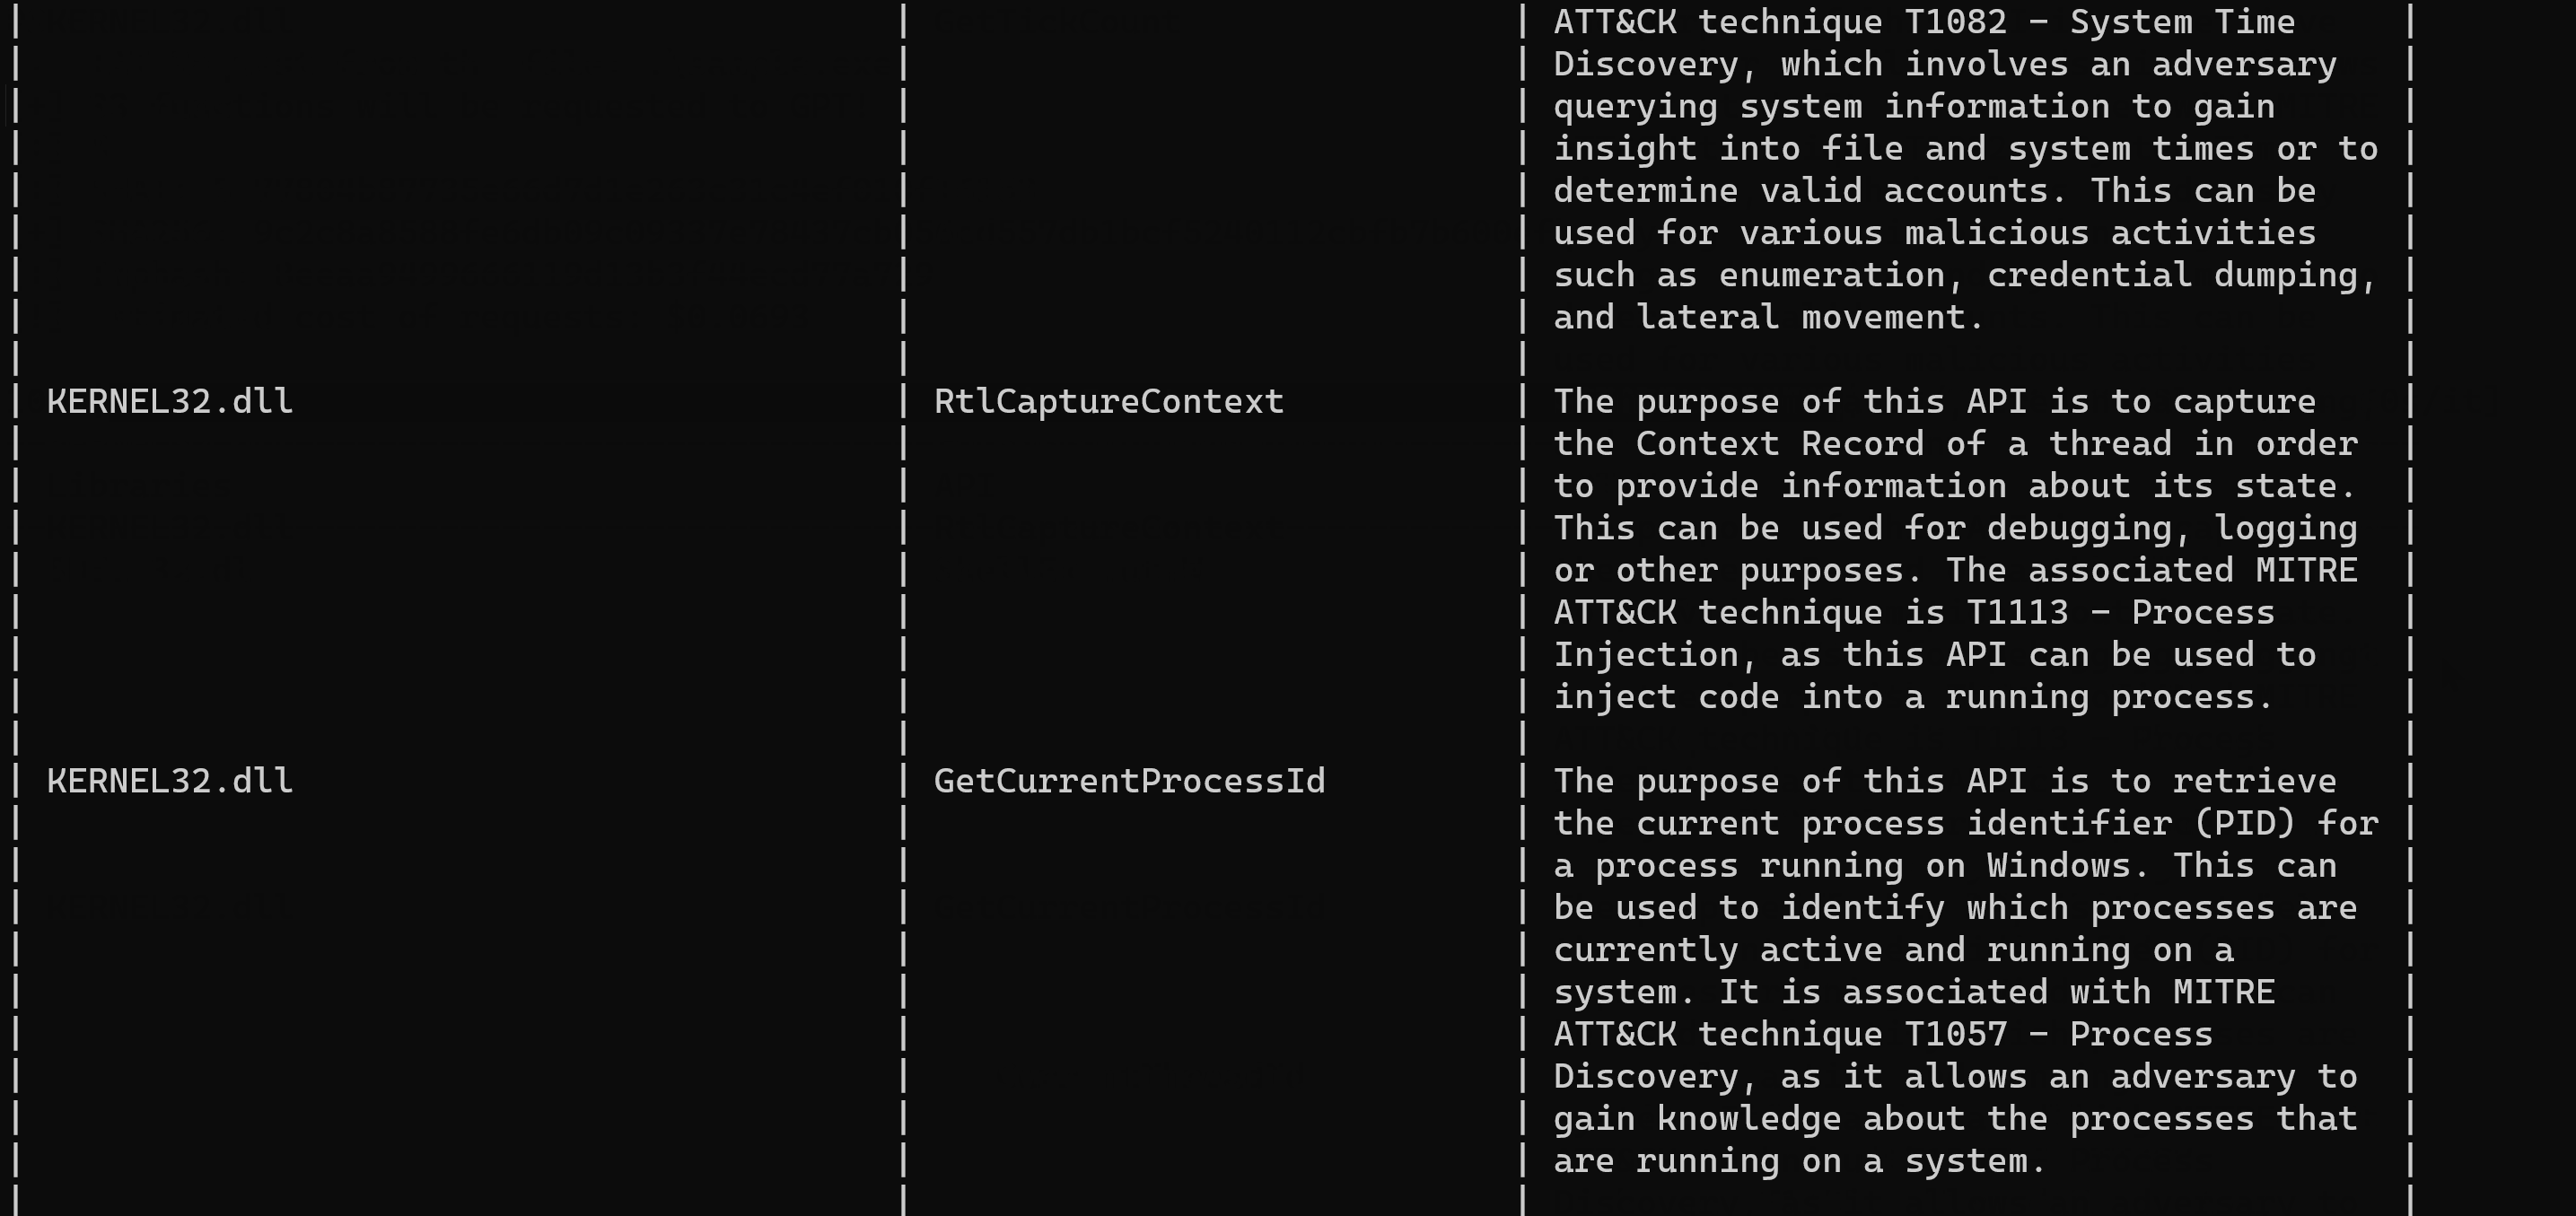
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…

Different methods to get current username without using whoami

Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…

Modular malware analysis artifact collection and correlation framework

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

Linux Distro for Mobile Security, Malware Analysis, and Forensics

Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.

You didn't think I'd go and leave the blue team out, right?

Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.

A technique of hiding malicious shellcode via Shannon encoding.

Auto Installer Script for Cuckoo Sandbox

This is working POC of CVE-2022-36271

Security sensor for realtime threat detection and protection