
gftrace
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
leandrofroes/gftraceA command line Windows API tracing tool for Golang binaries.
 tylabs/qs_old
Command line tool for scanning streams within office documents plus xor db attack
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
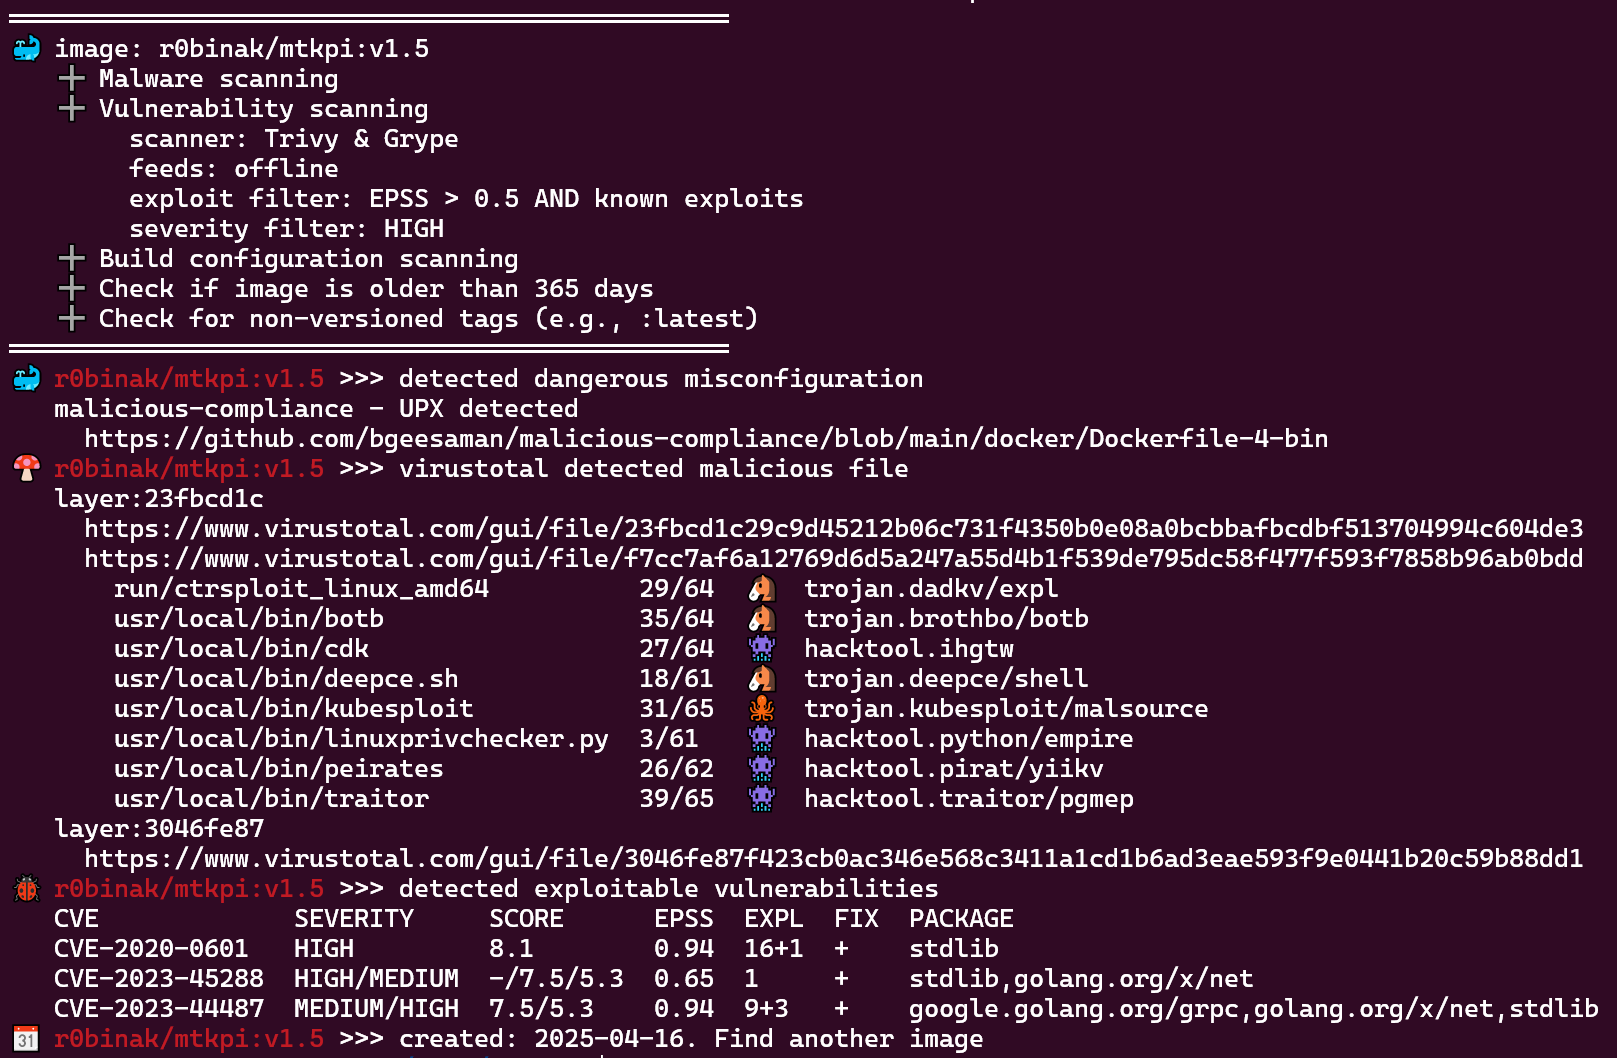 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
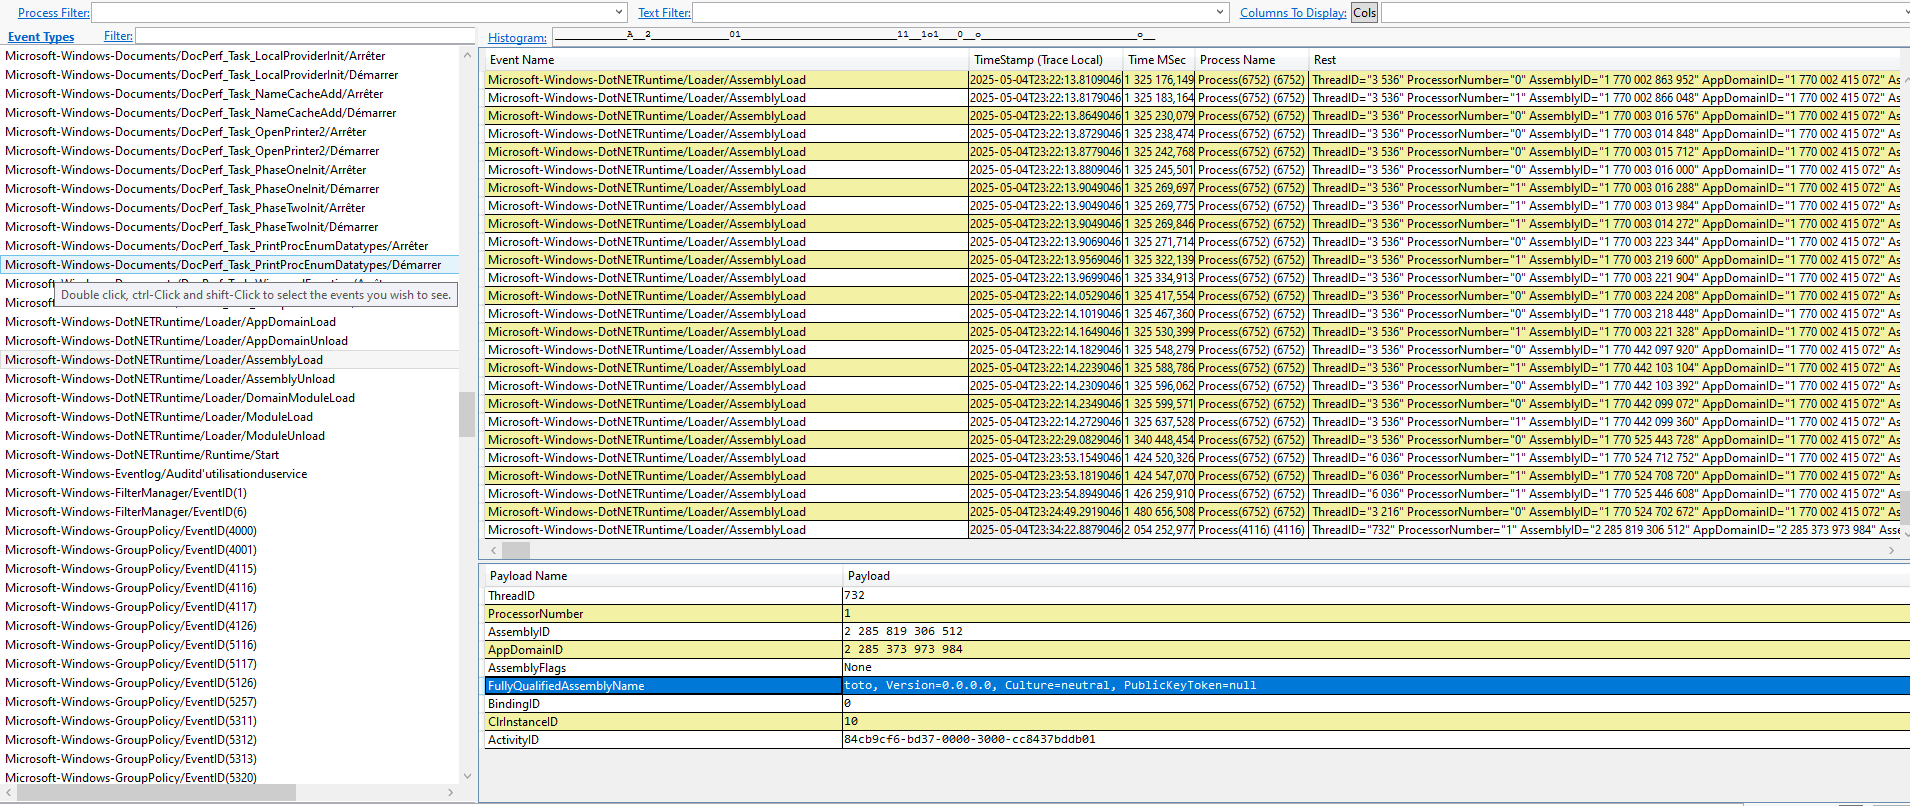 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework