
maldrolyzer
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
android-securitycommand-and-controlinformation-gathering+3
114
maldroid/maldrolyzerSimple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
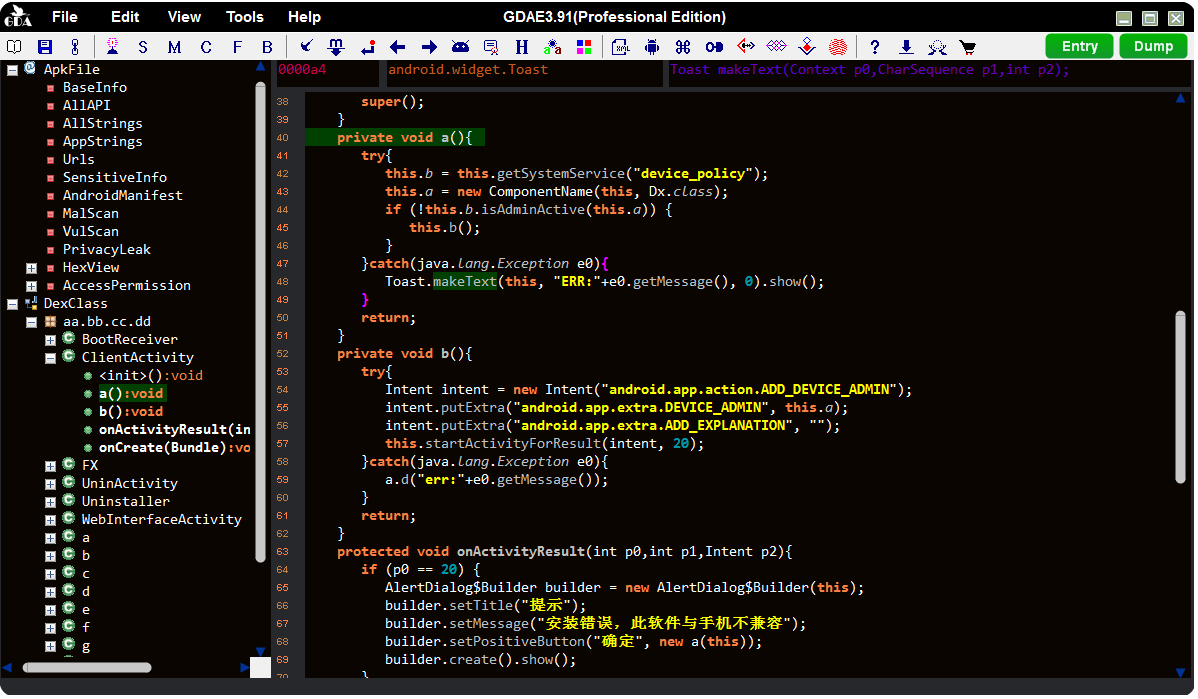 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 jeffssh/cve-2021-30860
Collection of materials relating to FORCEDENTRY
 eddinos2/cve-2026-28956-jxl-messages-surface
iOS Messages JPEG XL delivery-surface probe and patch-diff notes for CVE-2026-28956.