
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
522 results
wifiphisher preview

wifiphisher

GitHubwifiphisher/wifiphisher

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

impersonation-toolsmalware-analysisphishing+6
14.9k
4 months ago
BlueTeam-Tools preview

BlueTeam-Tools

GitHuba-poc/blueteam-tools

Tools and Techniques for Blue Team / Incident Response

curated-resourcesdata-recoverydefensive-tools+8
4.5k1 month ago
Veto preview

Veto

GitHubprofessorquantumuniverse/veto

Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
android-securitydynamic-analysis-sandboxingforensics+8
1913 days ago
Fortinet-FortiWeb-Fabric-Connector-CVE-2025-25257-Detection preview

Fortinet-FortiWeb-Fabric-Connector-CVE-2025-25257-Detection

GitHubgarethmsheldon/fortinet-fortiweb-fabric-connector-cve-2025-25257-detection

This repository provides production-ready detection engineering content for **CVE-2025-25257**, a pre-authentication SQL Injection vulnerability in…

educationexploitationforensics+8
7 months ago
ThreatScraper preview

ThreatScraper

GitHubamorath/threatscraper

Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
information-gatheringmalware-analysisthreat-intelligence+1
73 years ago
DeepTraffic preview

DeepTraffic

GitHubechowei/deeptraffic

Deep Learning models for network traffic classification
anomaly-detectionencryption-decryption-toolsintrusion-detection+4
7698 months ago
AntiVE-BehaviorWatch preview

AntiVE-BehaviorWatch

GitHubnirvanaon/antive-behaviorwatch

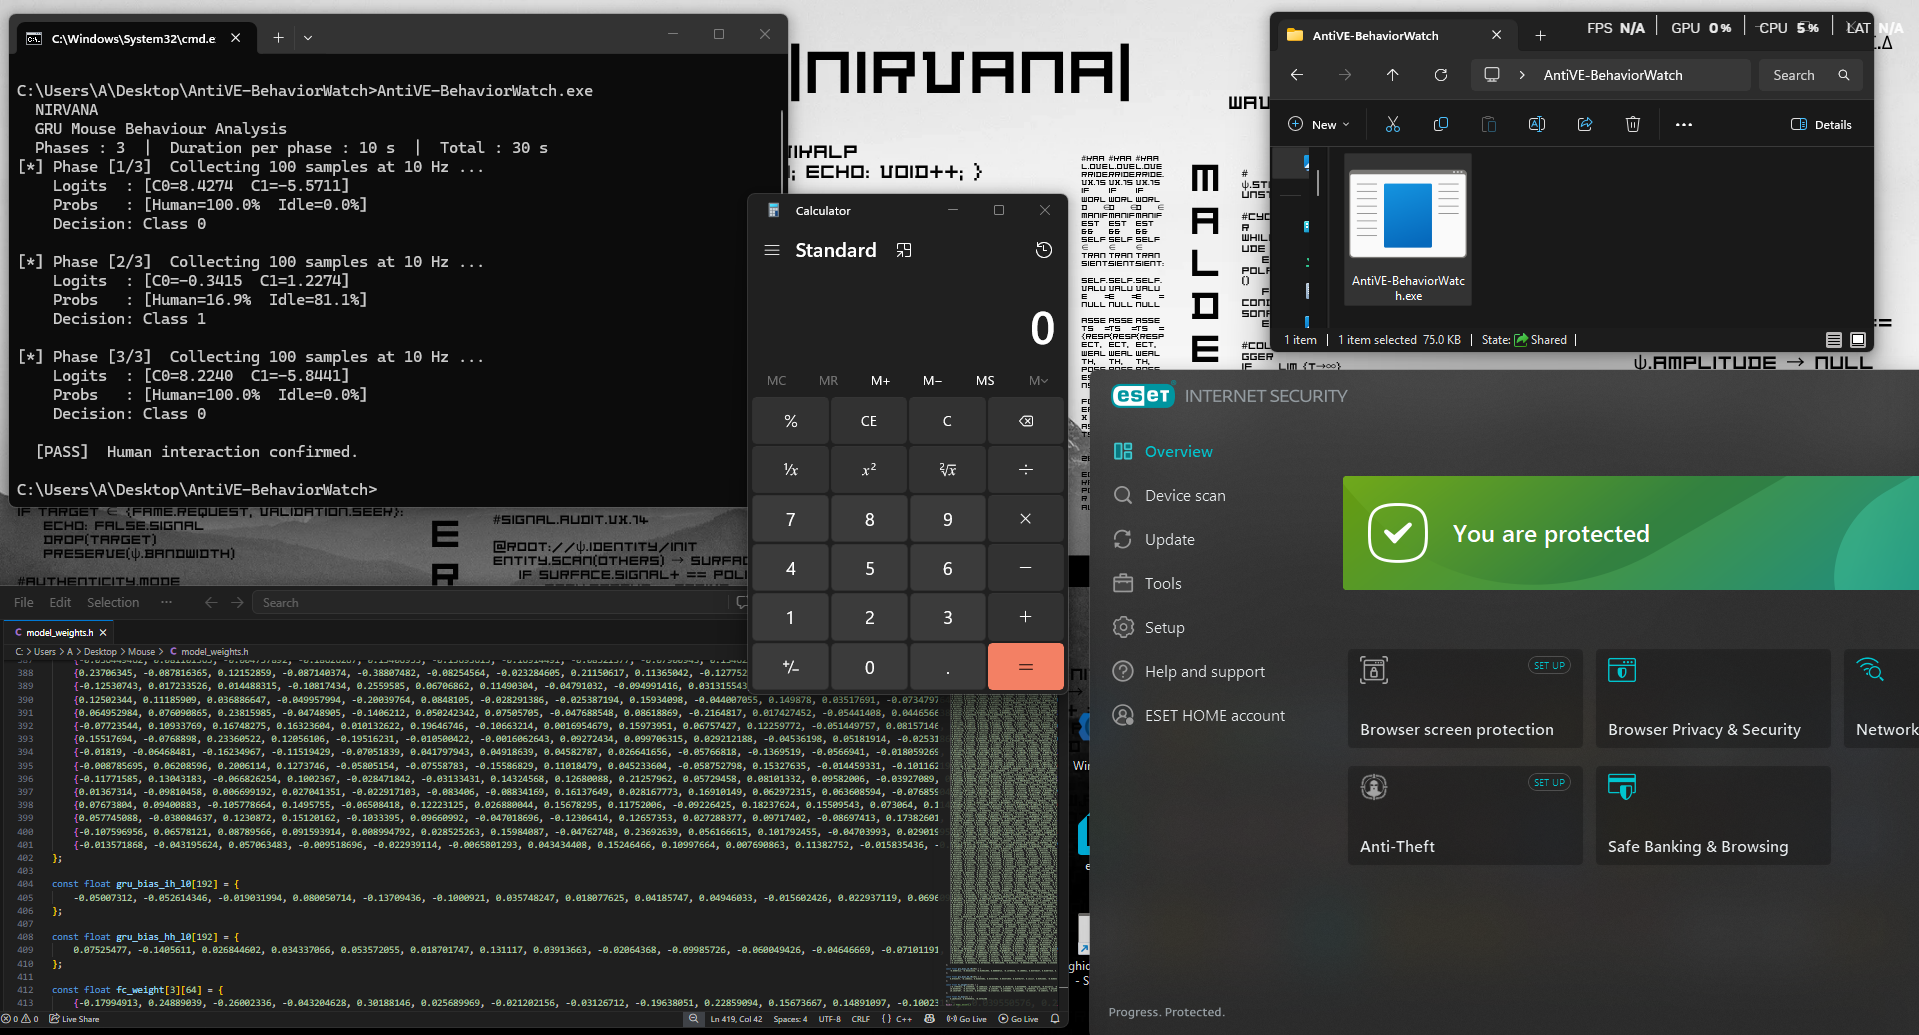
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
anti-botdynamic-analysis-sandboxingids-ips-evasion+3
402 months ago
speakeasy preview

speakeasy

GitHubmandiant/speakeasy

Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2.1k10h 17m ago
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

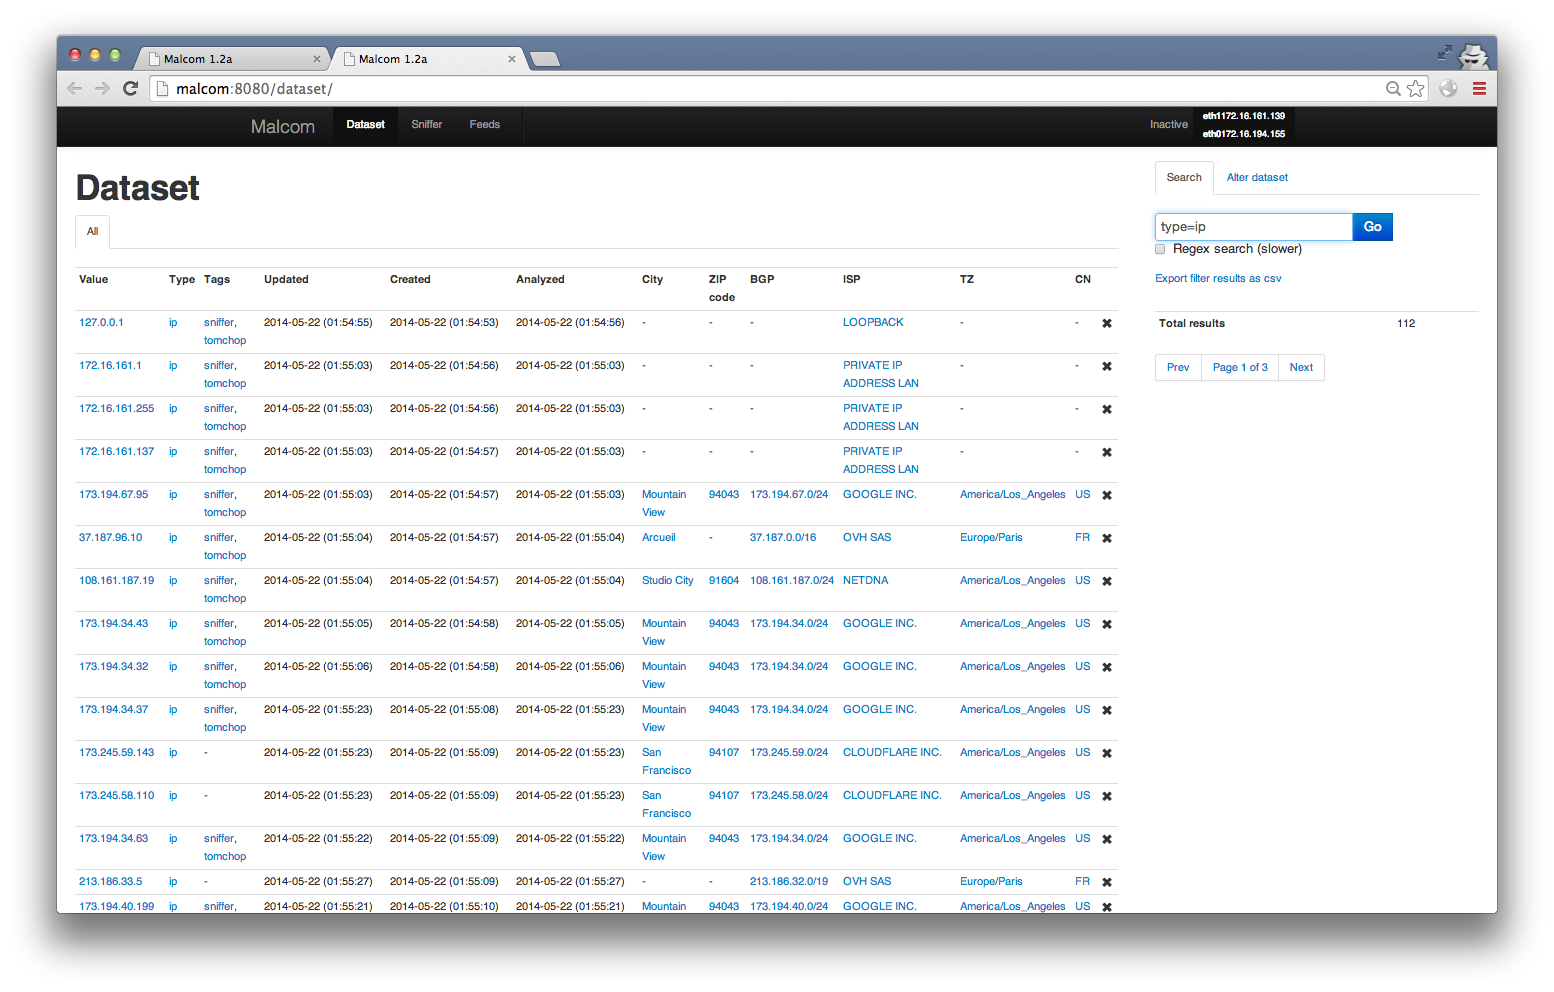
A tool to assist with network-based hunting for GRU's Drovorub malware c2
incident-responseintrusion-detectionmalware-analysis+3
256 years ago
malcom preview

malcom

GitHubtomchop/malcom

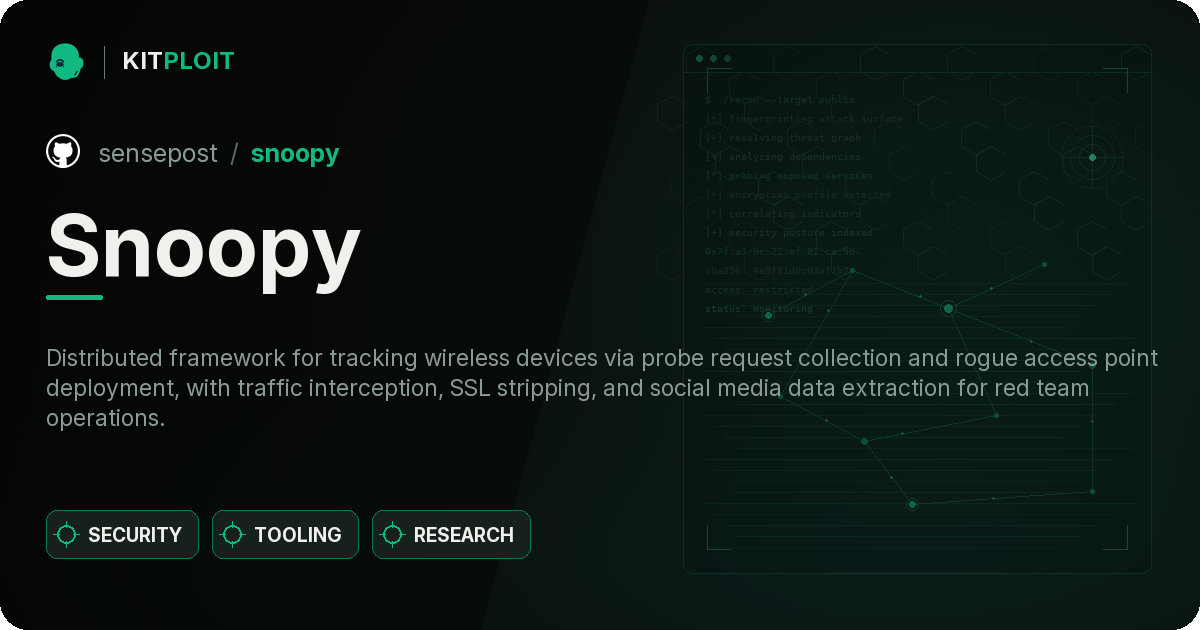
Malcom - Malware Communications Analyzer
malware-analysisnetwork-forensicsthreat-intelligence
1.2k8 years ago
Snoopy preview

Snoopy

GitHubsensepost/snoopy

Snoopy: A distributed tracking and data interception framework
malware-analysisnetwork-mappingosint+5
61313 years ago
doublepulsar-detection-script preview

doublepulsar-detection-script

GitHubwithsecurelabs/doublepulsar-detection-script

A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.
incident-responseintrusion-detectionmalware-analysis+2
1.0k9 years ago
flare-fakenet-ng preview

flare-fakenet-ng

GitHubmandiant/flare-fakenet-ng

FakeNet-NG - Next Generation Dynamic Network Analysis Tool
dynamic-analysis-sandboxingmalware-analysisnetwork-security+2
2.2k4 months ago
droidbox preview

droidbox

GitHubpjlantz/droidbox

Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
android-securitydynamic-analysis-sandboxinginformation-gathering+2
8106 years ago
dionaea preview

dionaea

GitHubdinotools/dionaea

Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.

defensive-toolsintrusion-detectionmalware-analysis+2
8185 years ago
stegowiper preview

stegowiper

GitHubmindcrypt/stegowiper

A powerful and flexible tool to apply active attacks for disrupting stegomalware
defensive-toolsincident-responsemalware-analysis+2
564 years ago
BPFDoor-controller-source preview

BPFDoor-controller-source

GitHubhaxrob/bpfdoor-controller-source

Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
command-and-controlexploitationmalware-analysis+4
156 months ago
pingback preview

pingback

GitHubcorelight/pingback

A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.

command-and-controlintrusion-detectionmalware-analysis+2
121 year ago
Previous12…29Next