
CTF-s-Tools
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
cryptographyctfcurated-resources+9
ph4l4nx/ctf-s-toolsRepository to index useful tools for CTF's

 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 outflanknl/evilclippy
A cross-platform assistant for creating malicious MS Office documents. Can hide VBA macros, stomp VBA code (via P-Code) and confuse macro analysis…
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 sobri3195/pegasus-malware-scan
Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…
 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration
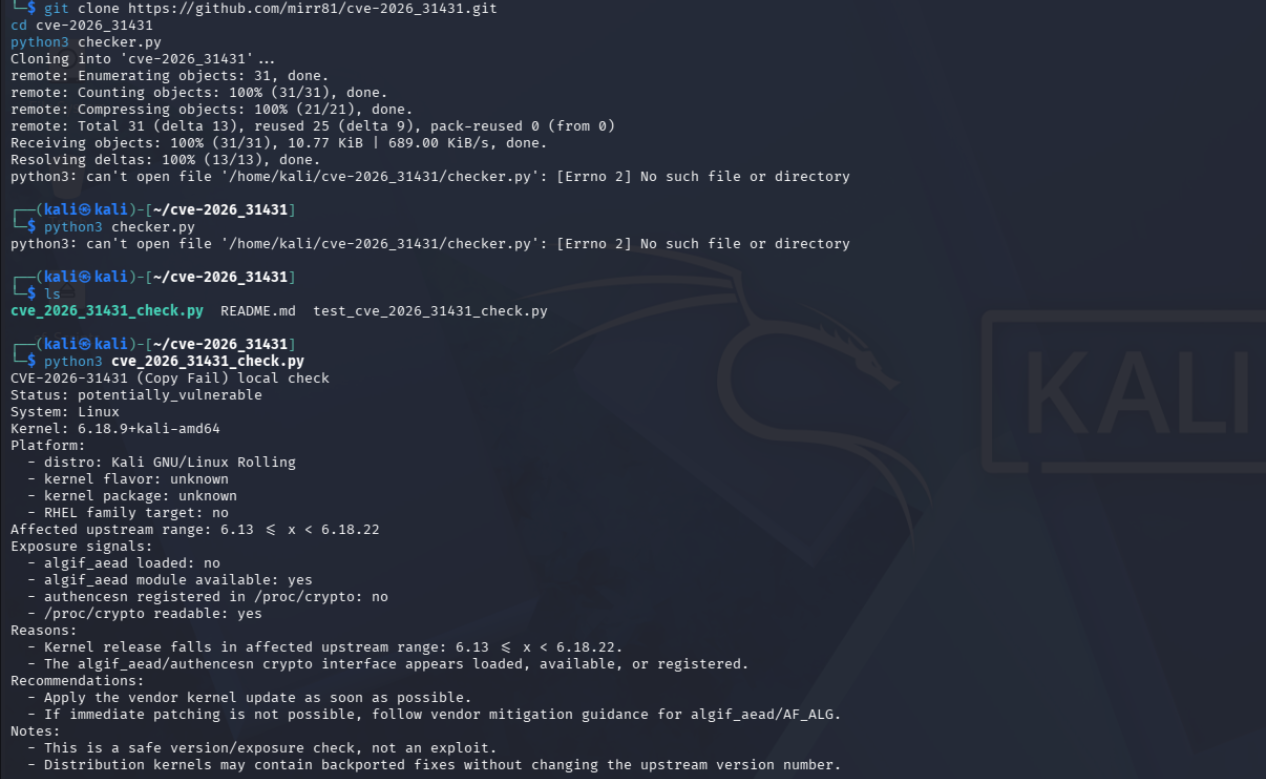 kuniyal08/copy-fail-cve-2026-31431-lab
Reproduced the fileless LPE CVE‑2026‑31431 (“Copy Fail”) on Kali Linux, then built auditd, Sigma & YARA detections to catch this stealthy kernel…
 solomon12354/lockinggirl-----cve-2022-0847-dirty_pipe_virus
Educational demonstration of CVE-2022-0847 (Dirty Pipe) Linux kernel exploit with automated compilation script for privilege escalation and file…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
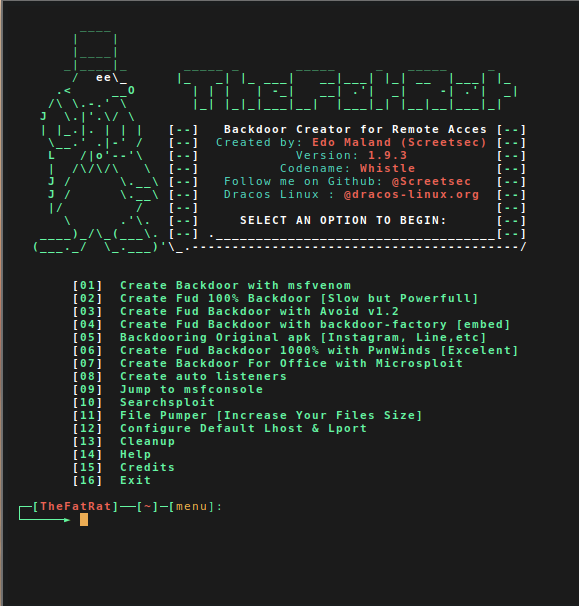 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.