

capstone
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.0k
capstone-engine/capstoneMulti-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 rek7/fireelf
fireELF - Fileless Linux Malware Framework
 punch-cyber/stoq
An open source framework for enterprise level automated analysis.
 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 viper-framework/viper
Binary analysis and management framework
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 danielbohannon/revoke-obfuscation
PowerShell Obfuscation Detection Framework
 sensepost/snoopy
Snoopy: A distributed tracking and data interception framework
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 cert-polska/karton
Distributed malware processing framework based on Python, Redis and S3.
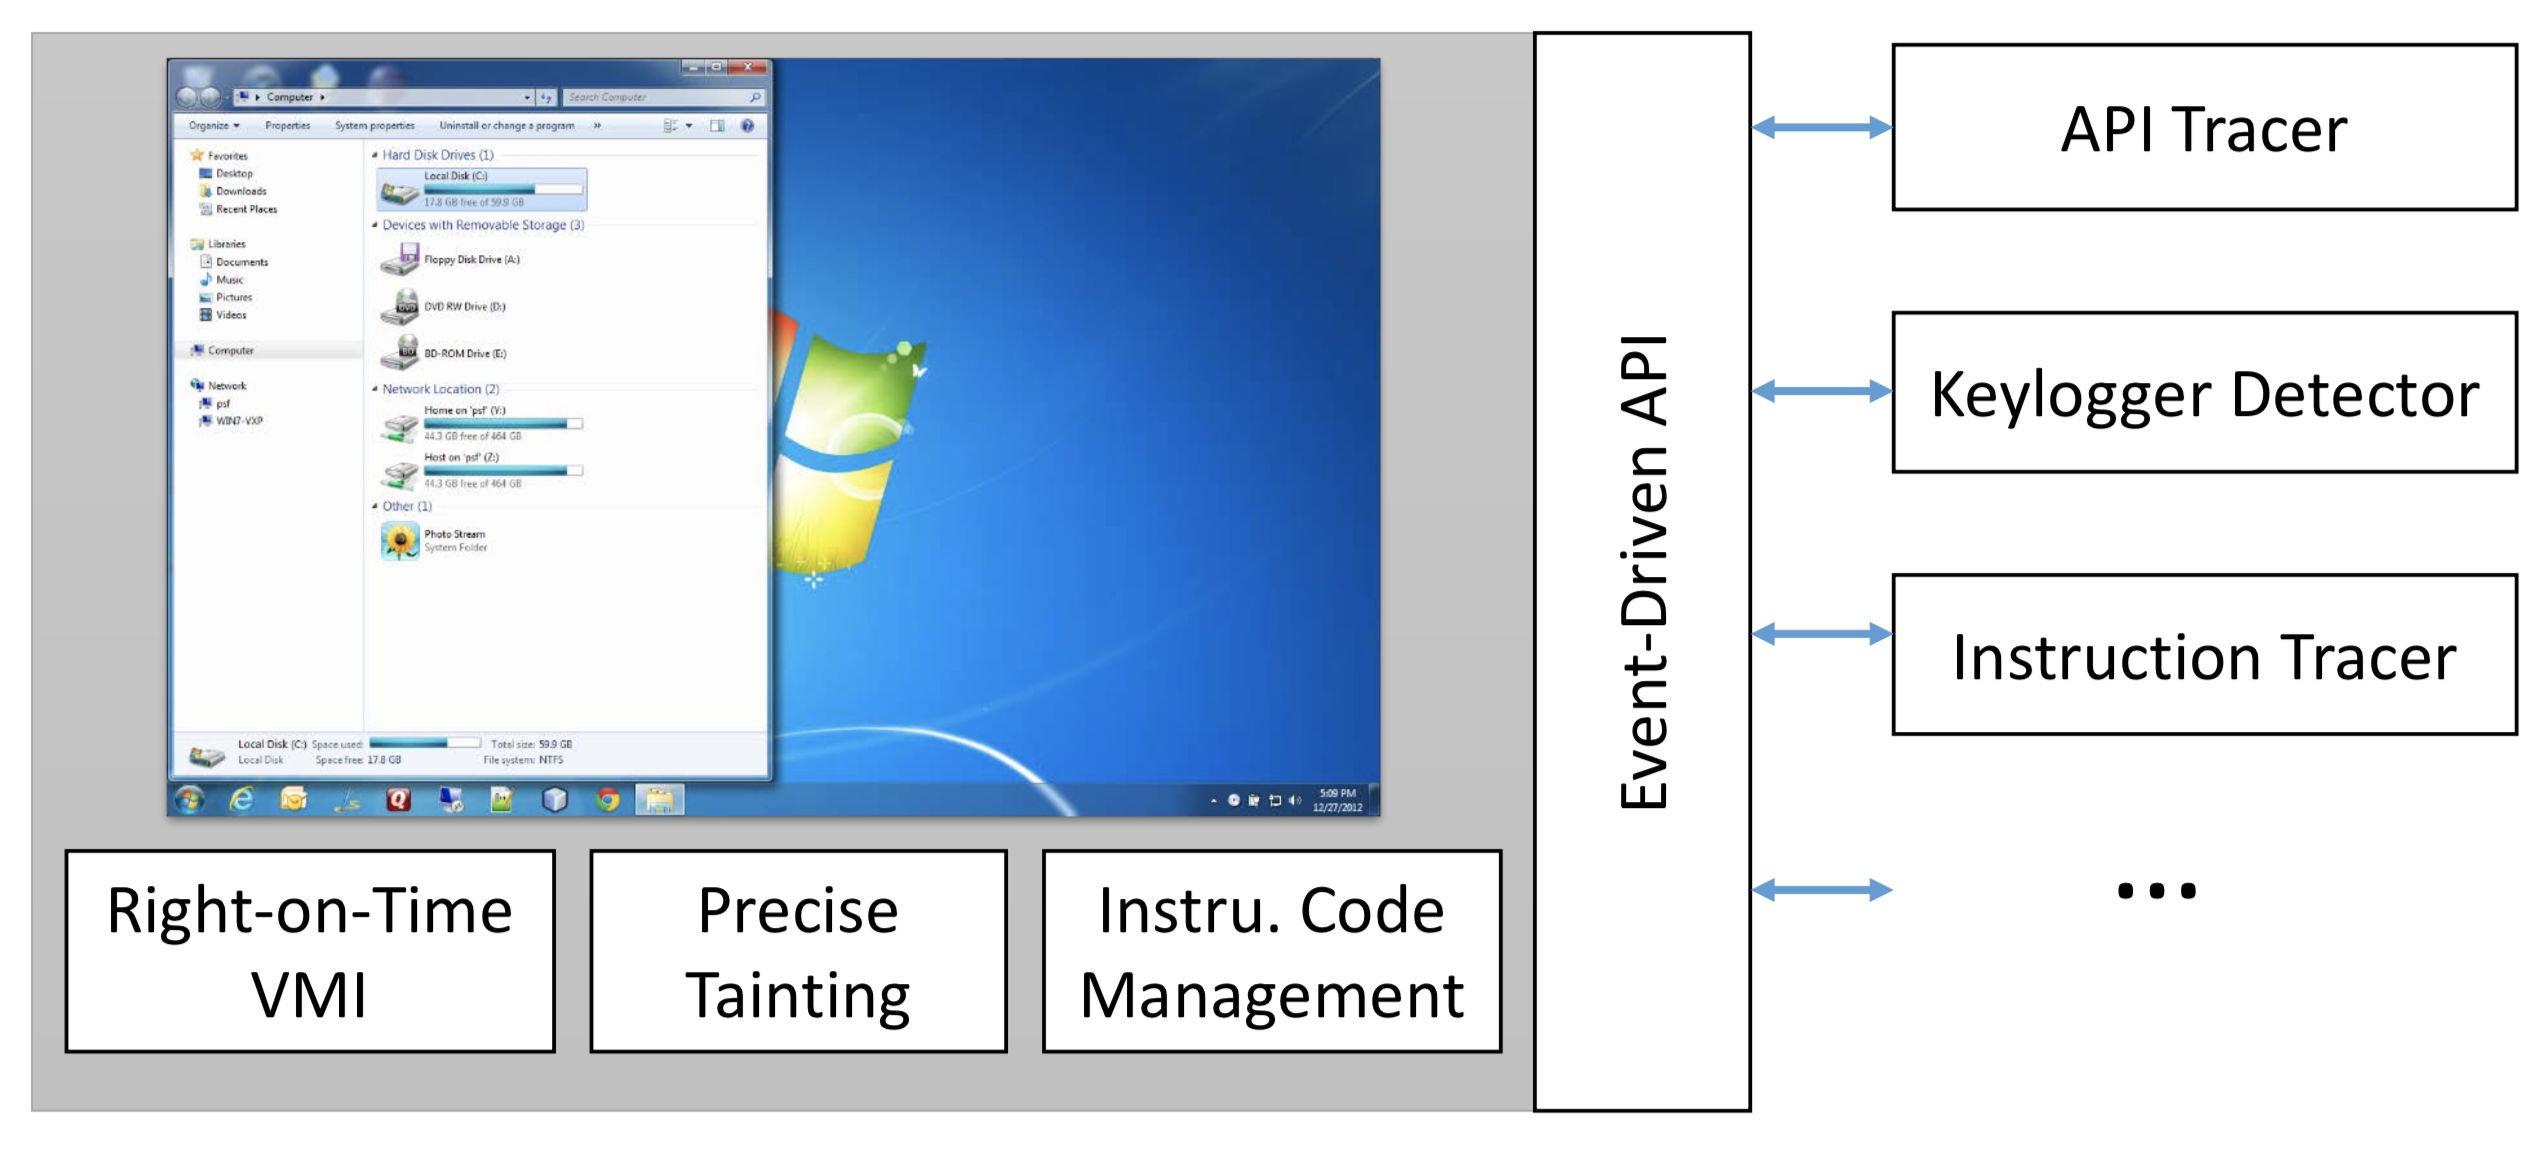 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…