
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
kaiju preview

kaiju

GitHubcmu-sei/kaiju

CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
binary-analysisfirmware-analysismalware-analysis+2
147
6 months ago
DECAF preview

DECAF

GitHubdecaf-project/decaf

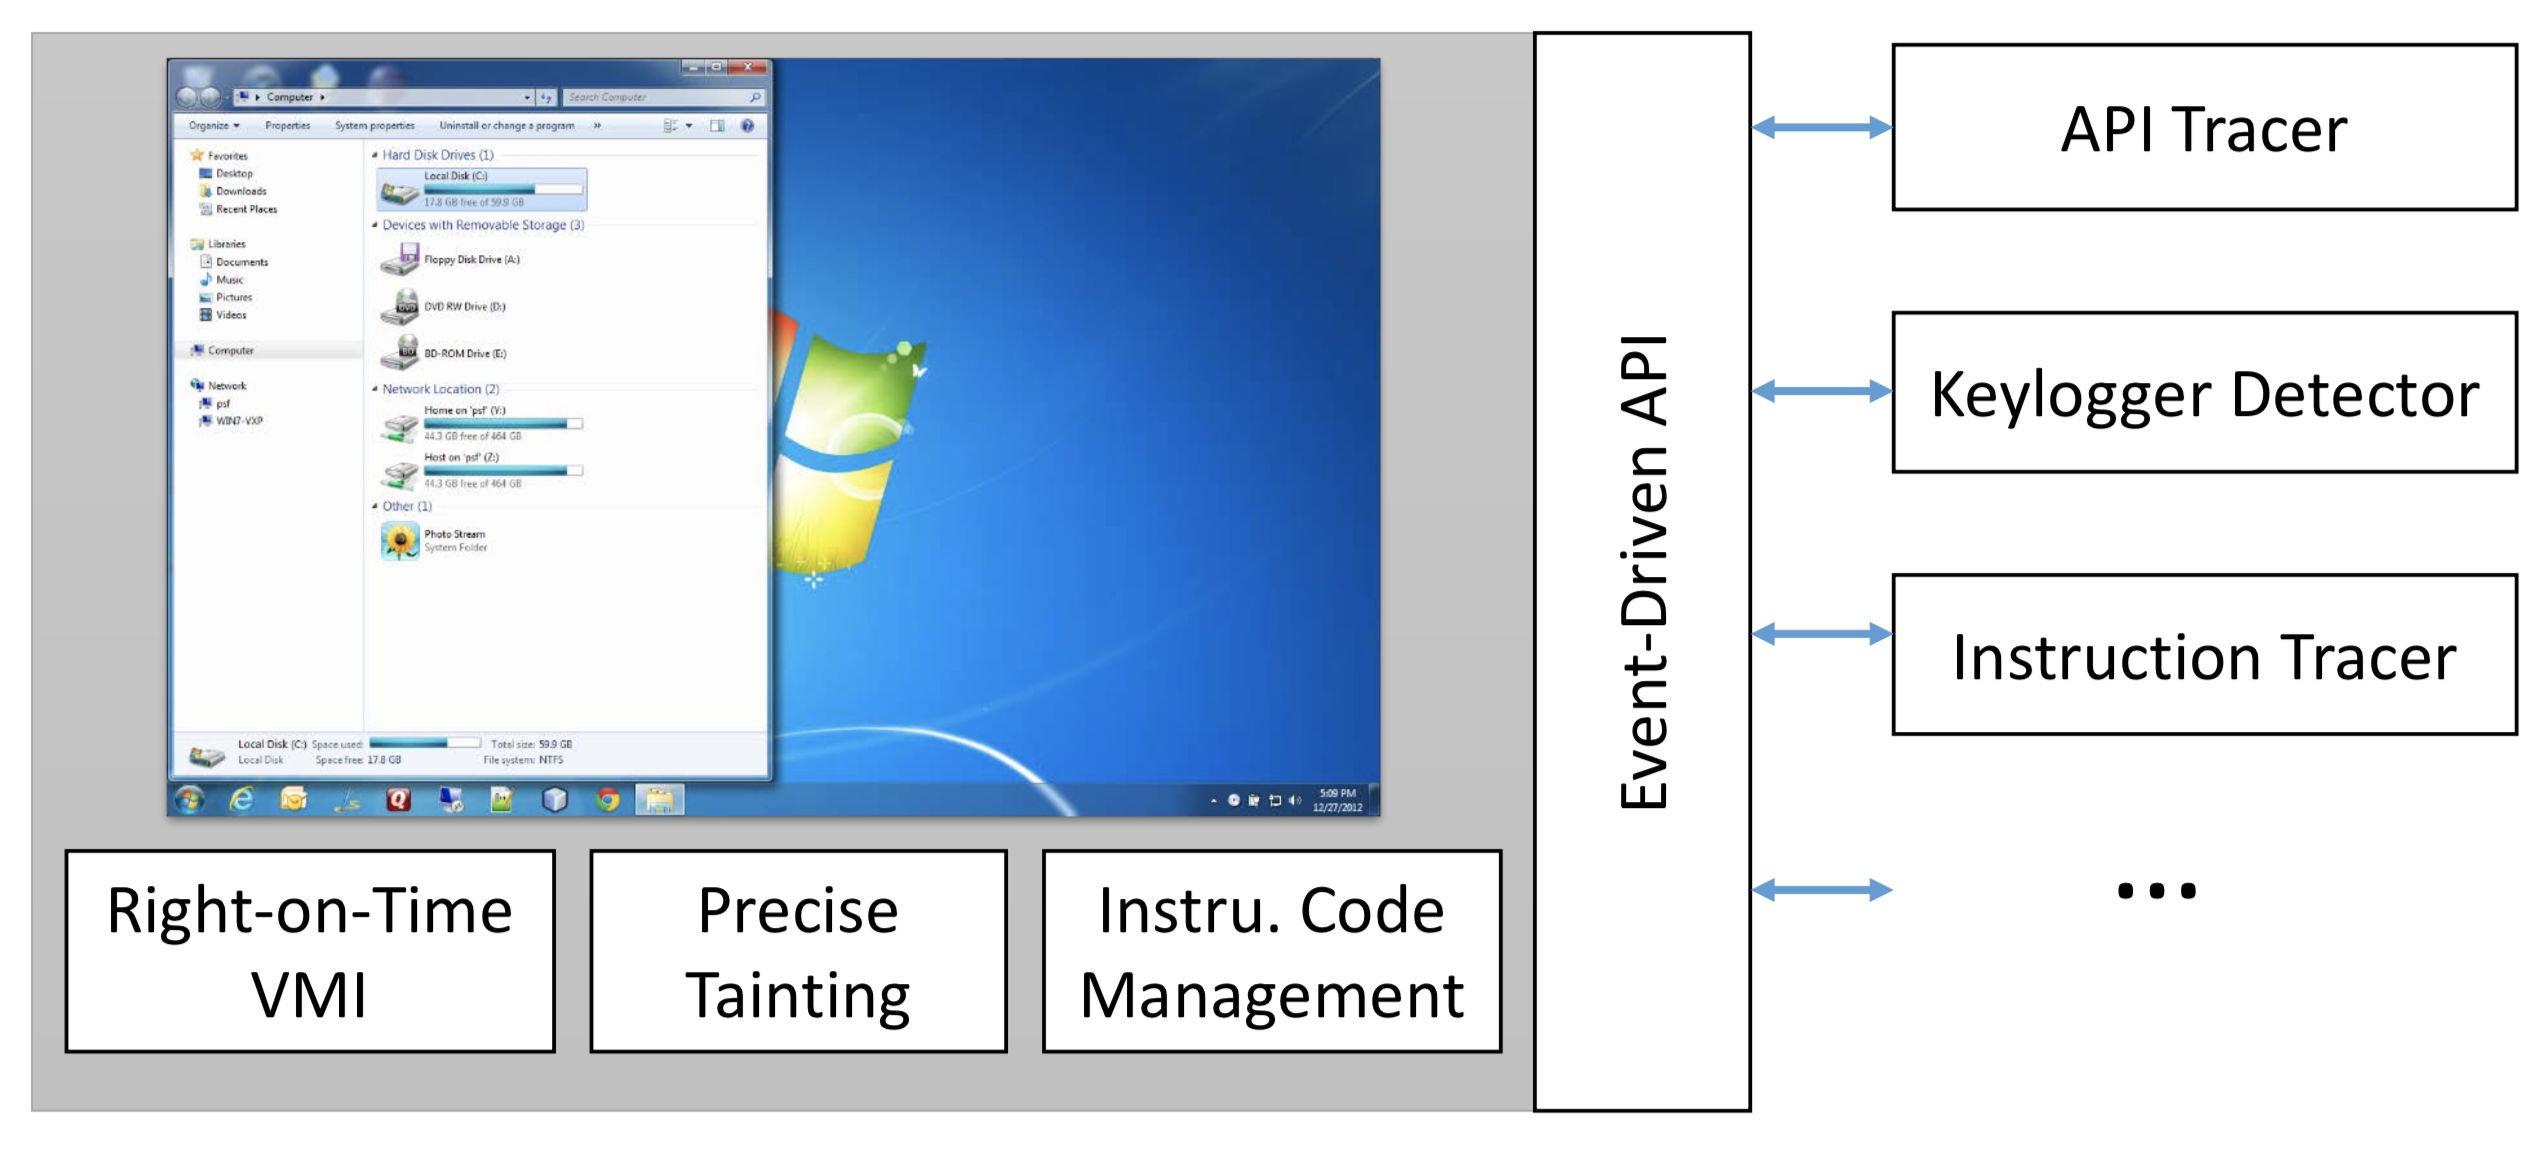
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
android-securitybinary-analysisdynamic-analysis-sandboxing+2
8415 years ago
flare-emu preview

flare-emu

GitHubmandiant/flare-emu

Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
9551 year ago
multiscanner preview

multiscanner

GitHubmitre/multiscanner

Modular file scanning/analysis framework
dynamic-analysis-sandboxingmalware-analysisstatic-analysis+1
6197 years ago
sharem preview

sharem

GitHubbw3ll/sharem

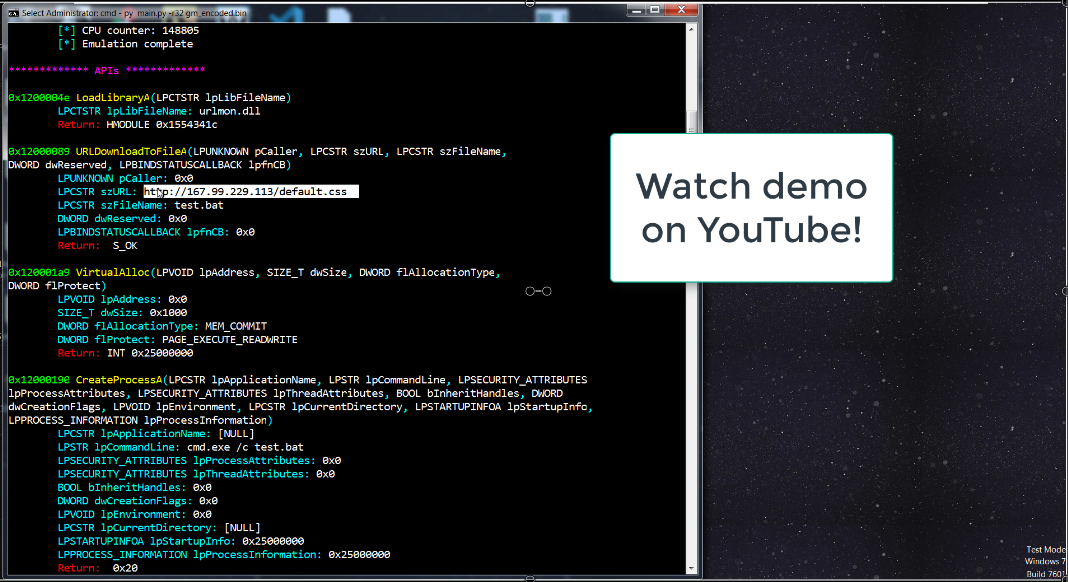
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4926 months ago
AndroPyTool preview

AndroPyTool

GitHubalexmyg/andropytool

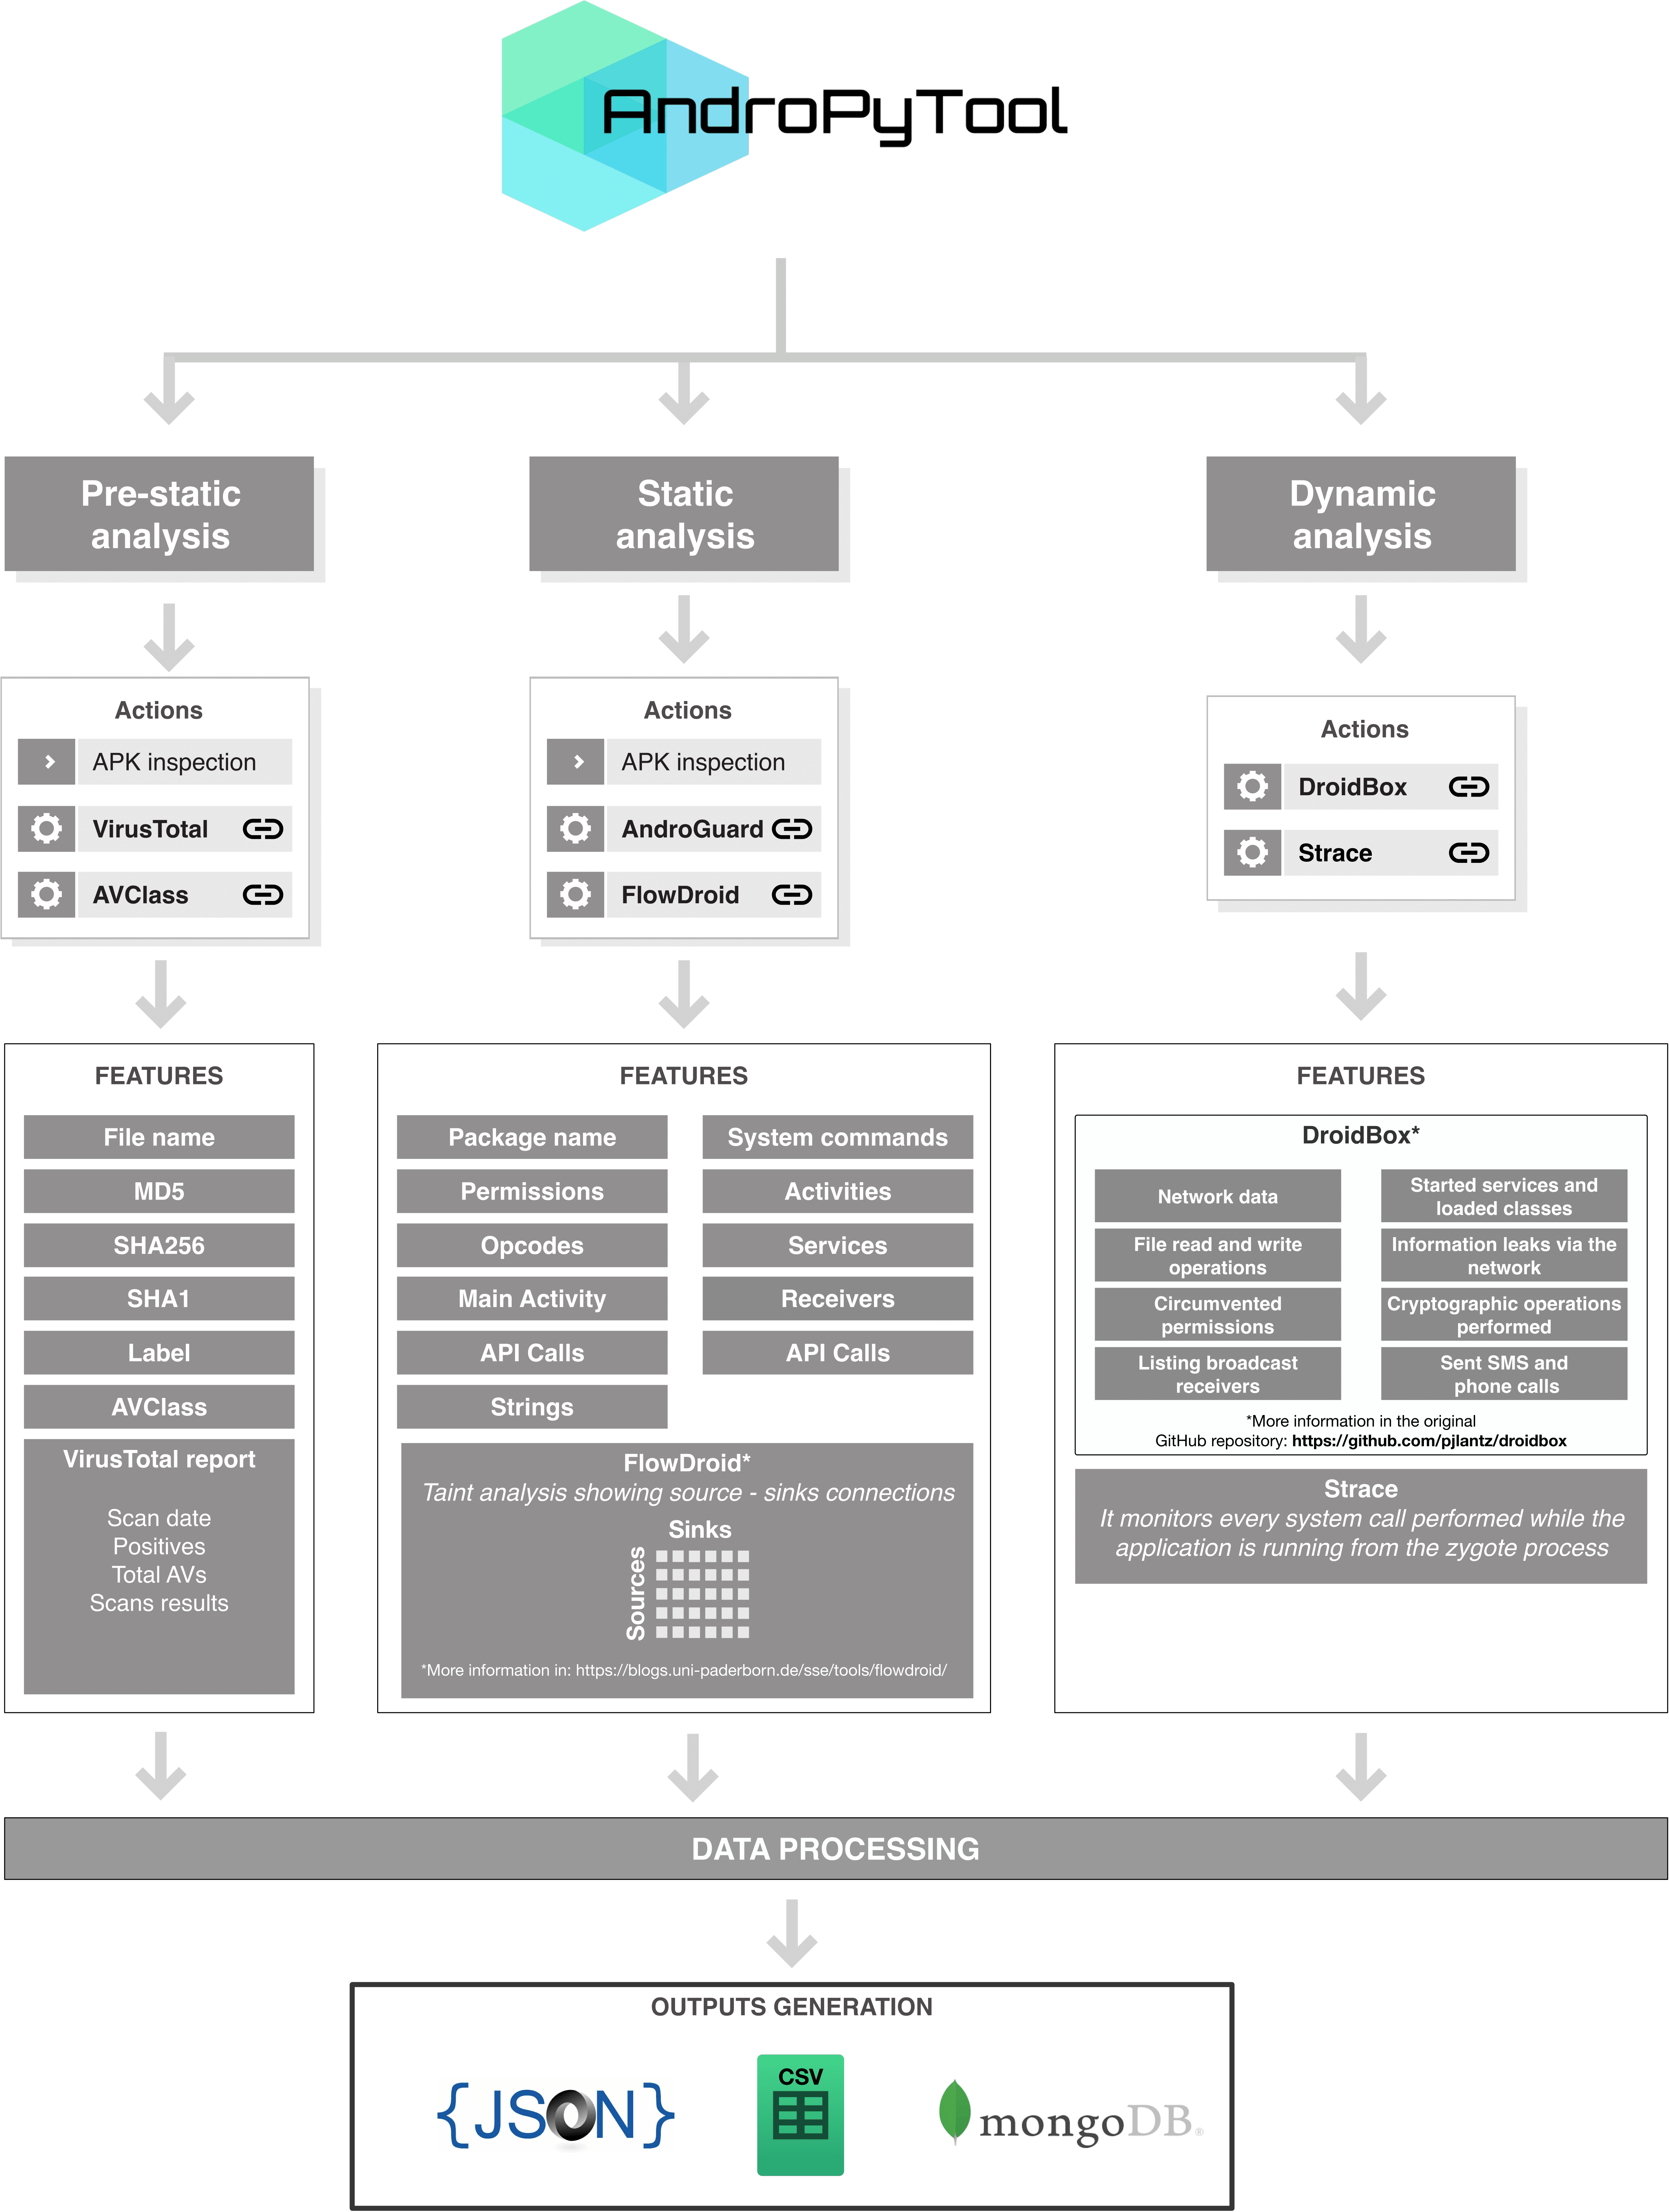
A framework for automated extraction of static and dynamic features from Android applications

android-securitydynamic-analysis-sandboxingmalware-analysis+2
3826 years ago
MalConfig preview

MalConfig

GitHubjacobsoo/malconfig

This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.

android-securitycommand-and-controlinformation-gathering+3
77 years ago
amtracker preview

amtracker

GitHubjacobsoo/amtracker

Android Malware Tracker
android-securitycommand-and-controlinformation-gathering+3
292 years ago
CrowdFMS preview
Archived

CrowdFMS

GitHubcrowdstrike/crowdfms

CrowdStrike Feed Management System. CrowdFMS is a framework for automating collection and processing of samples from VirusTotal, by leveraging the…
api-securitydynamic-analysis-sandboxingmalware-analysis+1
1337 years ago
neurax preview

neurax

GitHubredcode-labs/neurax

A framework for constructing self-spreading binaries

command-and-controlexploitationlateral-movement+7
1.0k2 years ago
viper preview
Archived

viper

GitHubviper-framework/viper

Binary analysis and management framework
binary-analysisexploit-frameworksforensics+3
1.6k3 years ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
digital-forensicsforensicsincident-response+2
4.5k17 days ago
buttinsky preview

buttinsky

GitHubmushorg/buttinsky

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…

information-gatheringintrusion-detectionmalware-analysis+2
8213 years ago
Androl4b preview

Androl4b

GitHubsh4hin/androl4b

A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
android-securityeducationlabs-practice+4
1.2k6 years ago
VMDragonSlayer preview

VMDragonSlayer

GitHubpoppopjmp/vmdragonslayer

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
4391 year ago
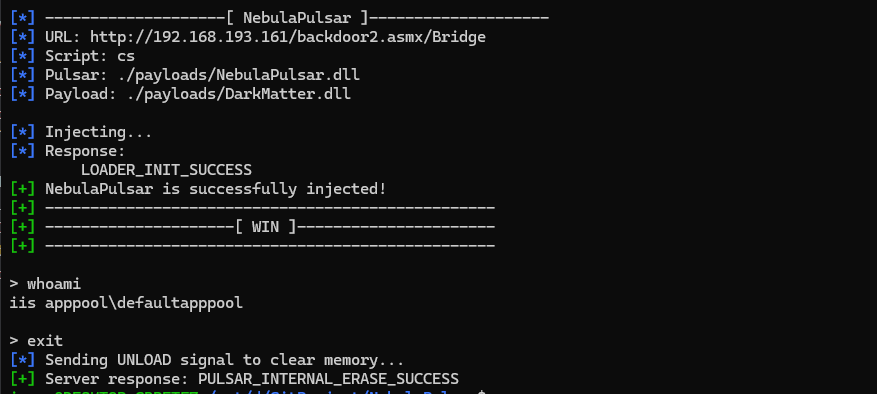
NebulaPulsar preview

NebulaPulsar

GitHubiss4cf0ng/nebulapulsar

NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…

dynamic-code-analysiseducationencryption-decryption-tools+7
463 months ago
pyREtic preview

pyREtic

GitHubmynameismeerkat/pyretic

pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
binary-analysiscode-analysisdebuggers+5
2683 years ago
volatility preview
Archived

volatility

GitHubvolatilityfoundation/volatility

An advanced memory forensics framework

digital-forensicsforensicsincident-response+4
8.1k1 year ago
Previous12Next