cve-2024-7965-poc
 xuedugu/cve-2024-7965-poc
CVE-2024-7965是Google Chrome浏览器中V8 JavaScript引擎的一个高危漏洞。该漏洞源于V8引擎在处理特定JavaScript代码时实现不当,导致堆内存损坏。攻击者可通过诱导用户访问包含特制JavaScript的恶意网页,利用此漏洞在Chrome渲染器中执行任意代码。
exploitationmalware-analysisvulnerability-analysis+1
1
xuedugu/cve-2024-7965-pocCVE-2024-7965是Google Chrome浏览器中V8 JavaScript引擎的一个高危漏洞。该漏洞源于V8引擎在处理特定JavaScript代码时实现不当,导致堆内存损坏。攻击者可通过诱导用户访问包含特制JavaScript的恶意网页,利用此漏洞在Chrome渲染器中执行任意代码。
 mohammadnassiri/yaasa
Yet Another APK Static Analyzer
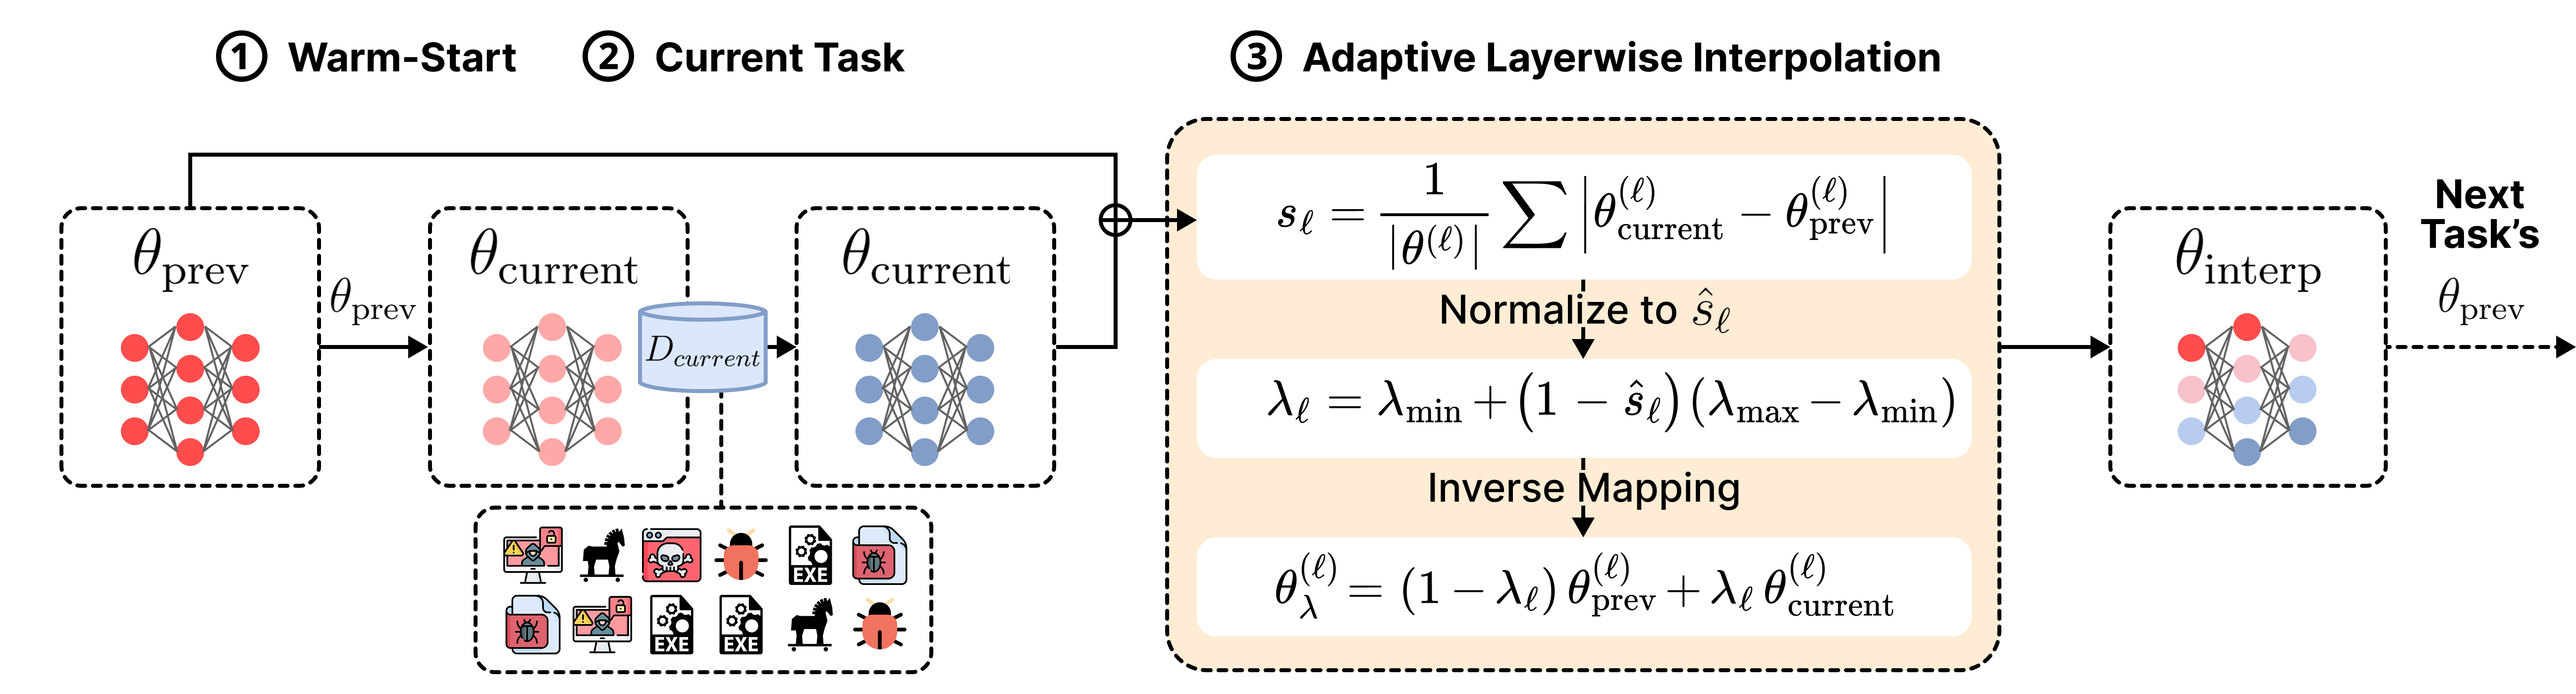 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
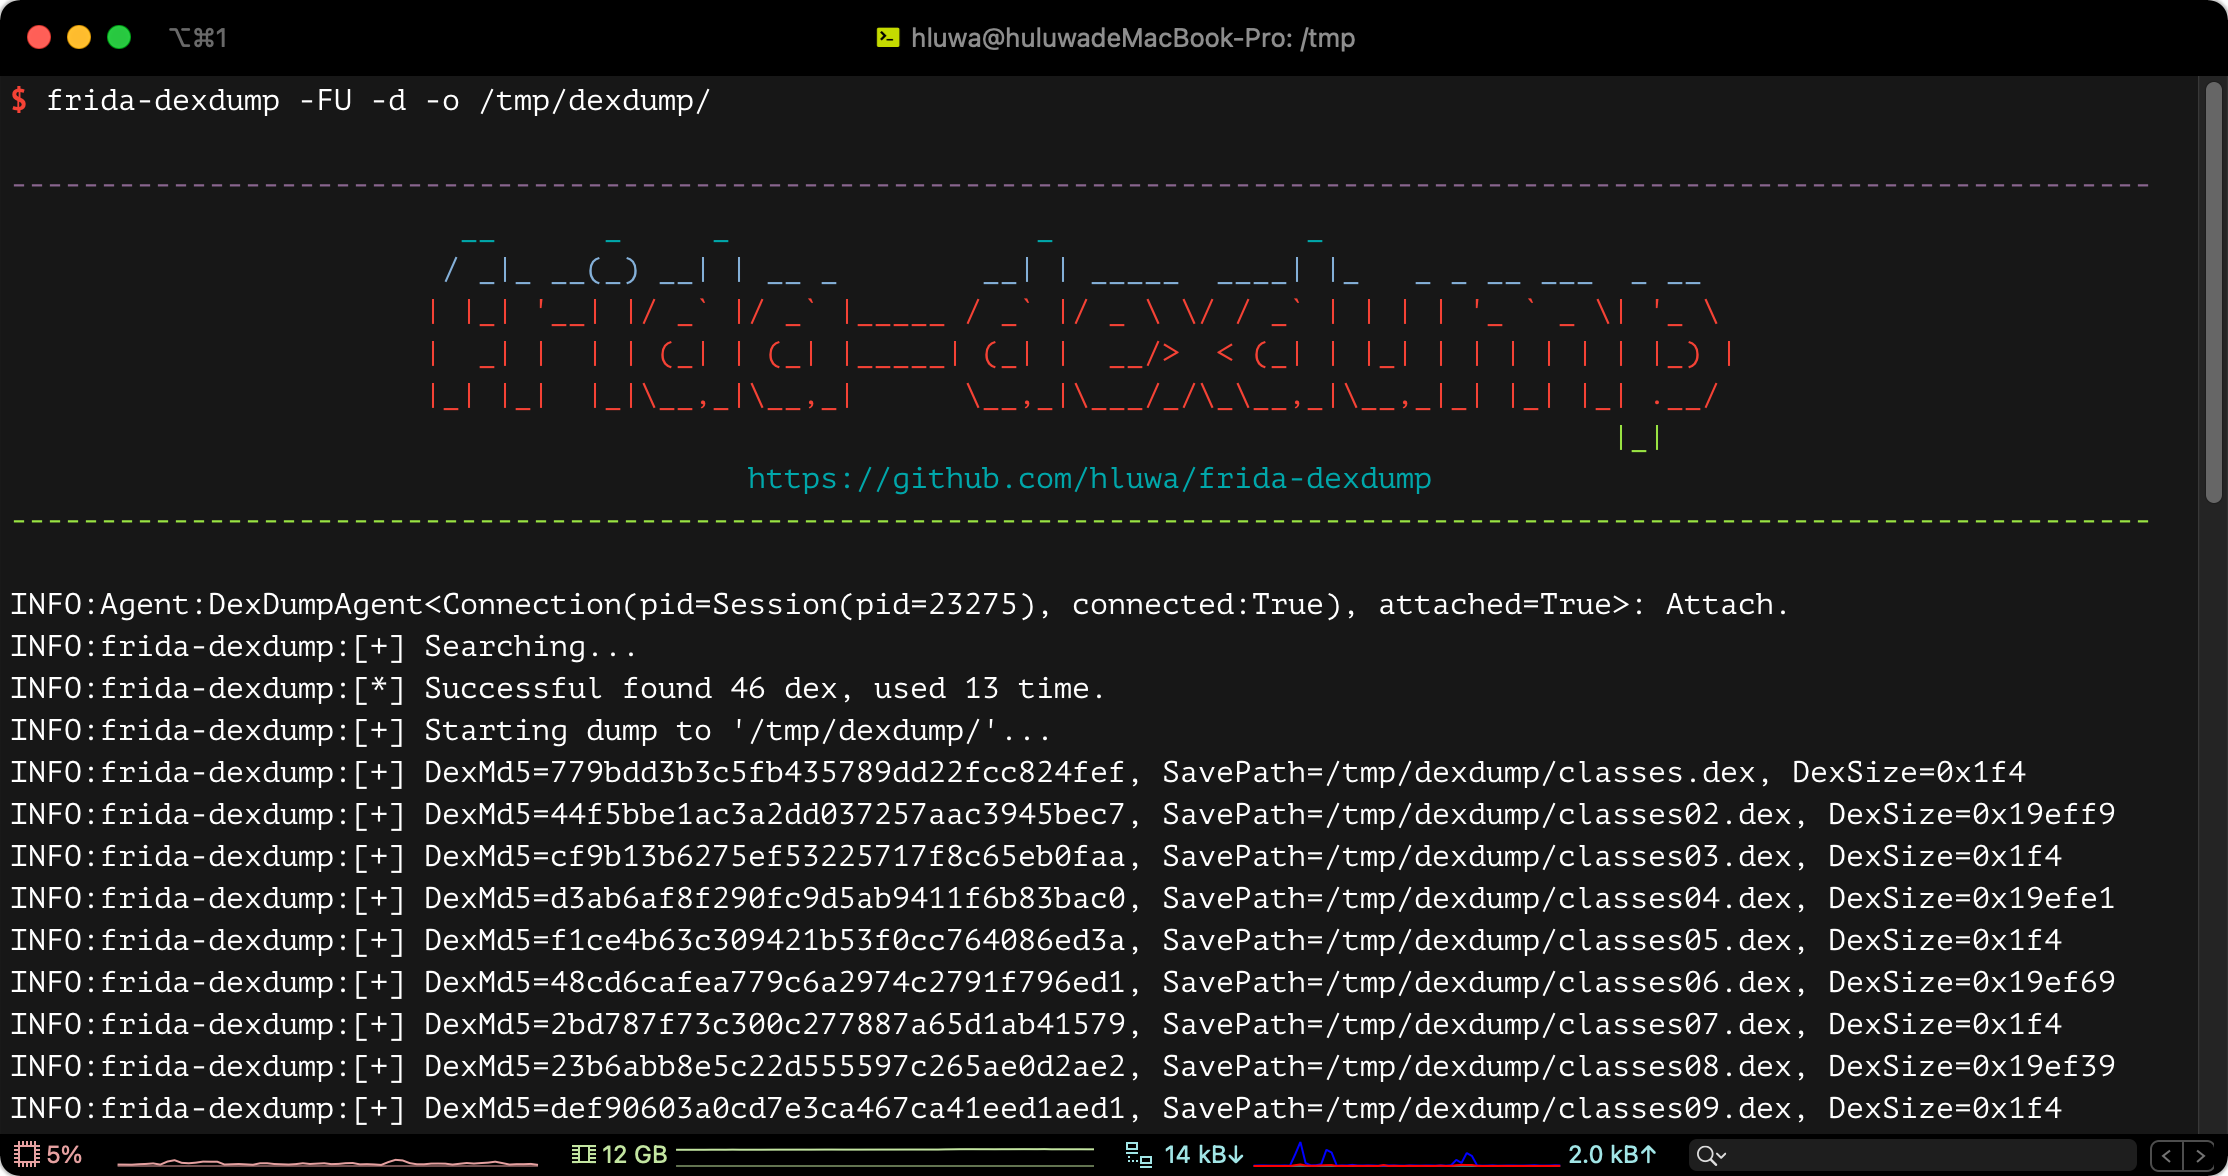 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration