
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
135 results
MalPipe preview

MalPipe

GitHubsilascutler/malpipe

Malware/IOC ingestion and processing engine
information-gatheringioc-managementmalware-analysis+2
1107 years ago
buttinsky preview

buttinsky

GitHubmushorg/buttinsky

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…

information-gatheringintrusion-detectionmalware-analysis+2
8213 years ago
WhoamiAlternatives preview

WhoamiAlternatives

GitHubricardojoserf/whoamialternatives

Different methods to get current username without using whoami
information-gatheringmalware-analysispost-exploitation+2
1872 years ago
TeleShadow3 preview

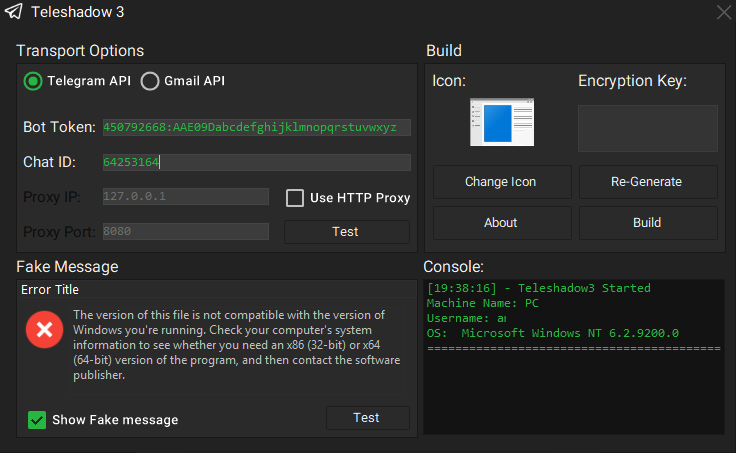
TeleShadow3

GitHubeternalc0der/teleshadow3

Telegram Desktop Session Stealer
information-gatheringmalware-analysisremote-access-trojan+1
1827 years ago
maldrolyzer preview

maldrolyzer

GitHubmaldroid/maldrolyzer

Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)

android-securitycommand-and-controlinformation-gathering+3
11211 years ago
intelligence preview

intelligence

GitHubctrlaltint3l/intelligence

Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
forensicsinformation-gatheringioc-management+3
5828 days ago
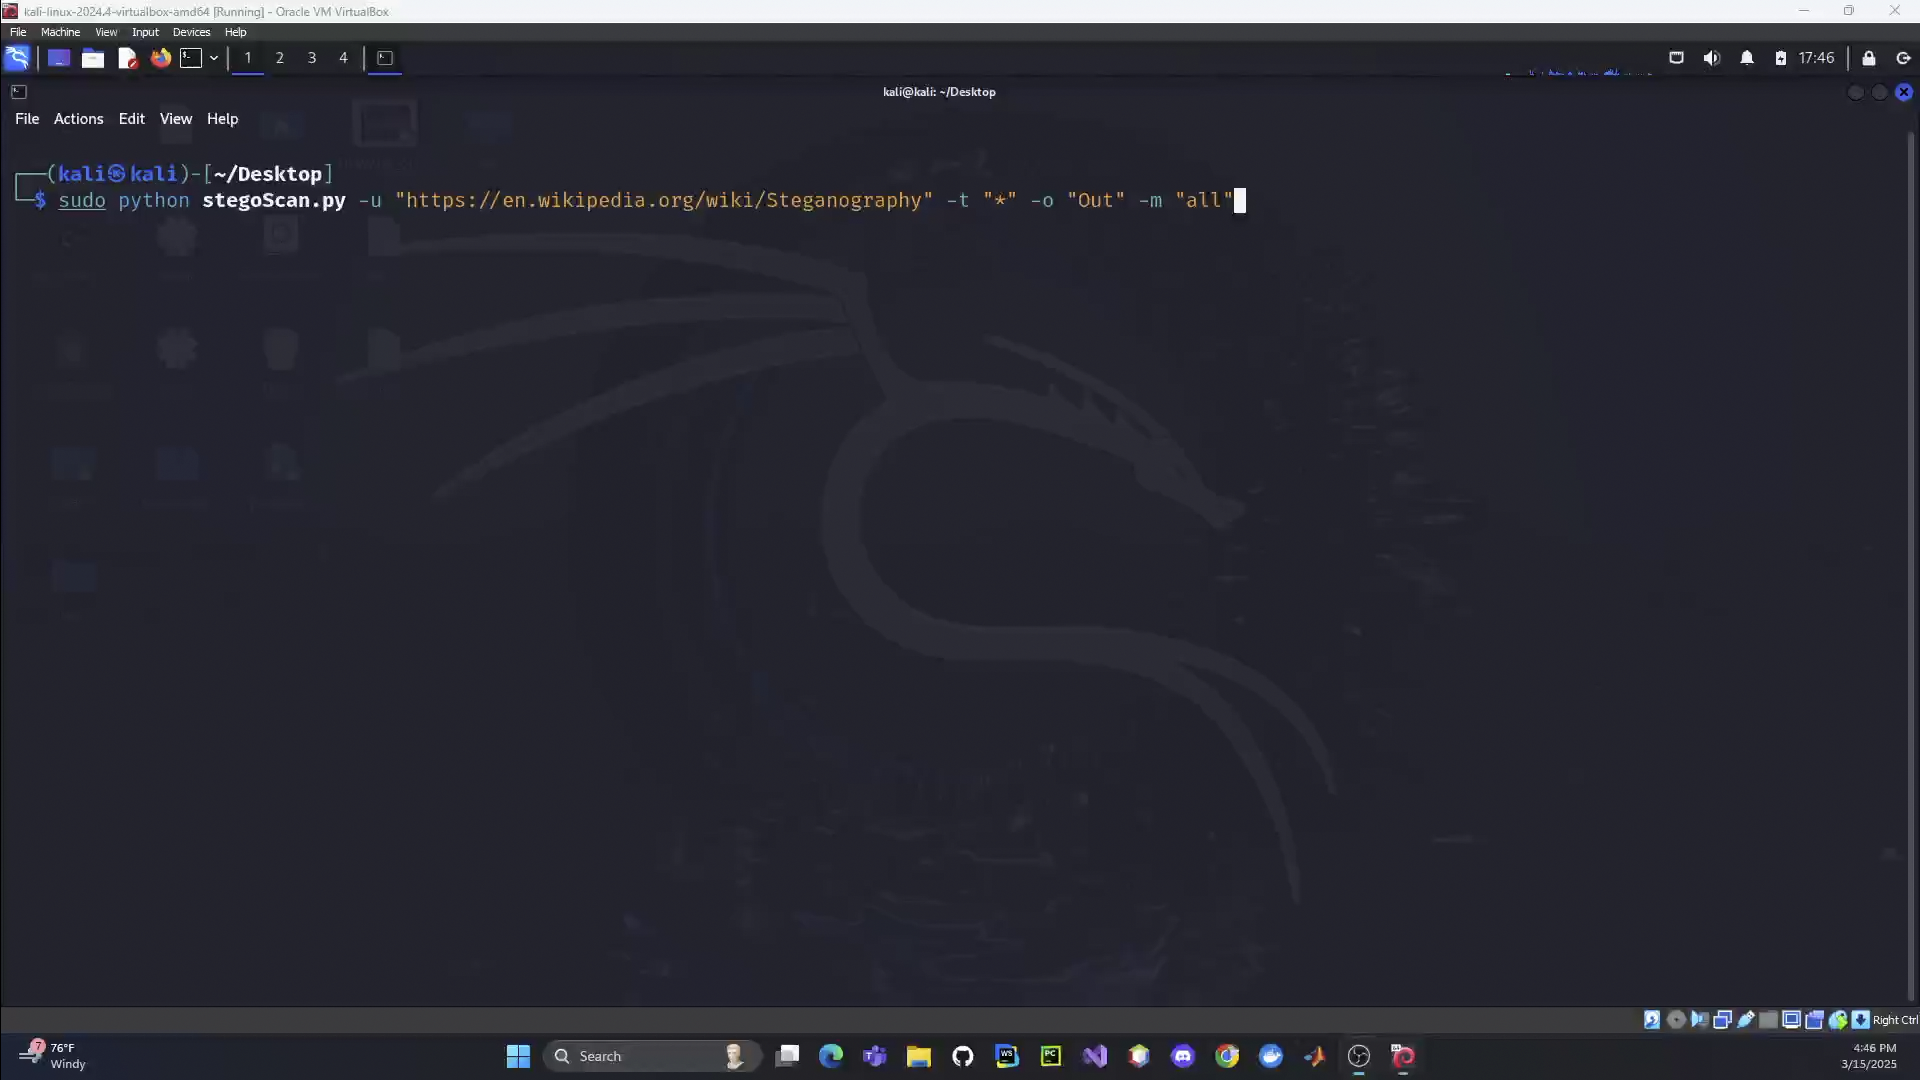
StegoScan preview

StegoScan

GitHublcbower33/stegoscan

Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
ai-securitybinary-analysiscrawler+7
1091 year ago
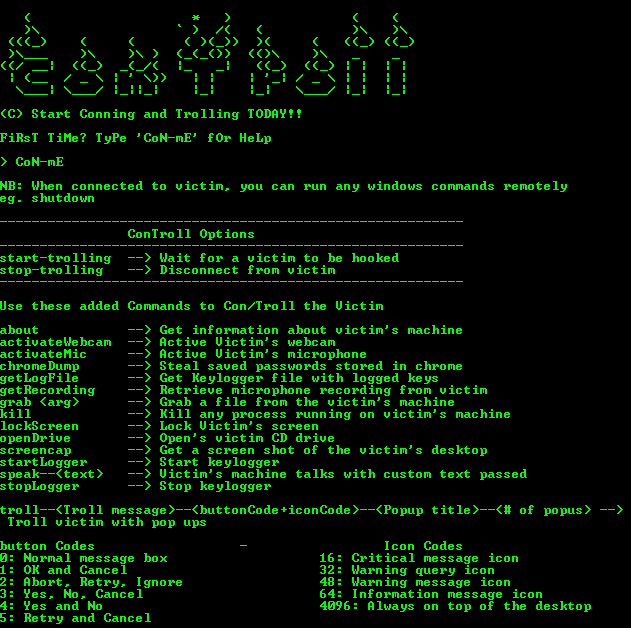
ConTroll_Remote_Access_Trojan preview

ConTroll_Remote_Access_Trojan

GitHublithium876/controll_remote_access_trojan

Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
command-and-controleducationinformation-gathering+7
1048 years ago
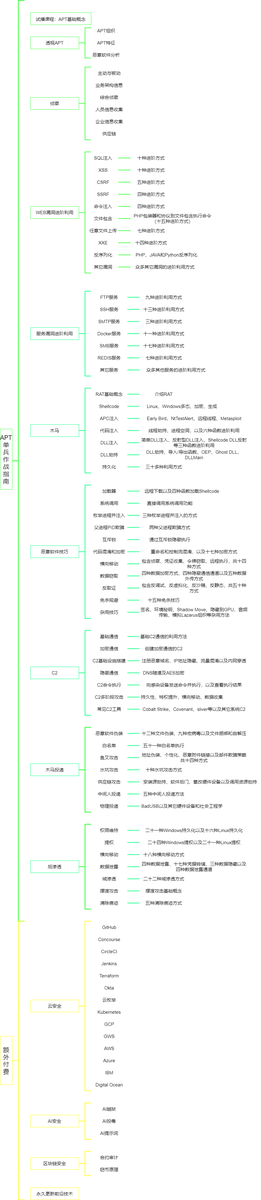
APT-Individual-Combat-Guide preview

APT-Individual-Combat-Guide

GitHubghostwolflab/apt-individual-combat-guide

Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

command-and-controleducationexploitation+7
11010 months ago
spybrowse preview

spybrowse

GitHub1d8/spybrowse

Code developed to steal certain browser config files (history, preferences, etc)
data-exfiltrationinformation-gatheringmalware-analysis+2
636 years ago
neto preview

neto

GitHubelevenpaths/neto

Neto | A tool to analyse browser extensions
code-analysiscryptographyinformation-gathering+2
887 years ago
dnschef-ng preview

dnschef-ng

GitHubbyt3bl33d3r/dnschef-ng

DNSChef (NG) - DNS proxy for Penetration Testers and Malware Analysts

data-exfiltrationdns-analysisinformation-gathering+4
1752 years ago
cisco_asa_research preview

cisco_asa_research

GitHubjbaines-r7/cisco_asa_research

Cisco ASA Software and ASDM Security Research
exploitationexploit-frameworksinformation-gathering+7
884 years ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
defensive-toolsdynamic-analysis-sandboxingforensics+7
586 days ago
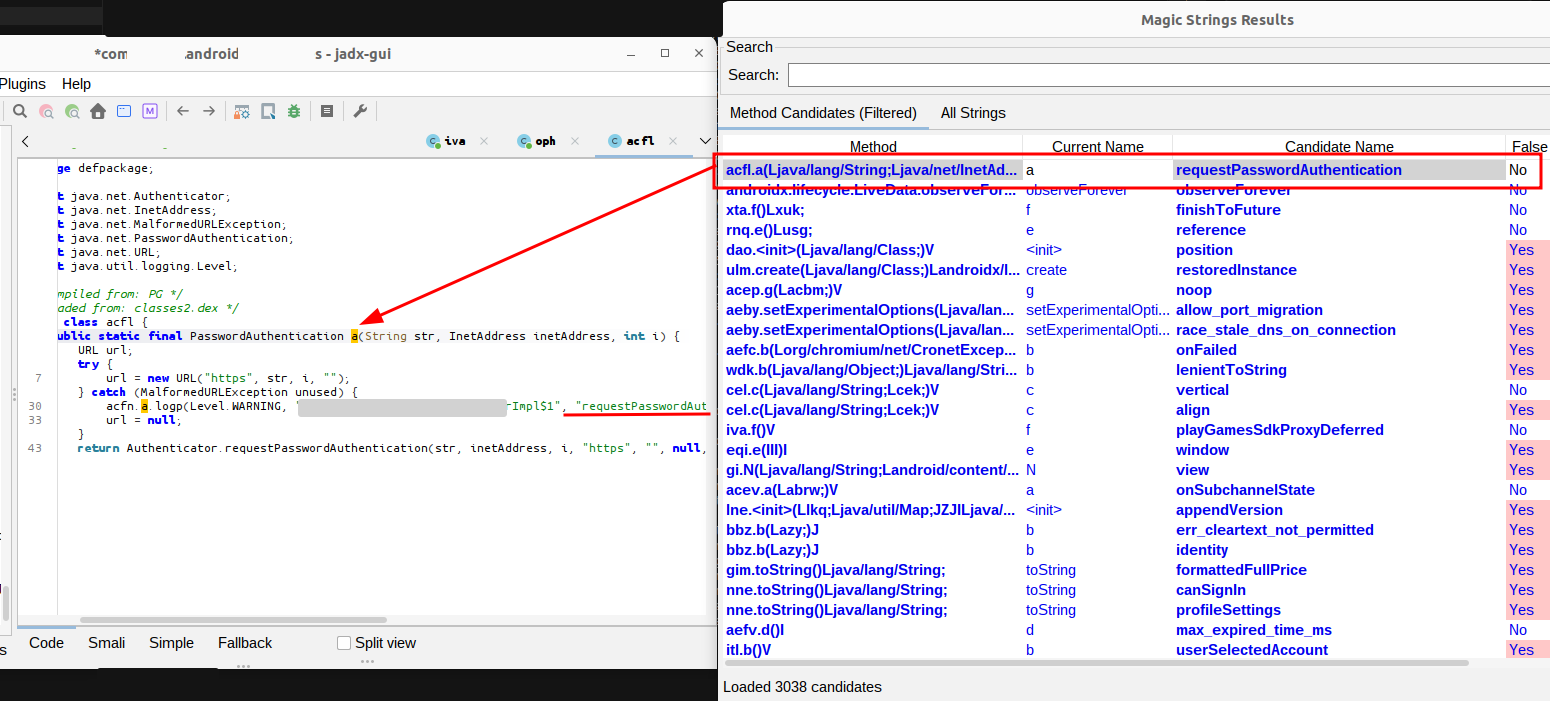
jadx-magic-strings preview

jadx-magic-strings

GitHub0rshemesh/jadx-magic-strings

JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
android-securitybinary-analysiscode-analysis+5
4519 days ago
subparse preview

subparse

GitHubjstrosch/subparse

Modular malware analysis artifact collection and correlation framework

dynamic-analysis-sandboxingforensicsinformation-gathering+3
562 years ago
Neton preview

Neton

GitHubaetsu/neton

Agent-based tool that collects OS, hardware, file, and hook data from internet-connected sandboxes via HTTPS exfiltration, aiding Red Team artifact…
educationinformation-gatheringmalware-analysis+1
1003 years ago
zettelforge preview

zettelforge

GitHubthreatrecall/zettelforge

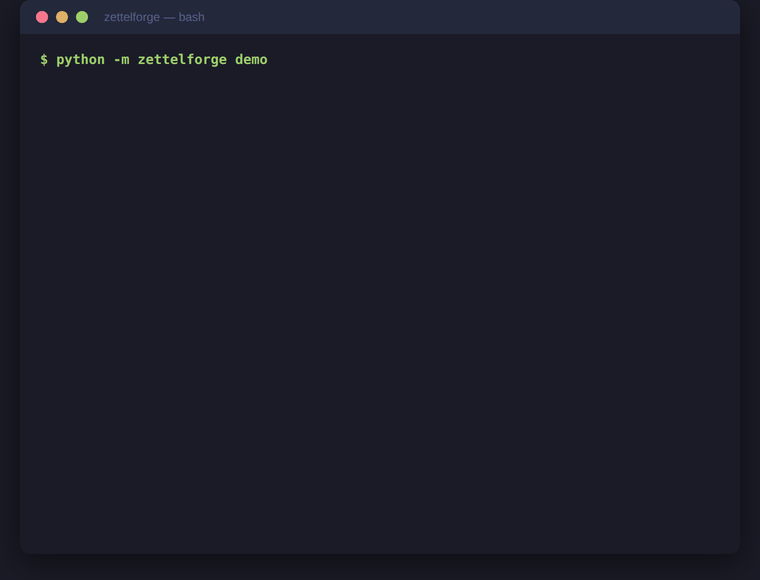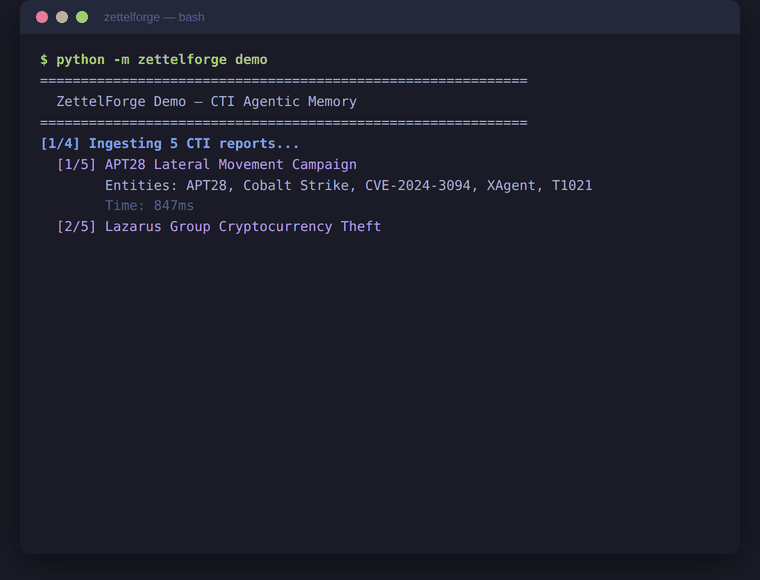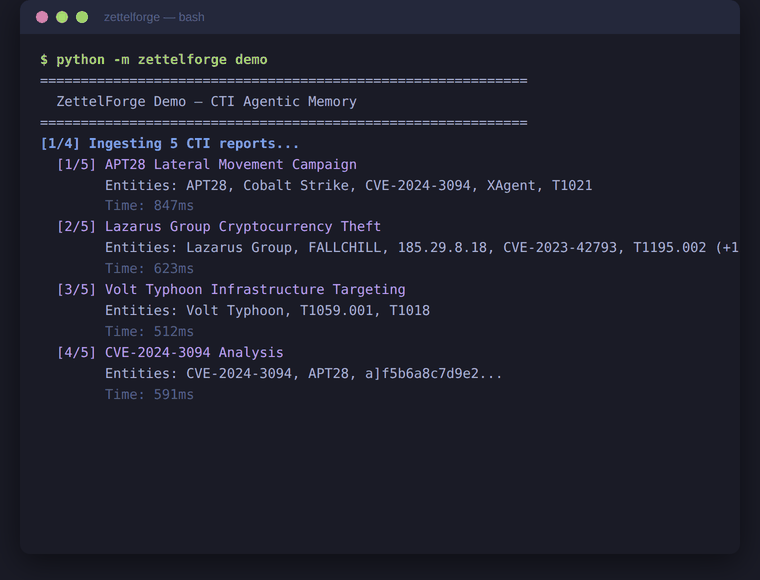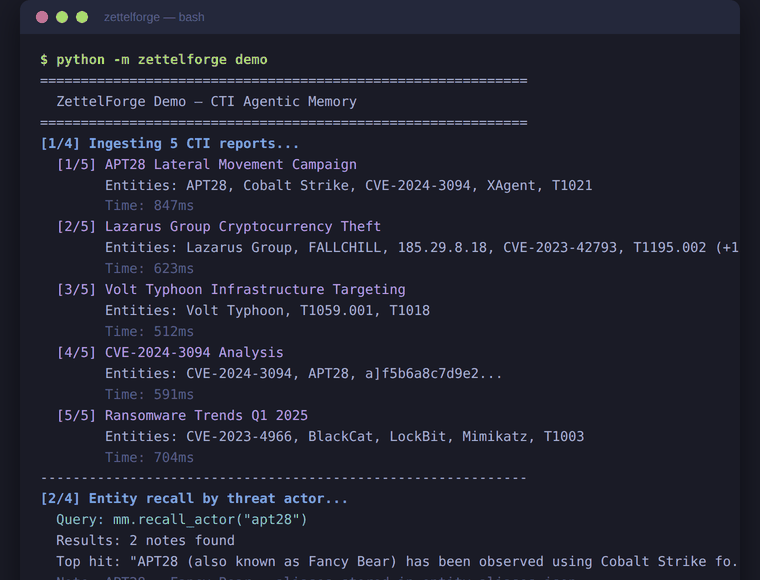
Agentic memory for CTI in Python — STIX knowledge graphs, threat-actor alias resolution, offline-first RAG, MCP server for Claude Code and LangChain…

ai-securityeducationforensics+8
632 months ago
Previous1…456…8Next