
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
90 results
VMDragonSlayer preview

VMDragonSlayer

GitHubpoppopjmp/vmdragonslayer

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
431
1 year ago
memhunter preview

memhunter

GitHubmarcosd4h/memhunter

Live hunting of code injection techniques
defensive-toolsincident-responsemalware-analysis+1
3847 years ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
digital-forensicsdynamic-analysis-sandboxingforensics+8
3202 years ago
VMUnprotect.Dumper preview

VMUnprotect.Dumper

GitHubvoid-stack/vmunprotect.dumper

VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
binary-analysisdynamic-code-analysismalware-analysis+1
4594 years ago
OpenPetya preview

OpenPetya

GitHubiss4cf0ng/openpetya

A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
binary-exploitationcryptographyeducation+4
2601 month ago
telnet-iot-honeypot preview

telnet-iot-honeypot

GitHubphype/telnet-iot-honeypot

Python telnet honeypot for catching botnet binaries

iot-securitymalware-analysisnetwork-security+1
3144 years ago
NovaLdr preview

NovaLdr

GitHubblacksnufkin/novaldr

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
code-analysiseducationexploitation+7
2672 years ago
TiEtwAgent preview

TiEtwAgent

GitHubxuanxuan0/tietwagent

PoC memory injection detection agent based on ETW, for offensive and defensive research purposes

defensive-toolseducationmalware-analysis+1
3005 years ago
themida-devirt preview

themida-devirt

GitHubbackengineering/themida-devirt

Themida Devirt Results
binary-analysisdebuggersfirmware-analysis+3
1125 months ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
binary-analysiseducationlabs-practice+6
1591 year ago
thematrix preview

thematrix

GitHubenkomio/thematrix

a PE Loader and Windows API tracer. Useful in malware analysis.

api-securitydebuggersdynamic-analysis-sandboxing+2
1434 years ago
Door404 preview

Door404

GitHubm4dm0e/door404

Web application backdoor builder

defensive-toolseducationexploitation+2
825 years ago
0xCr0ssCrush preview

0xCr0ssCrush

GitHubdeathshotxd/0xcr0sscrush

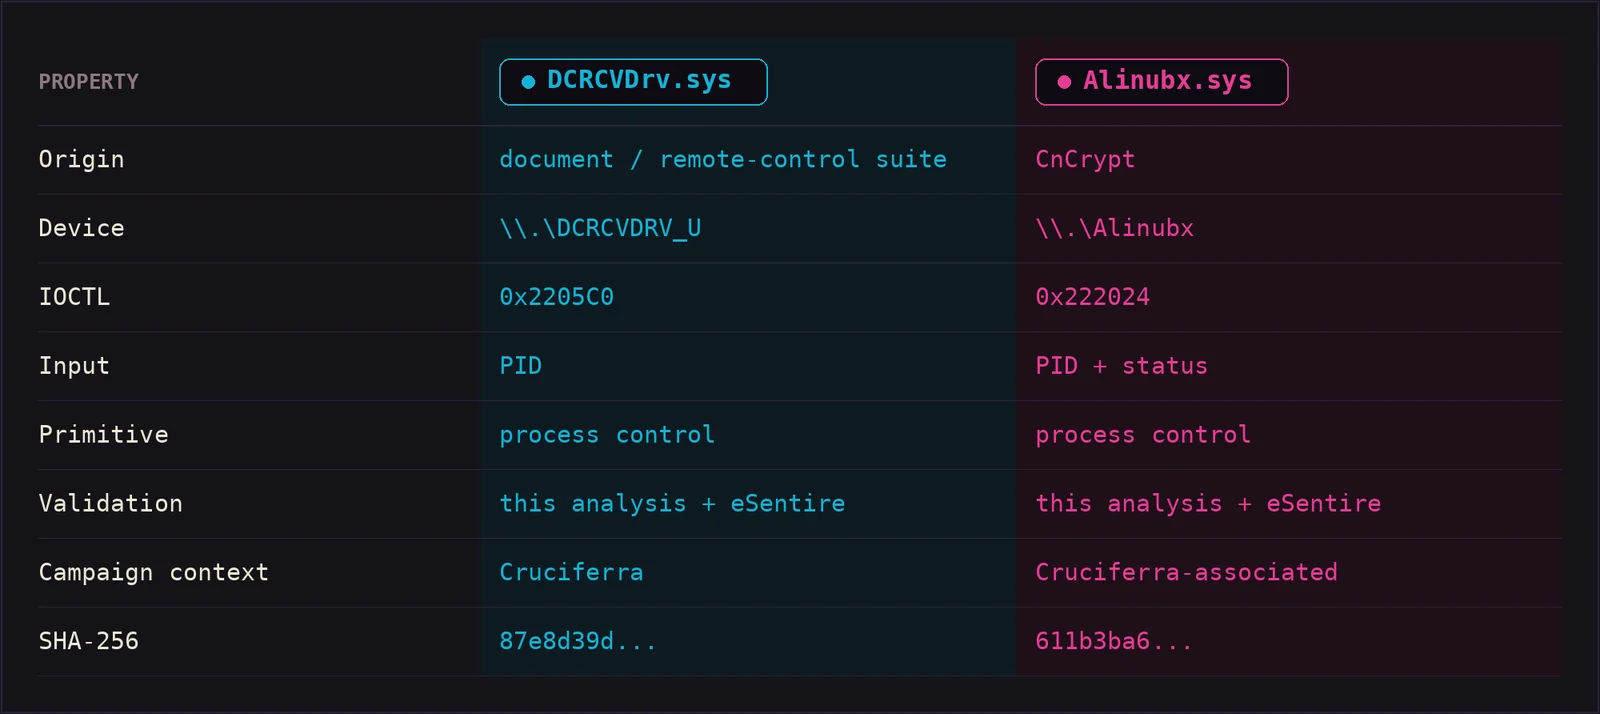
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
binary-analysisdefensive-toolsexploitation+4
389 days ago
Common-Registry preview

Common-Registry

GitHubeballoon/common-registry

Proof-of-concept C code demonstrating registry-based communication, PFN clearing, and custom process attachment techniques for stealthy payload…
malware-analysispayload-developmentpersistence-mechanisms+2
484 years ago
project-rvbbit preview

project-rvbbit

GitHubbuter-chkalova/project-rvbbit

Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
defensive-toolseducationmalware-analysis+3
321 month ago
icicle-python preview

icicle-python

GitHubicicle-emu/icicle-python

Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
binary-analysisdebuggersdynamic-analysis-sandboxing+5
431 year ago
TinyProcessor preview

TinyProcessor

GitHubgoatmilkkk/tinyprocessor

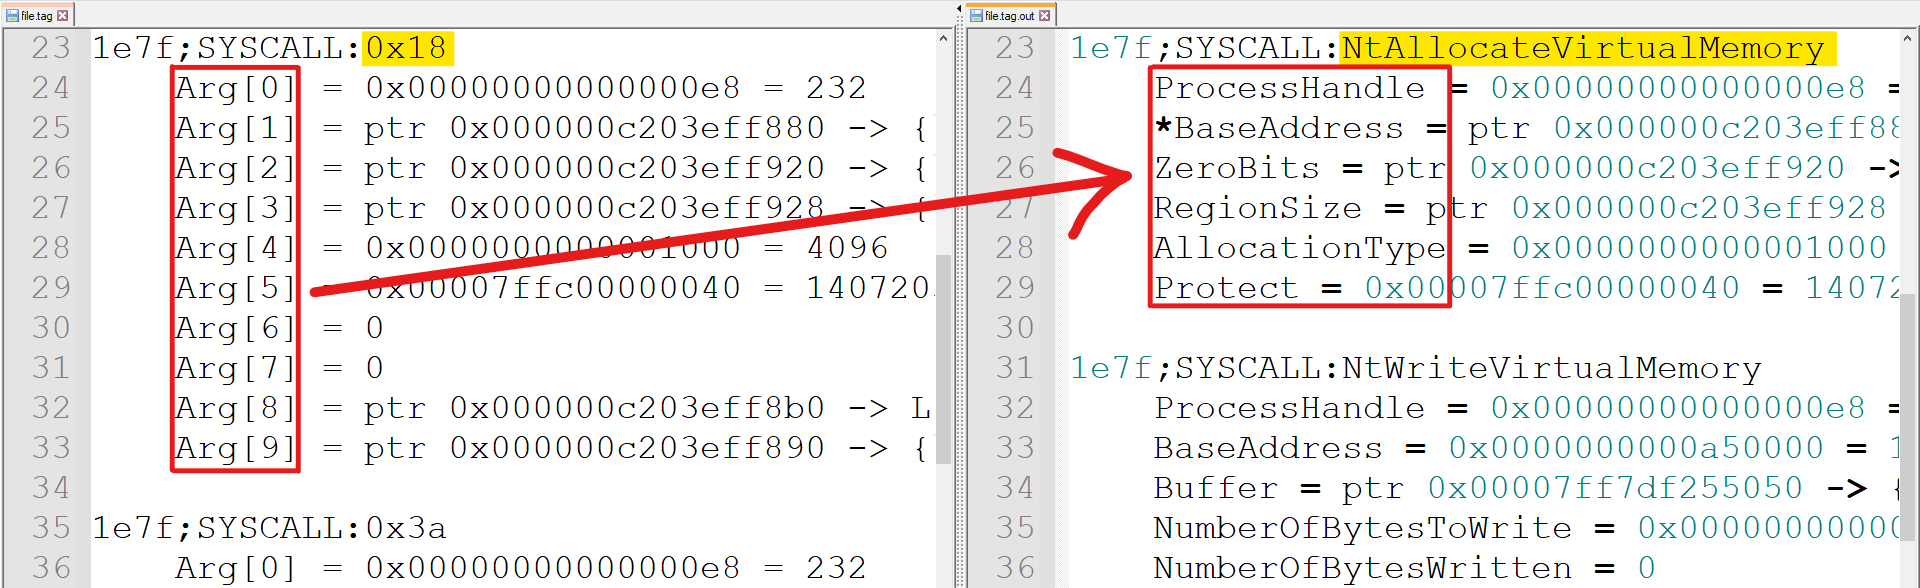
A post-processing script for TinyTracer
log-analysismalware-analysisreverse-engineering
403 years ago
pesieve-go preview

pesieve-go

GitHubhasherezade/pesieve-go

Golang bindings for PE-sieve

binary-analysisdynamic-code-analysismalware-analysis+1
432 years ago
Previous12345Next