
droidbox
 pjlantz/droidbox
Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
android-securitydynamic-analysis-sandboxinginformation-gathering+2
806
pjlantz/droidboxDynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
 decaf-project/decaf
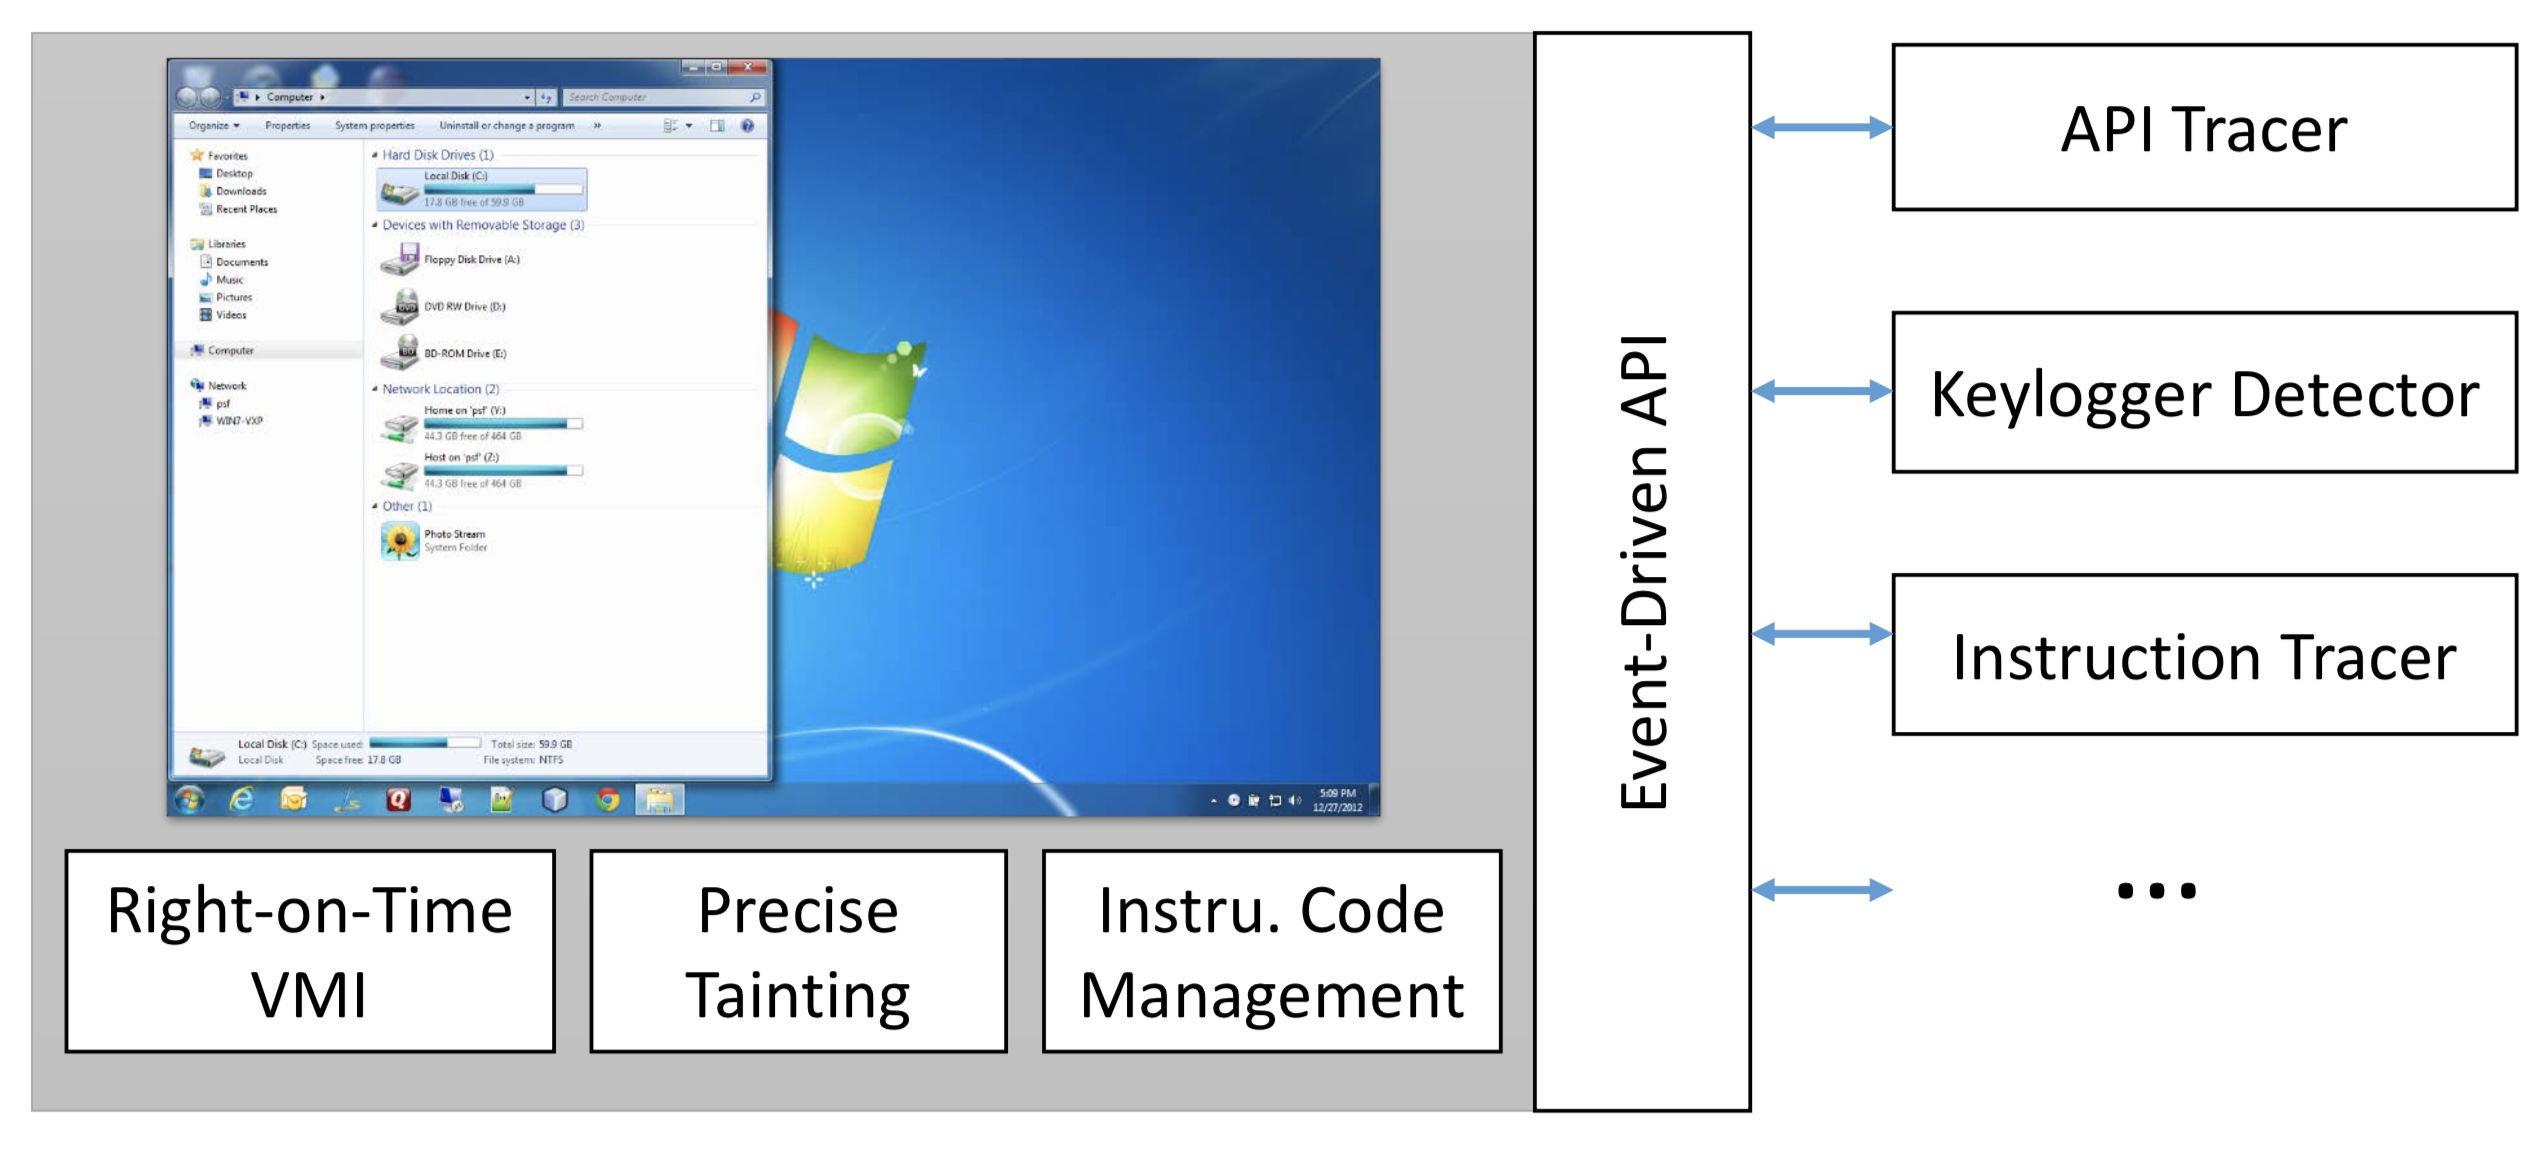
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 calebfenton/dex-oracle
A pattern based Dalvik deobfuscator which uses limited execution to improve semantic analysis
 cryptax/droidlysis
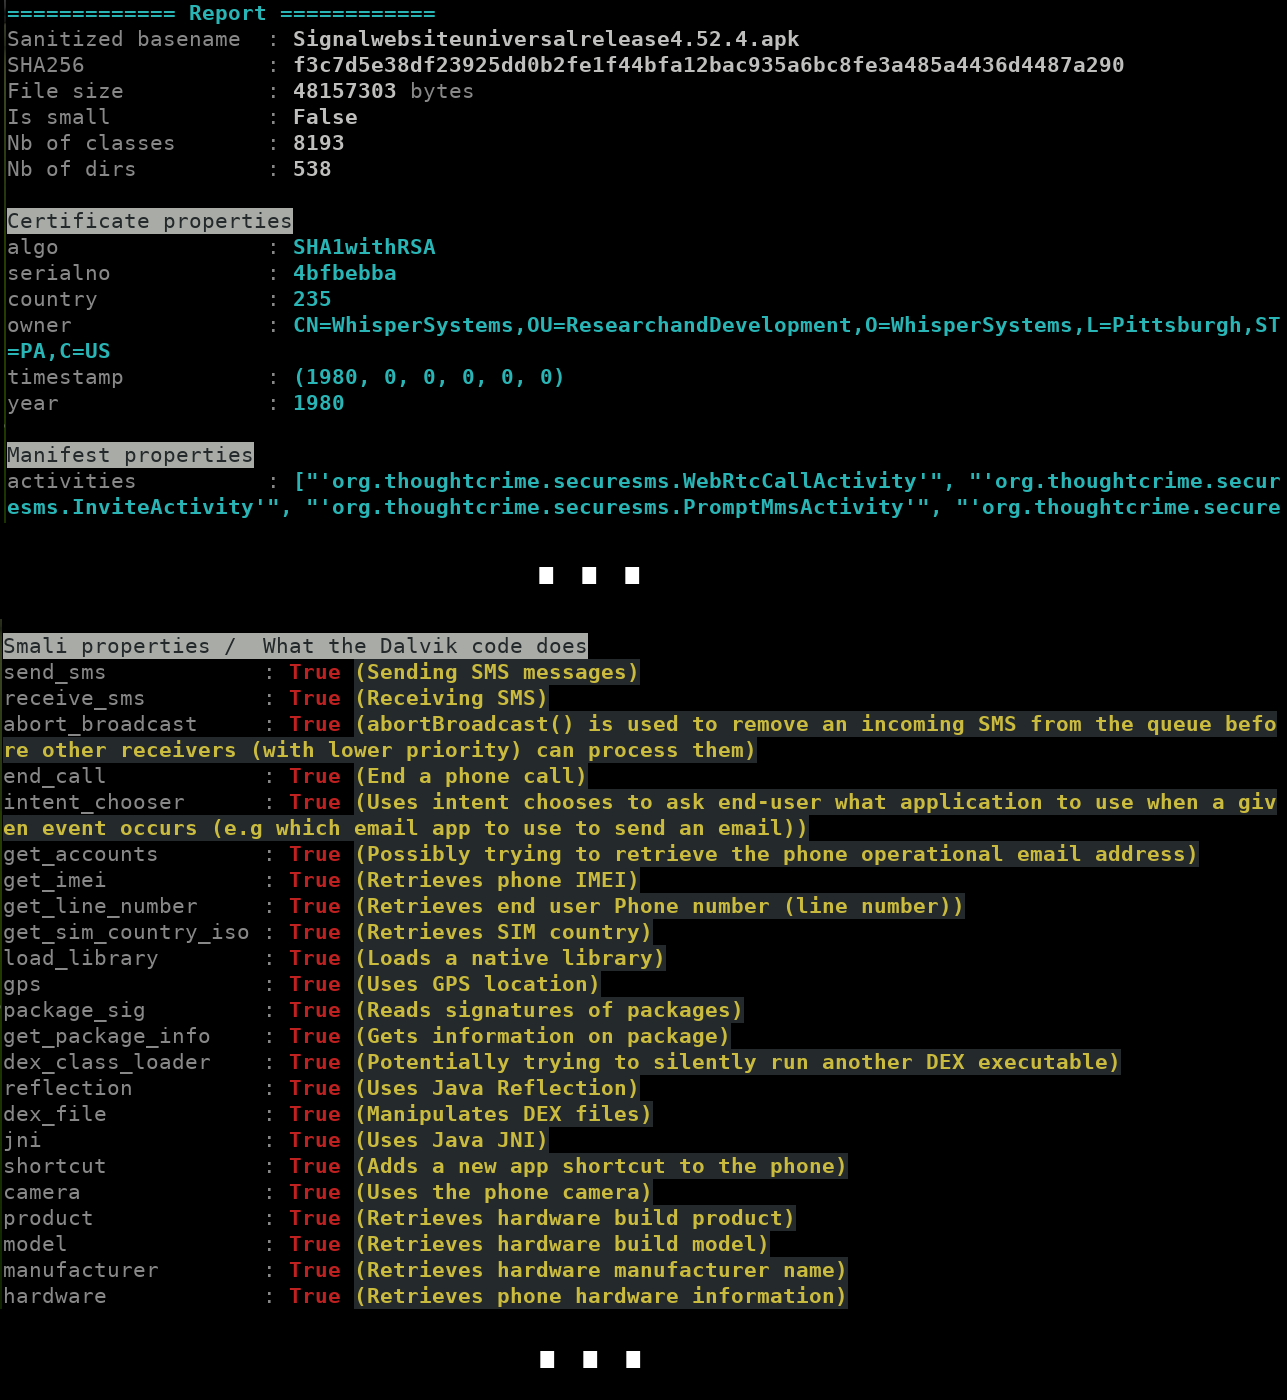
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 sslab-gatech/avpass
Tool for leaking and bypassing Android malware detection system
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
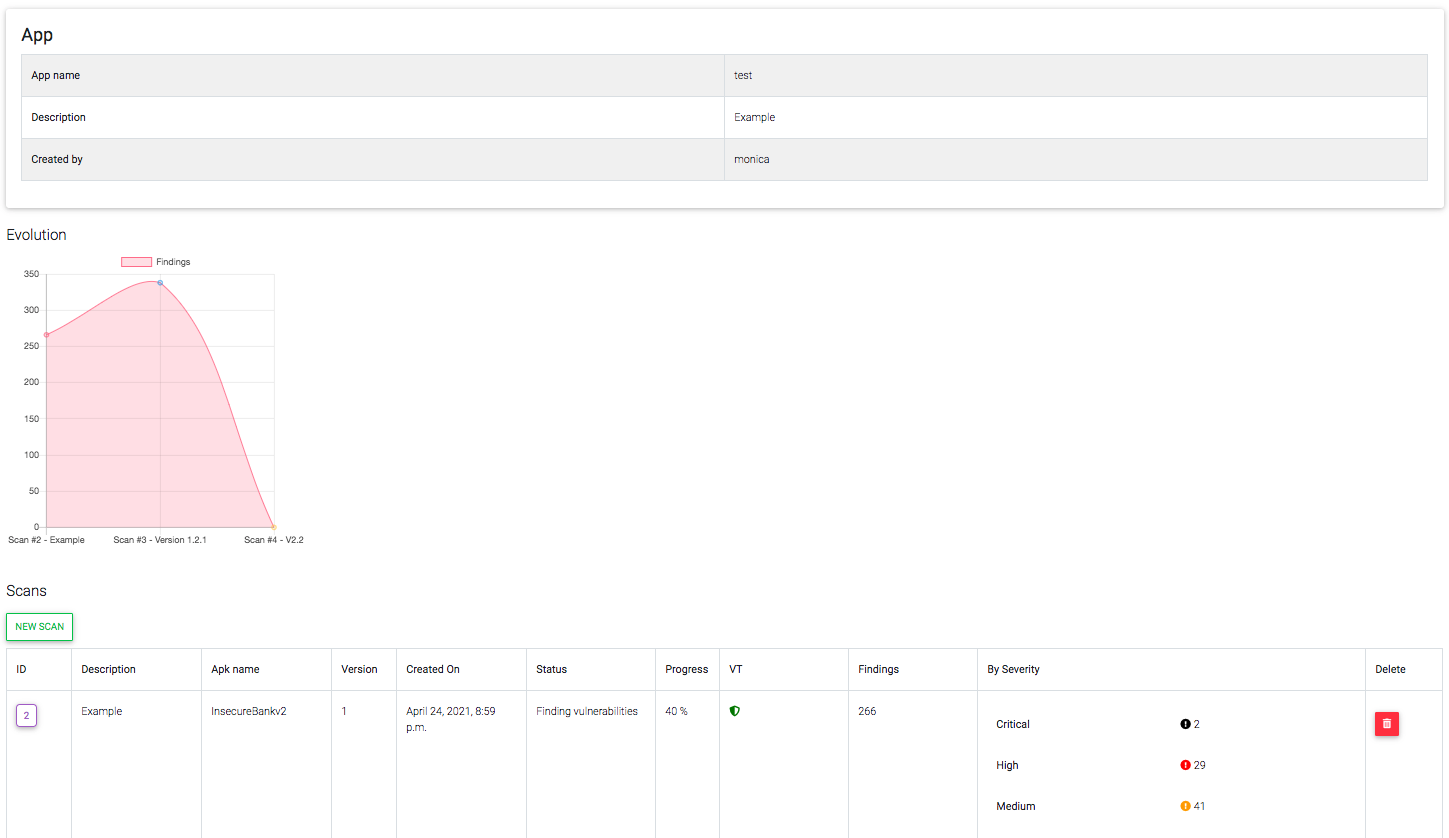 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 maddiestone/conpresentations
Slide decks from my conference presentations
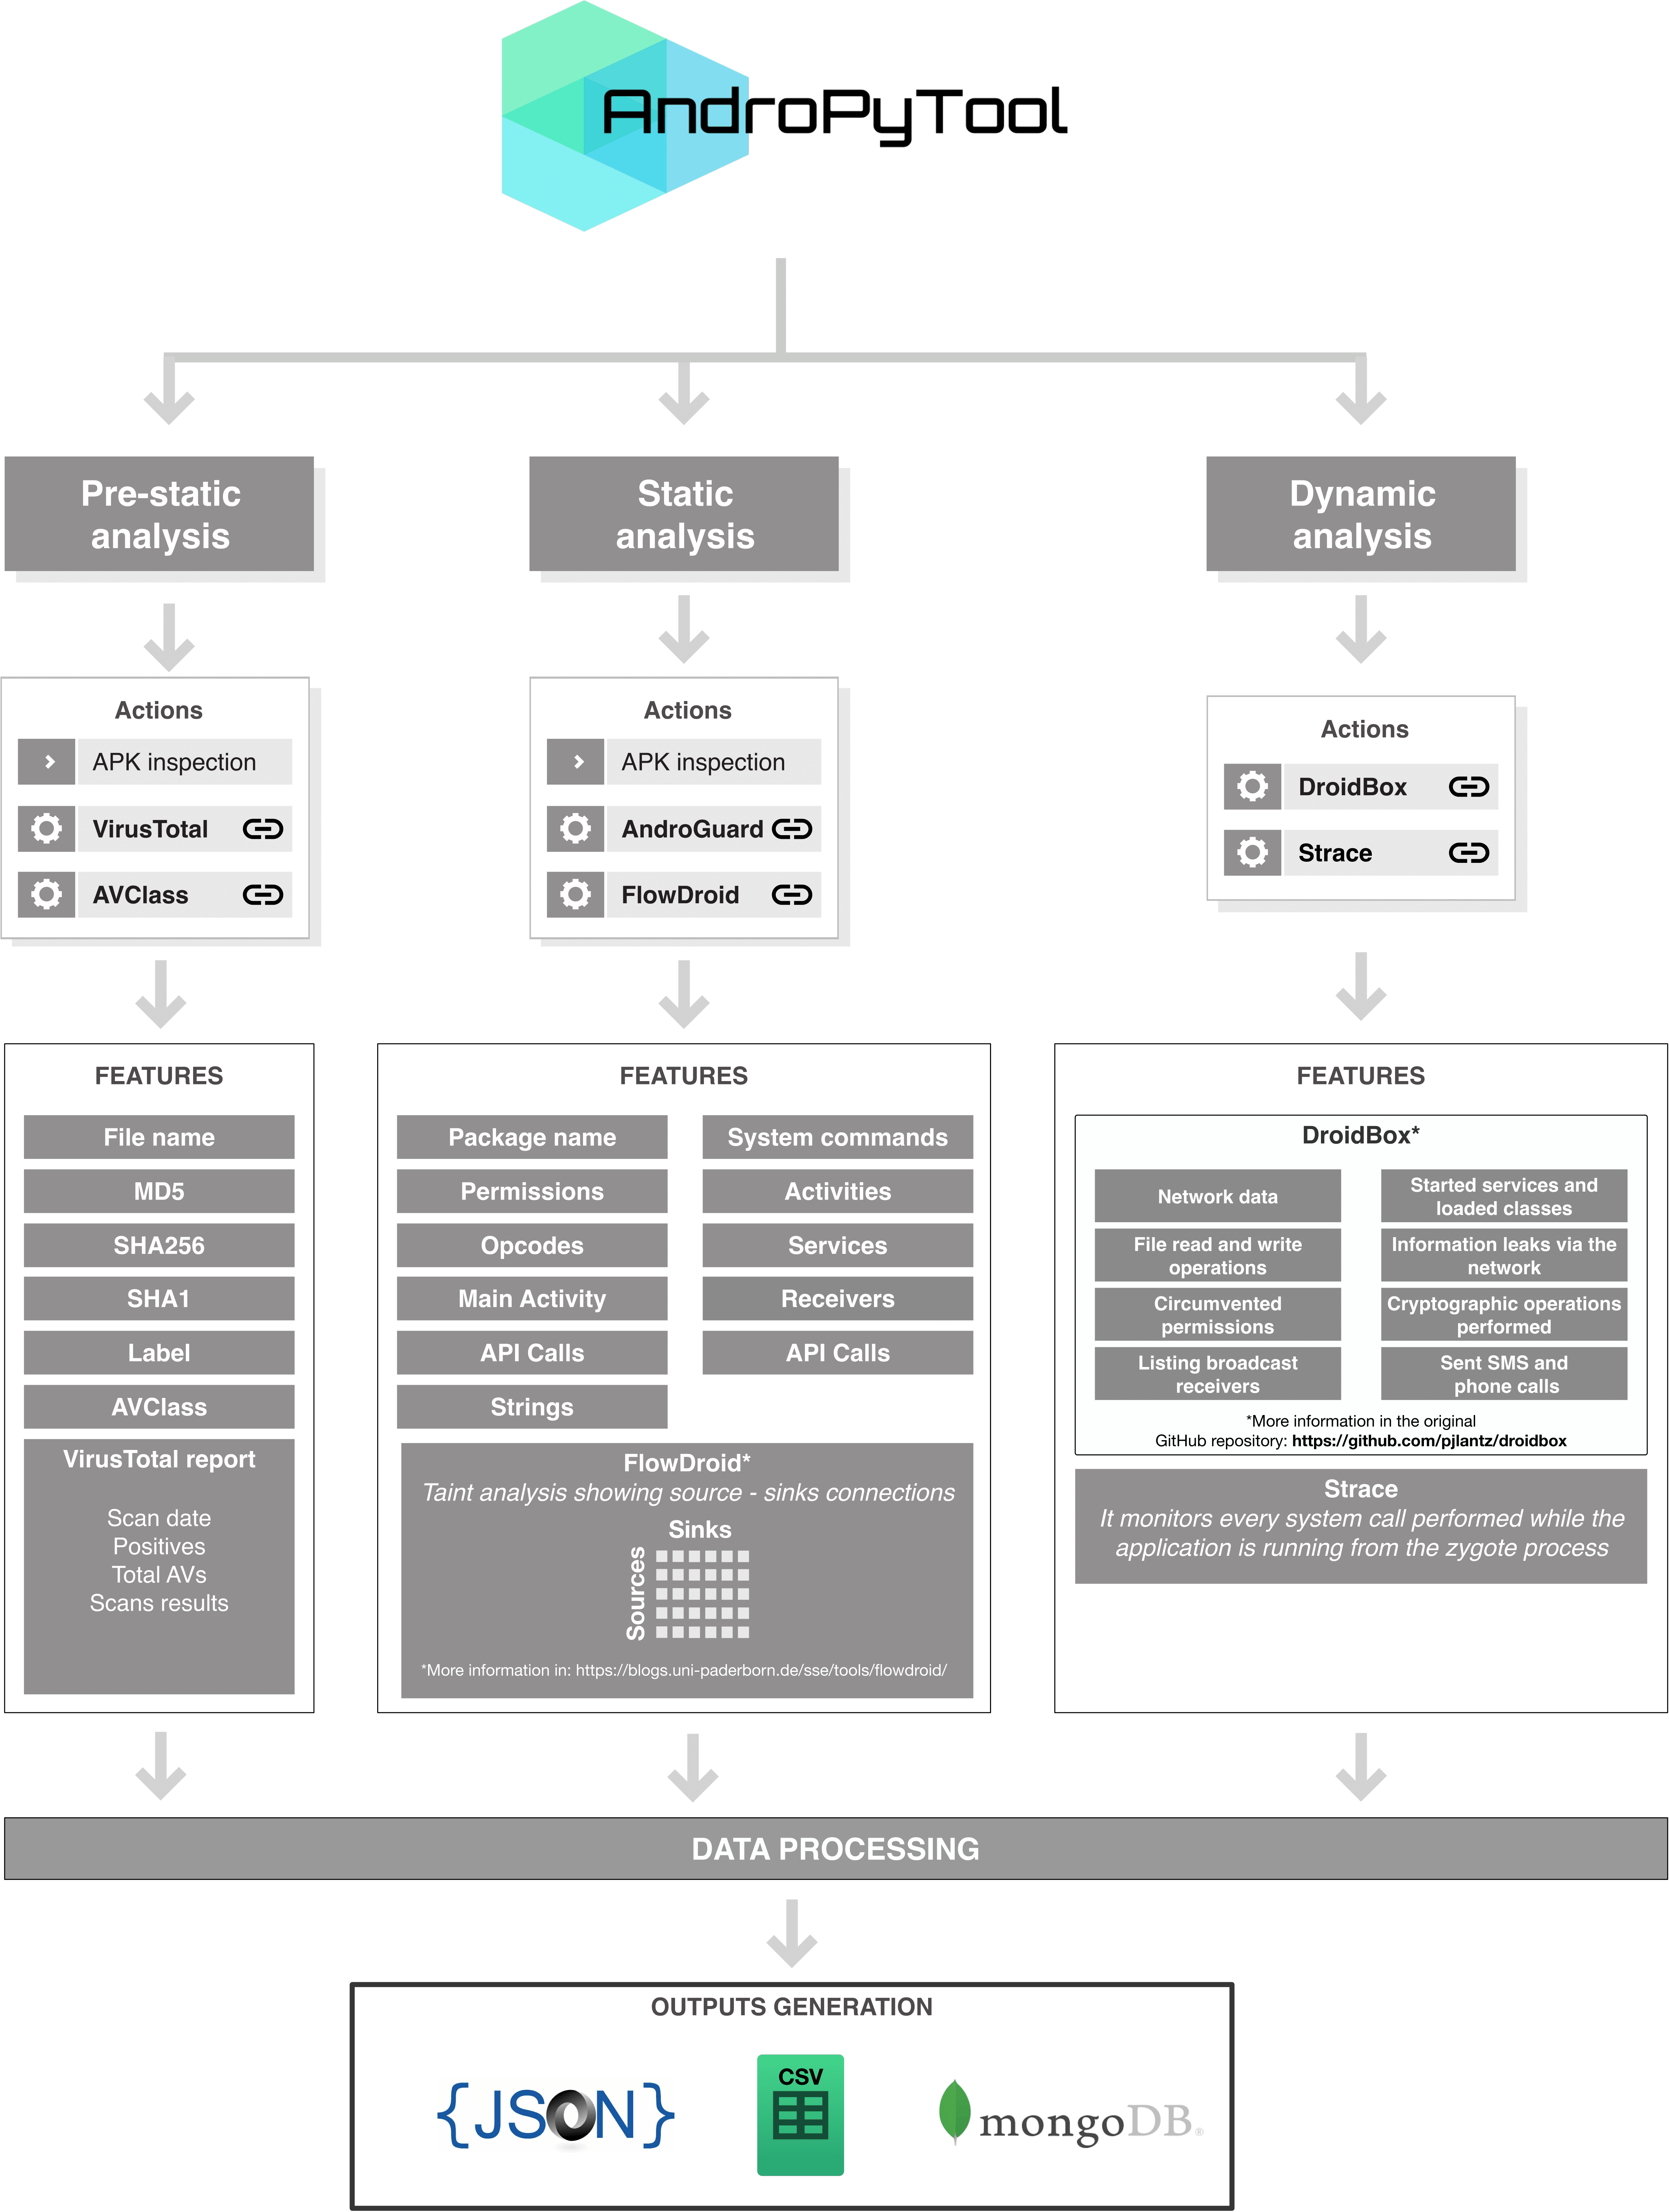 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 stefan2200/aparoid
Static and dynamic Android application security analysis
 mirsamantajbakhsh/livehiddencamera
Live Hidden Camera is a library which record live video and audio from Android device without displaying a preview.