
vbSparkle
 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
code-analysisdefensive-toolsmalware-analysis+2
82
airbus-cert/vbsparkleVBScript & VBA source-to-source deobfuscator with partial-evaluation
 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
 andrewaeva/dga
The repository that contains the algorithms for generating domain names, dictionaries of malicious domain names. Developed to research the…
 gherardofiori/maliciousbrowserextensions
This Repository is created after my own research into malicious browser extensions, by brining the work of many others and news articles into one…
 nccgroup/mimikatz-detector-busylight
USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 blunden/unacev2.dll-cve-2018-20250
A version of the binary patched to address CVE-2018-20250
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 emirkmo/xz-backdoor-github
History of commits related to the xz backdoor Discovered On March 29, 2024: CVE-2024-3094.
 ytisf/thezoo
Curated repository of live malware samples and source code for educational malware analysis and research, with an organized database and CLI tools…
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 dhmosfunk/7-zip-cve-2025-0411-poc
This repository contains POC scenarios as part of CVE-2025-0411 MotW bypass.
 cesarbtakeda/7-zip-cve-2025-0411-poc
Proof-of-concept exploit for CVE-2025-0411, demonstrating Mark-of-the-Web bypass in 7-Zip to enable arbitrary code execution via crafted archives…
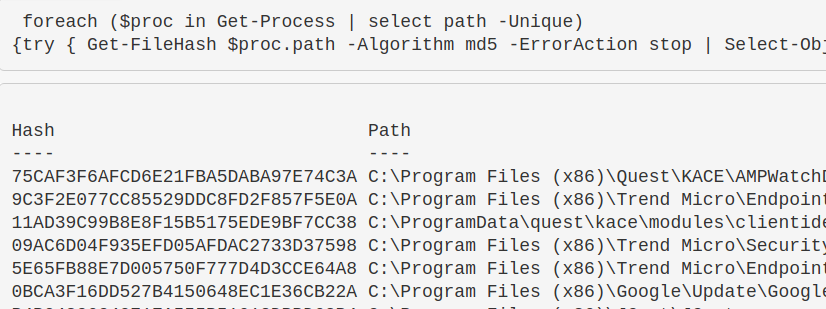 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 chvancooten/maldev-for-dummies
A workshop about Malware Development
 idanr1986/cuckoo-droid
CuckooDroid - Automated Android Malware Analysis with Cuckoo Sandbox.
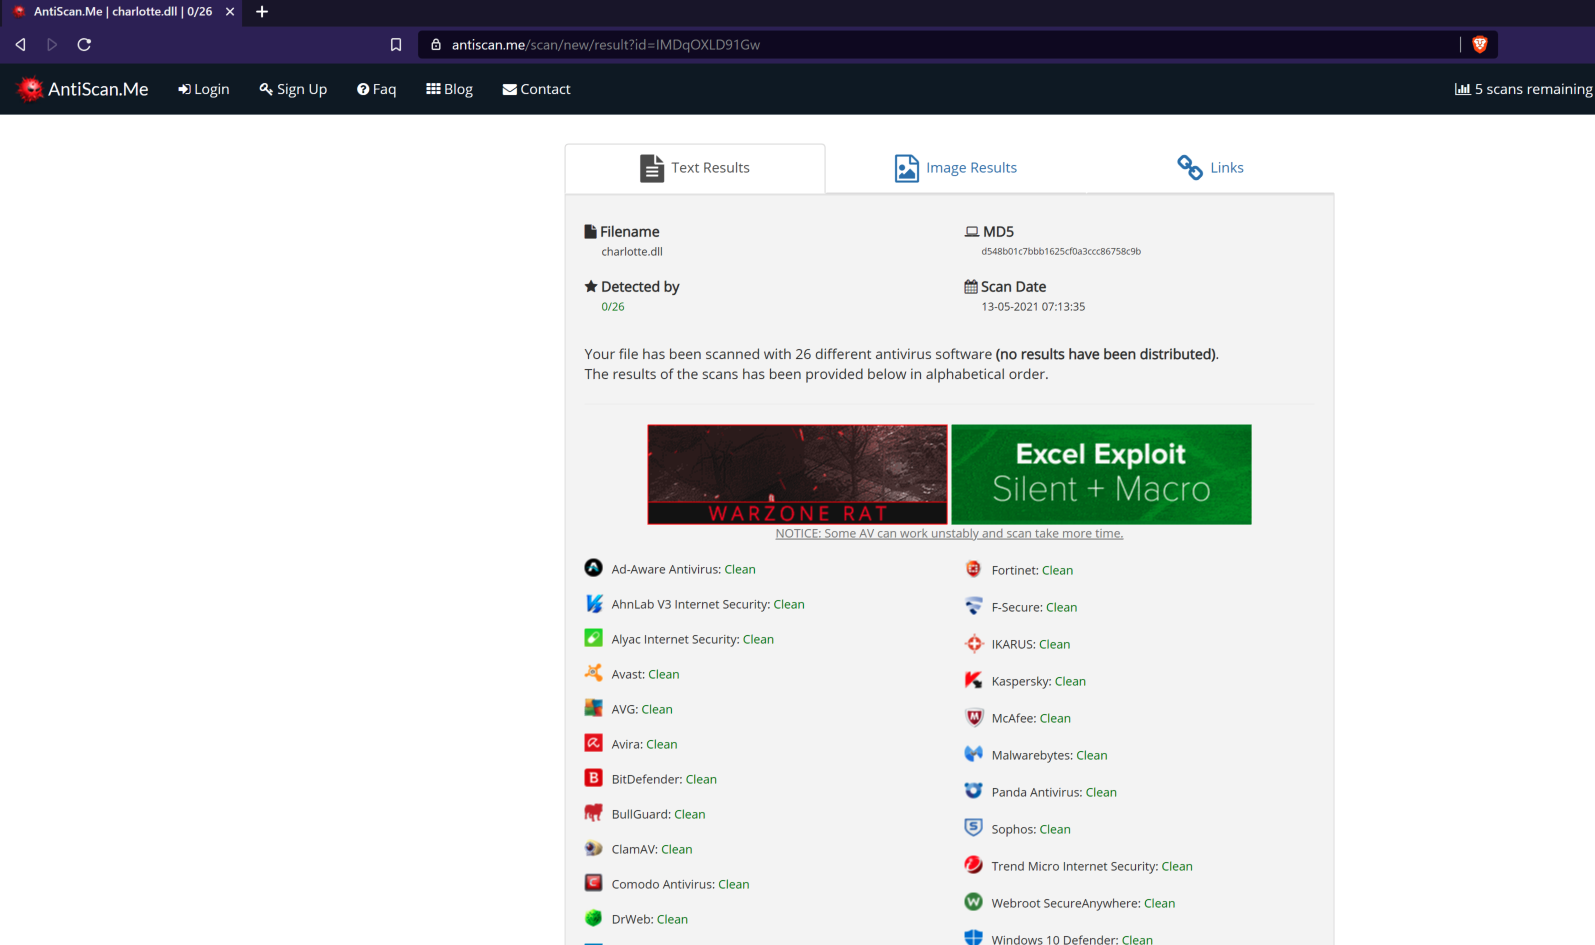 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
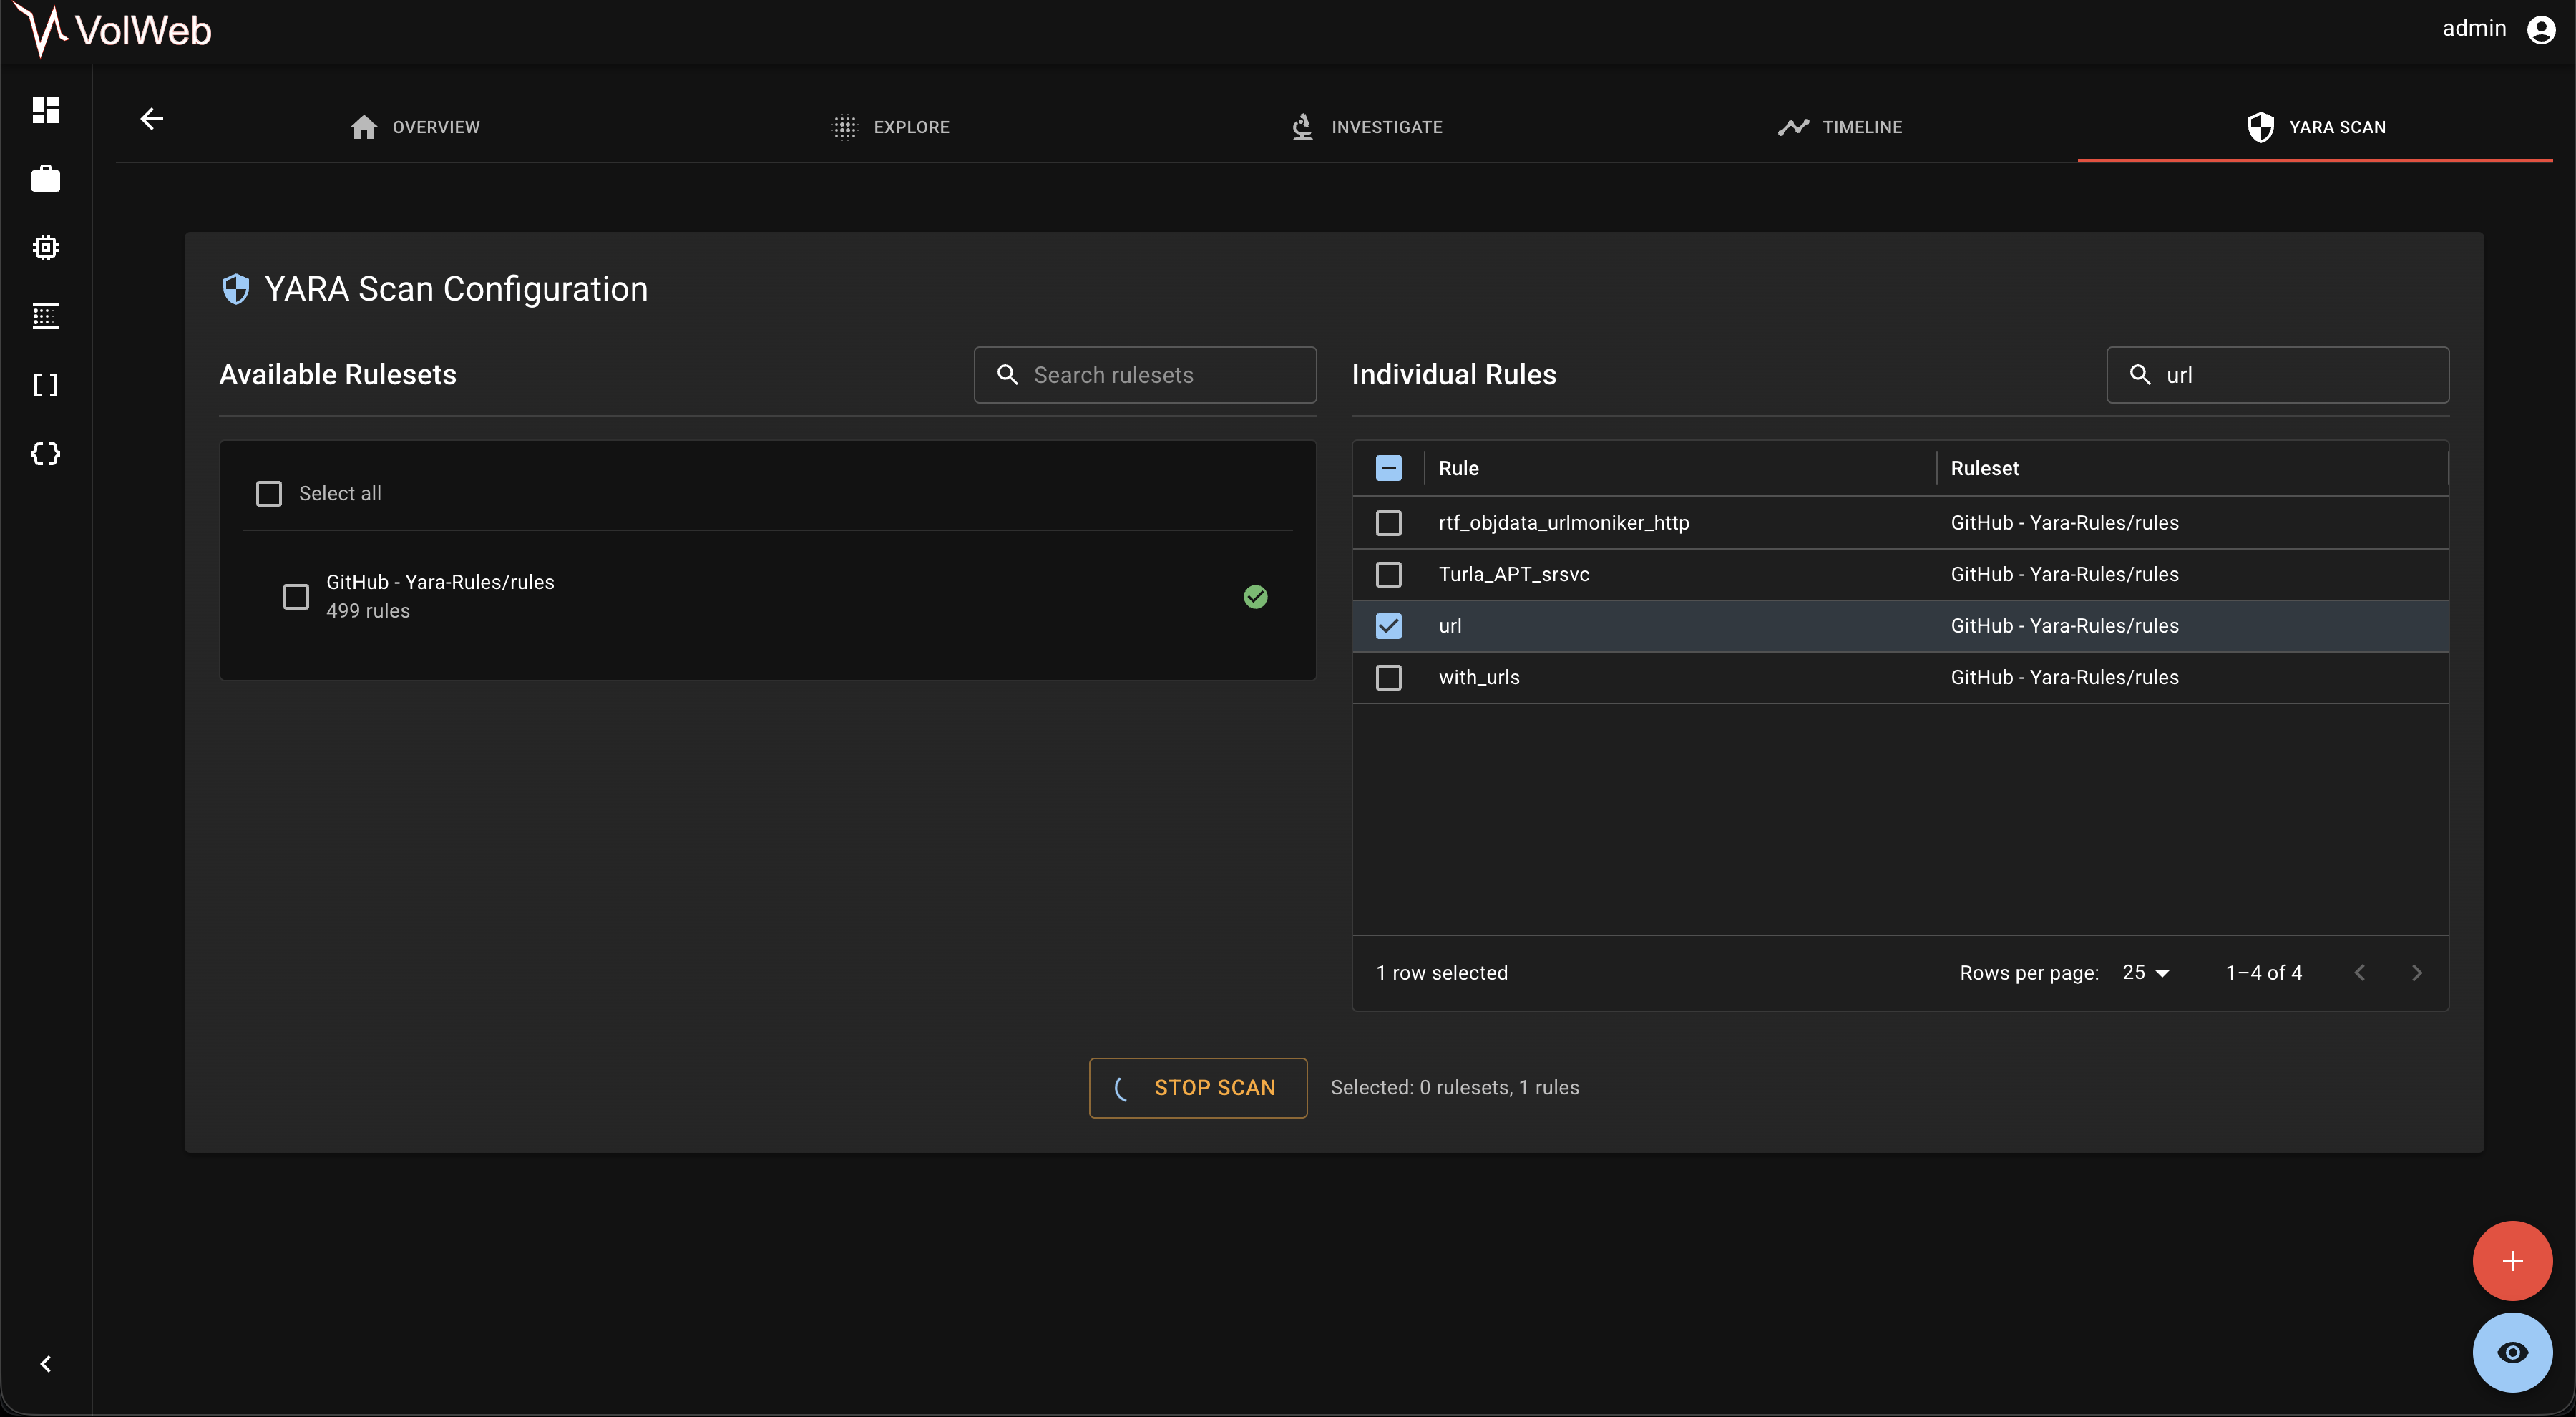 k1nd0ne/volweb
A centralized and enhanced memory analysis platform