
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
274 results
WDExtract preview

WDExtract

GitHubhfiref0x/wdextract

Extract Windows Defender database from vdm files and unpack it

binary-analysisencryption-decryption-toolsforensics+2
4906 months ago
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
anti-botbinary-analysisdefensive-tools+4
3531 month ago
mkPIVM preview

mkPIVM

GitHubd7ead/mkpivm

Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.

exploitationmalware-analysispayload-generation+3
4092 months ago
Vba2Graph preview

Vba2Graph

GitHubmalwarecantfly/vba2graph

Vba2Graph - Generate call graphs from VBA code, for easier analysis of malicious documents.
code-analysismalware-analysisreverse-engineering+1
2836 years ago
MemoryModulePP preview

MemoryModulePP

GitHubstrivexjun/memorymodulepp

C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…

binary-analysisexploitationmalware-analysis+2
2256 years ago
bluepot preview

bluepot

GitHubandrewmichaelsmith/bluepot

Java-based Bluetooth honeypot that captures and stores malware from BlueBugging and BlueSnarfing attacks, with a GUI for monitoring and log analysis.
bluetooth-securitydefensive-toolsinformation-gathering+1
2777 months ago
AndroPyTool preview

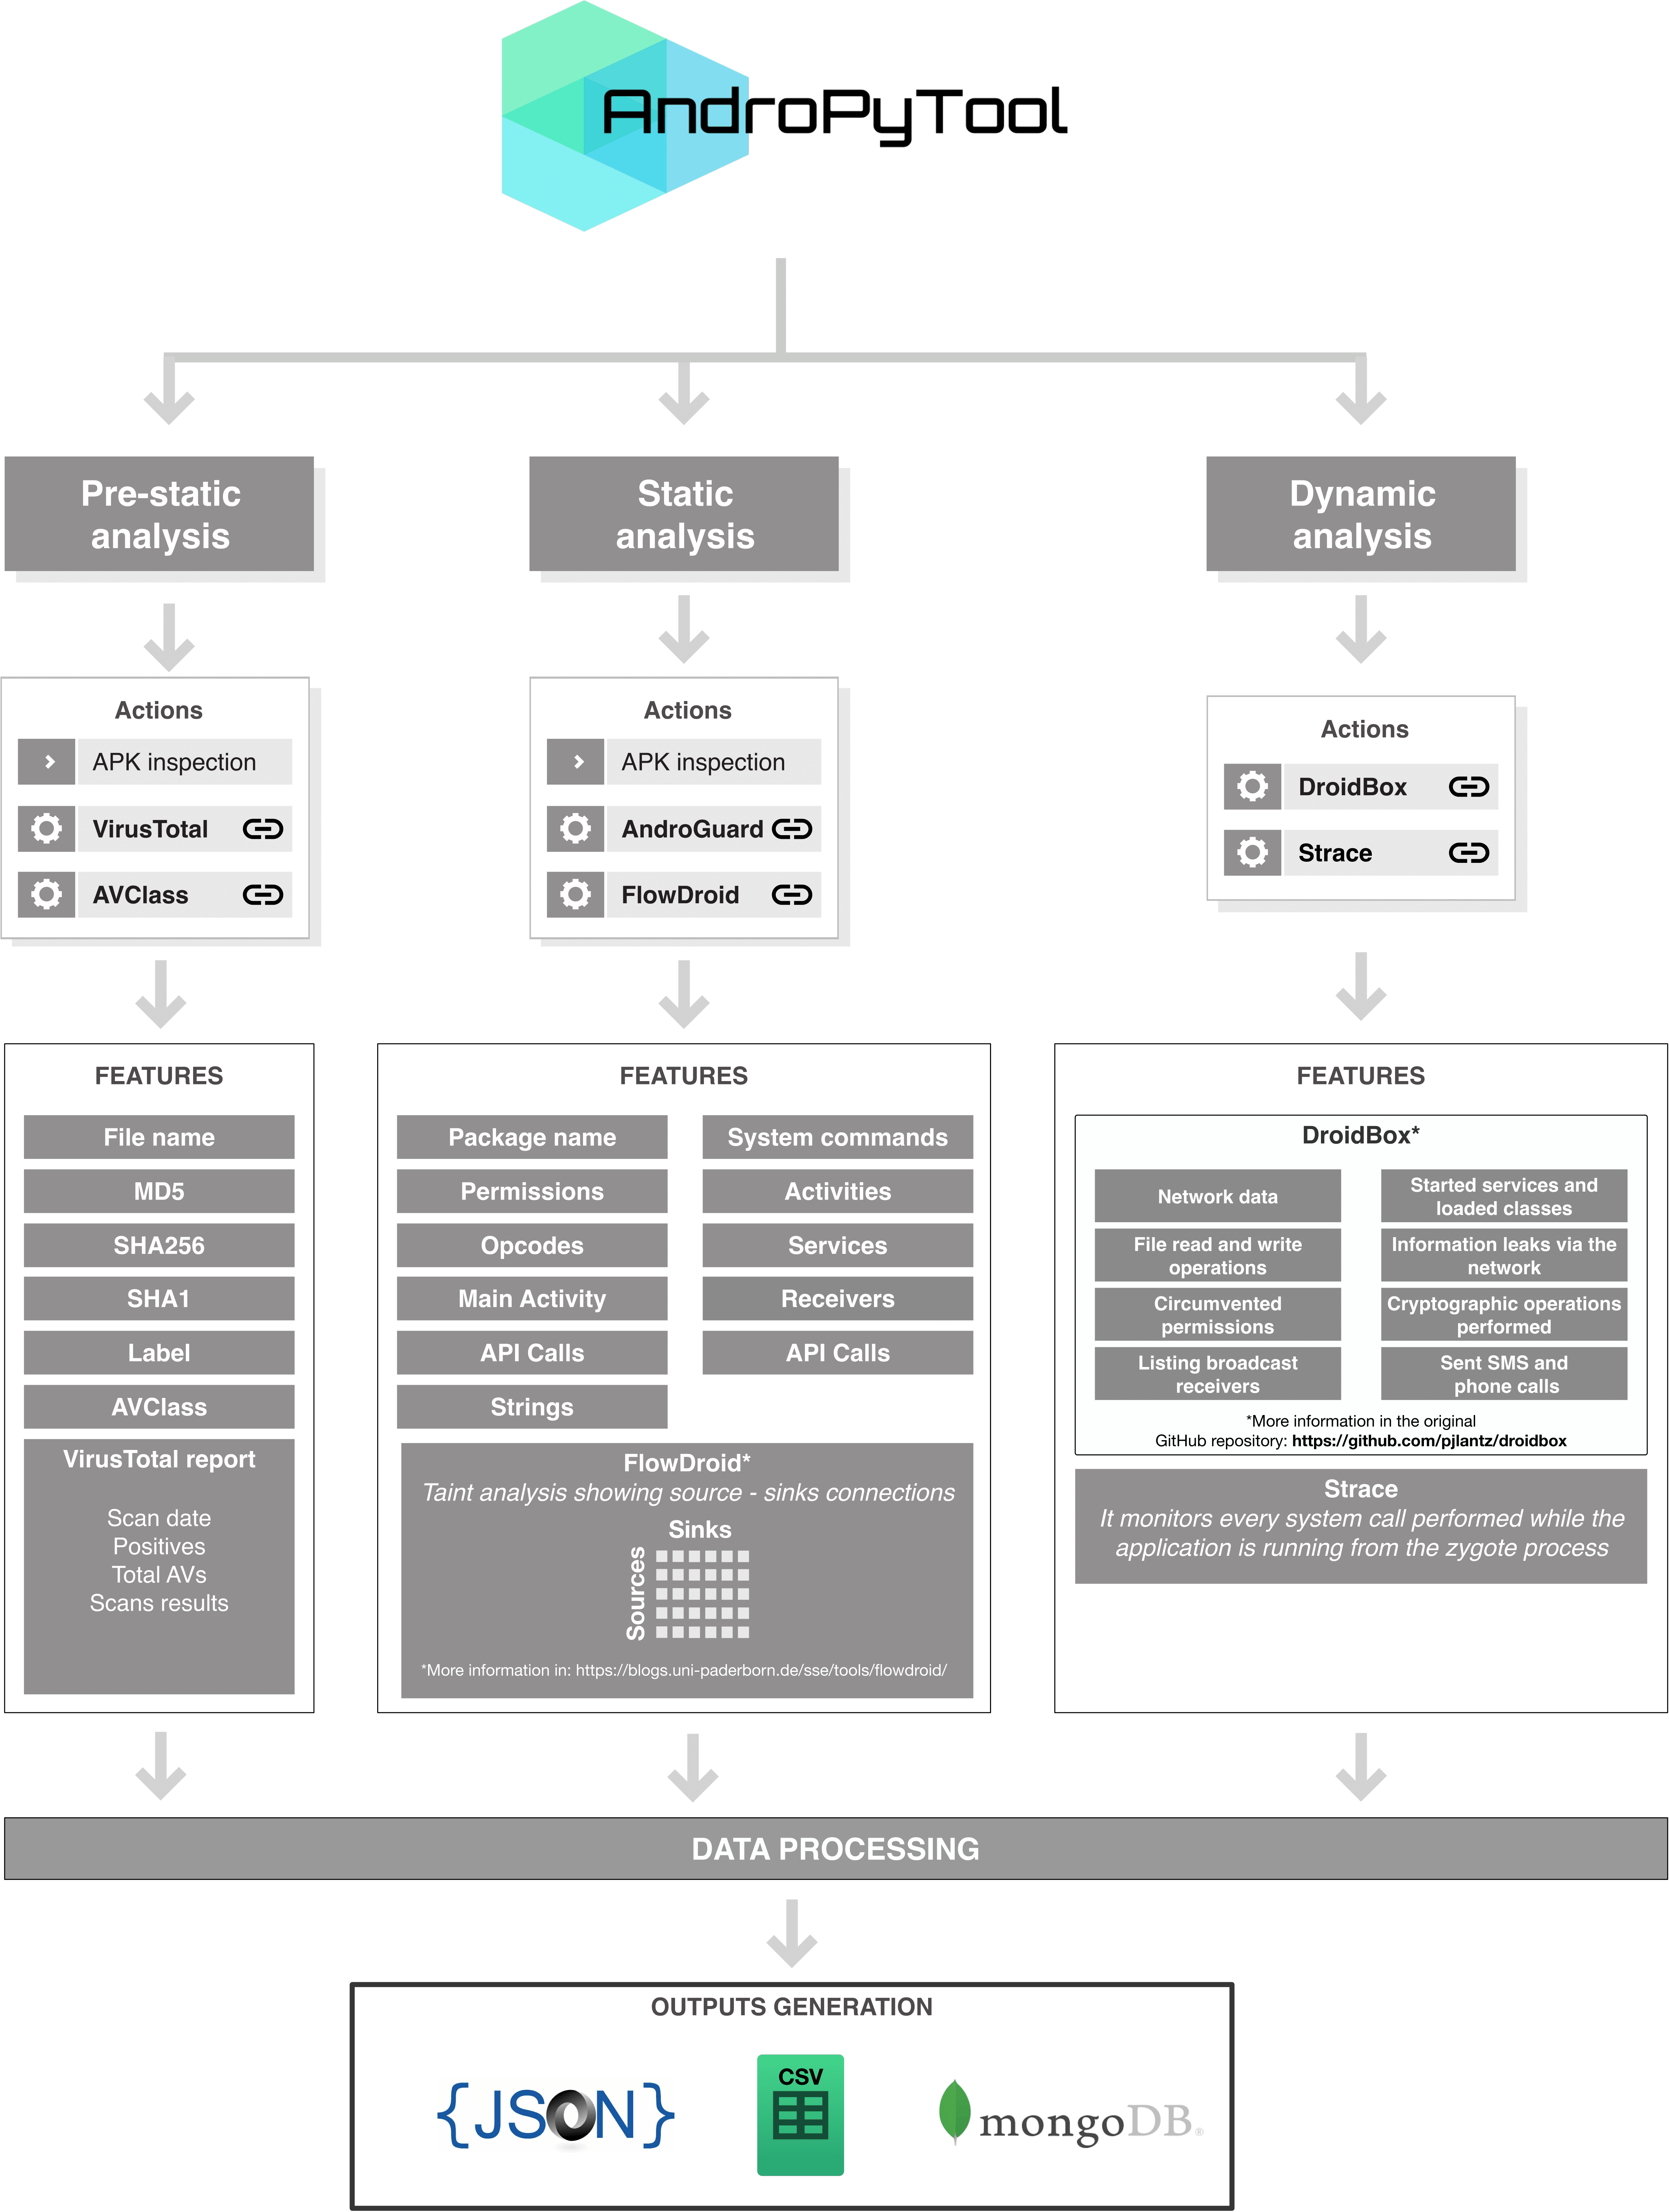
AndroPyTool

GitHubalexmyg/andropytool

A framework for automated extraction of static and dynamic features from Android applications
android-securitydynamic-analysis-sandboxingmalware-analysis+2
3816 years ago
Nim-RunPE preview

Nim-RunPE

GitHubs3cur3th1ssh1t/nim-runpe

A Nim implementation of reflective PE-Loading from memory
binary-exploitationexploitationmalware-analysis+3
2952 years ago
DGA preview

DGA

GitHub360netlab/dga

Suspicious DGA from PDNS and Sandbox.

dns-analysisinformation-gatheringioc-management+3
1884 years ago
sigma-rules preview

sigma-rules

GitHubjoesecurity/sigma-rules

Sigma rules from Joe Security
curated-resourcesdefensive-toolsintrusion-detection+3
2412 years ago
jsunpack-n preview

jsunpack-n

GitHuburule99/jsunpack-n

Automatically exported from code.google.com/p/jsunpack-n
dynamic-analysis-sandboxingmalware-analysisweb-security
16911 years ago
arya preview

arya

GitHubclaroty/arya

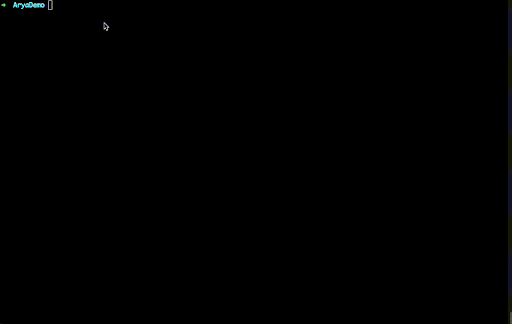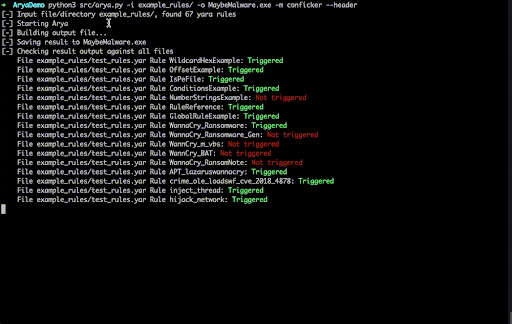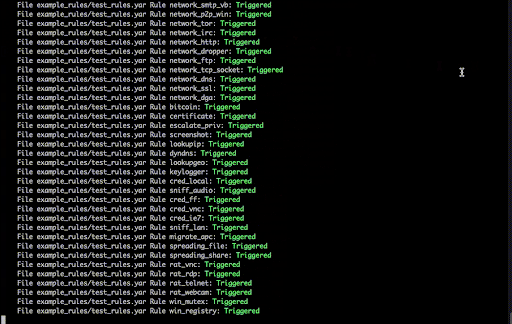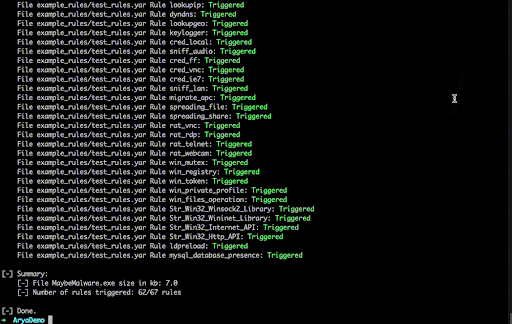
Generates pseudo-malicious files from YARA rules to trigger AV/EDR detection, enabling malware research, rule QA, and network sensor pressure testing…

educationlabs-practicemalware-analysis+2
2613 years ago
Remote-Access-Trojan-Database preview

Remote-Access-Trojan-Database

GitHubrainkin1993/remote-access-trojan-database

A database of RAT collected from Internet
curated-resourceseducationforensics+3
1606 years ago
DetectWindowsCopyOnWriteForAPI preview

DetectWindowsCopyOnWriteForAPI

GitHubnccgroup/detectwindowscopyonwriteforapi

Enumerate various traits from Windows processes as an aid to threat hunting

anomaly-detectiondefensive-toolsforensics+3
2004 years ago
doublepulsar-usermode-injector preview

doublepulsar-usermode-injector

GitHubwithsecurelabs/doublepulsar-usermode-injector

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…

exploitationmalware-analysispayload-development+2
1249 years ago
kunglao-agent preview

kunglao-agent

GitHubamd2g2zz/kunglao-agent

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
ai-assisted-reversingandroid-securitybinary-analysis+8
7015h 48m ago
iocs preview

iocs

GitHubthreatlabz/iocs

This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
curated-resourcesincident-responseioc-management+4
796 days ago
maldrolyzer preview

maldrolyzer

GitHubmaldroid/maldrolyzer

Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)

android-securitycommand-and-controlinformation-gathering+3
11211 years ago
Previous1234…16Next