

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
125 results
speakeasy preview

speakeasy

GitHubmandiant/speakeasy

Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2.1k
3 days ago
RATDecoders preview

RATDecoders

GitHubkevthehermit/ratdecoders

Python Decoders for Common Remote Access Trojans
dynamic-analysis-sandboxingforensicsincident-response+6
1.1k5 years ago
python-exe-unpacker preview

python-exe-unpacker

GitHubwithsecurelabs/python-exe-unpacker

A helper script for unpacking and decompiling EXEs compiled from python code.
binary-analysisdynamic-analysis-sandboxingforensics+2
1.0k8 years ago
unlicense preview

unlicense

GitHubergrelet/unlicense

Dynamic unpacker and import fixer for Themida/WinLicense 2.x and 3.x.
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
1.5k3 years ago
USBvalve preview

USBvalve

GitHubcecio/usbvalve

Expose USB activity on the fly
dynamic-analysis-sandboxingembedded-systems-securityforensics+2
1.3k2 months ago
karton preview

karton

GitHubcert-polska/karton

Distributed malware processing framework based on Python, Redis and S3.
dynamic-analysis-sandboxingmalware-analysisutilities-frameworks
48022h 23m ago
Limon preview

Limon

GitHubmonnappa22/limon

Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
dynamic-analysis-sandboxingmalware-analysismemory-forensics+1
40510 years ago
multiscanner preview

multiscanner

GitHubmitre/multiscanner

Modular file scanning/analysis framework
dynamic-analysis-sandboxingmalware-analysisstatic-analysis+1
6217 years ago
VMwareCloak preview

VMwareCloak

GitHubd4rksystem/vmwarecloak

A PowerShell script that attempts to help malware analysts hide their VMware Windows VM's from malware that may be trying to evade analysis.

defensive-toolsdynamic-analysis-sandboxingmalware-analysis+1
4511 year ago
rikune preview

rikune

GitHublast-emo-boy/rikune

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
binary-analysisdynamic-analysis-sandboxingeducation+8
2401 month ago
HydraDragonAntivirus preview

HydraDragonAntivirus

GitHubhydradragonantivirus/hydradragonantivirus

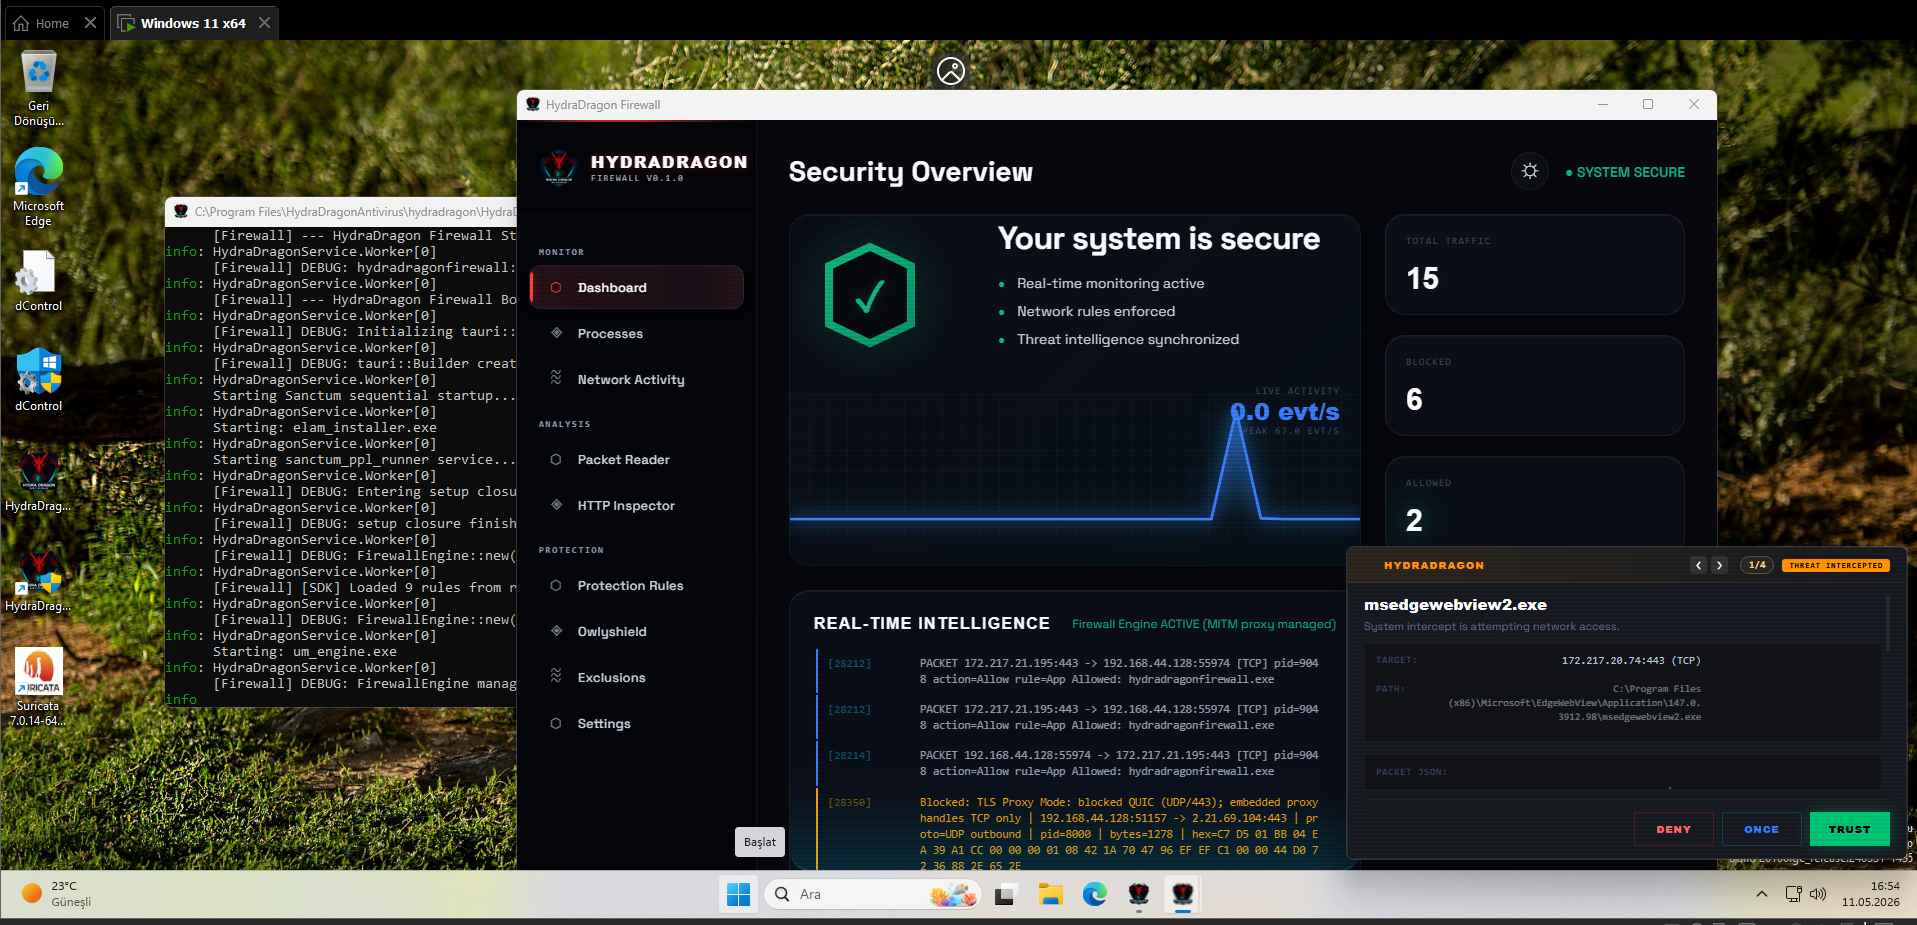
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
dynamic-analysis-sandboxingids-ips-evasionmachine-learning+2
2531h 40m ago
detux preview

detux

GitHubdetuxsandbox/detux

The Multiplatform Linux Sandbox
dynamic-analysis-sandboxingforensicsmalware-analysis+1
2668 years ago
DrSemu preview

DrSemu

GitHubsecrary/drsemu

DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2807 years ago
distro preview

distro

GitHubremnux/distro

Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
digital-forensicsdynamic-analysis-sandboxingforensics+5
11913 days ago
malduck preview

malduck

GitHubcert-polska/malduck

🦆 Malduck is your ducky companion in malware analysis journeys
binary-analysiscryptographydynamic-analysis-sandboxing+3
3581 year ago
wsb-detect preview

wsb-detect

GitHublloydlabs/wsb-detect

wsb-detect enables you to detect if you are running in Windows Sandbox ("WSB")
dynamic-analysis-sandboxingmalware-analysispayload-development+1
3733 years ago
Sandbox_Scryer preview

Sandbox_Scryer

GitHubpayloadsecurity/sandbox_scryer

Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
dynamic-analysis-sandboxingeducationinformation-gathering+6
2304 years ago
attack_monitor preview

attack_monitor

GitHubyarox24/attack_monitor

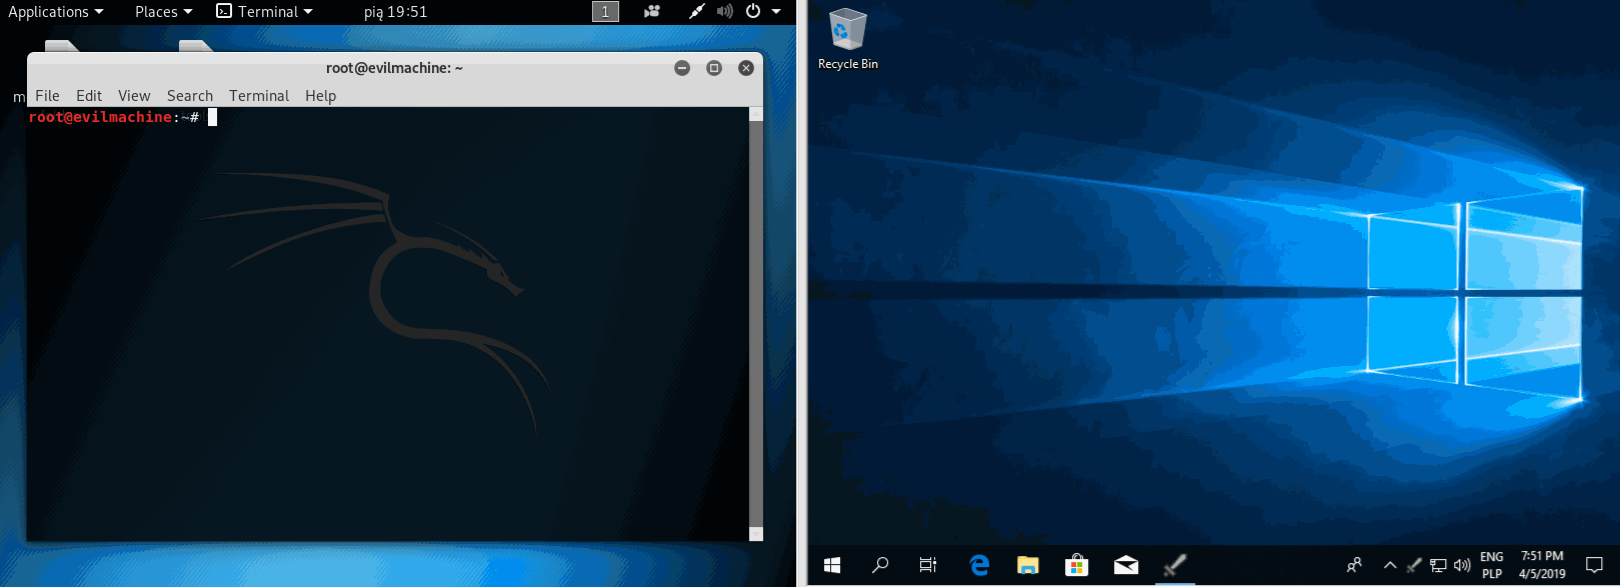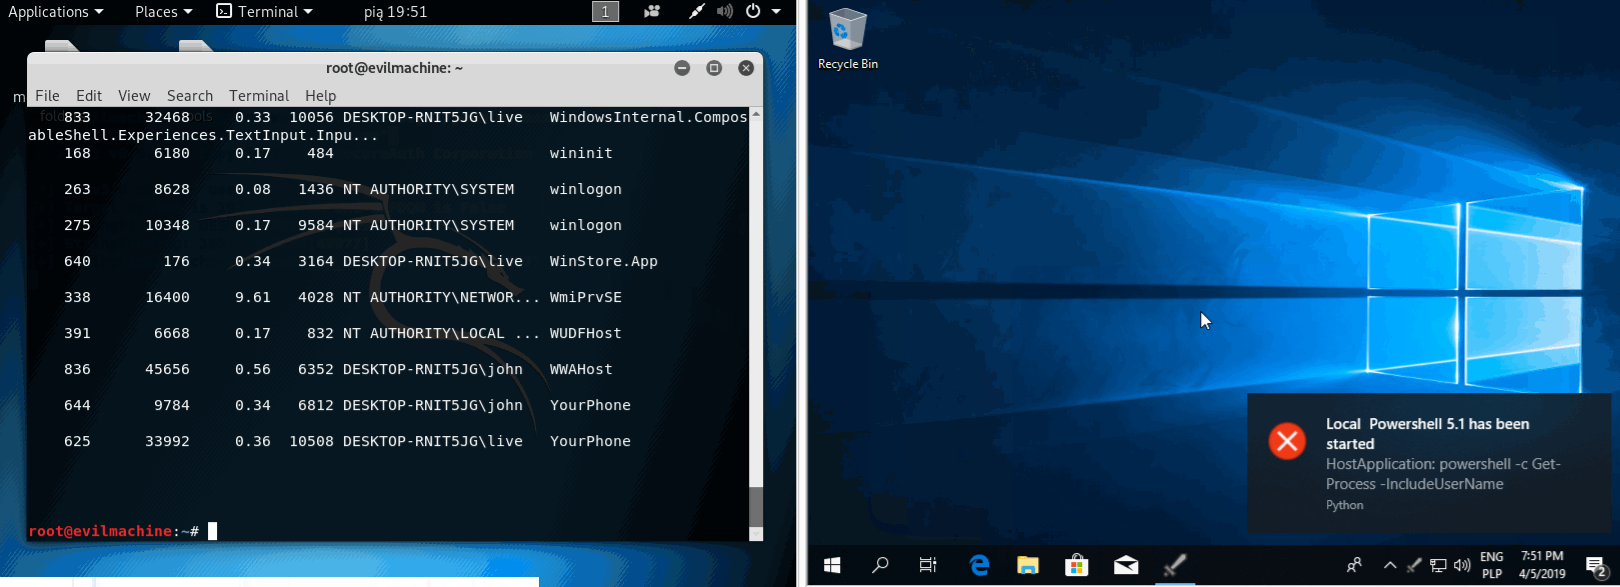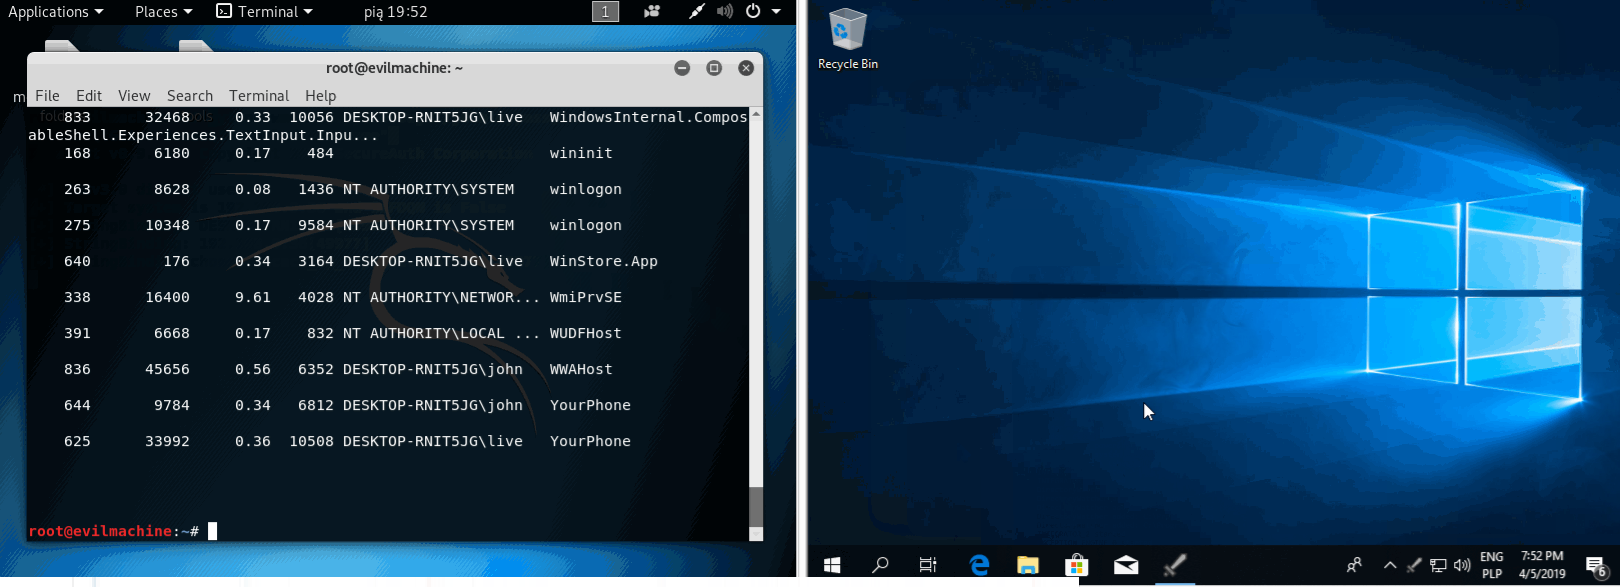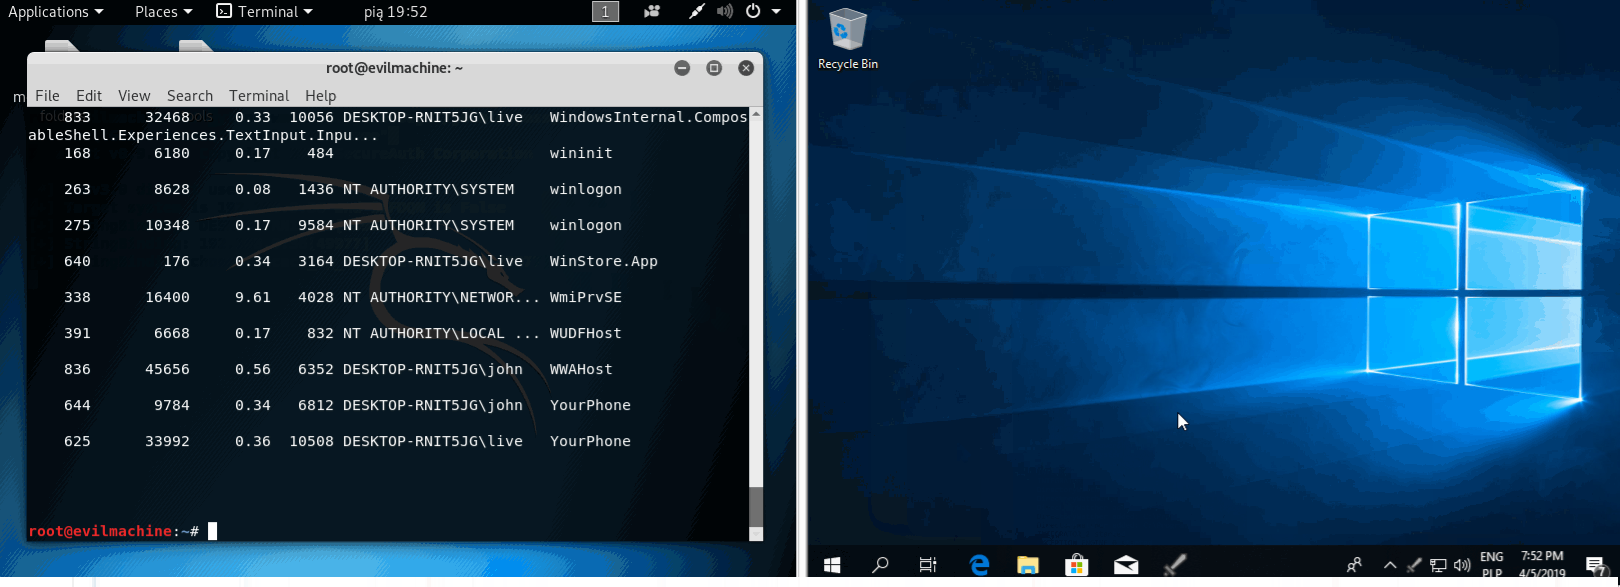
Endpoint detection & Malware analysis software

defensive-toolsdynamic-analysis-sandboxingincident-response+1
2346 years ago
Previous1234567Next