
droidbox
 pjlantz/droidbox
Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
android-securitydynamic-analysis-sandboxinginformation-gathering+2
805
pjlantz/droidboxDynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
 rek7/fireelf
fireELF - Fileless Linux Malware Framework
 decaf-project/decaf
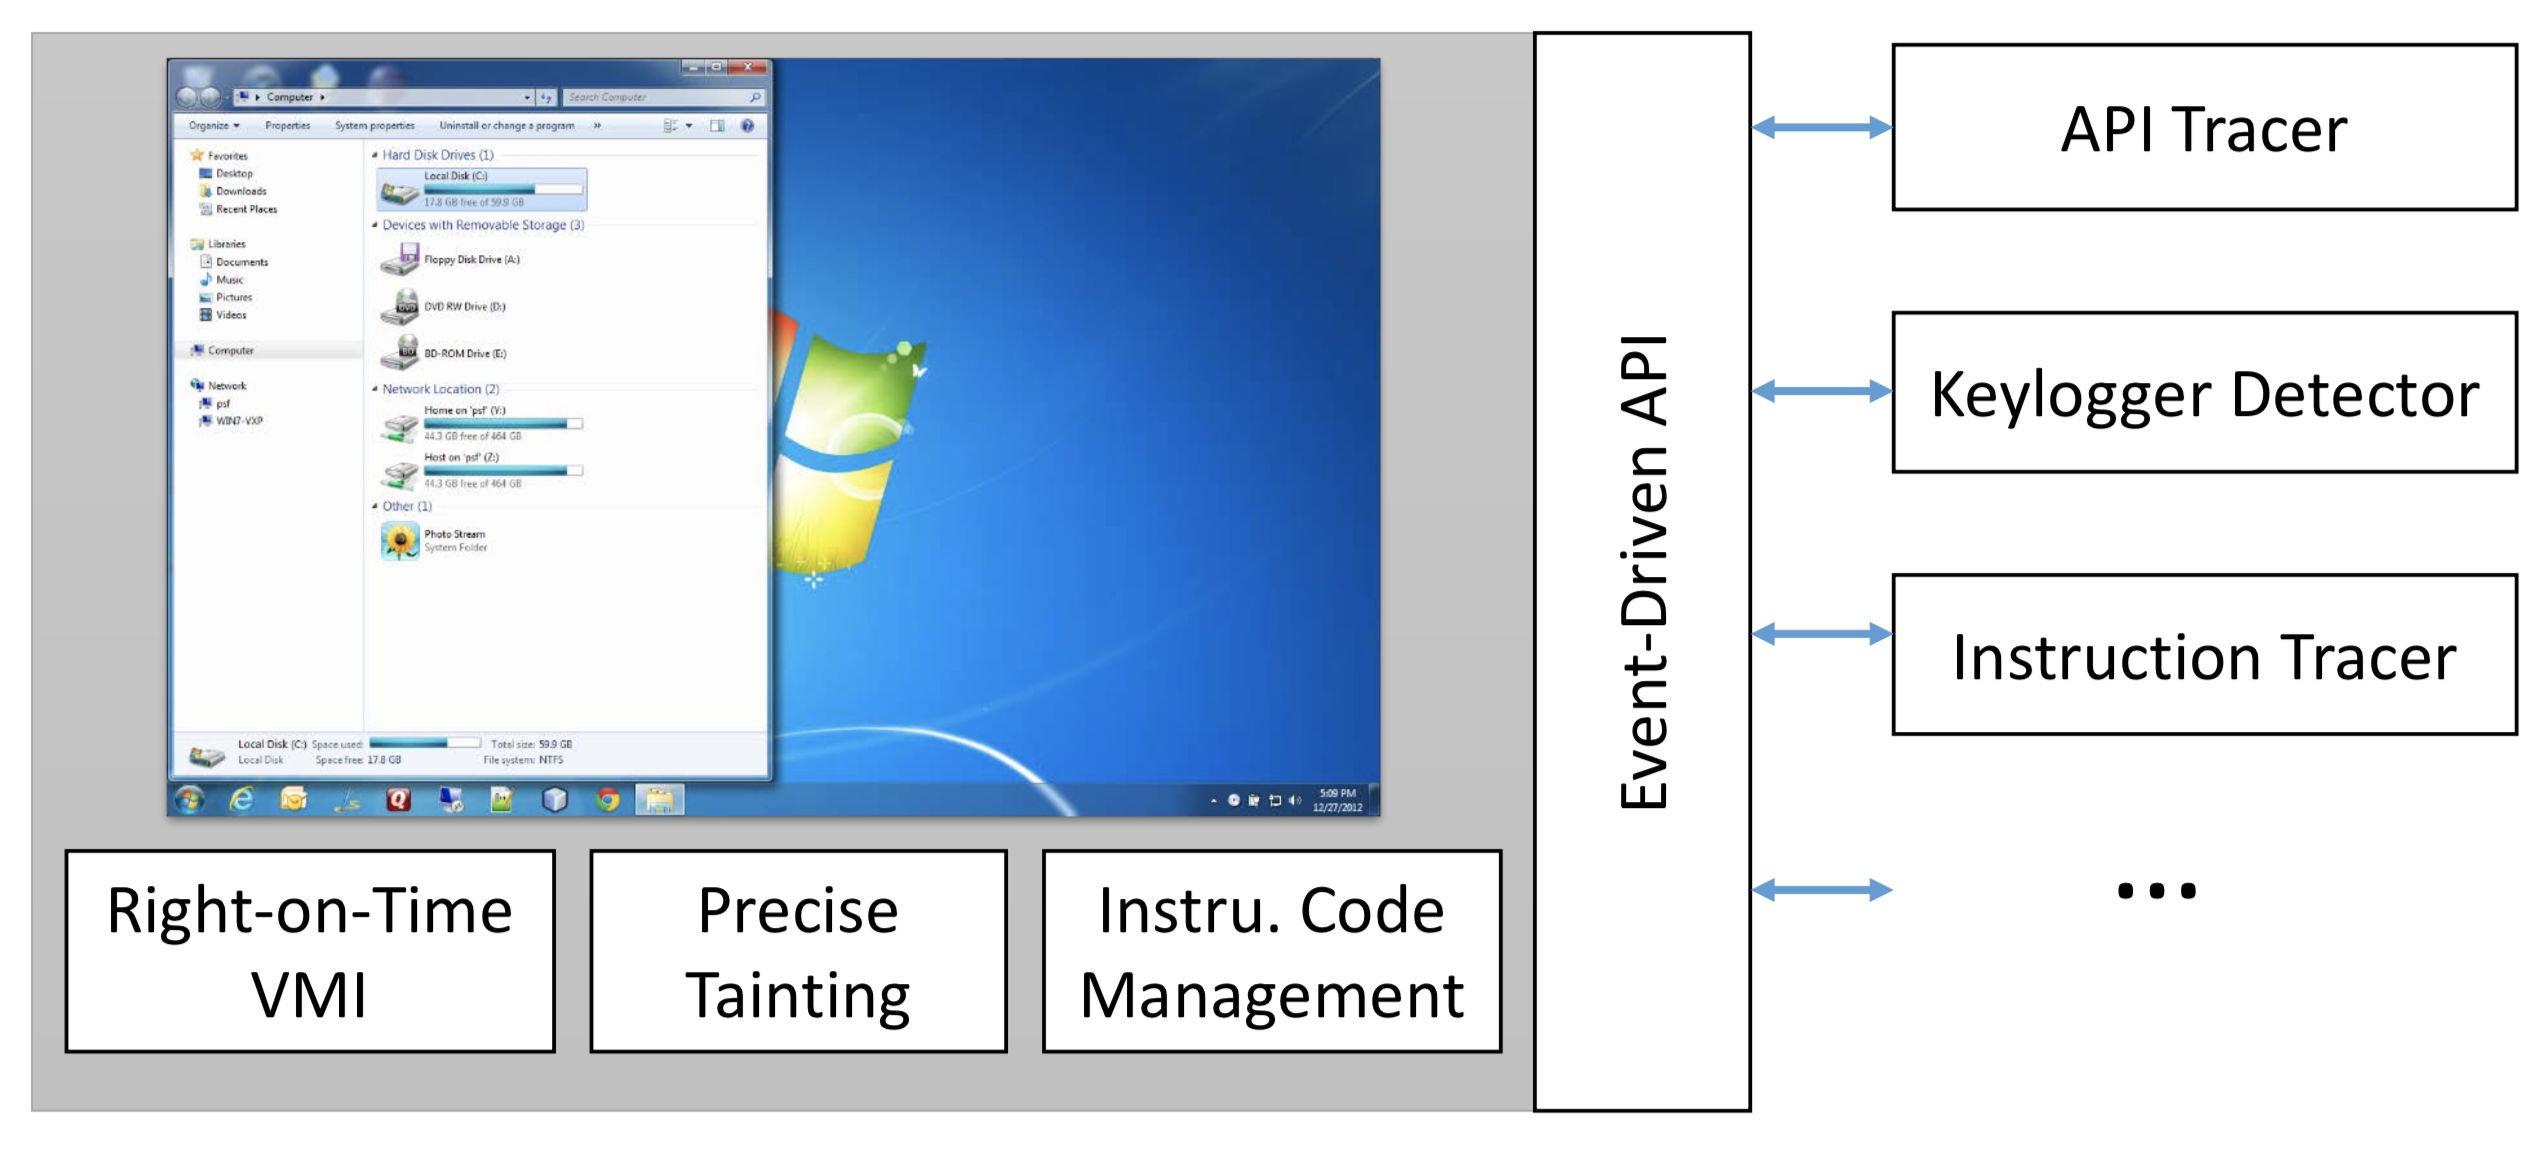
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 calebfenton/dex-oracle
A pattern based Dalvik deobfuscator which uses limited execution to improve semantic analysis
 cryptax/droidlysis
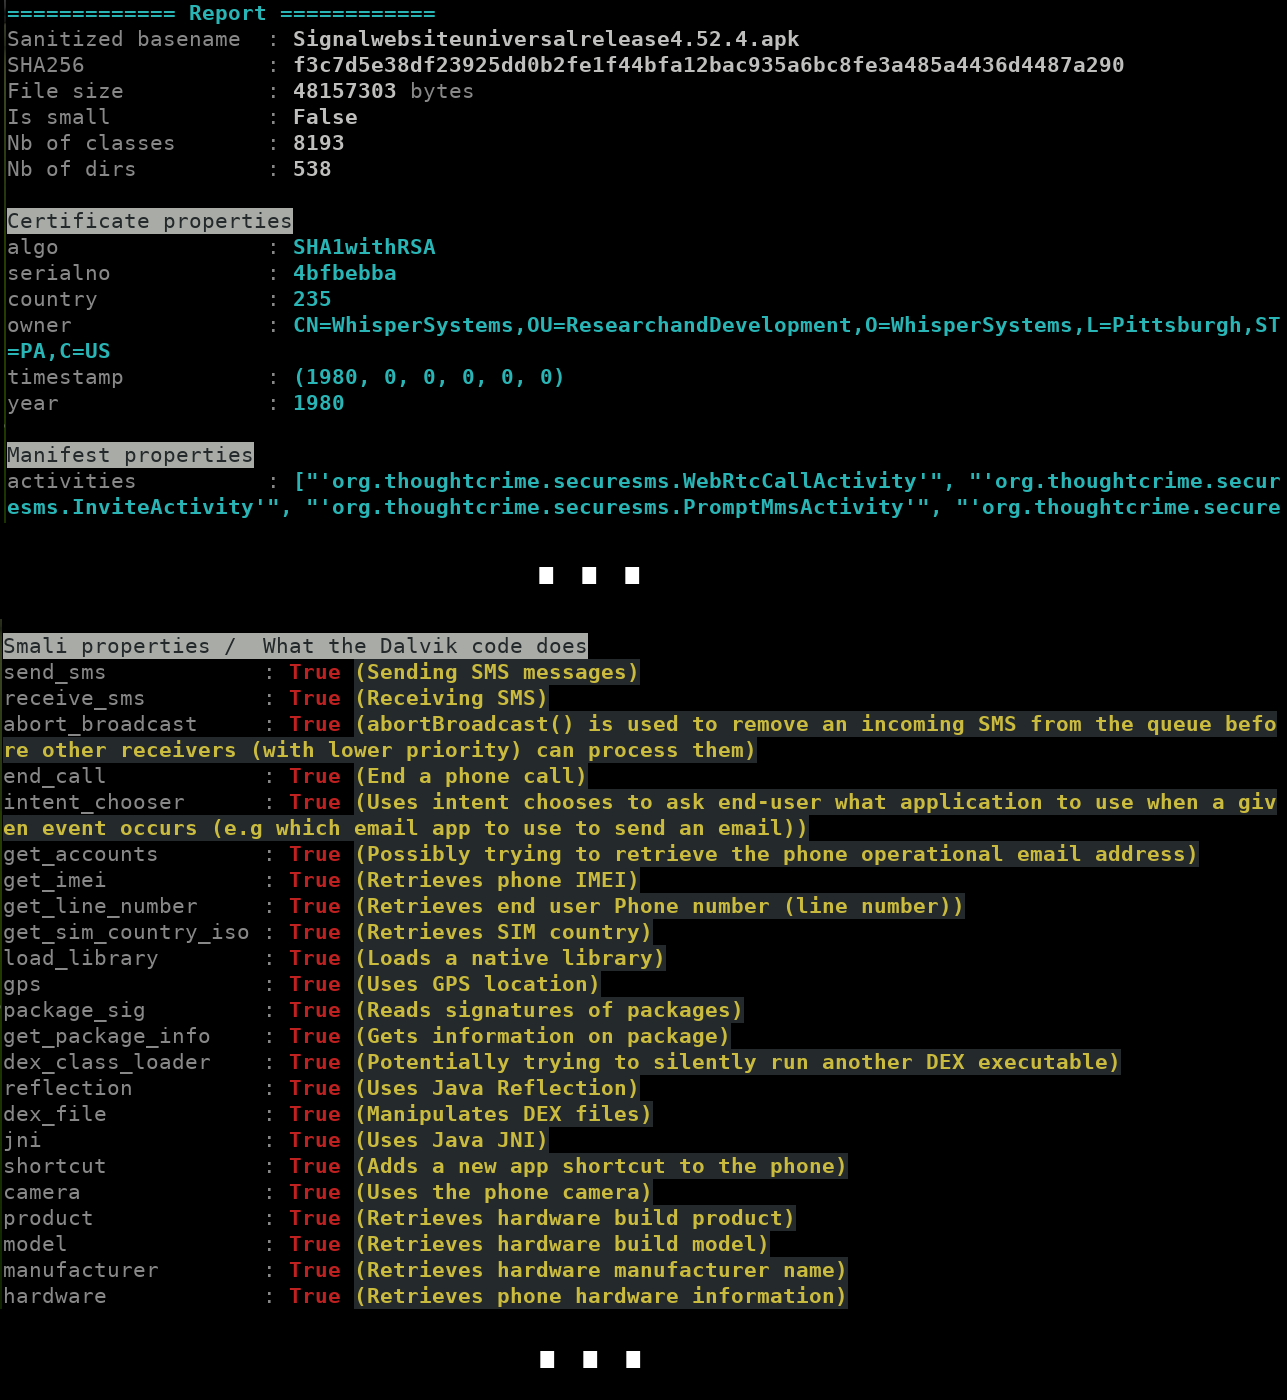
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
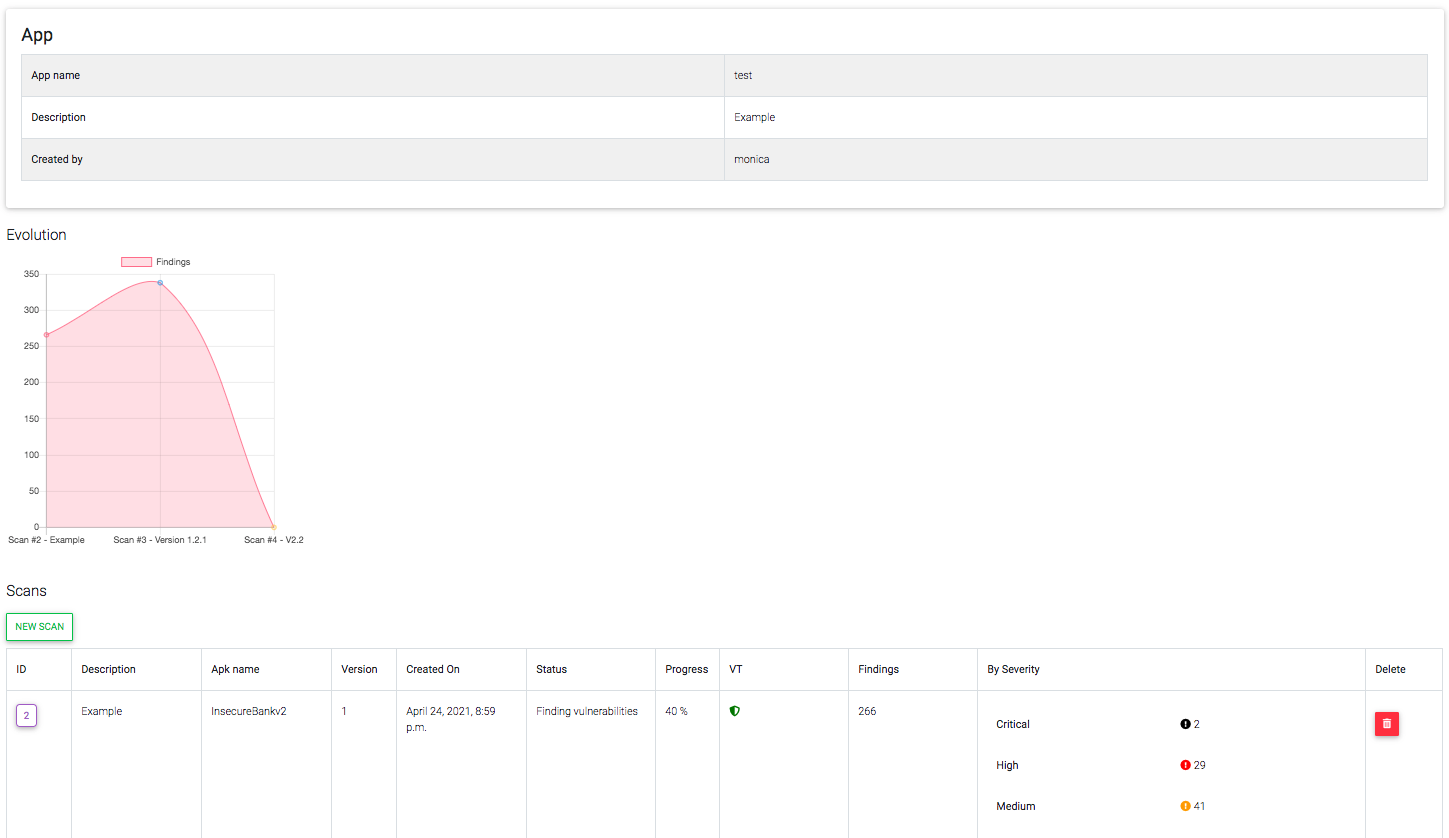 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 maddiestone/conpresentations
Slide decks from my conference presentations
 malwaretech/tinyxpb
Windows XP 32-Bit Bootkit
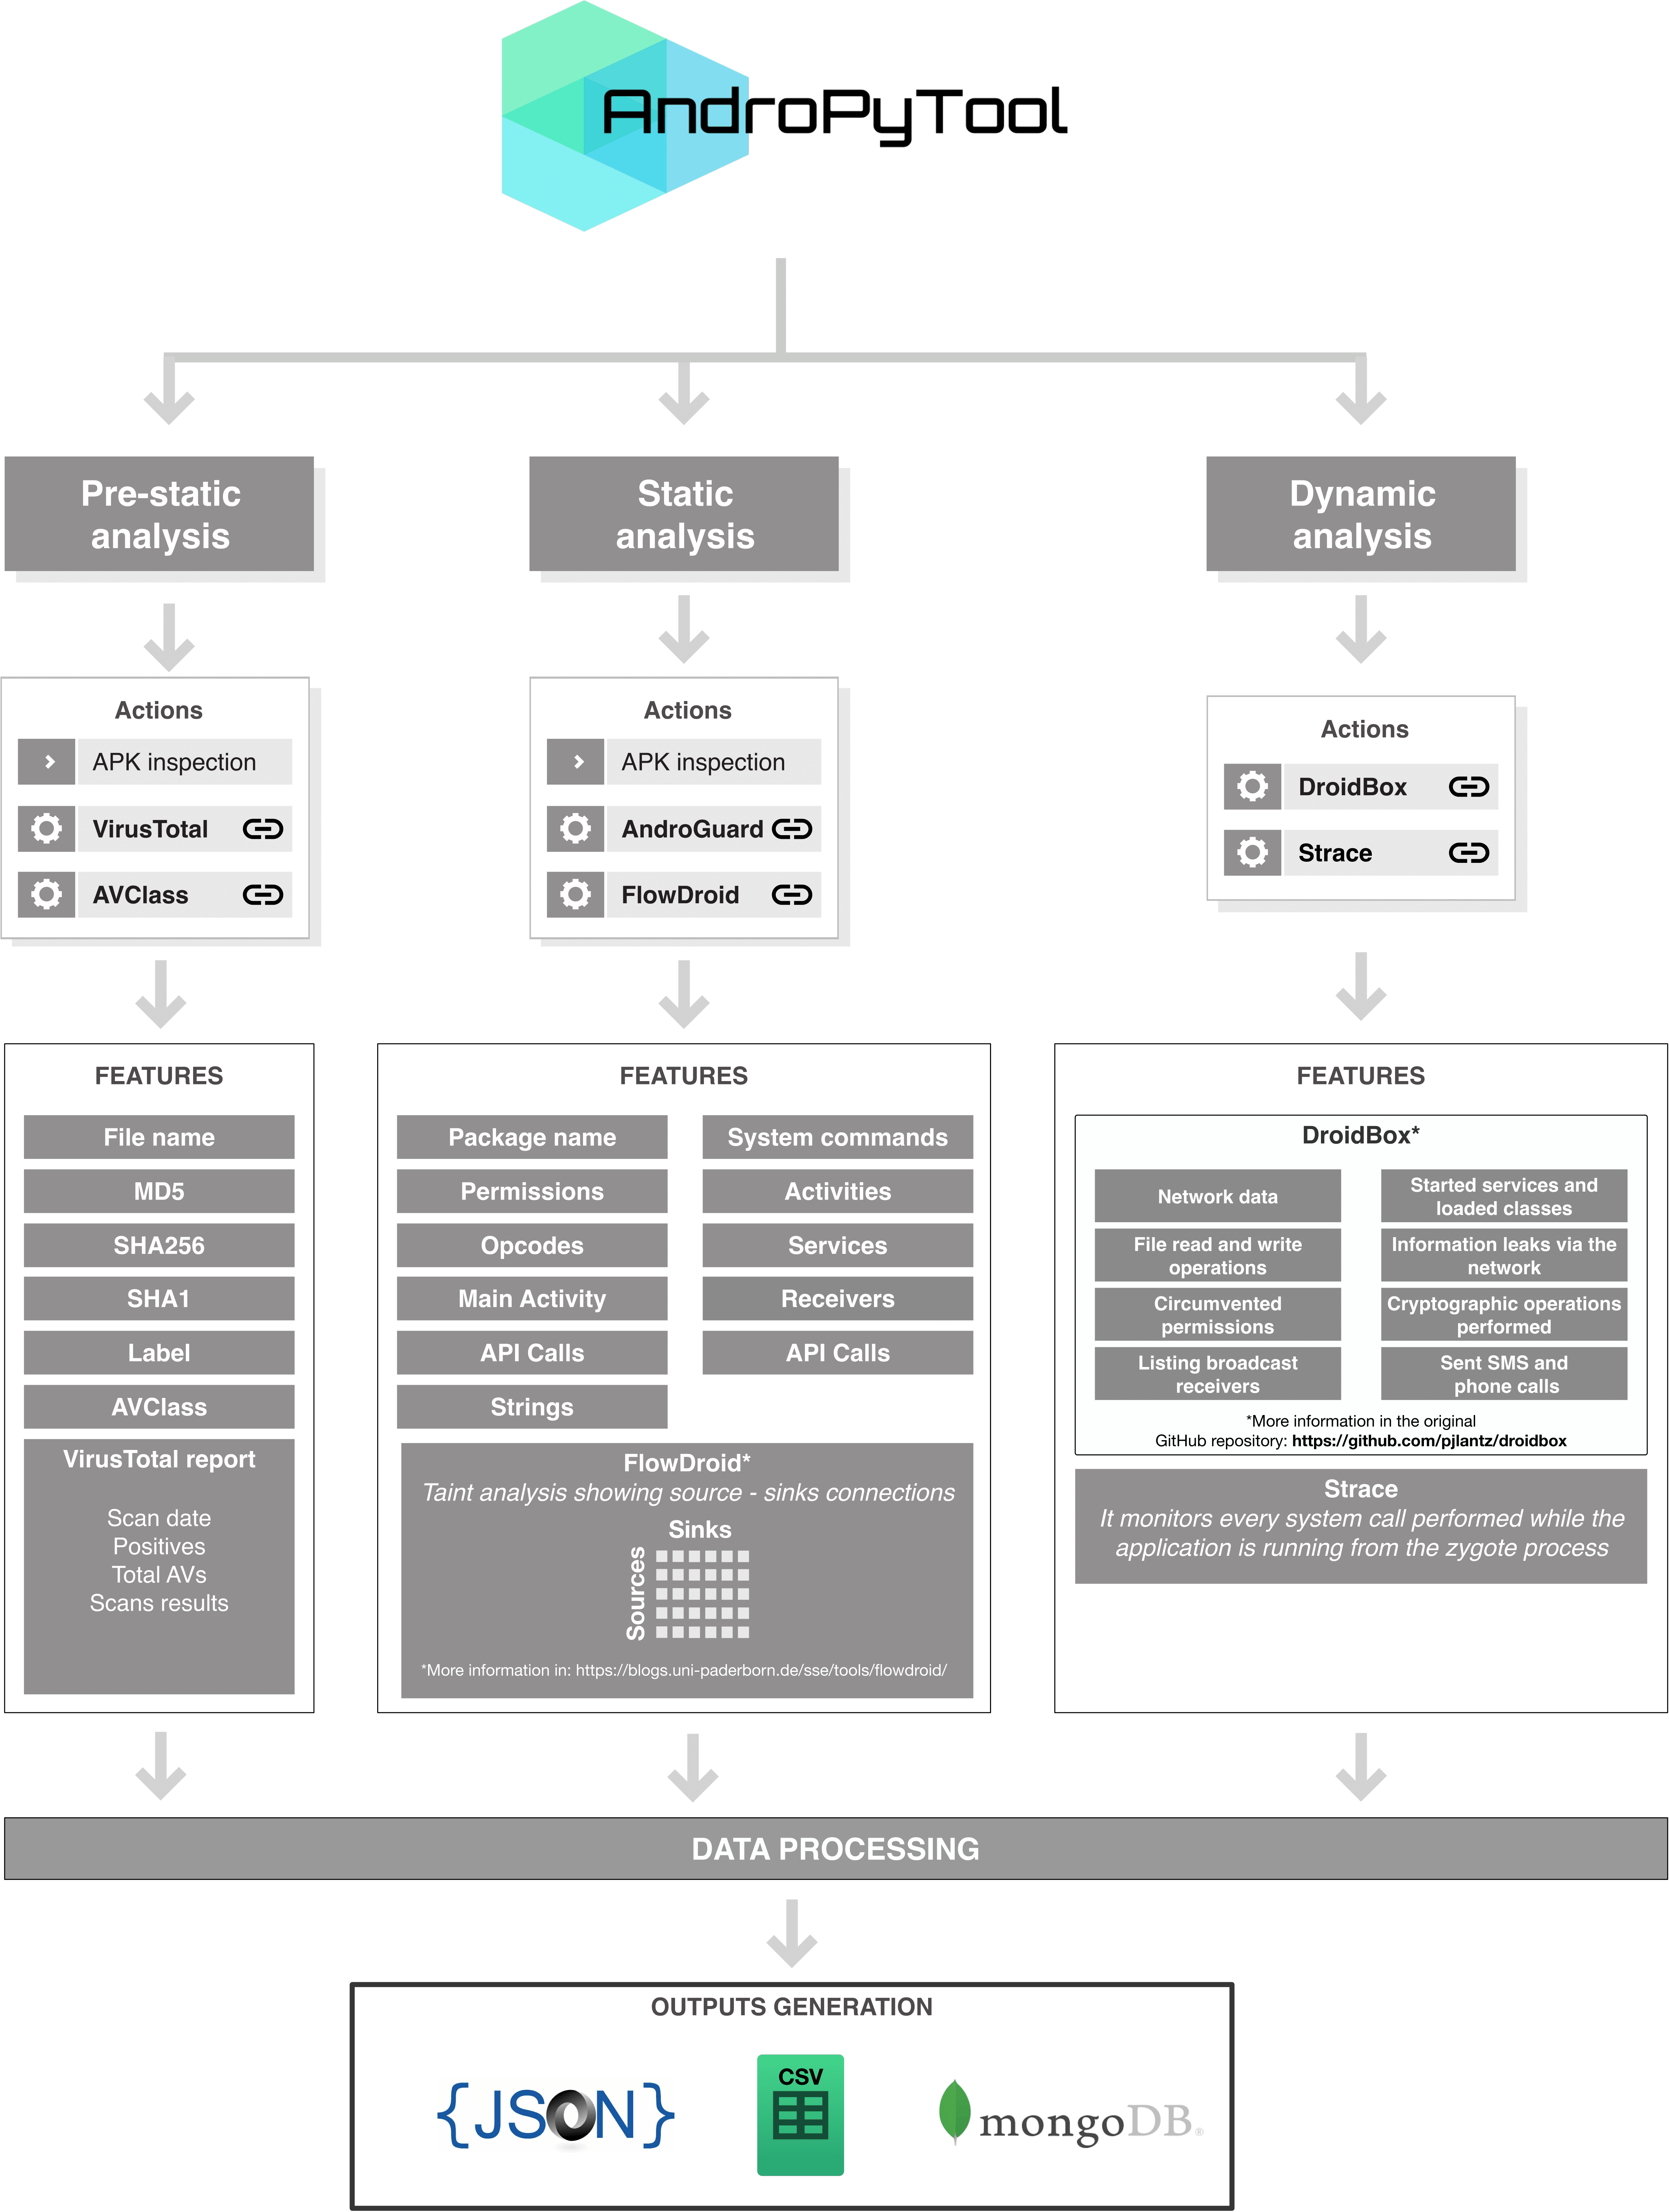 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 sqrtzeroknowledge/cve-2023-23397_exploit_0day
Exploit for the CVE-2023-23397
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…