
red-detector
 lightspin-tech/red-detector
Automated vulnerability, misconfiguration, and rootkit scanner for AWS EC2 instances using Vuls, Lynis, and Chkrootkit via snapshot-based offline…
cloud-securitymalware-analysismisconfiguration+1
89
lightspin-tech/red-detectorAutomated vulnerability, misconfiguration, and rootkit scanner for AWS EC2 instances using Vuls, Lynis, and Chkrootkit via snapshot-based offline…
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 knifeyspoony/ghidra-copilot
Provides a chat-based, LLM-assisted reverse engineering experience within Ghidra
 hasherezade/bunitu_tests
Scripts for communication with Bunitu Trojan C&Cs
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
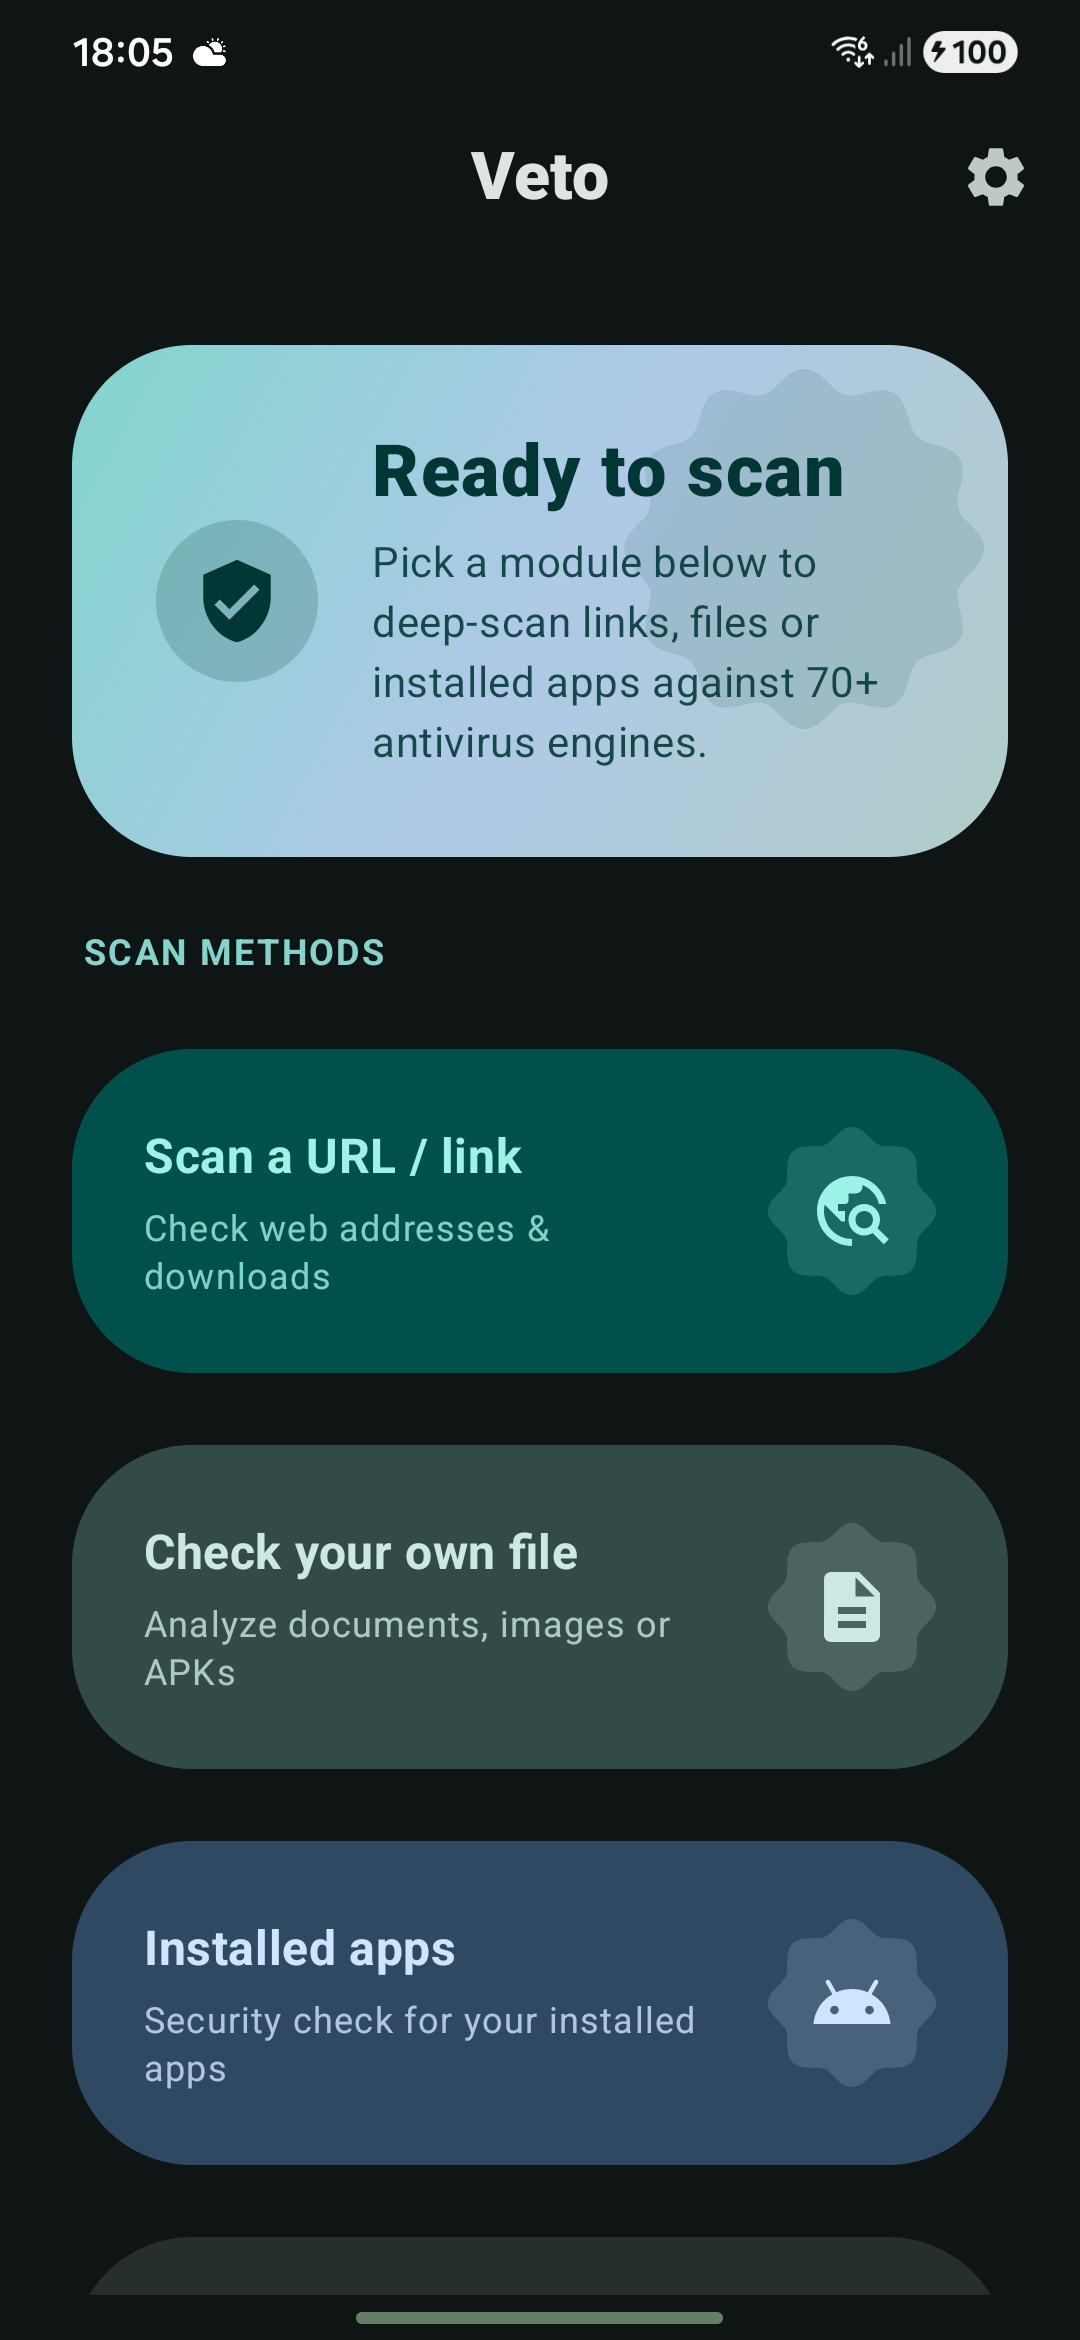 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
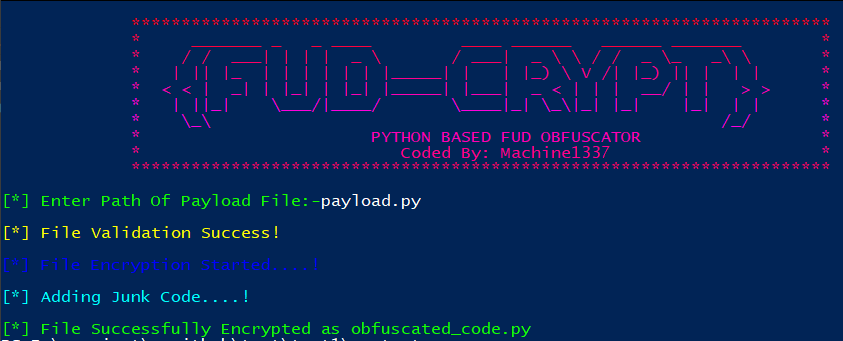 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
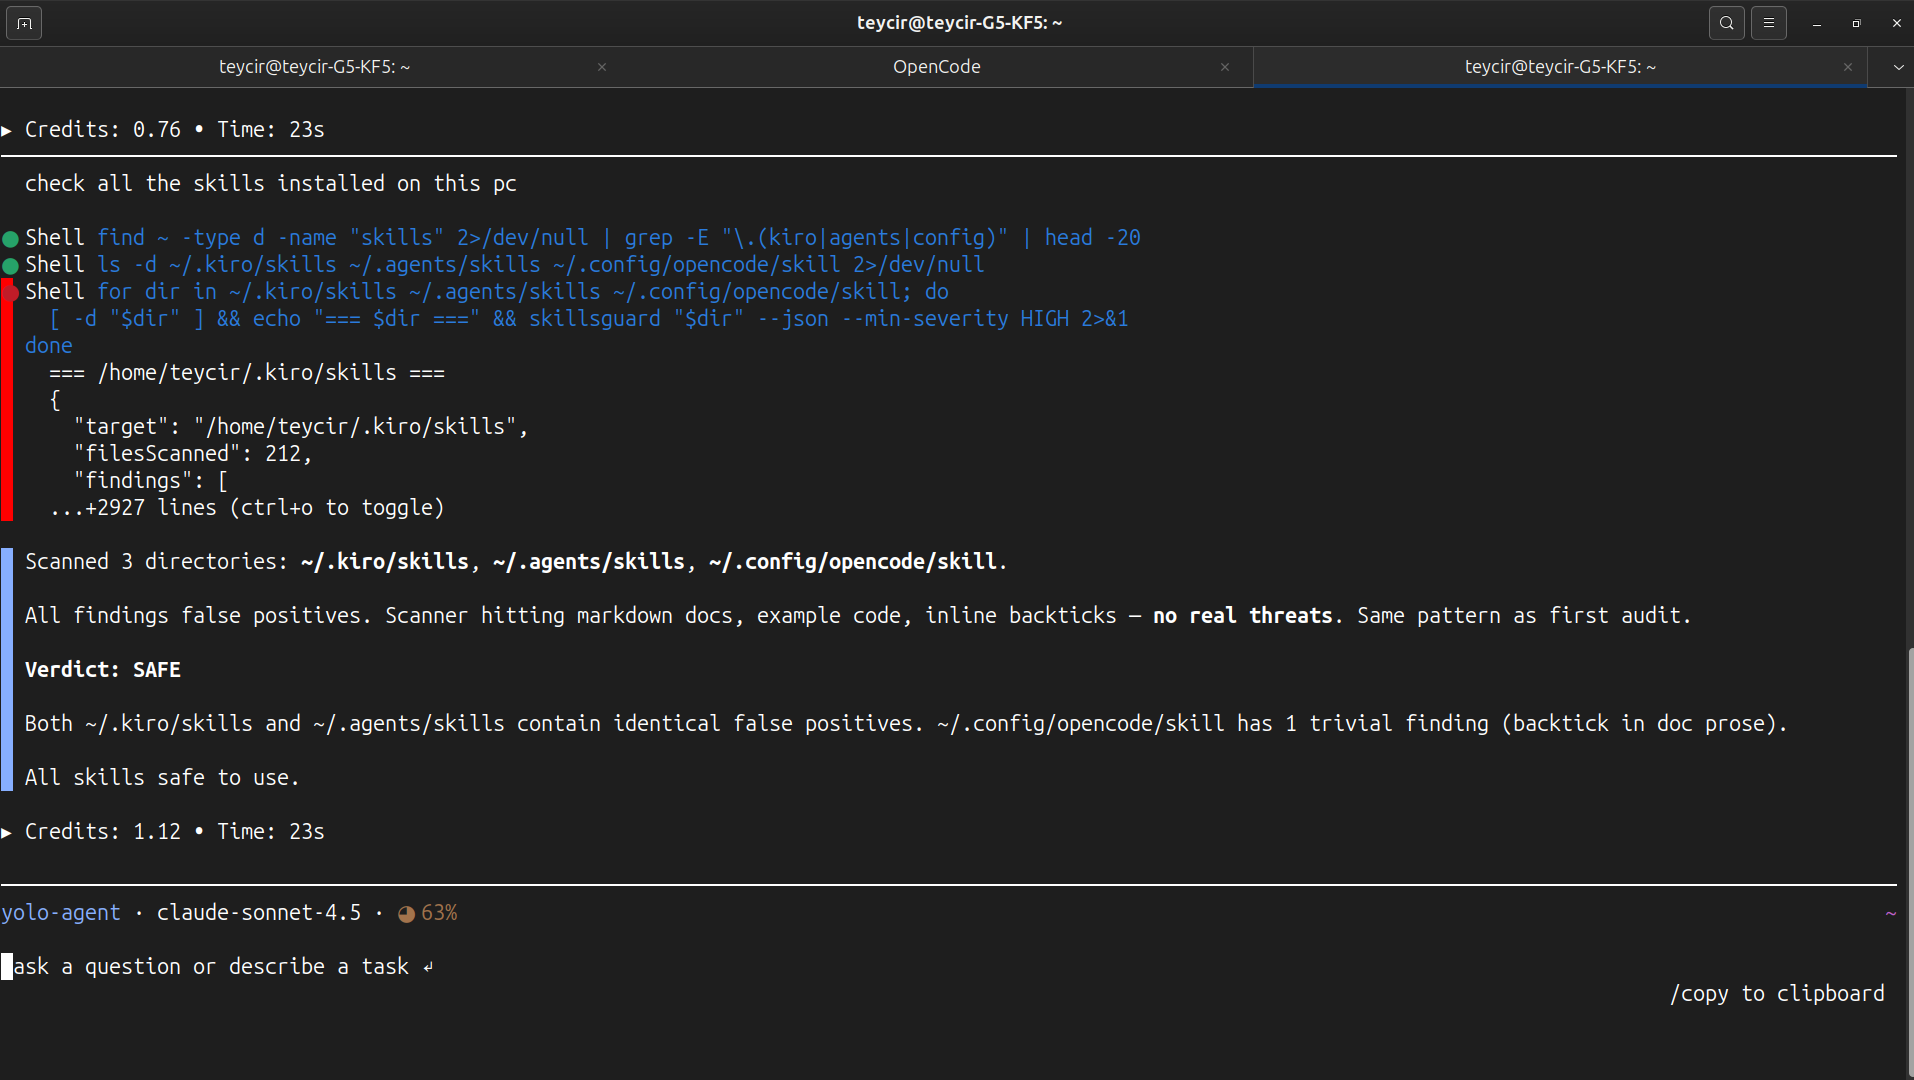 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 hellwound/batchfuscate
A simple script to obfuscate batch(bat) code easily
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 neorai/vt-py-scanner
Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…