

pyREtic
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
binary-analysiscode-analysisdebuggers+5
2673 years ago
mynameismeerkat/pyreticpyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 not-matthias/amd_hypervisor
Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
 guibacellar/nxransomware
A next generation of ransomware. Fully written using a .Net Framework + C&C System
 enkomio/sojobo
A binary analysis framework
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 bkcs-hust/lstm-mi
A LSTM based framework for handling multiclass imbalance in DGA botnet detection
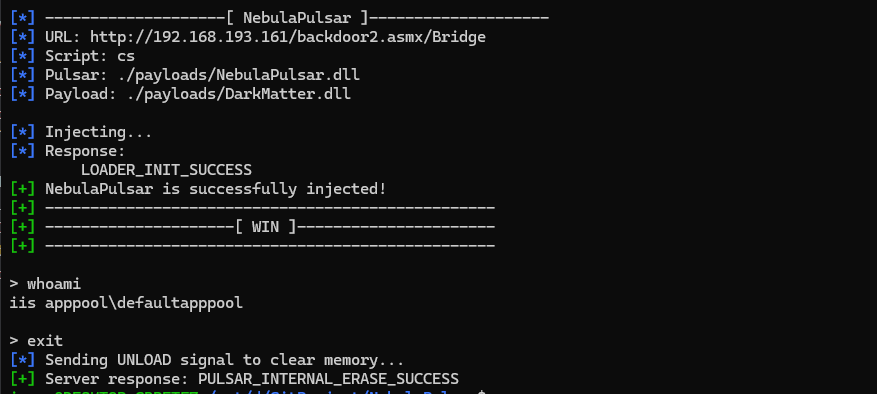 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…