
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
41 results
IoT-Home-Guard preview

IoT-Home-Guard

GitHubarthastang/iot-home-guard

A tool for malicious behavior detection in IoT devices
anomaly-detectionintrusion-detectioniot-security+2
777 years ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

database-securitydigital-forensicsdisk-forensics+8
856 months ago
flowinspect preview

flowinspect

GitHub7h3ram/flowinspect

A Network Inspection Tool

forensicsfuzzingintrusion-detection+5
829 years ago
malware-check preview

malware-check

GitHubmomenbasel/malware-check

Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
binary-analysiscode-analysisdevsecops+7
639 days ago
filterforge preview

filterforge

GitHubcloudflare/filterforge

Tool for solving BPF filters and crafting packets based on these.

binary-analysisforensicsfuzzing+5
637 months ago
stegowiper preview

stegowiper

GitHubmindcrypt/stegowiper

A powerful and flexible tool to apply active attacks for disrupting stegomalware

defensive-toolsincident-responsemalware-analysis+2
564 years ago
Hunt-Weird-ImageLoads preview

Hunt-Weird-ImageLoads

GitHubtheflink/hunt-weird-imageloads

Small tool to play with IOCs caused by Imageload events
anomaly-detectiondefensive-toolsincident-response+2
473 years ago
strafer preview

strafer

GitHubadityaks/strafer

Strafer: A tool to detect potential infections in Elasticsearch instances
cloud-securitydatabase-securityinformation-gathering+4
275 years ago
EventHorizon preview

EventHorizon

GitHubhullabrian/eventhorizon

Tool that gathers a customizable set of ETW telemetry and generates user-defined detections
defensive-toolseducationforensics+5
569 months ago
melee preview

melee

GitHubadityaks/melee

Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
database-securityincident-responsemalware-analysis+2
233 years ago
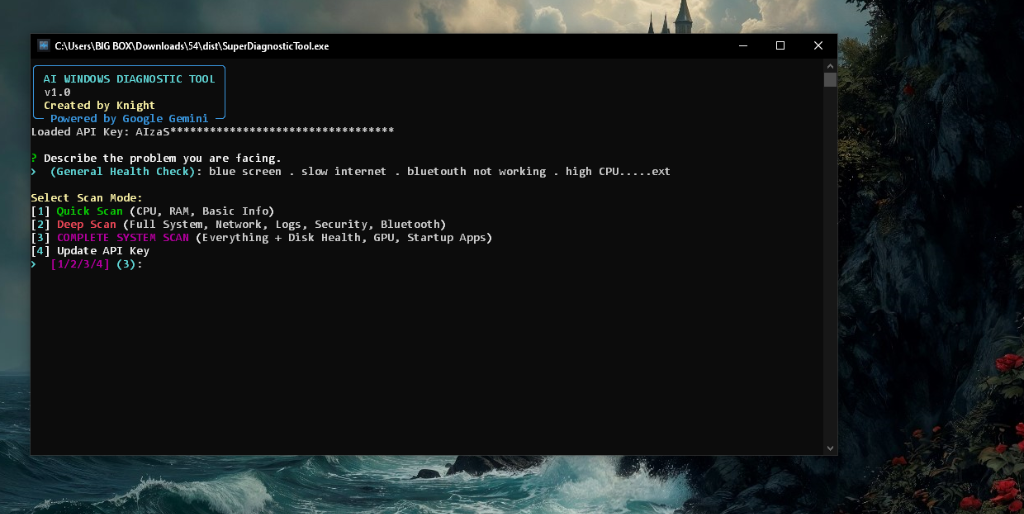
SuperDiagnosticTool preview

SuperDiagnosticTool

GitHubguettaf-hossam/superdiagnostictool

AI-powered Windows diagnostic & auto-repair tool using Google Gemini. Detect crashes, optimize performance, scan for malware, and generate PowerShell…
ai-securityconfiguration-auditingforensics+7
1917 days ago
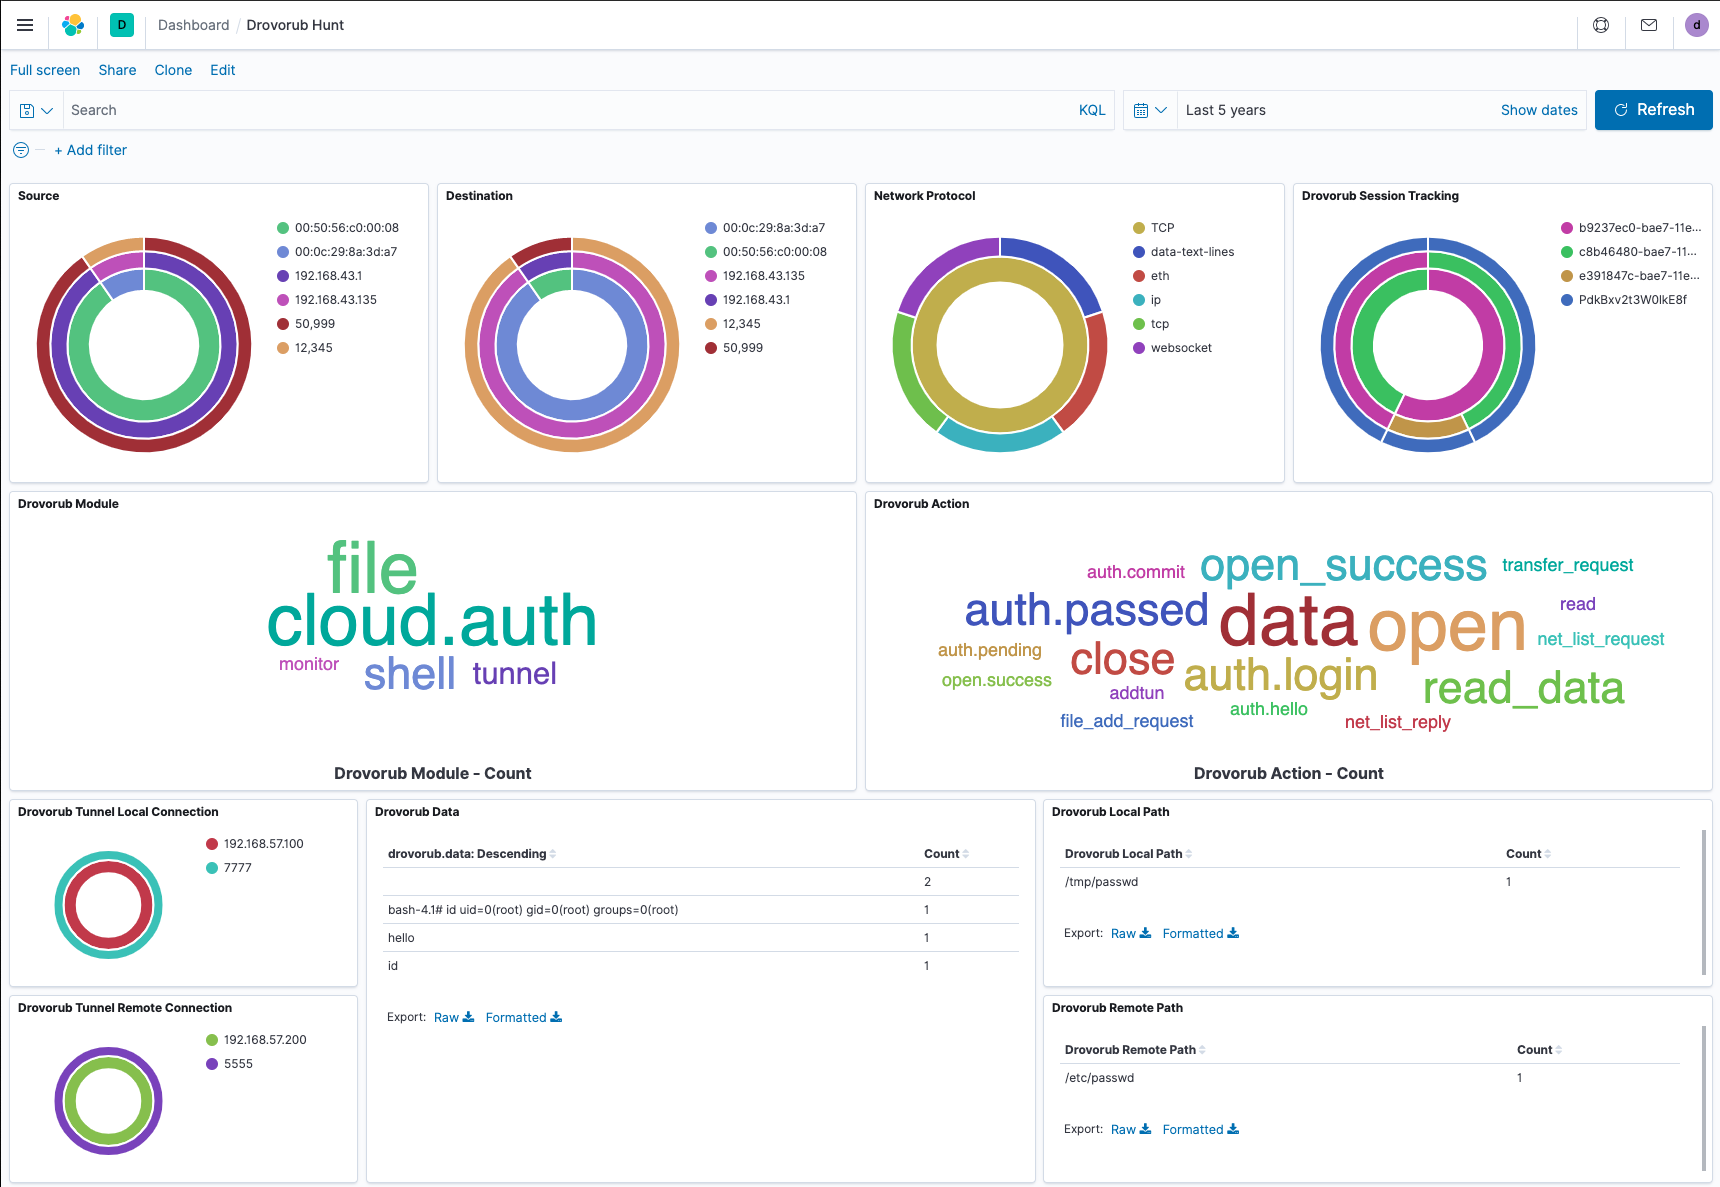
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

A tool to assist with network-based hunting for GRU's Drovorub malware c2

incident-responseintrusion-detectionmalware-analysis+3
256 years ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

android-securitycryptographydynamic-analysis-sandboxing+8
1010 days ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
15.6k4h 17m ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.2k20h 44m ago
NtWarden preview

NtWarden

GitHubmrt4ntr4/ntwarden

Windows Analysis and Research Toolkit

binary-analysisdefensive-toolsdigital-forensics+4
6766 months ago
CrimsonEDR preview

CrimsonEDR

GitHubhelixo32/crimsonedr

Simulate the behavior of AV/EDR for malware development training.
binary-analysisdefensive-toolsdynamic-analysis-sandboxing+3
5682 years ago
fastfinder preview

fastfinder

GitHubcodeyourweb/fastfinder

Incident Response - Fast suspicious file finder

digital-forensicsforensicsincident-response+1
2609 months ago
Previous123Next