

Archived
flare-ida
 mandiant/flare-ida
IDA Pro utilities from FLARE team
binary-analysisdebuggersdynamic-analysis-sandboxing+3
2.5k
 rurik/noriben
Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 denuvosoftwaresolutions/gamba
Simplification of General Mixed Boolean-Arithmetic Expressions: GAMBA
 woj-ciech/daily-dose-of-malware
Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…
 emposha/php-shell-detector
Web Shell Detector – is a php script that helps you find and identify php/cgi(perl)/asp/aspx shells. Web Shell Detector has a “web shells” signature…
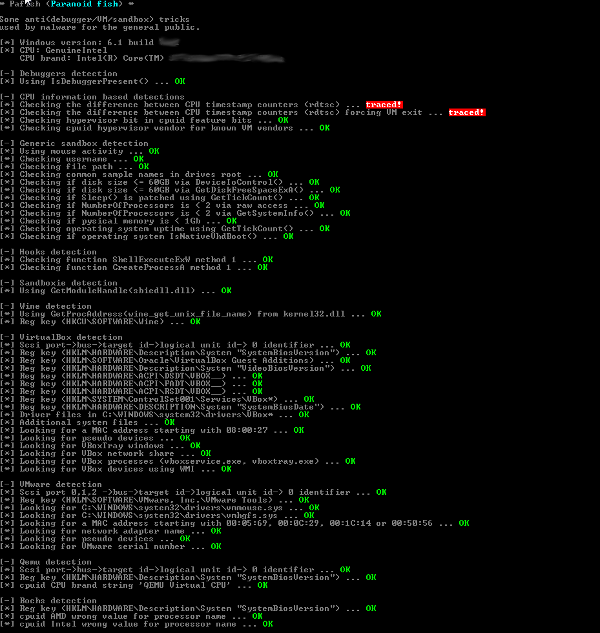 nsmfoo/antivmdetection
Script to create templates to use with VirtualBox to make vm detection harder
 corelight/detect-ransomware-filenames
Zeek script that monitors SMB traffic and alerts on known ransomware filenames using the Anti-Ransomware File System Resource Manager list.
 tadash10/detect-cve-2024-0762
Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature
 hellwound/batchfuscate
A simple script to obfuscate batch(bat) code easily
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 oalabs/frida-wshook
Script analysis tool based on Frida.re
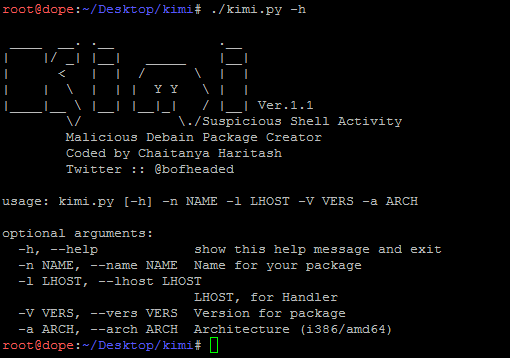 chaitanyaharitash/kimi
Script to generate malicious debian packages (debain trojans).
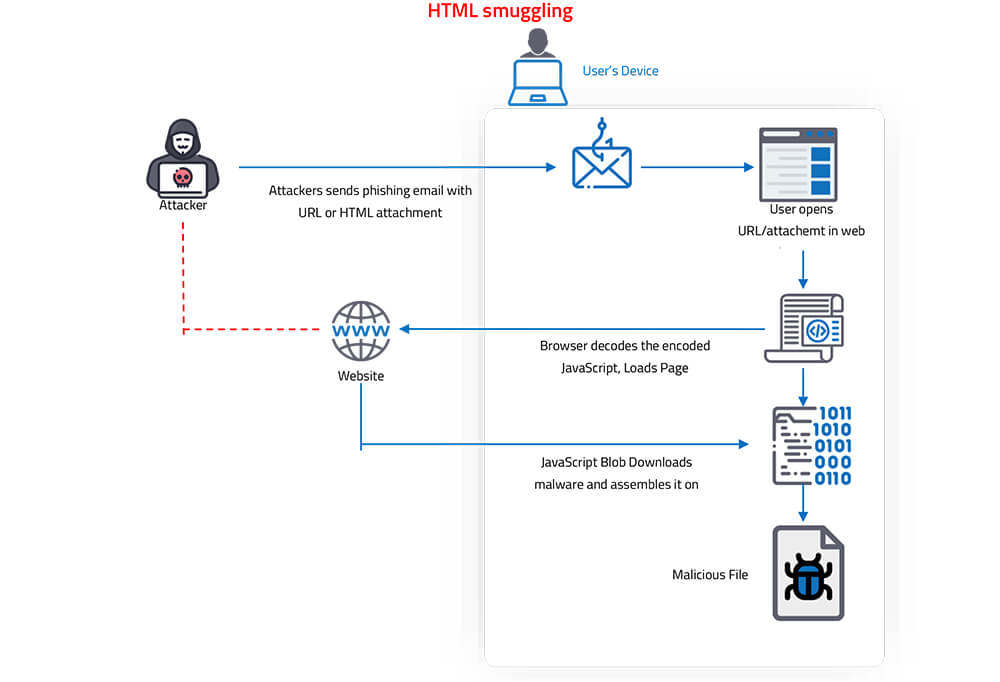 de3vil/htmlsmuggling
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 mahfuzreham/cpanel-cve-2026-41940
cPanel CVE-2026-41940 nuclear.x86 Security Audit & Cleanup Script
 emalderson/thephish
ThePhish: an automated phishing email analysis tool