
Archived
flashmingo
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
binary-analysisdynamic-analysis-sandboxingeducation+6
120
mandiant/flashmingoAutomatic analysis of SWF files based on some heuristics. Extensible via plugins.
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 amorath/threatscraper
Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
 rurik/noriben
Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
 cert-polska/karton
Distributed malware processing framework based on Python, Redis and S3.
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
 0x534a/dynmx
Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
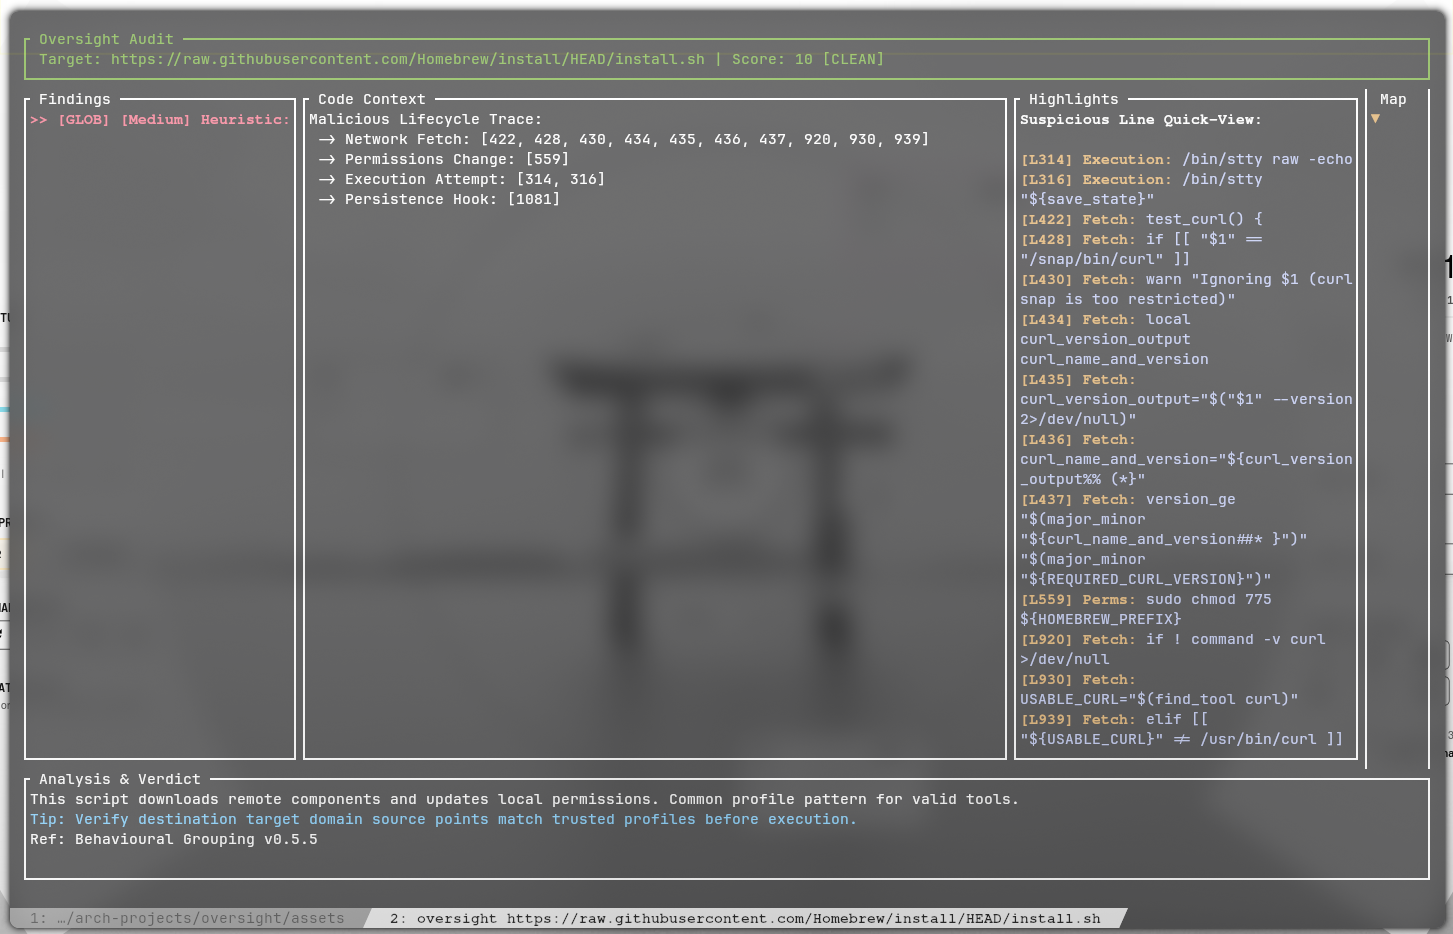 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…