Vidar-Stealer-Reverse-Engineering

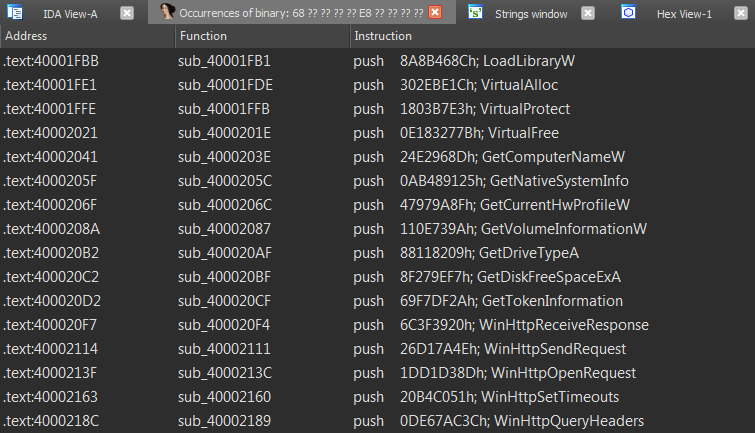
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…

InjectProc - Process Injection Techniques [This project is not maintained anymore]

Open-source Windows kernel-level EDR lab for understanding and testing detection methods against process injection, credential dumping, and other…

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

CVE-2025-61301 proof-of-concept demonstrating denial-of-analysis in CAPEv2 via recursive process forking that triggers MongoDB BSON limits and orjson…

A small utility to deal with malware embedded hashes.

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs

👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.

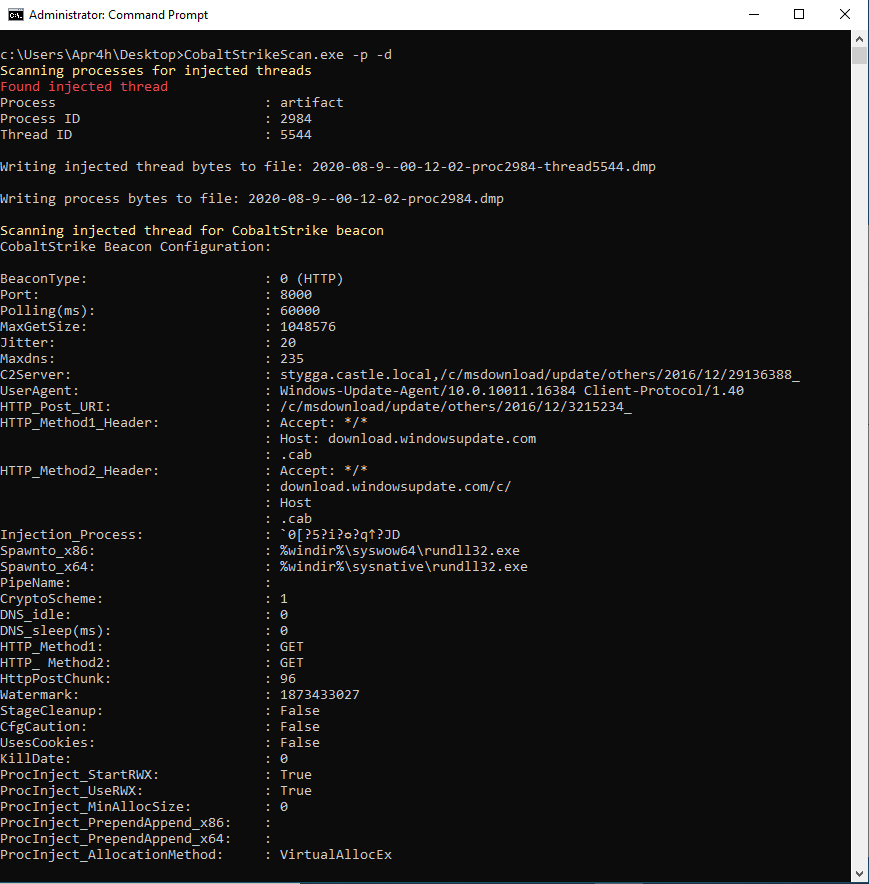
Scan files or process memory for CobaltStrike beacons and parse their configuration

An information disclosure vulnerability occurs when LibreOffice 6.0.3 and Apache OpenOffice Writer 4.1.5 automatically process and initiate an SMB…

Windows kernel driver that removes Process Protection (PP) and Process Protection Light (PPL).

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

An API hooking framework for intercepting and monitoring Windows applications