
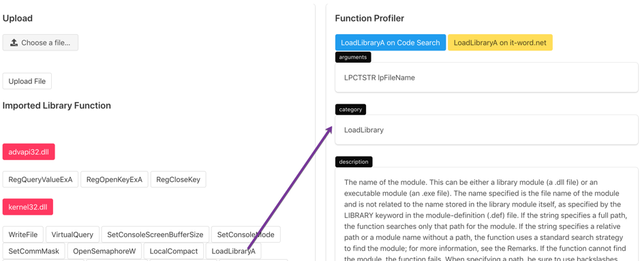
malwinx
 mohitdabas/malwinx
Just a normal flask web app to understand win32api with code snippets and references.
code-analysiseducationmalware-analysis
mohitdabas/malwinxJust a normal flask web app to understand win32api with code snippets and references.
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 eset/malware-research
Code written as part of our various malware investigations
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
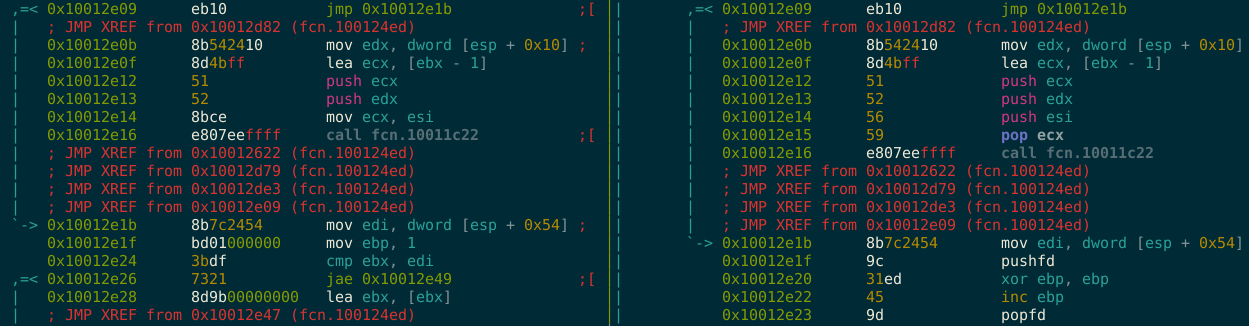 a0rtega/metame
metame is a metamorphic code engine for arbitrary executables
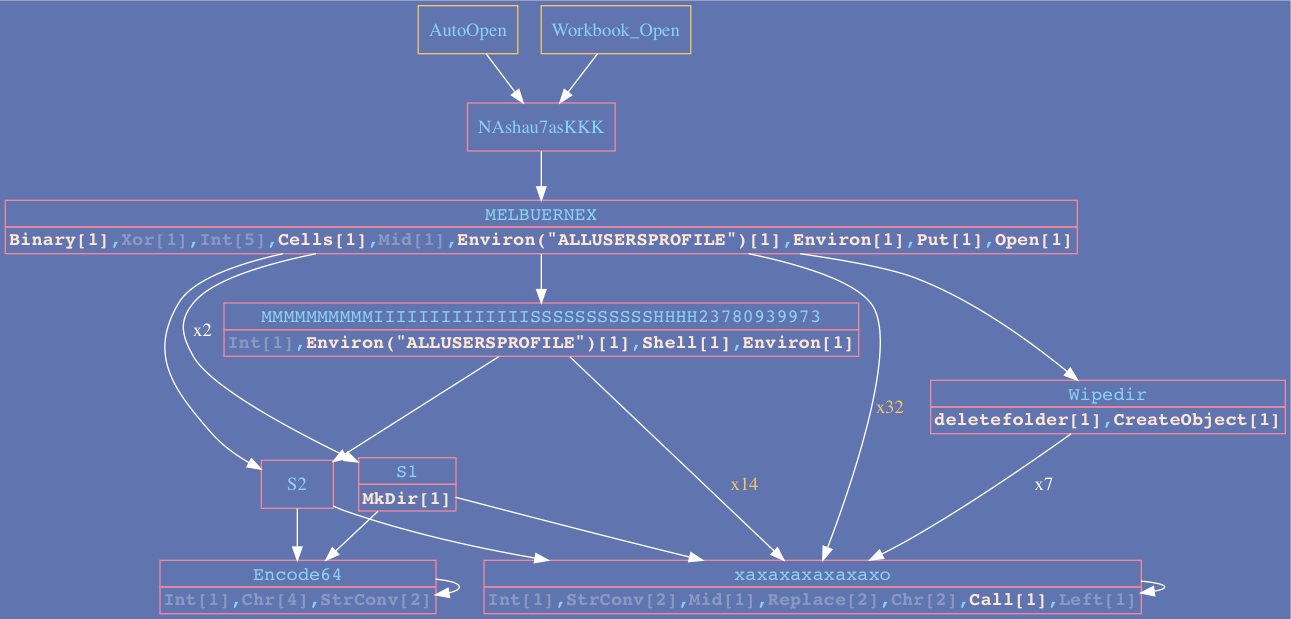 malwarecantfly/vba2graph
Vba2Graph - Generate call graphs from VBA code, for easier analysis of malicious documents.
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
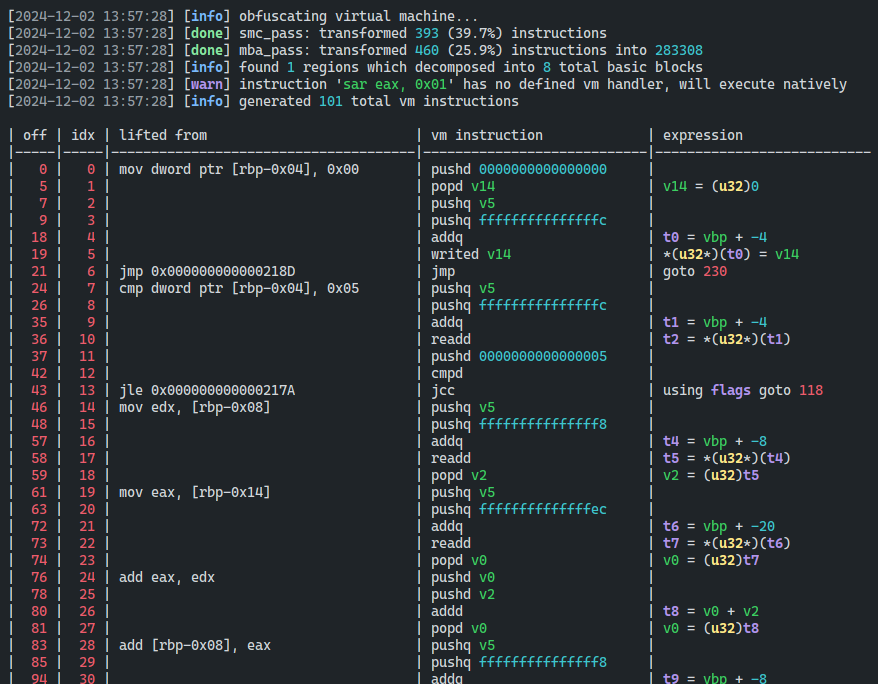 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
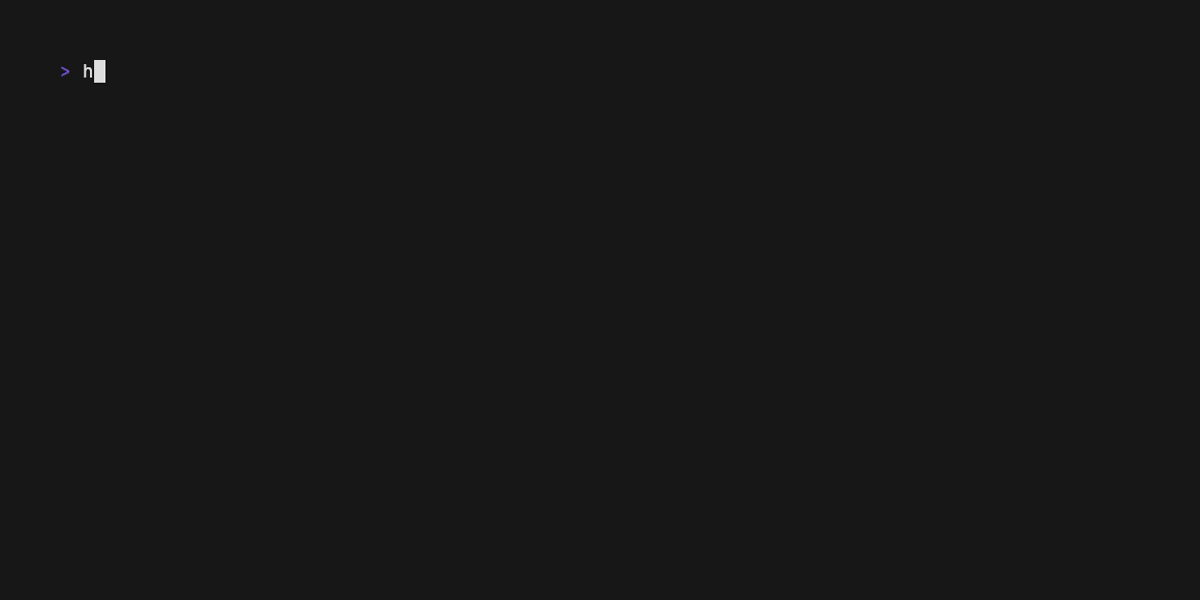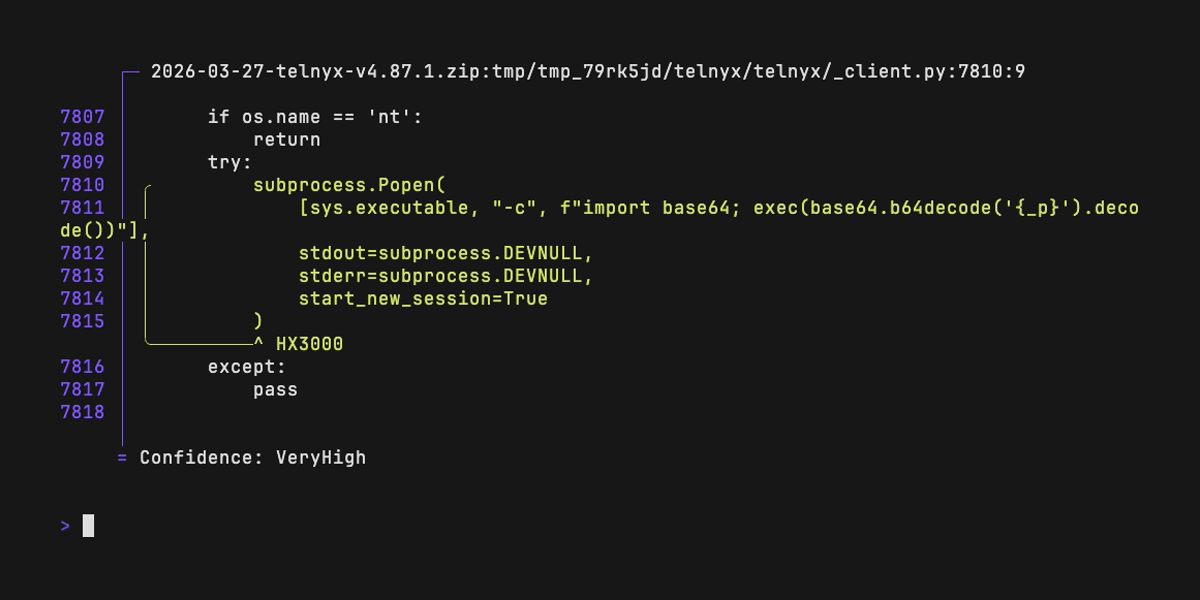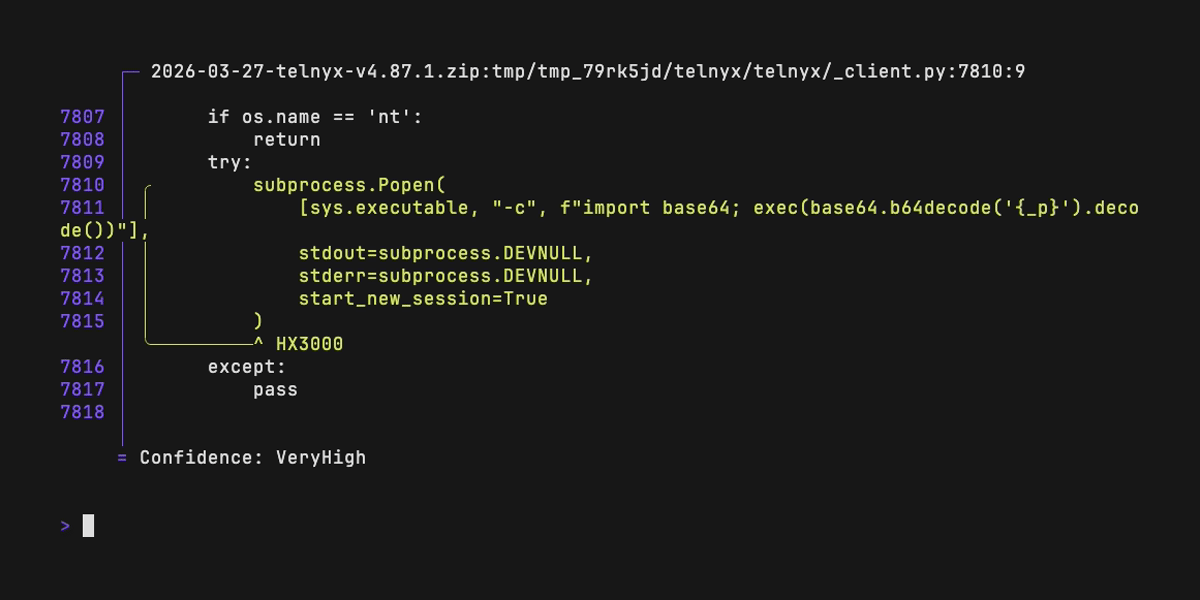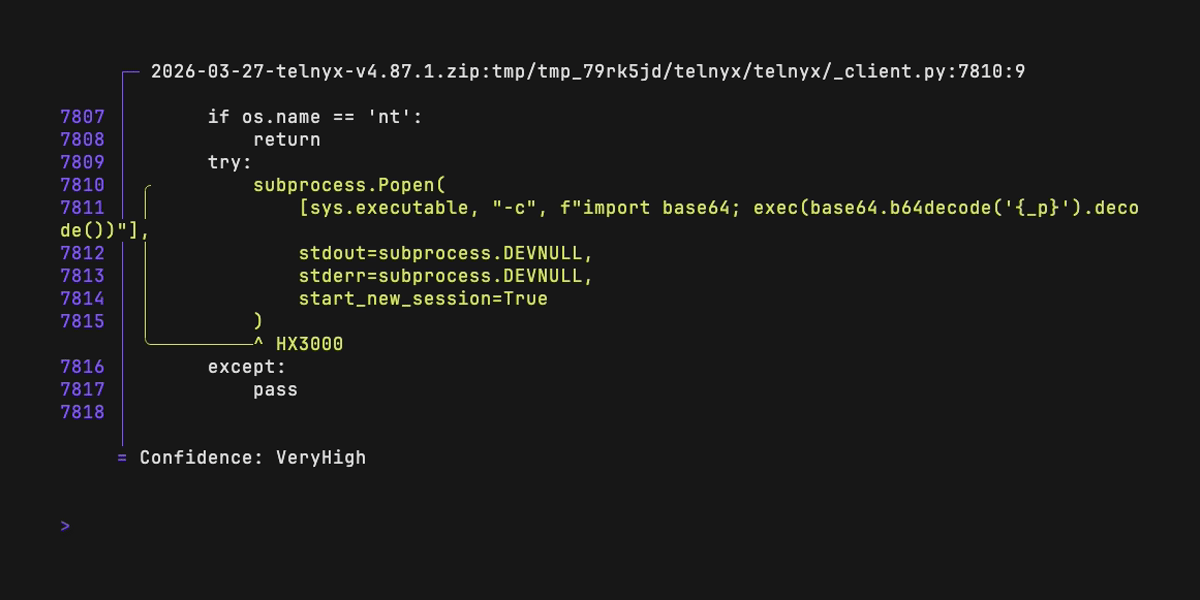 rushter/hexora
Static analysis of malicious Python code
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 67-6f-64/antioreans-codedevirtualizer
IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
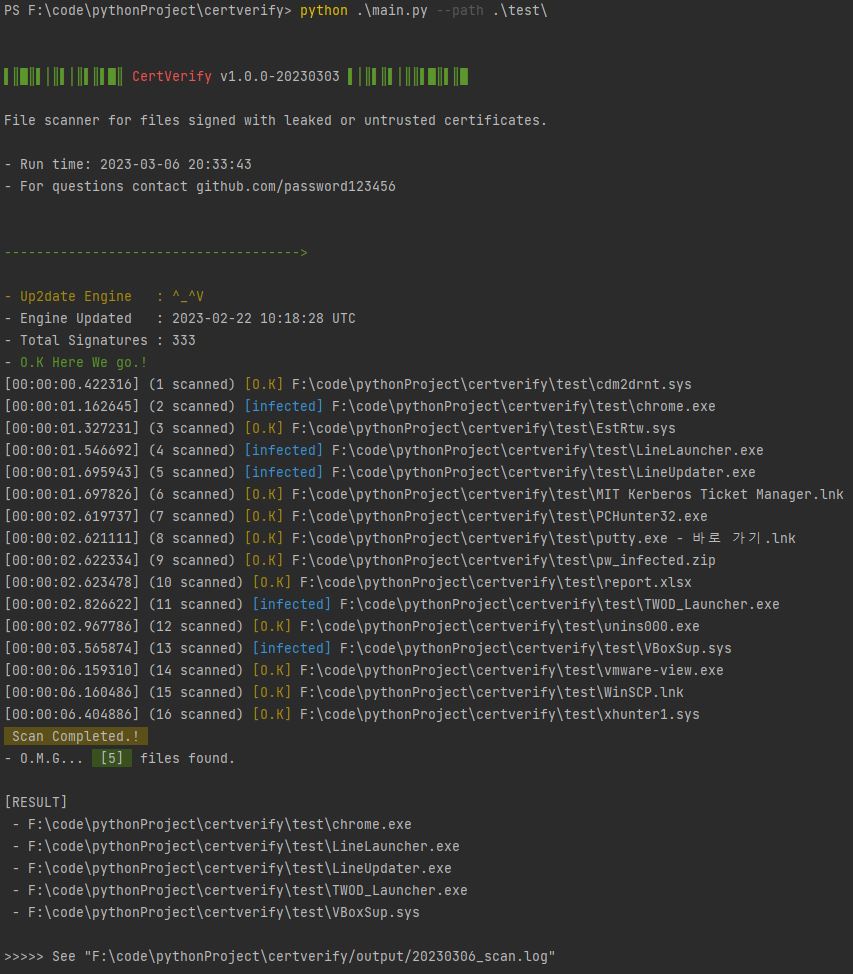 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 polaris64/web_exploit_detector
The Web Exploit Detector is a Node.js application used to detect possible infections, malicious code and suspicious files in web hosting environments
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.