
awesome-malware-analysis
 rshipp/awesome-malware-analysis
Defund the Police.
curated-resourceseducationforensics+10
14.2k
rshipp/awesome-malware-analysisDefund the Police.
 cisco-talos/clamav
Open-source antivirus engine for detecting trojans, viruses, and malware via signature-based scanning; includes a daemon, on-demand CLI, and…
 google/bindiff
Quickly find differences and similarities in disassembled code
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
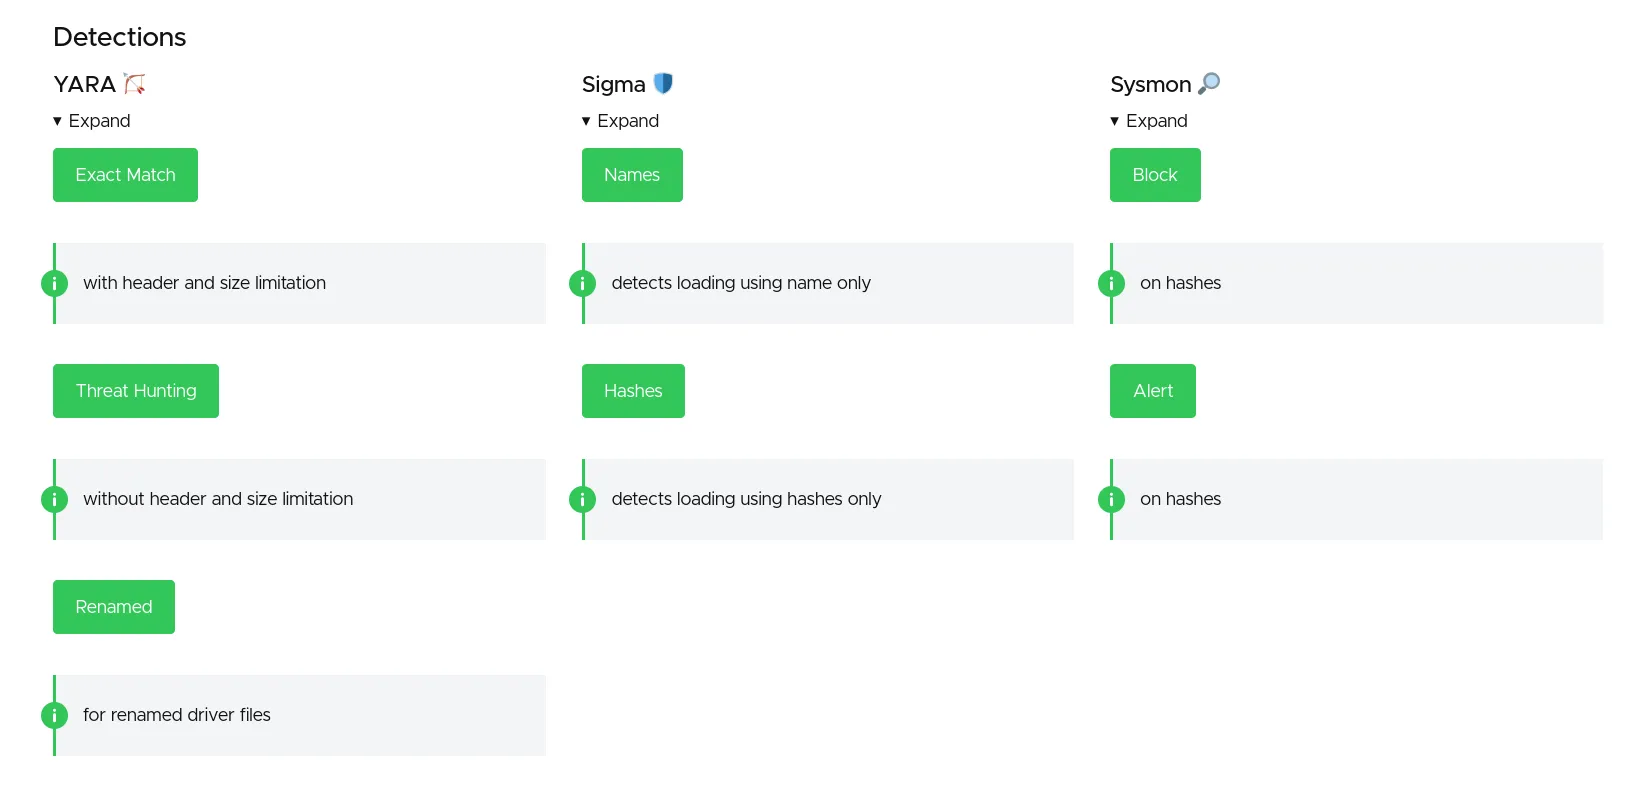 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 idanr1986/cuckoo-droid
CuckooDroid - Automated Android Malware Analysis with Cuckoo Sandbox.
 xacone/bestedrofthemarket
Open-source Windows kernel-level EDR lab for understanding and testing detection methods against process injection, credential dumping, and other…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 cert-ee/cuckoo3
Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
 cristianzsh/freki
Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
 helixo32/crimsonedr
Simulate the behavior of AV/EDR for malware development training.
 oalabs/hashdb-ida
HashDB API hash lookup plugin for IDA Pro
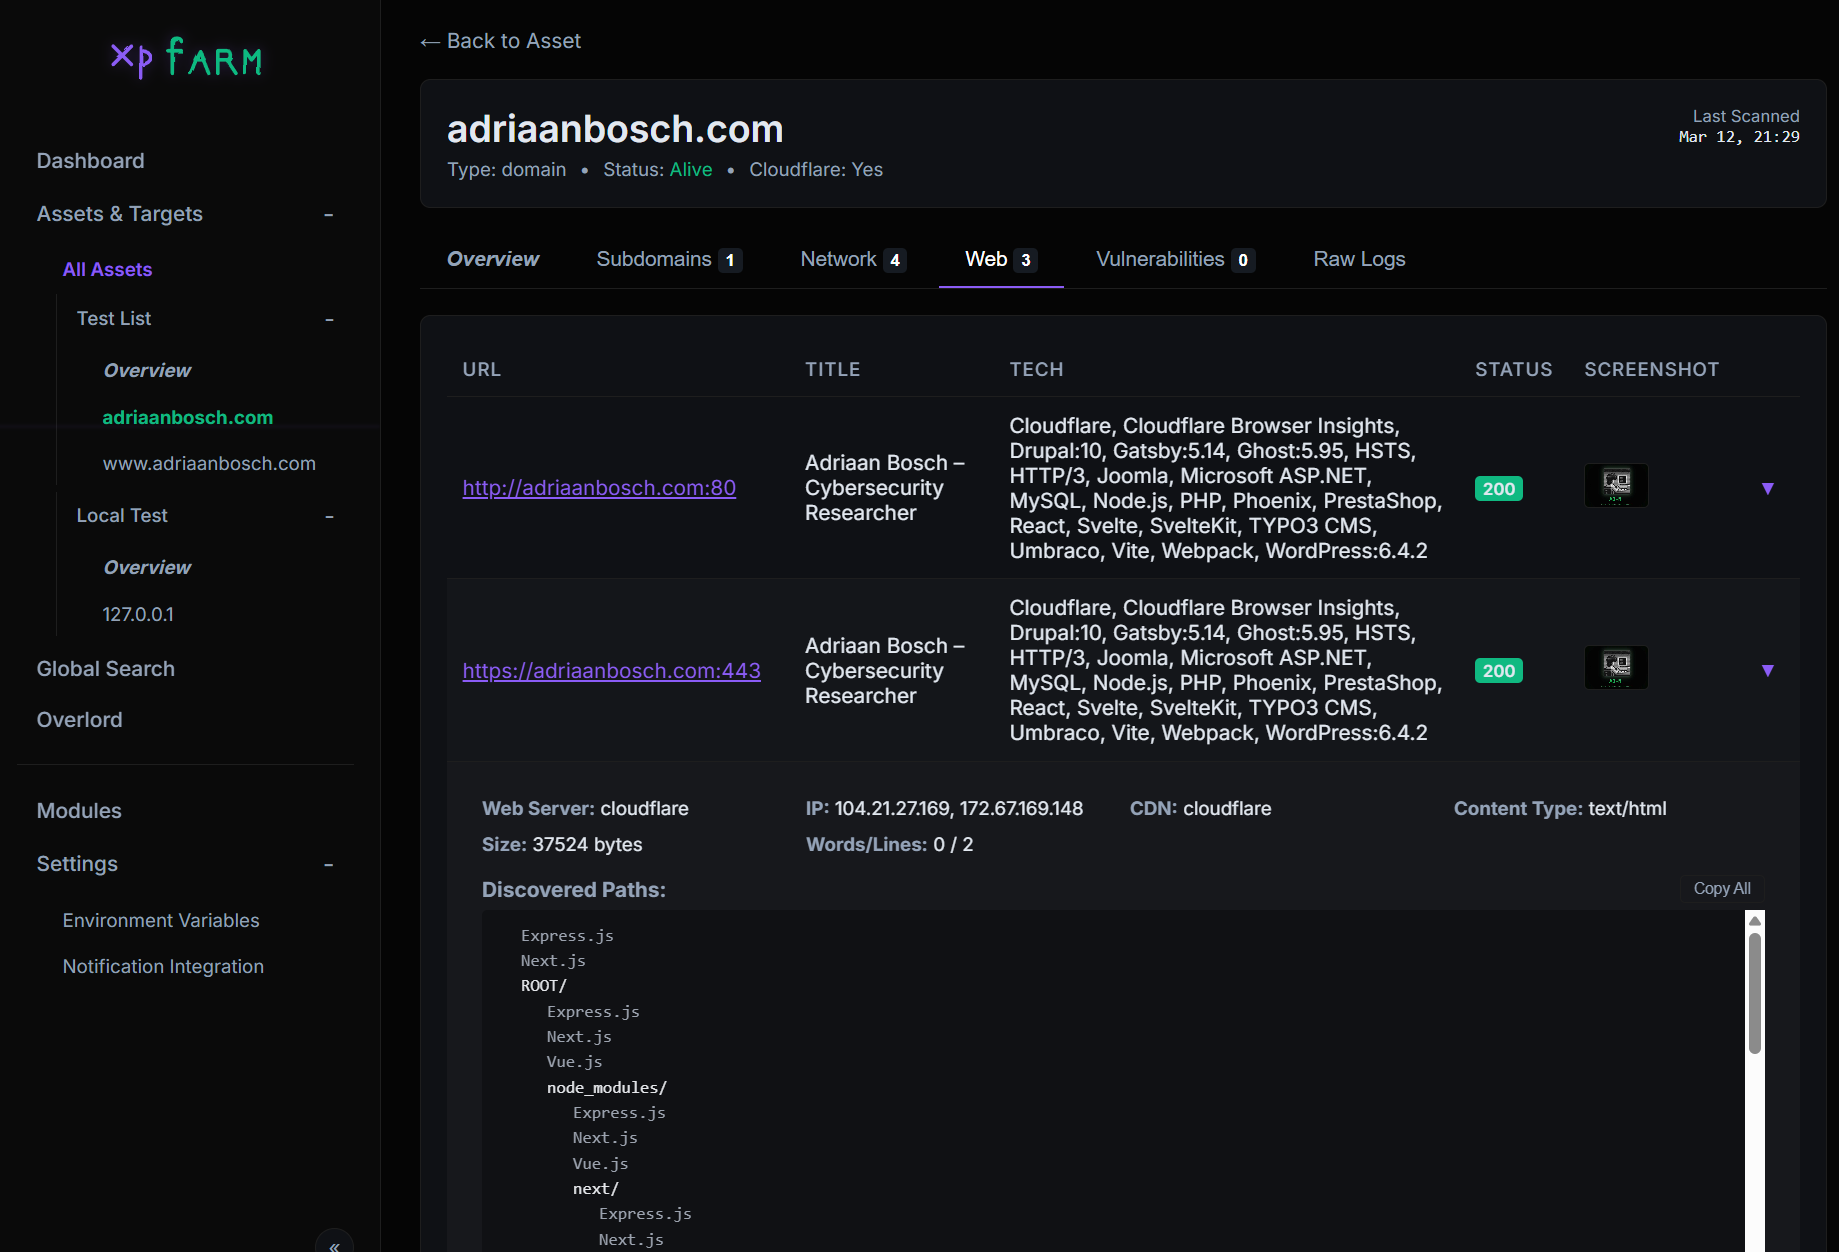 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 armadito/armadito-av
Armadito antivirus main repository
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
