

WhoamiAlternatives
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
information-gatheringmalware-analysispost-exploitation+2
187
ricardojoserf/whoamialternativesDifferent methods to get current username without using whoami
 lightspin-tech/red-detector
Automated vulnerability, misconfiguration, and rootkit scanner for AWS EC2 instances using Vuls, Lynis, and Chkrootkit via snapshot-based offline…
 0rshemesh/jadx-magic-strings
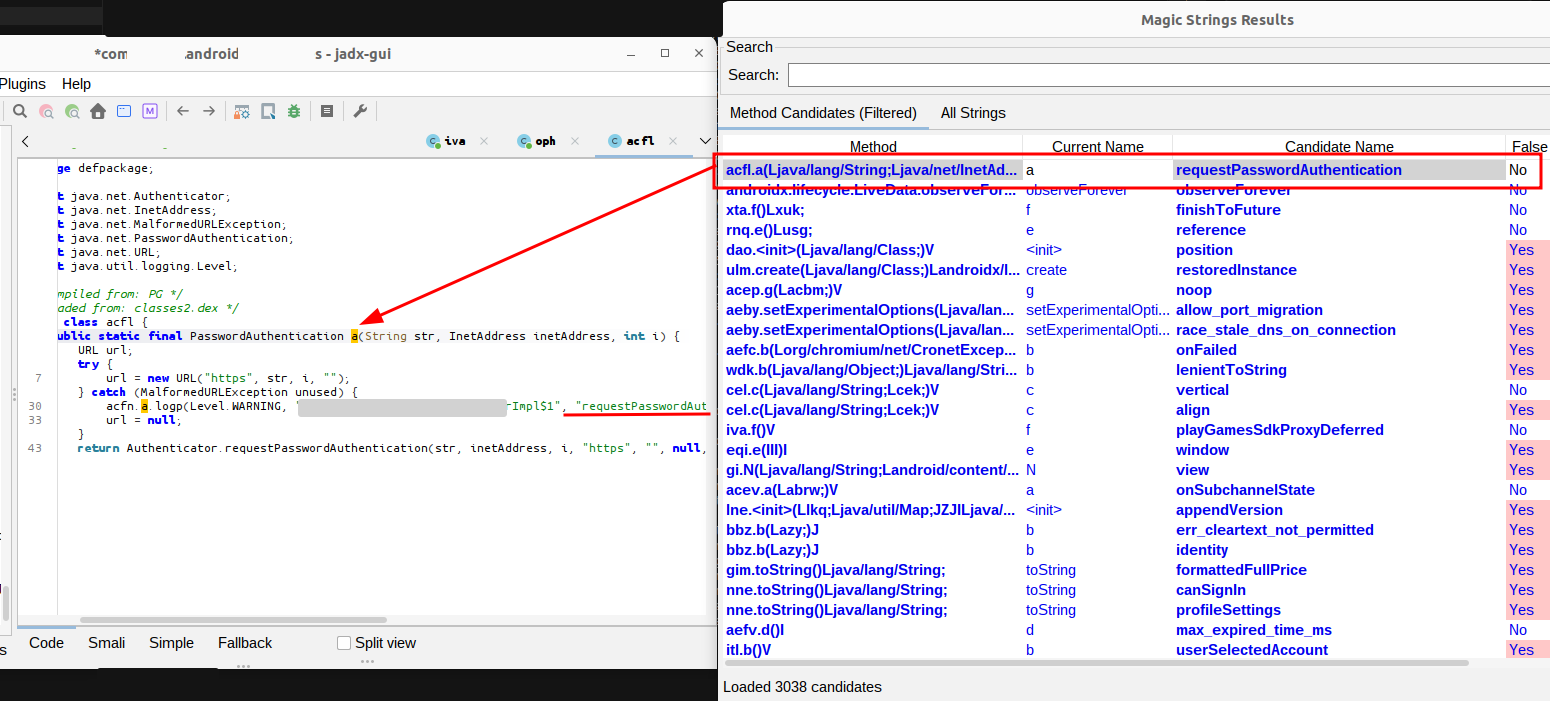
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.

 hasherezade/sig_finder
Signature finder (from PE-bear)
 murataydemir/greyenergy-mini-module-malware-analysis
GreyEnergy Mini Module Malware Analysis (Turkish)
 anjai7/tryhack3m-bricks-heist
TryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification
 hluwa/frida-dexdump
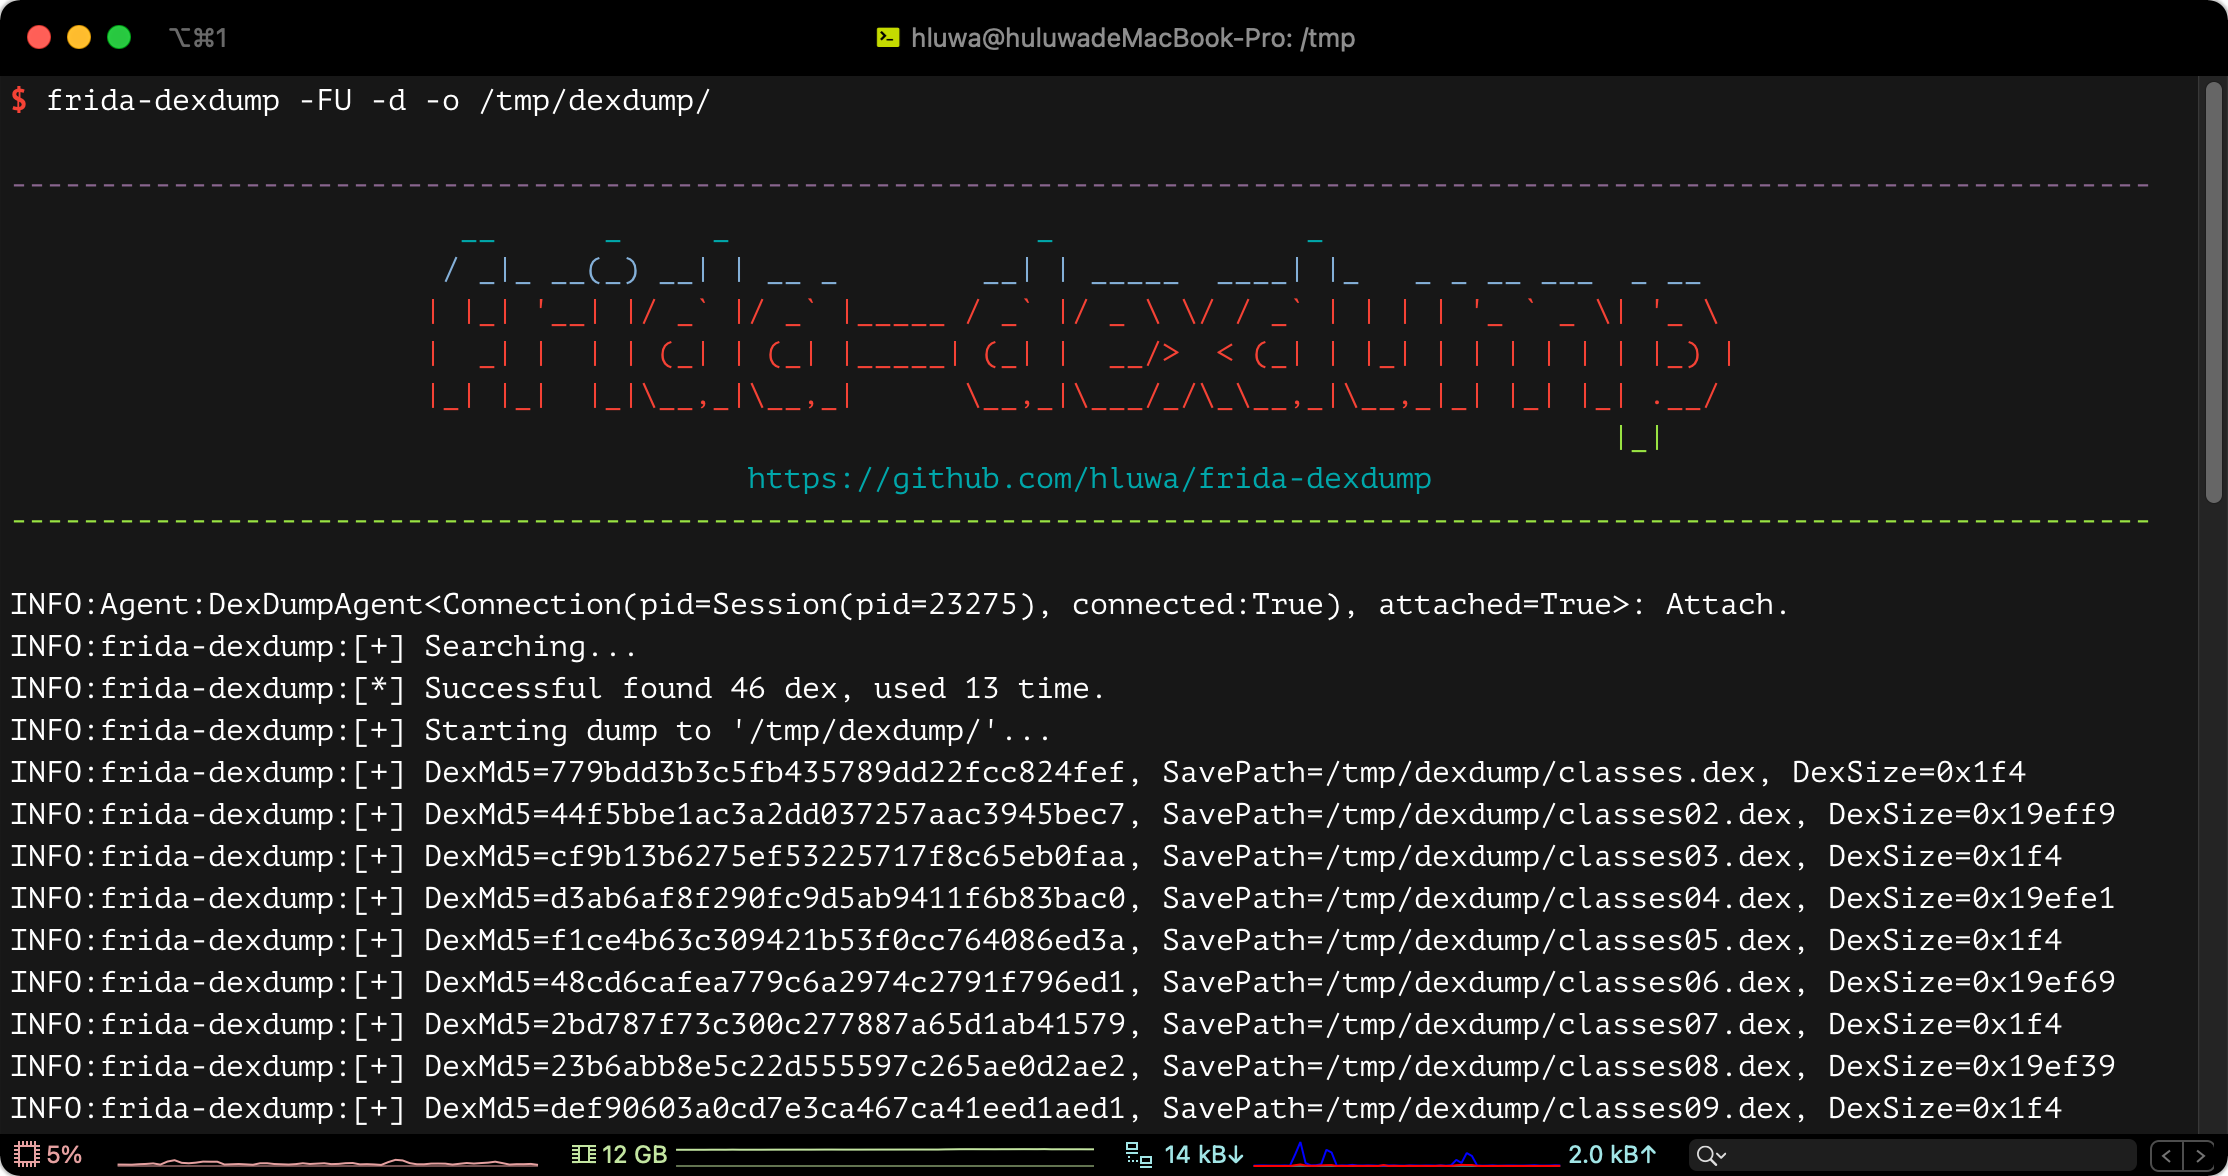
A frida tool to dump dex in memory to support security engineers analyzing malware.
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 volatilityfoundation/community
Community-maintained Volatility plugin collection for memory forensics, extending memory dump analysis with modules for malware and process…
 marcosd4h/memhunter
Live hunting of code injection techniques
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
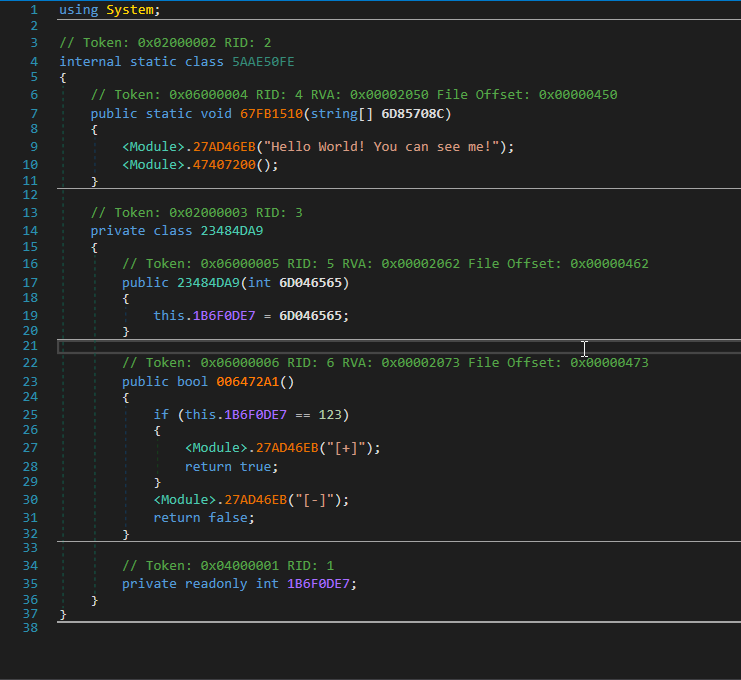 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
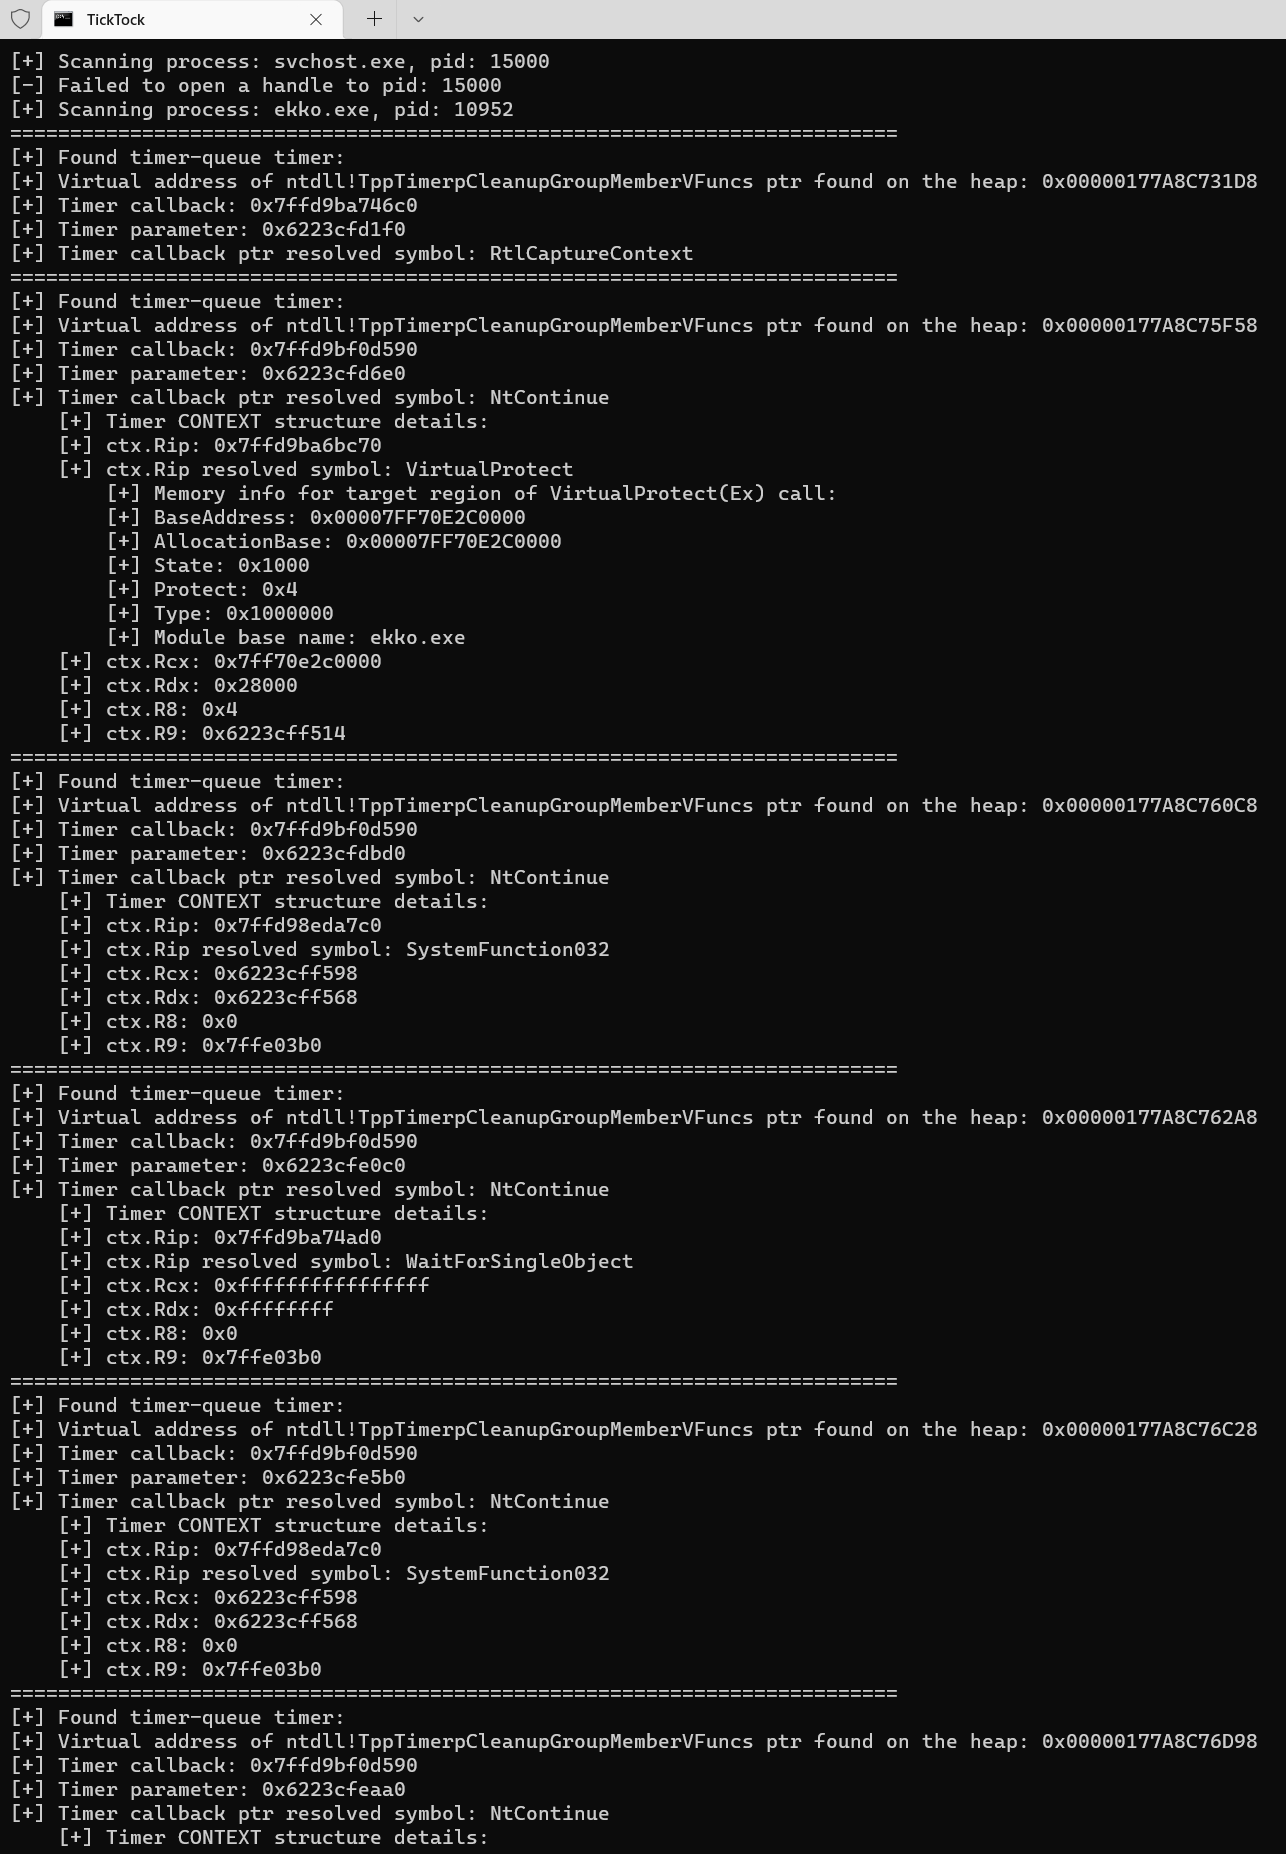 withsecurelabs/ticktock
Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…