PoC-and-yara-rules-of-CVE-2025-59528-Flowise-has-Remote-Code-Execution-vulnerability

Proof-of-concept exploit and YARA detection rules for CVE-2025-59528, a remote code execution vulnerability in Flowise, intended for authorized…

Proof-of-concept exploit and YARA detection rules for CVE-2025-59528, a remote code execution vulnerability in Flowise, intended for authorized…

Firefox/Tor Browser 0day exploit analysis (CVE-2024-9680) A UAF in animation timelines leading to RCE. Patched.

Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…

CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit

CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV

Exploit for CVE-2026-21509, a Microsoft Office OLE validation bypass using a speculative race-condition technique to evade AMSI/EDR and achieve code…

YARA rule and python script to detect potential exploits for the CVE-2026-21509 vulnerability in MS Office

Proof-of-concept exploit for CVE-2025-0411, demonstrating Mark-of-the-Web bypass in 7-Zip to enable arbitrary code execution via crafted archives…

Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE

Proof-of-concept exploit for CVE-2019-6440 achieving SYSTEM privilege escalation on Zemana antimalware via man-in-the-middle update interception and…

Educational analysis of the Log4Shell (CVE-2021-44228) vulnerability, detailing its exploitation in a cryptocurrency mining campaign with IoCs, MITRE…

Real-world attack analysis of CVE-2025-55182 (React2Shell) - React Server Components RCE vulnerability

Automated vulnerability, misconfiguration, and rootkit scanner for AWS EC2 instances using Vuls, Lynis, and Chkrootkit via snapshot-based offline…

The Web Exploit Detector is a Node.js application used to detect possible infections, malicious code and suspicious files in web hosting environments

Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…

Script to extract malicious payload and decoy document from CVE-2015-1641 exploit documents

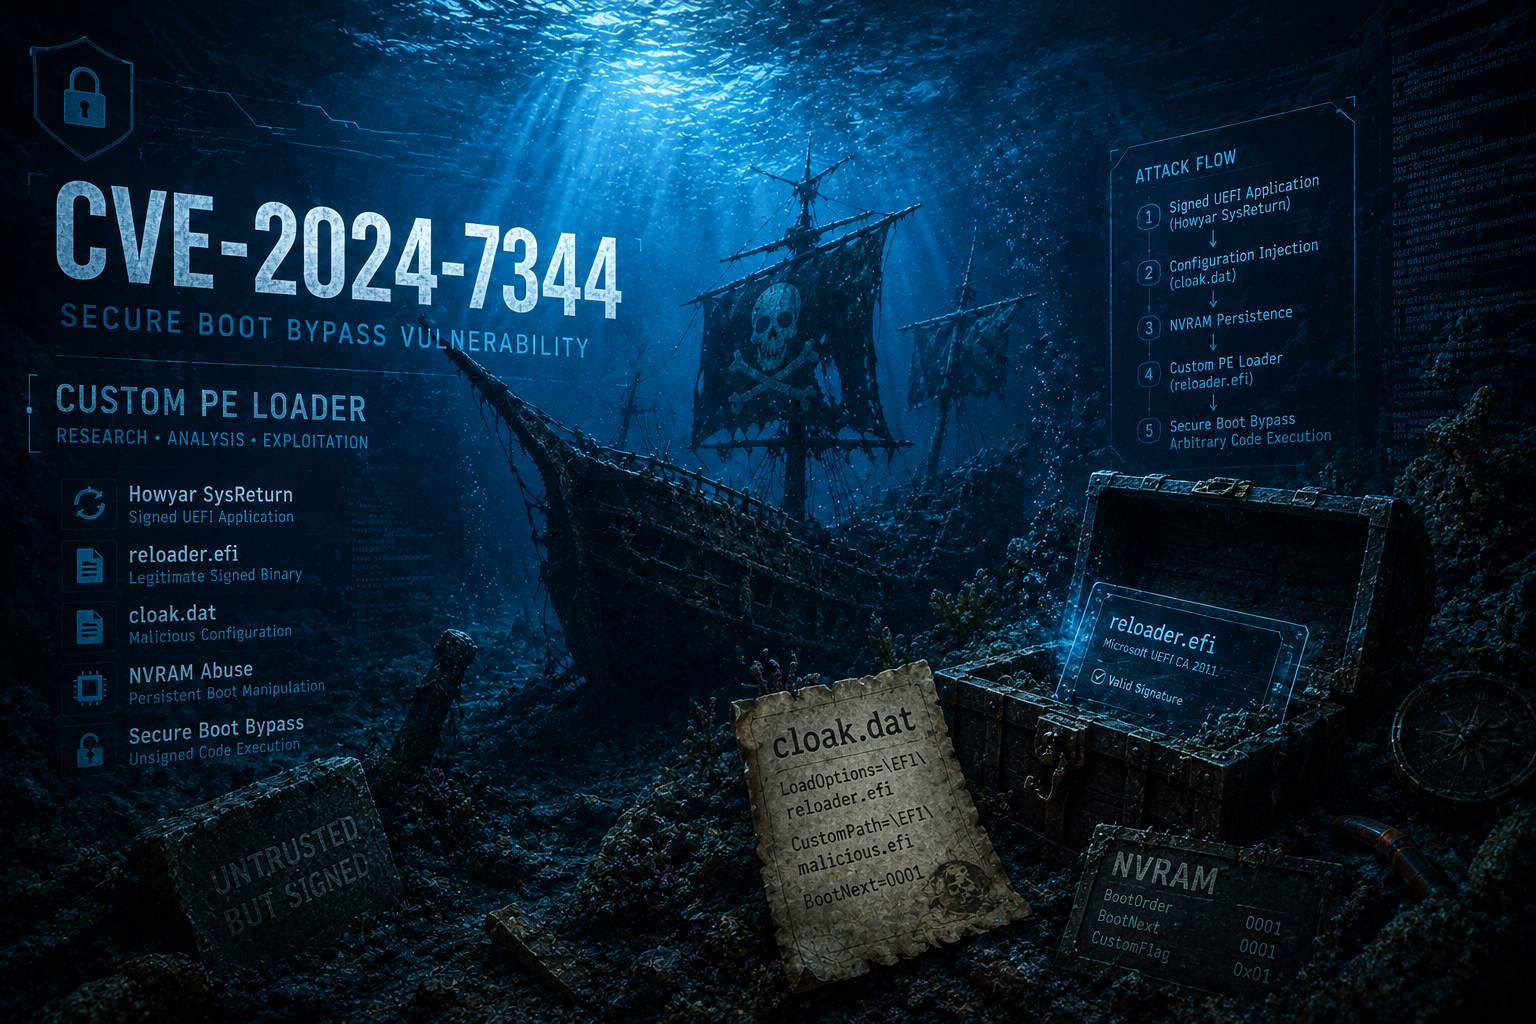
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…

Proof-of-concept exploit for CVE-2026-33057, an unauthenticated RCE in Mesop, with accompanying YARA rules for detection.