

Yara-Rules
 pandare9x/yara-rules
Repository of Yara Rules
curated-resourcesdefensive-toolsmalware-analysis+2
pandare9x/yara-rulesRepository of Yara Rules
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 limo57640-crypto/cpanel-cve-41940-detector
Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
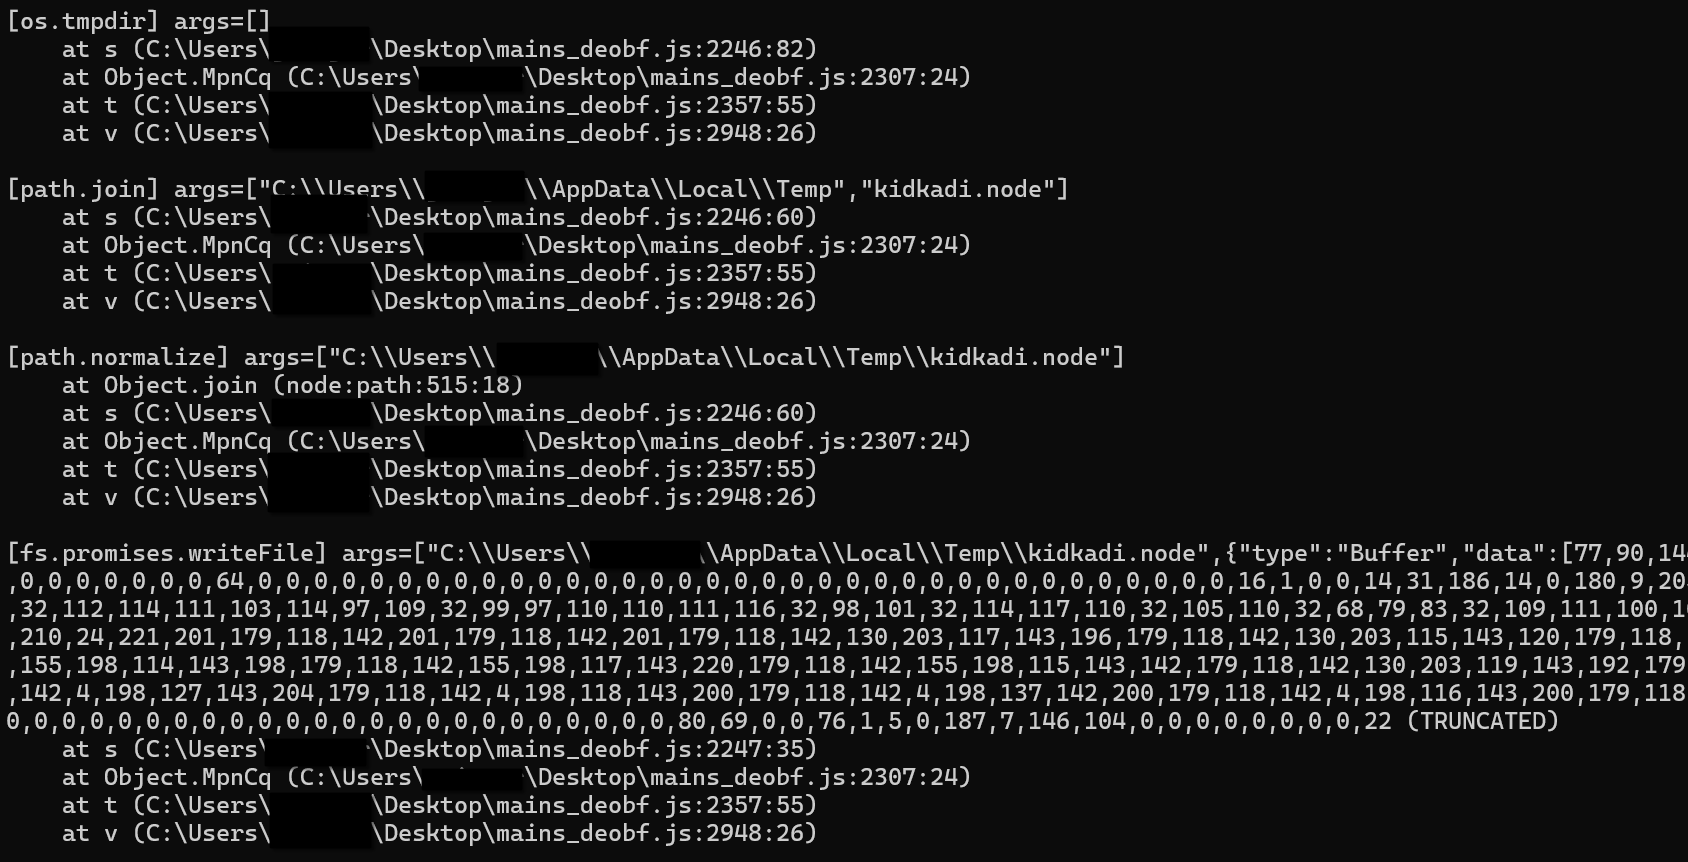 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 password123456/malwarescanner
Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
 deividasterechovas/soc335-cve-2024-49138-exploitation-detected
Documented incident response case for CVE-2024-49138 exploitation, featuring log analysis, hash validation, C2 detection, and containment procedures…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
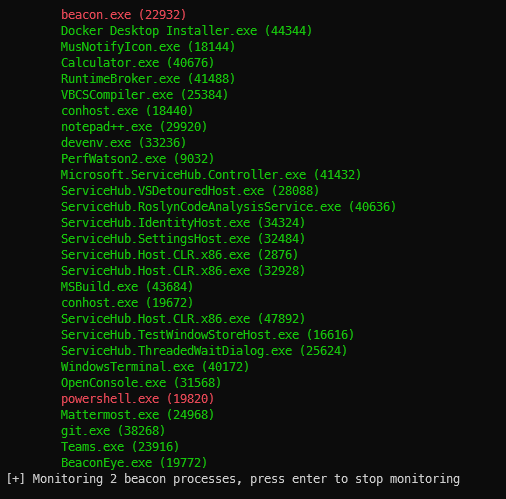 ccob/beaconeye
Hunts out CobaltStrike beacons and logs operator command output
 sh1n0g1/z9
Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
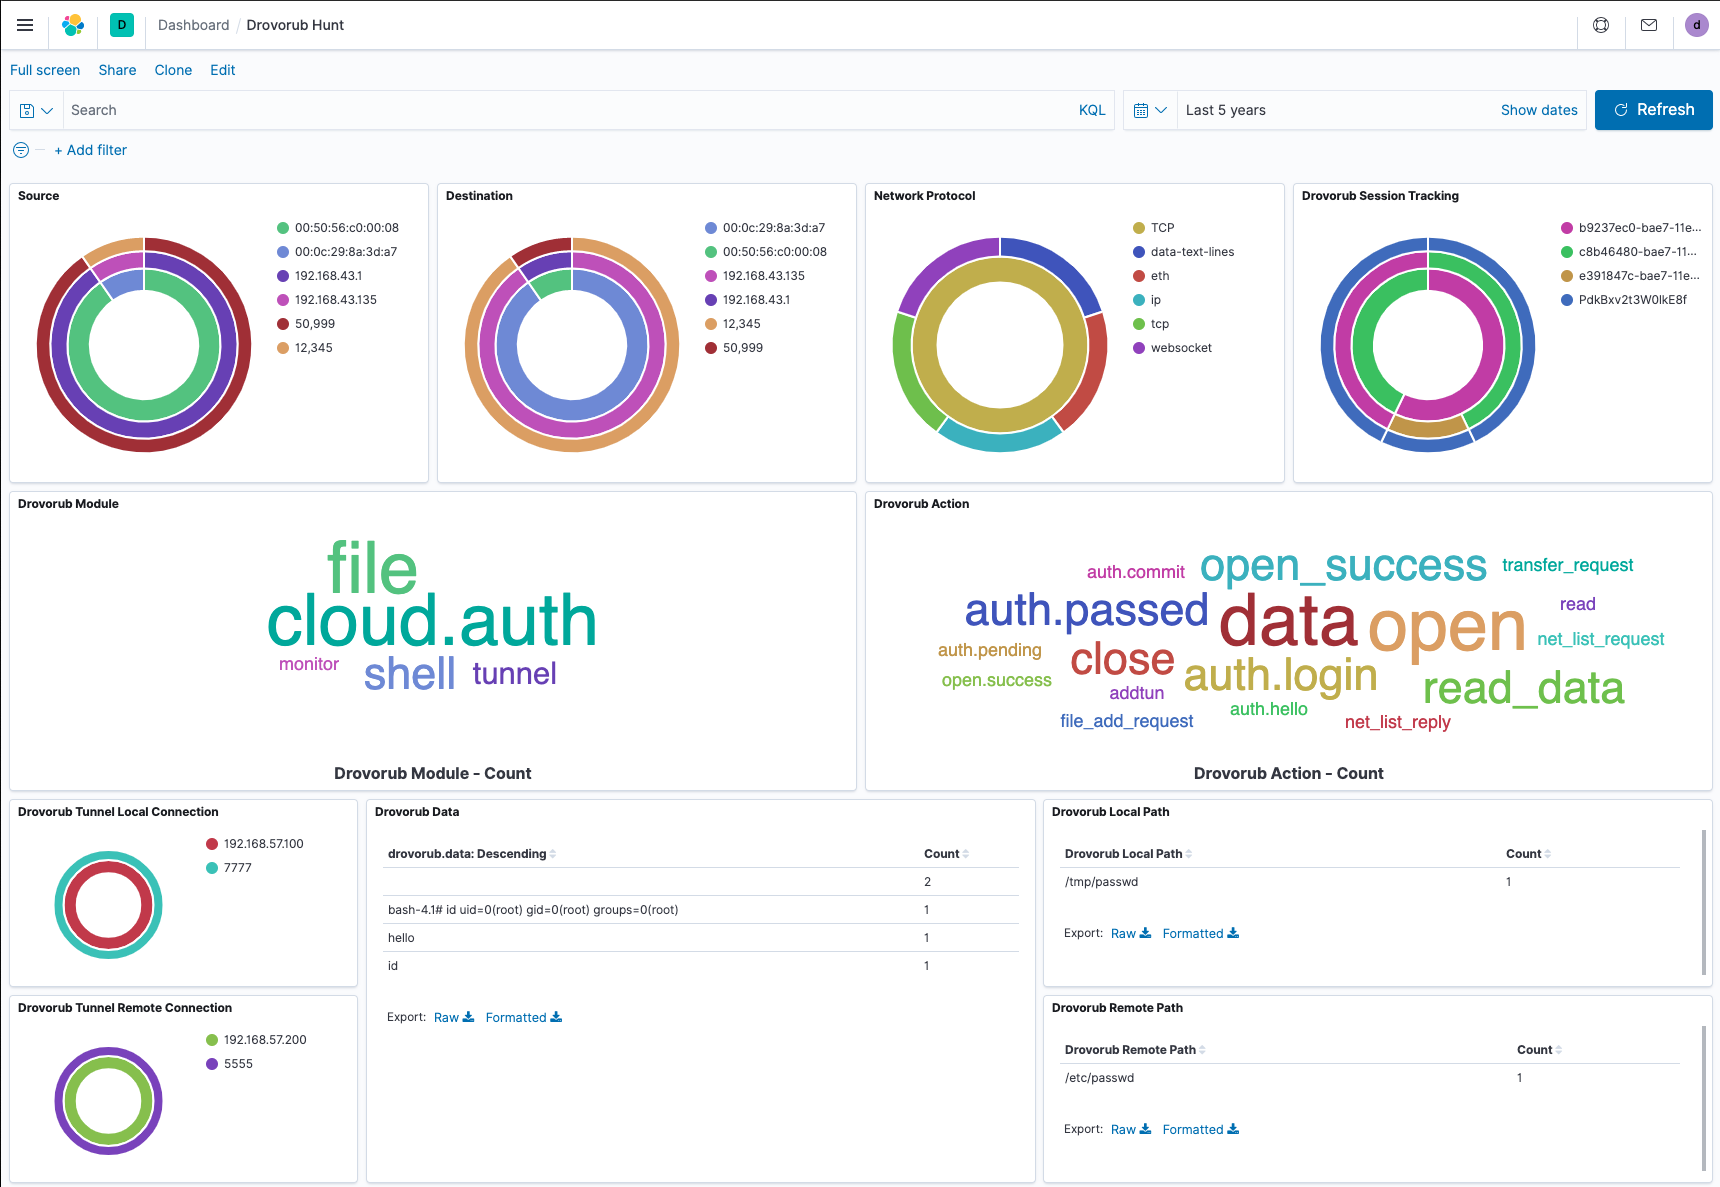 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
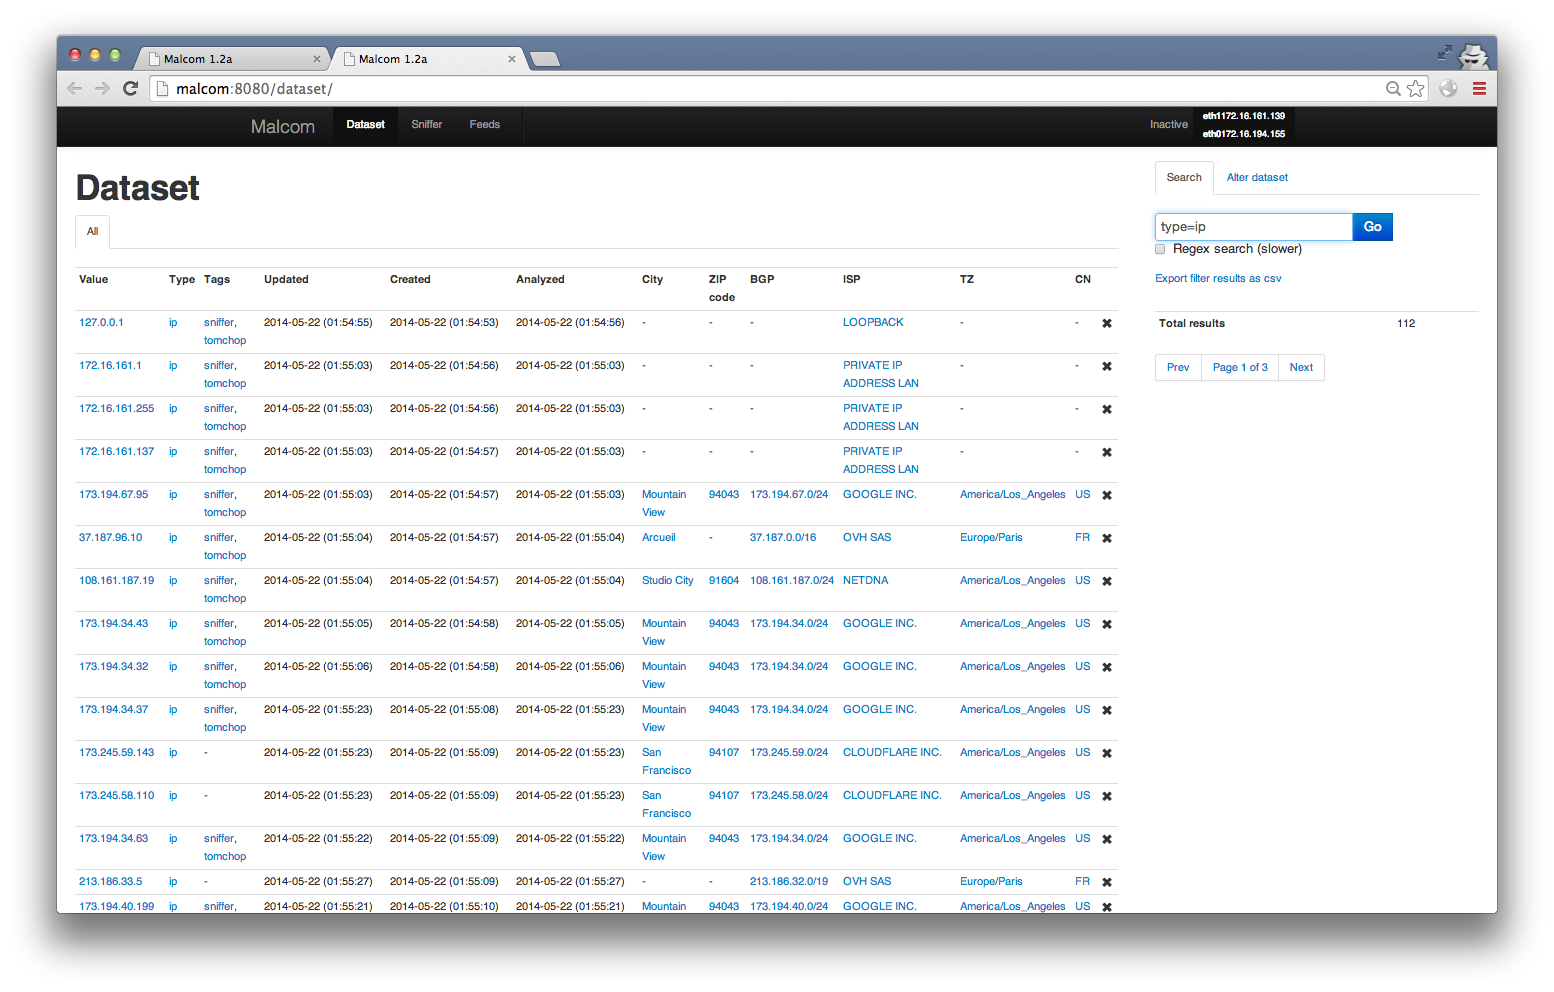 tomchop/malcom
Malcom - Malware Communications Analyzer