

MANTIS
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
ai-securitybinary-analysisinformation-gathering+7
fareedfauzi/mantisMulti-Sources Analysis & Threat Intelligence Search
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
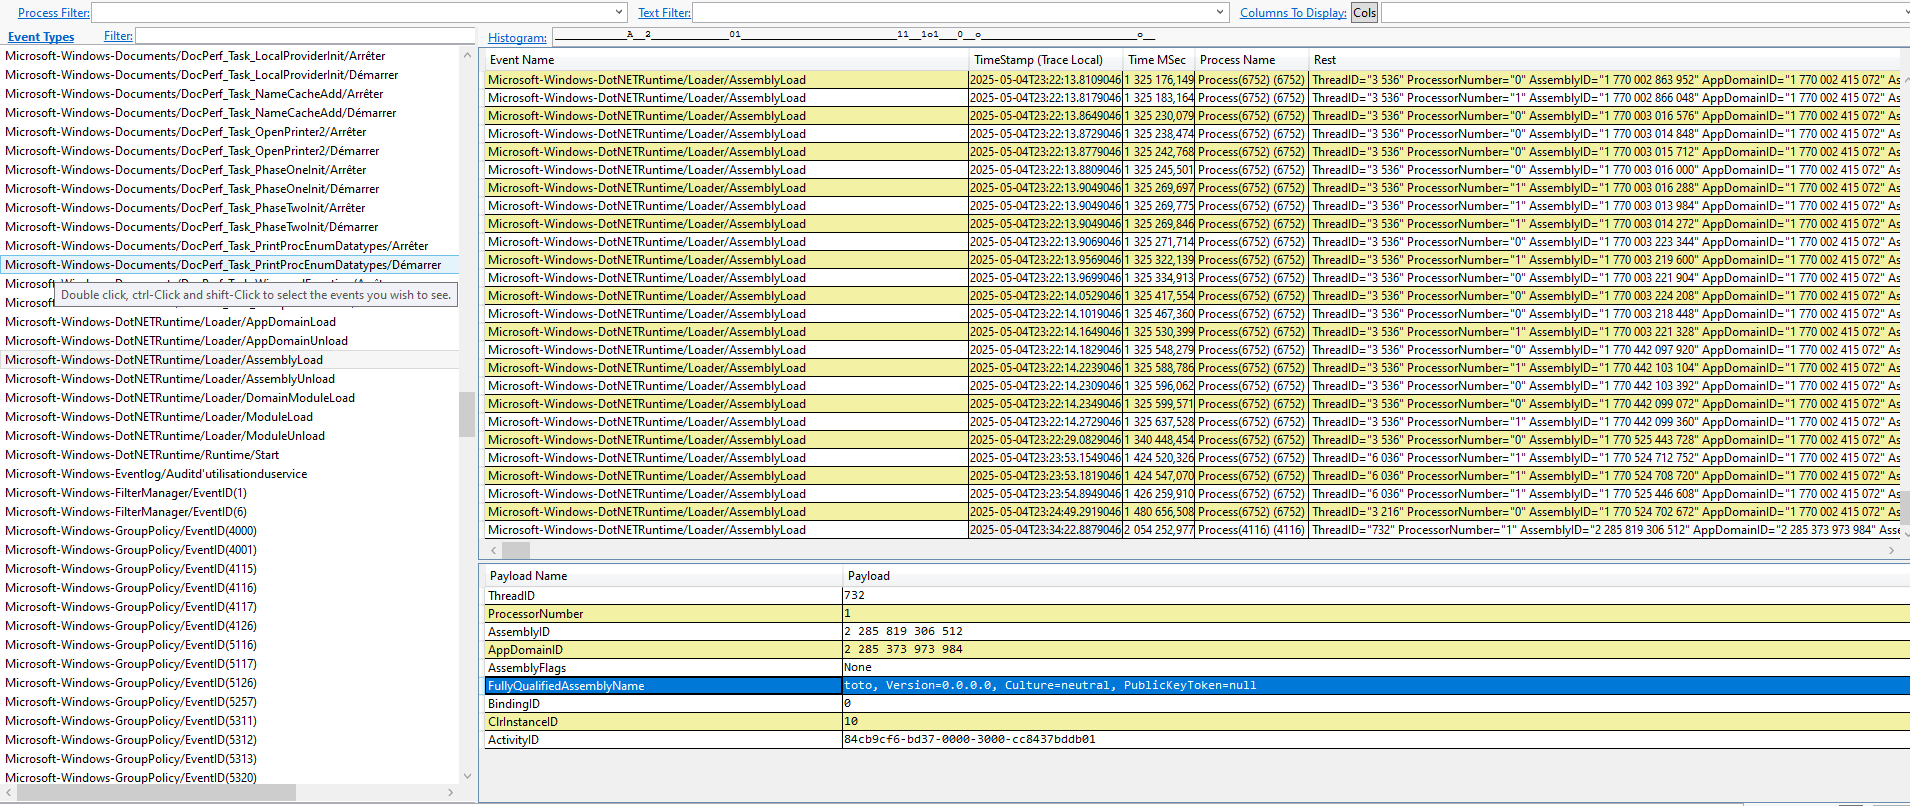 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 destiny-creates/goxlr-malware-family
Malware analysis from the domain goxlr.net
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
 mrprogrammer2938/black-tool
Install the tools and start Attacking , black-tool v5.5.5 ! ⬛
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
 cy83rr0h1t/cve-2023-20052
CVE-2023-20052 information leak vulnerability in the DMG file parser of ClamAV
 amorath/threatscraper
Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…