

so-crates
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
container-securitydigital-forensicseducation+8
6062 days ago
dougburks/so-cratesSO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
 target/strelka
Real-time, container-based file scanning at enterprise scale
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 makitos666/cve-2026-31431-copy-fail-detection-toolkit
Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…
 extracoding-dozen/cve-2024-3094
Research of CVE-2024-3094 vulnerability.
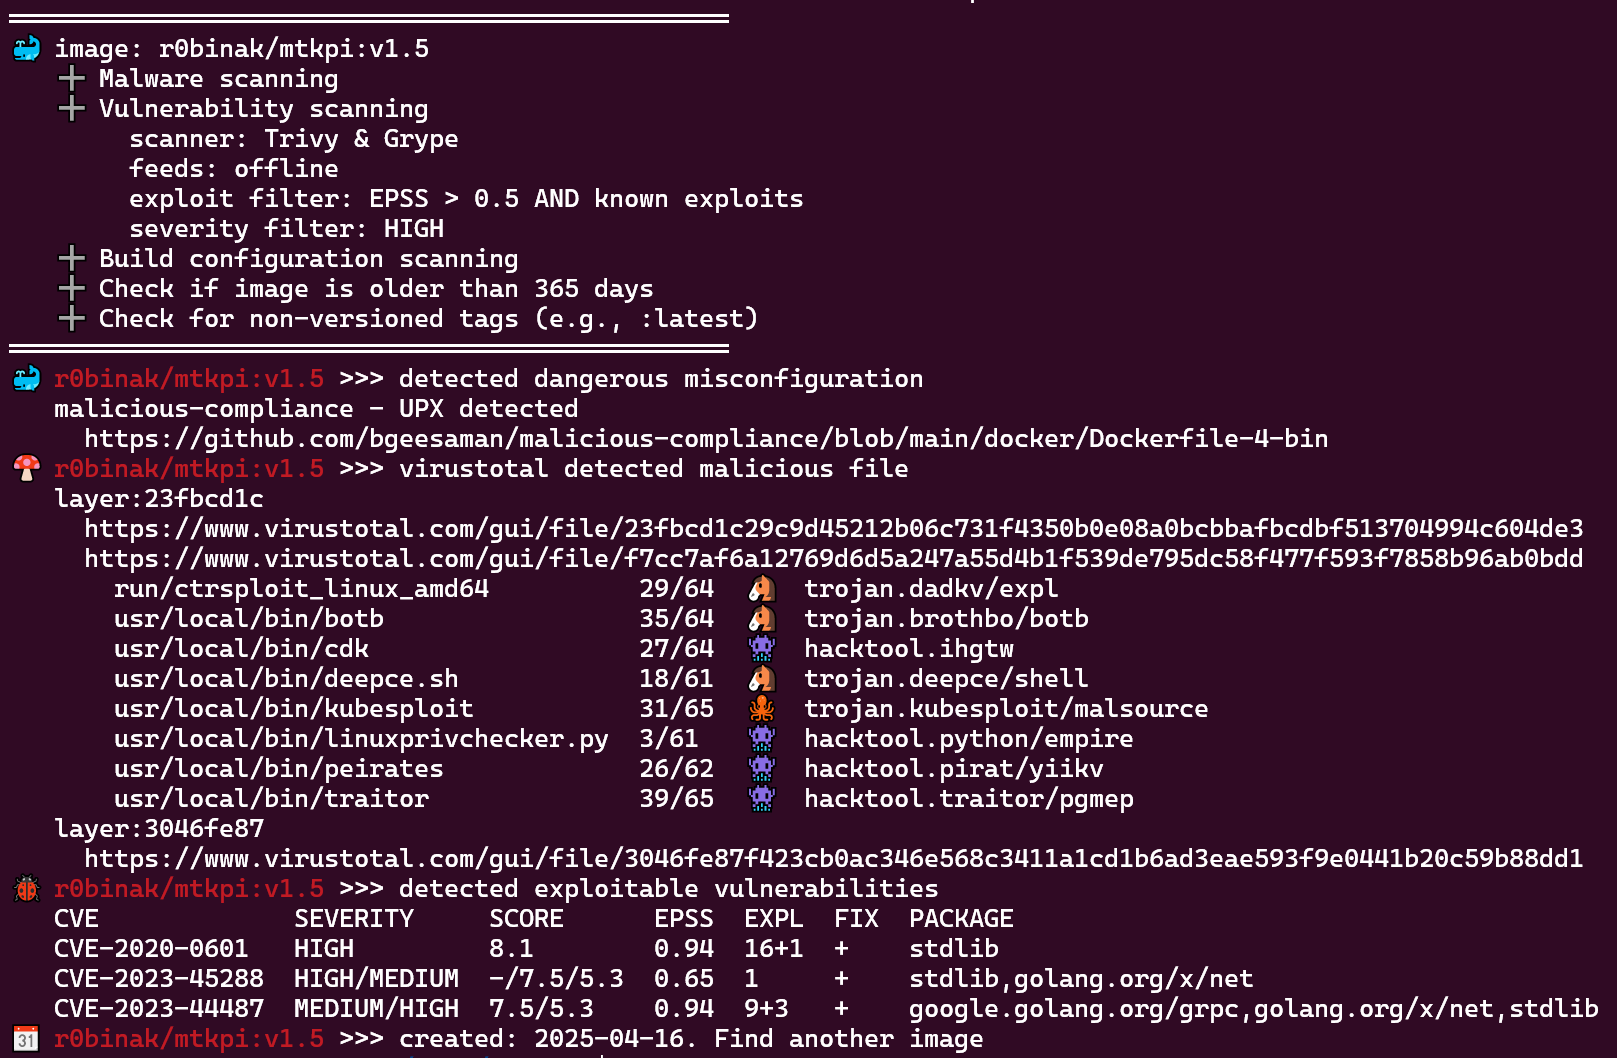 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 kube-tarian/tarian
eBPF-based runtime security agent for Kubernetes that detects unknown processes and file changes, enforces pre-registered constraints, and automates…
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.