
PortEx
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
anomaly-detectionbinary-analysisforensics+3
5431 day ago
struppigel/portexJava library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 google/bindiff
Quickly find differences and similarities in disassembled code
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 hassan-pouladi/cisco-fmc-honeypot
Originally a Honeypot for CVE-2026-20131
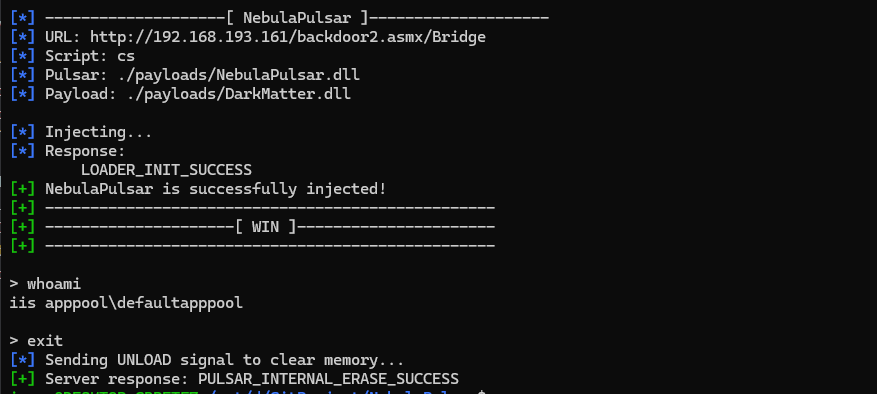 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
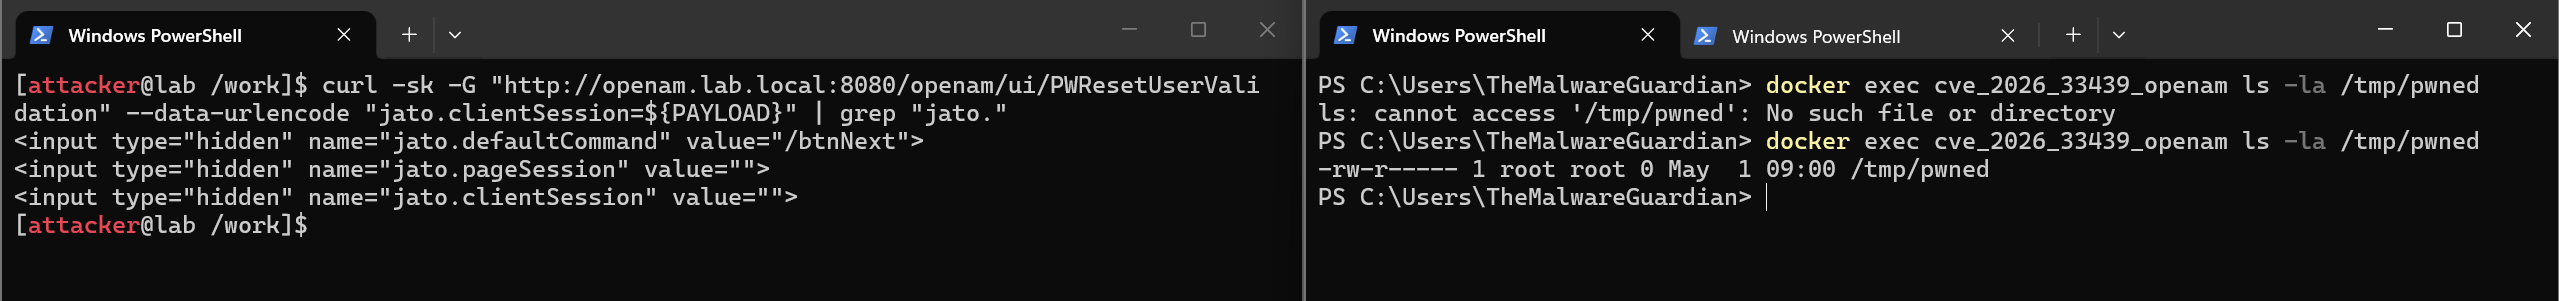 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
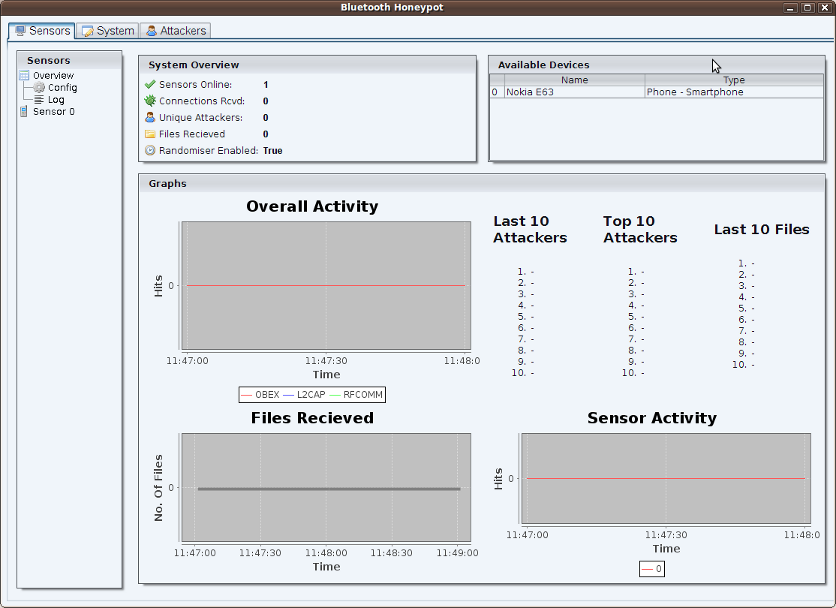 andrewmichaelsmith/bluepot
Java-based Bluetooth honeypot that captures and stores malware from BlueBugging and BlueSnarfing attacks, with a GUI for monitoring and log analysis.
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
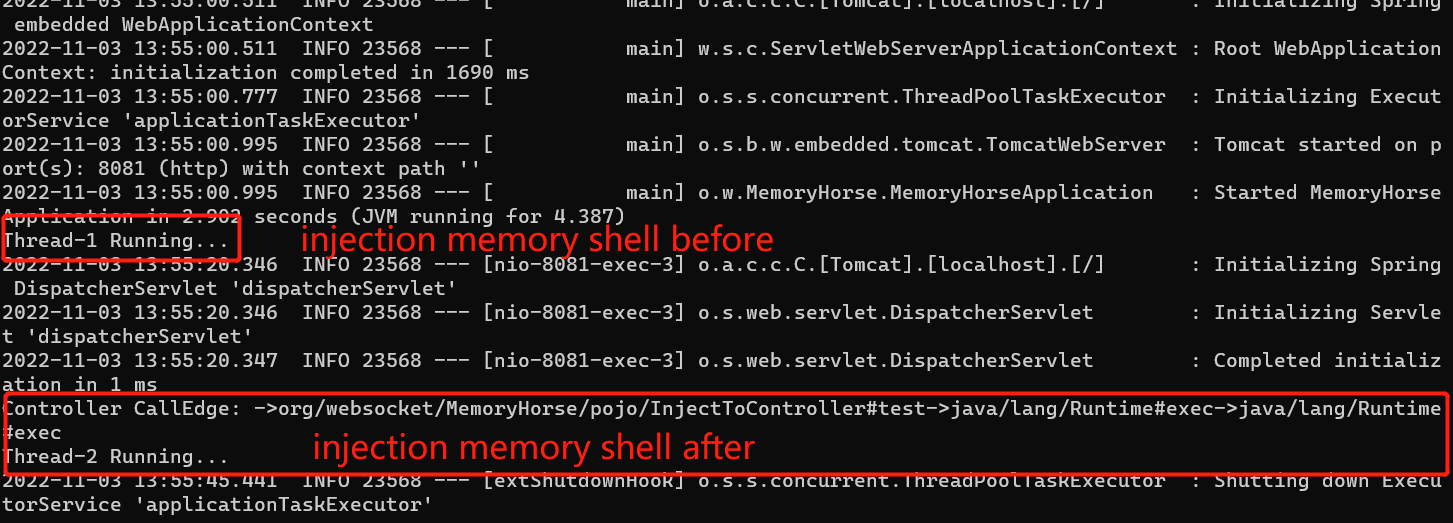 sf197/memoryshellhunter
Java Agent memory horse scanner combined with Call Graph modus
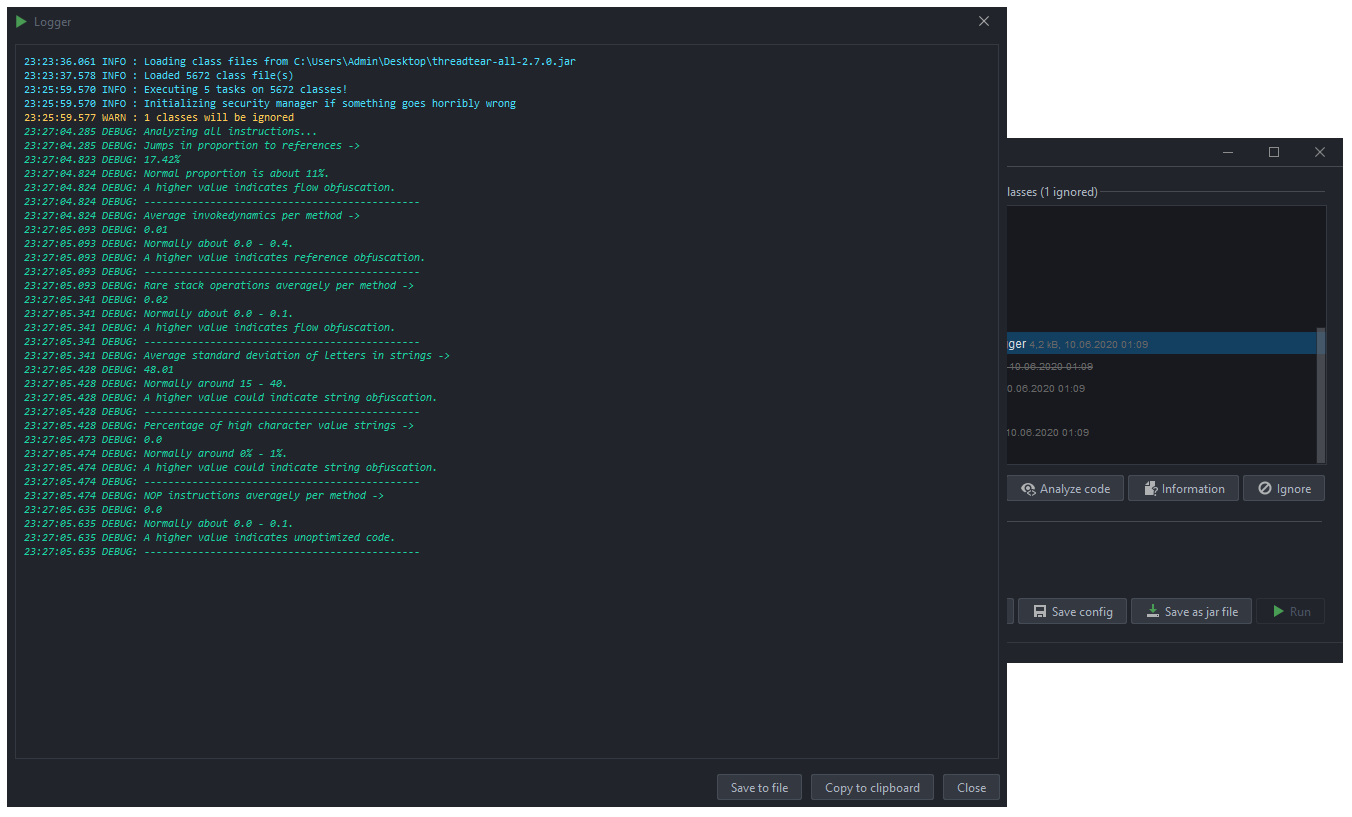 loerting/threadtear
Multifunctional java deobfuscation tool suite
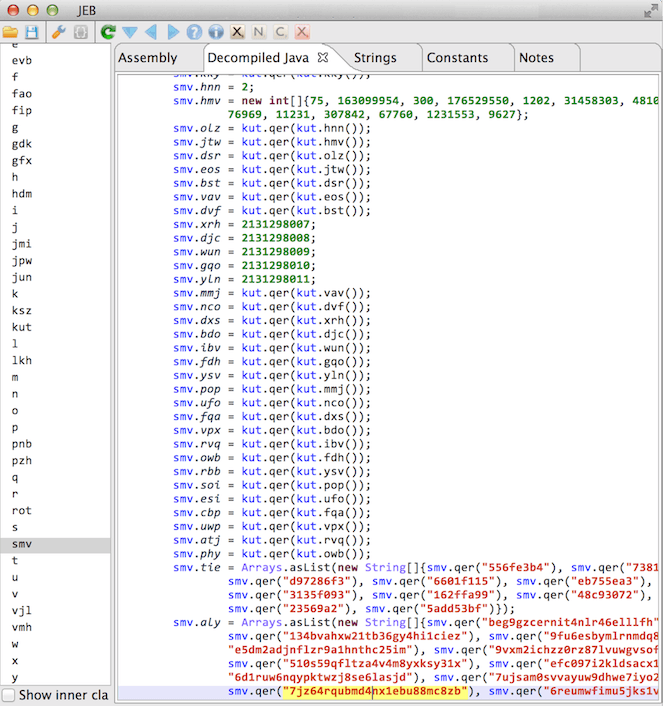 calebfenton/simplify
Android virtual machine and deobfuscator
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan