
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
magika preview

magika

GitHubgoogle/magika

Fast and accurate AI powered file content types detection

code-analysisforensicsgeneral-purpose-utilities+3
18.7k17h 37m ago
fibratus preview

fibratus

GitHubrabbitstack/fibratus

Security sensor for realtime threat detection and protection

defensive-toolsforensicsincident-response+3
2.5k5 days ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
digital-forensicsforensicsincident-response+2
4.4k7 days ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

You didn't think I'd go and leave the blue team out, right?

curated-resourcesdigital-forensicseducation+5
1.8k14 days ago
IntelOwl preview

IntelOwl

GitHubintelowlproject/intelowl

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
curated-resourcesdigital-forensicsdynamic-analysis-sandboxing+14
4.7k22 days ago
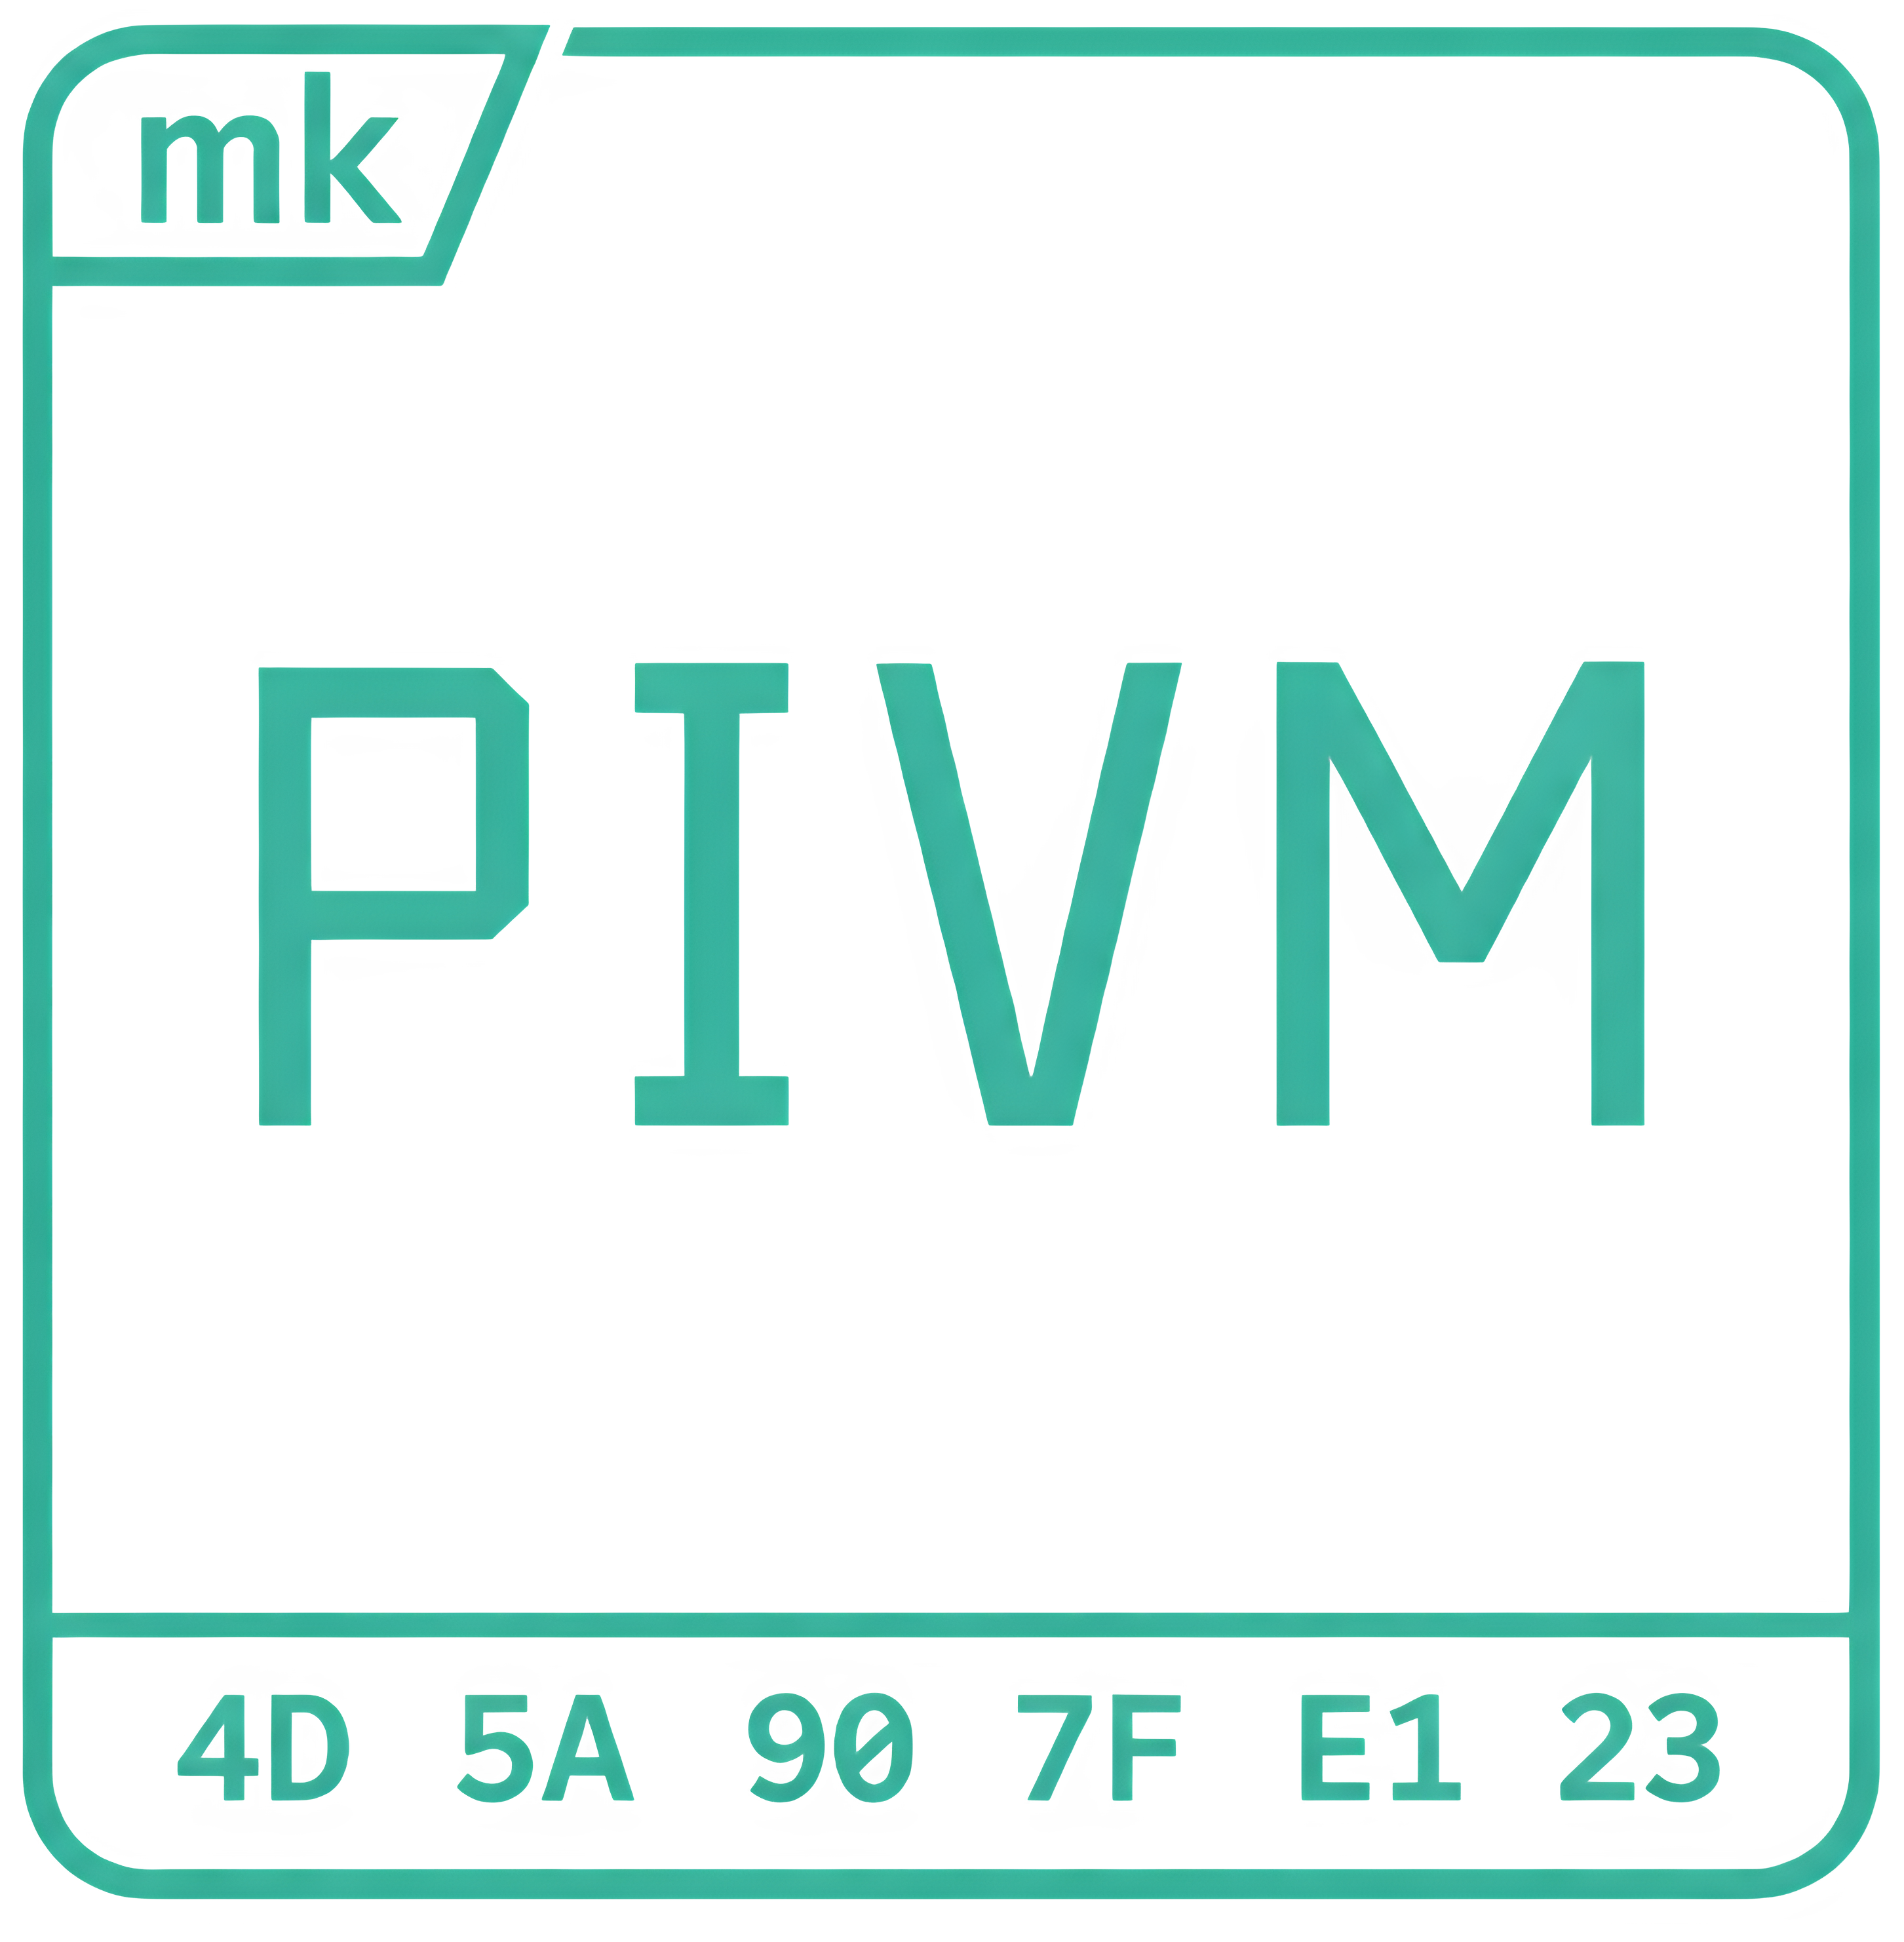
droidlysis preview

droidlysis

GitHubcryptax/droidlysis

Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
android-securityinformation-gatheringmalware-analysis+3
31228 days ago
mkPIVM preview

mkPIVM

GitHubd7ead/mkpivm

Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
exploitationmalware-analysispayload-generation+3
3861 month ago
Adamantium-Thief preview

Adamantium-Thief

GitHublimerboy/adamantium-thief

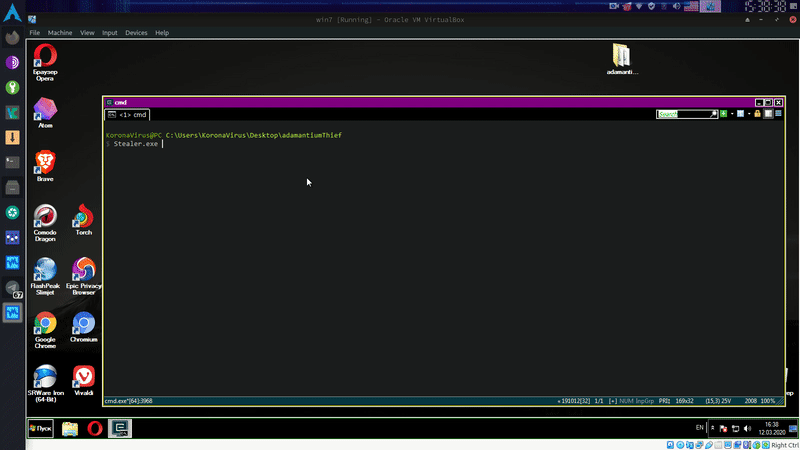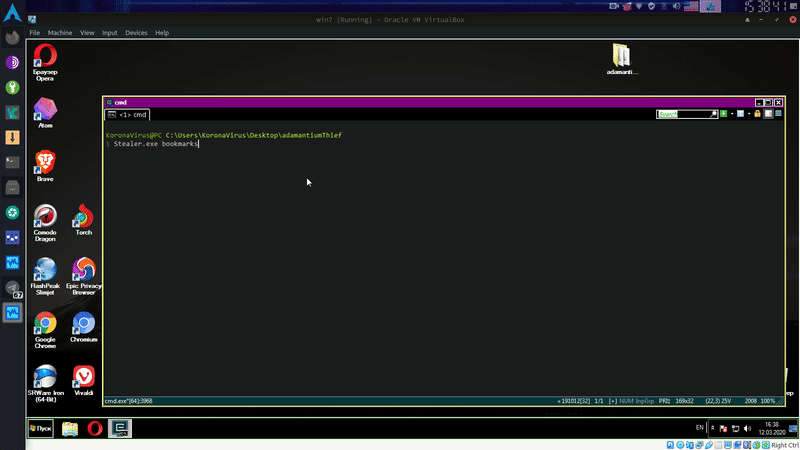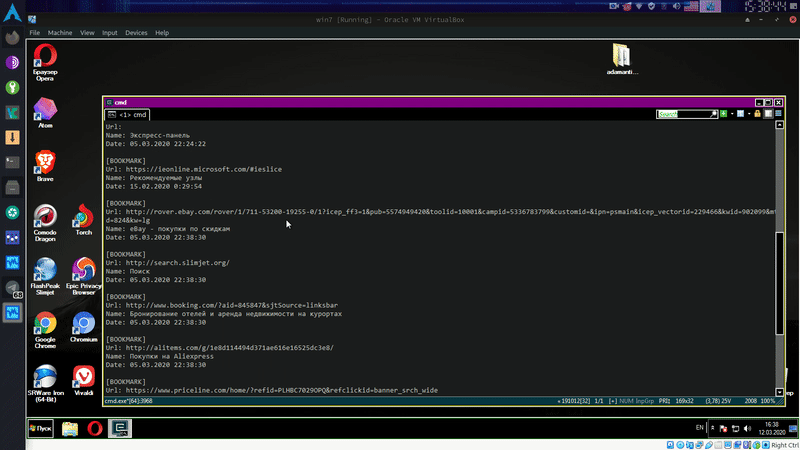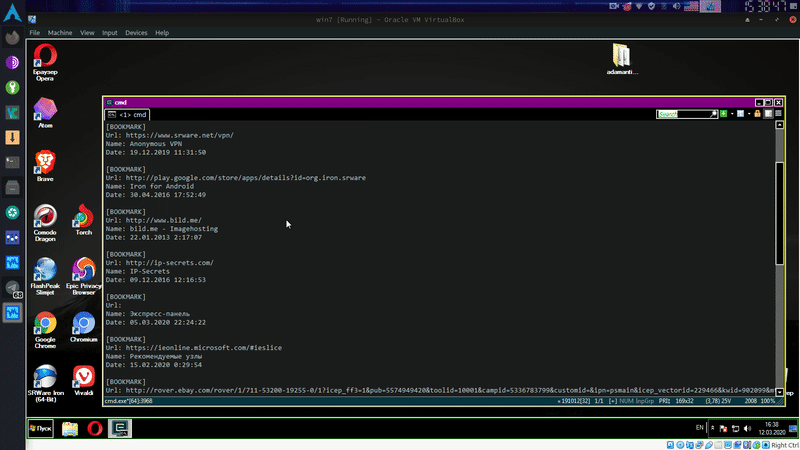
:key: (THIS CODE IS OUTDATED FOR NEW CHROME VERSIONS) Decrypt chromium based browsers passwords, cookies, credit cards, history, bookmarks, autofill.…
data-exfiltrationinformation-gatheringmalware-analysis+1
8201 year ago
subparse preview

subparse

GitHubjstrosch/subparse

Modular malware analysis artifact collection and correlation framework

dynamic-analysis-sandboxingforensicsinformation-gathering+3
562 years ago
WhoamiAlternatives preview

WhoamiAlternatives

GitHubricardojoserf/whoamialternatives

Different methods to get current username without using whoami
information-gatheringmalware-analysispost-exploitation+2
1862 years ago
Keylogger preview

Keylogger

GitHubaydinnyunus/keylogger

Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
data-exfiltrationinformation-gatheringmalware-analysis+5
2.8k2 years ago
ThreatPursuit-VM preview
Archived

ThreatPursuit-VM

GitHubmandiant/threatpursuit-vm

Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
curated-resourcesdigital-forensicseducation+8
1.3k3 years ago
IATelligence preview

IATelligence

GitHubfr0gger/iatelligence

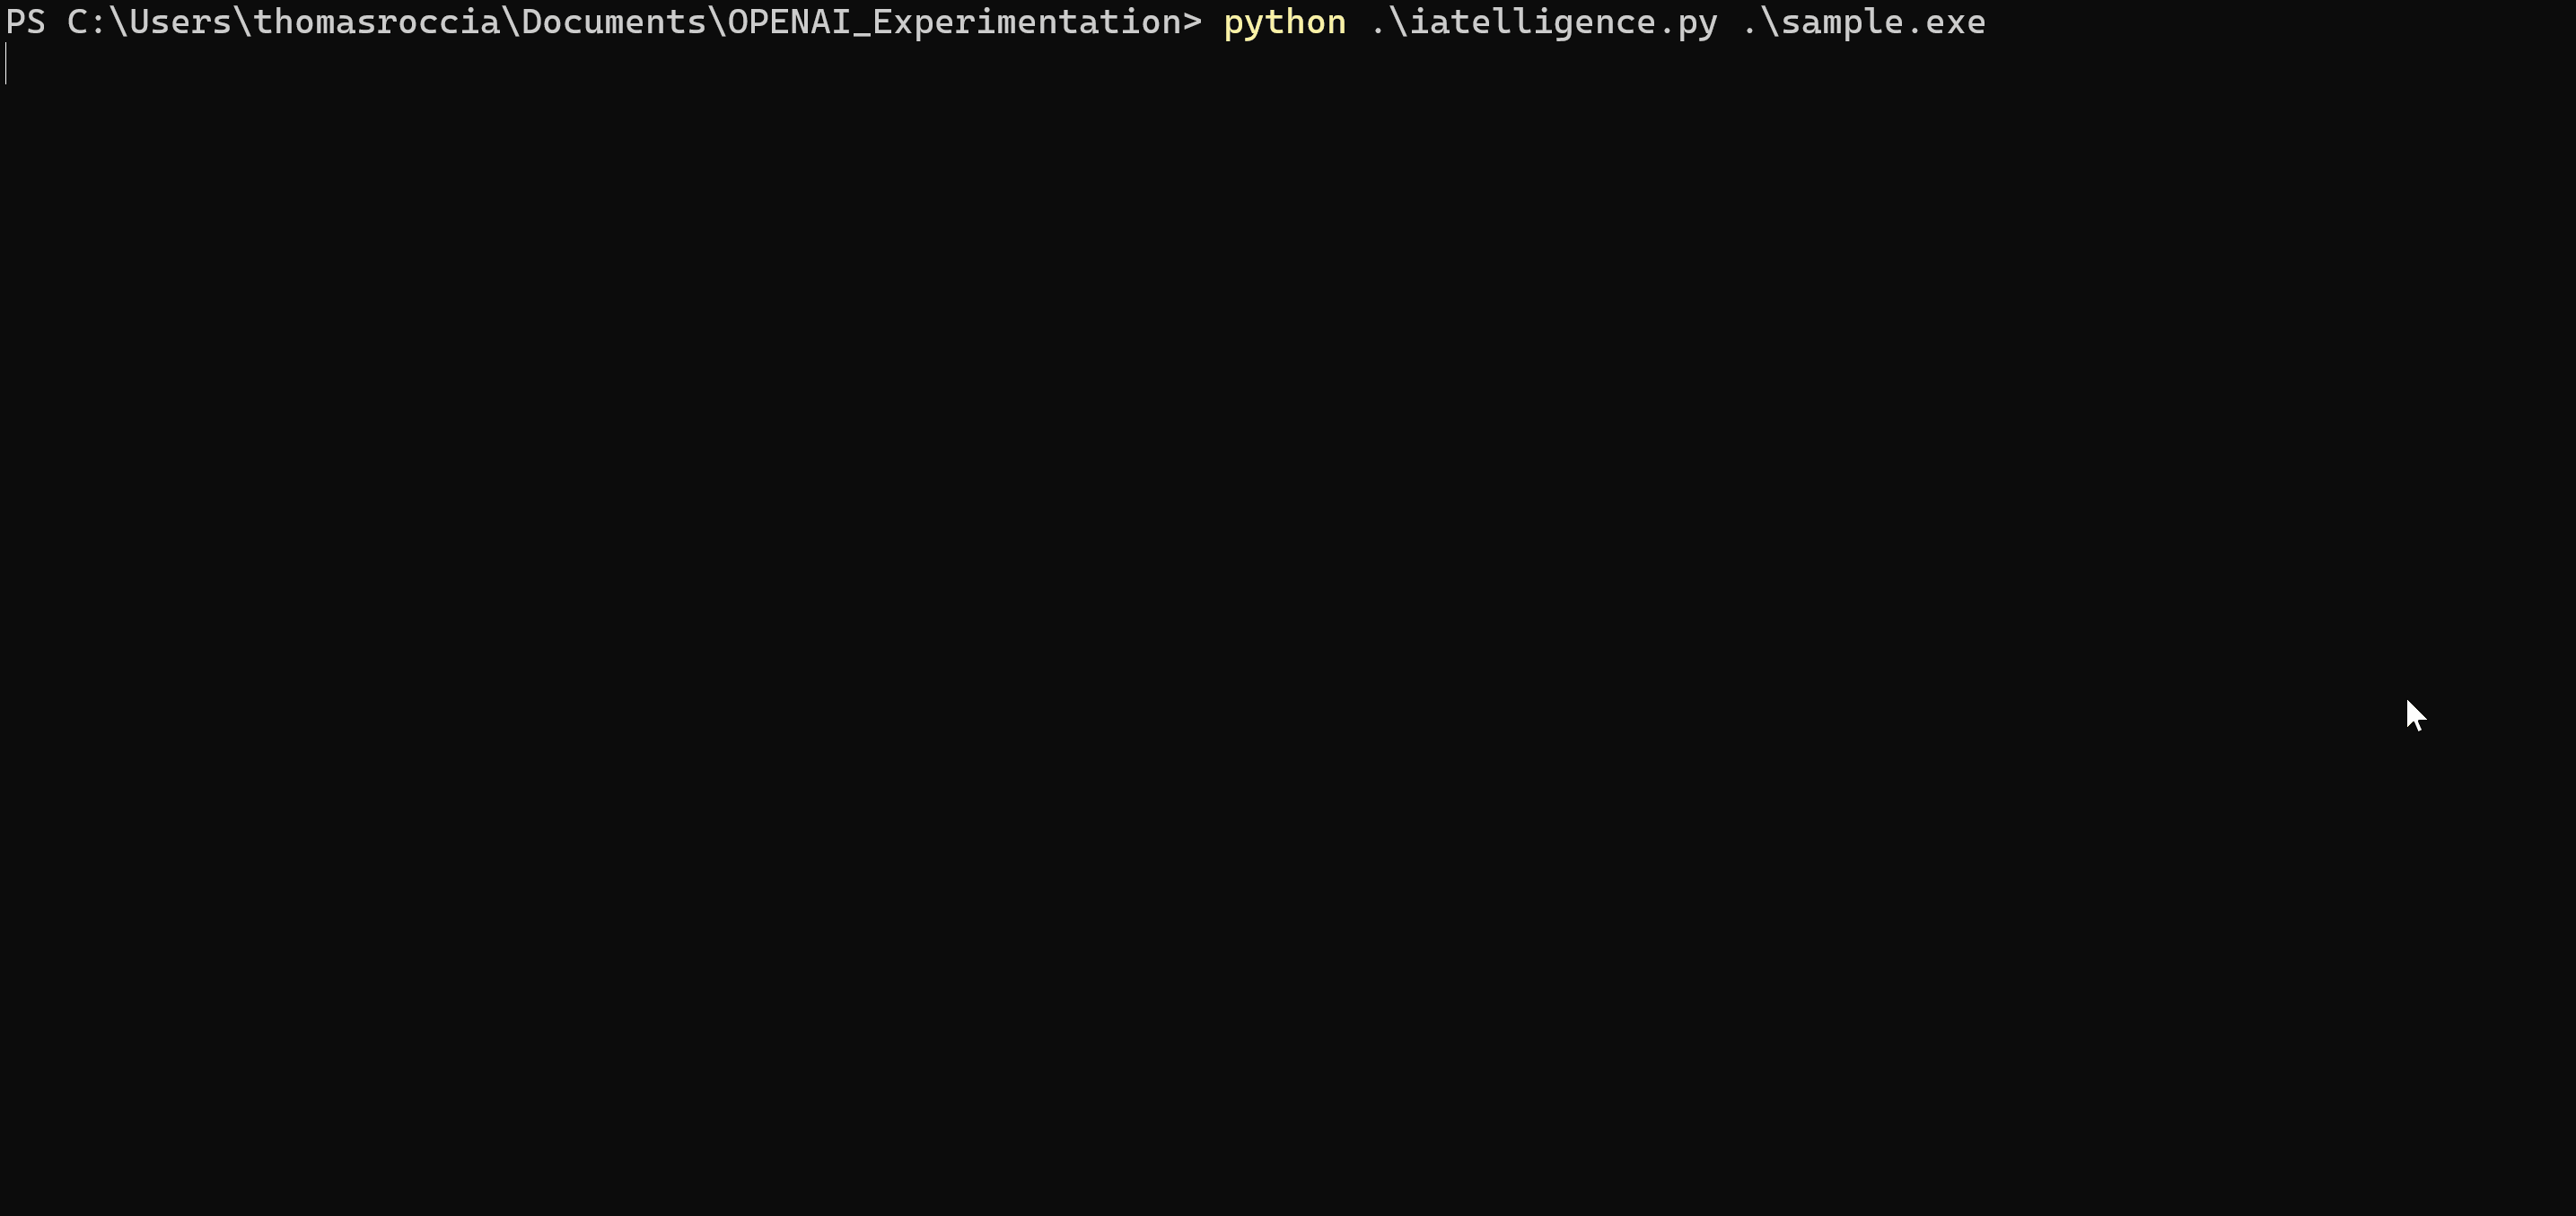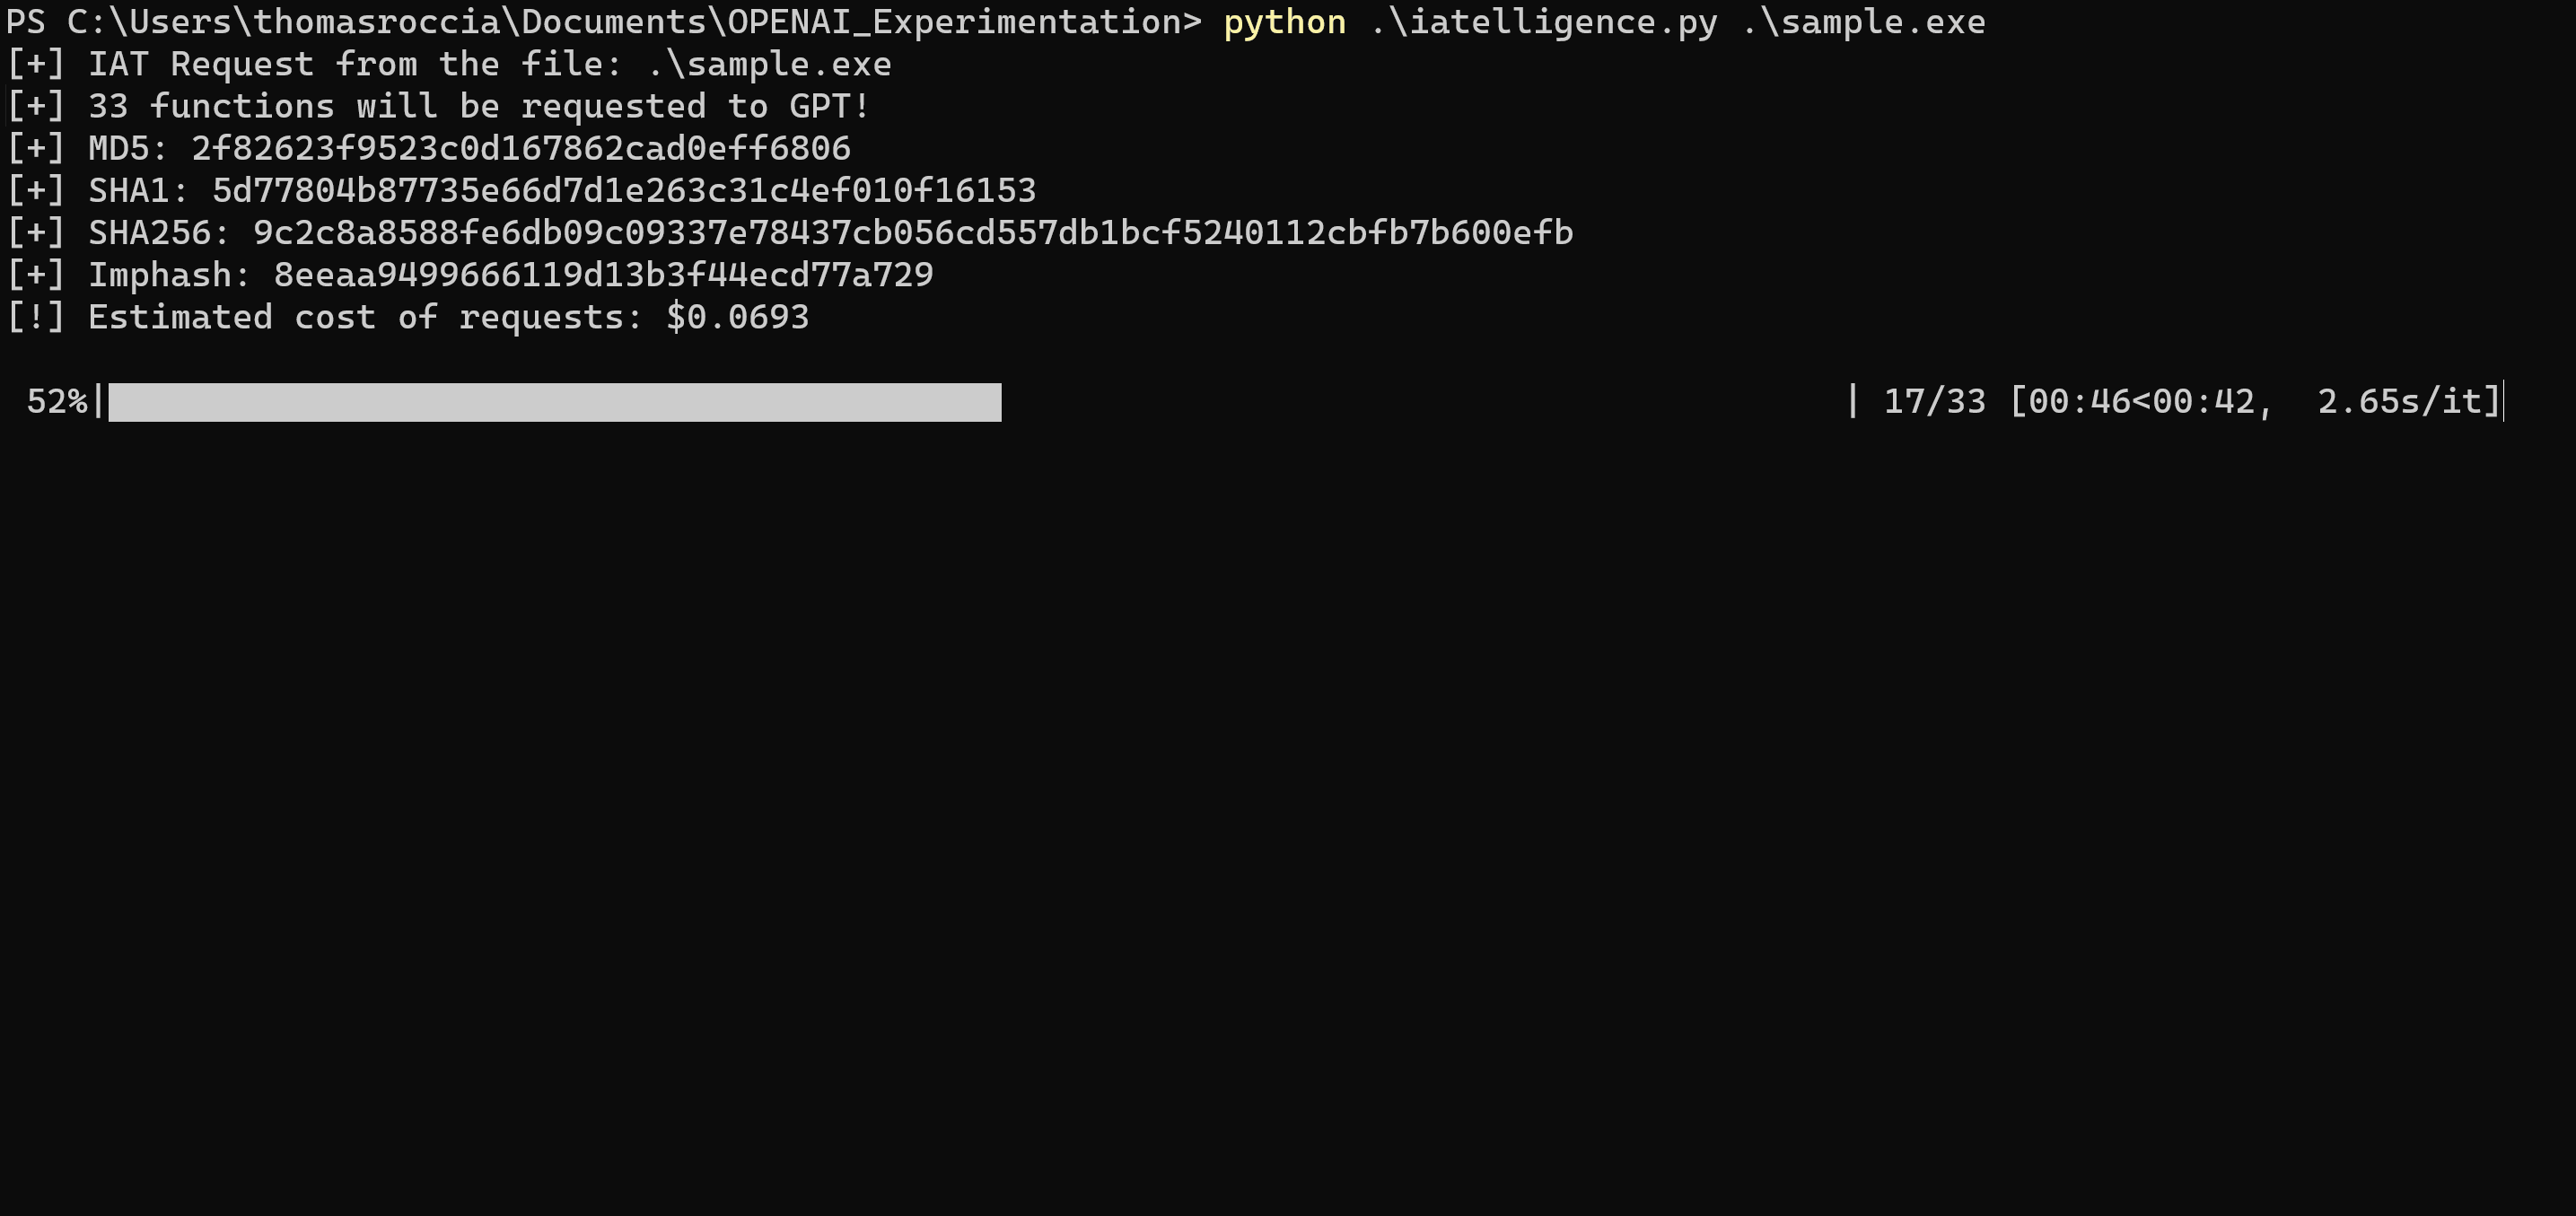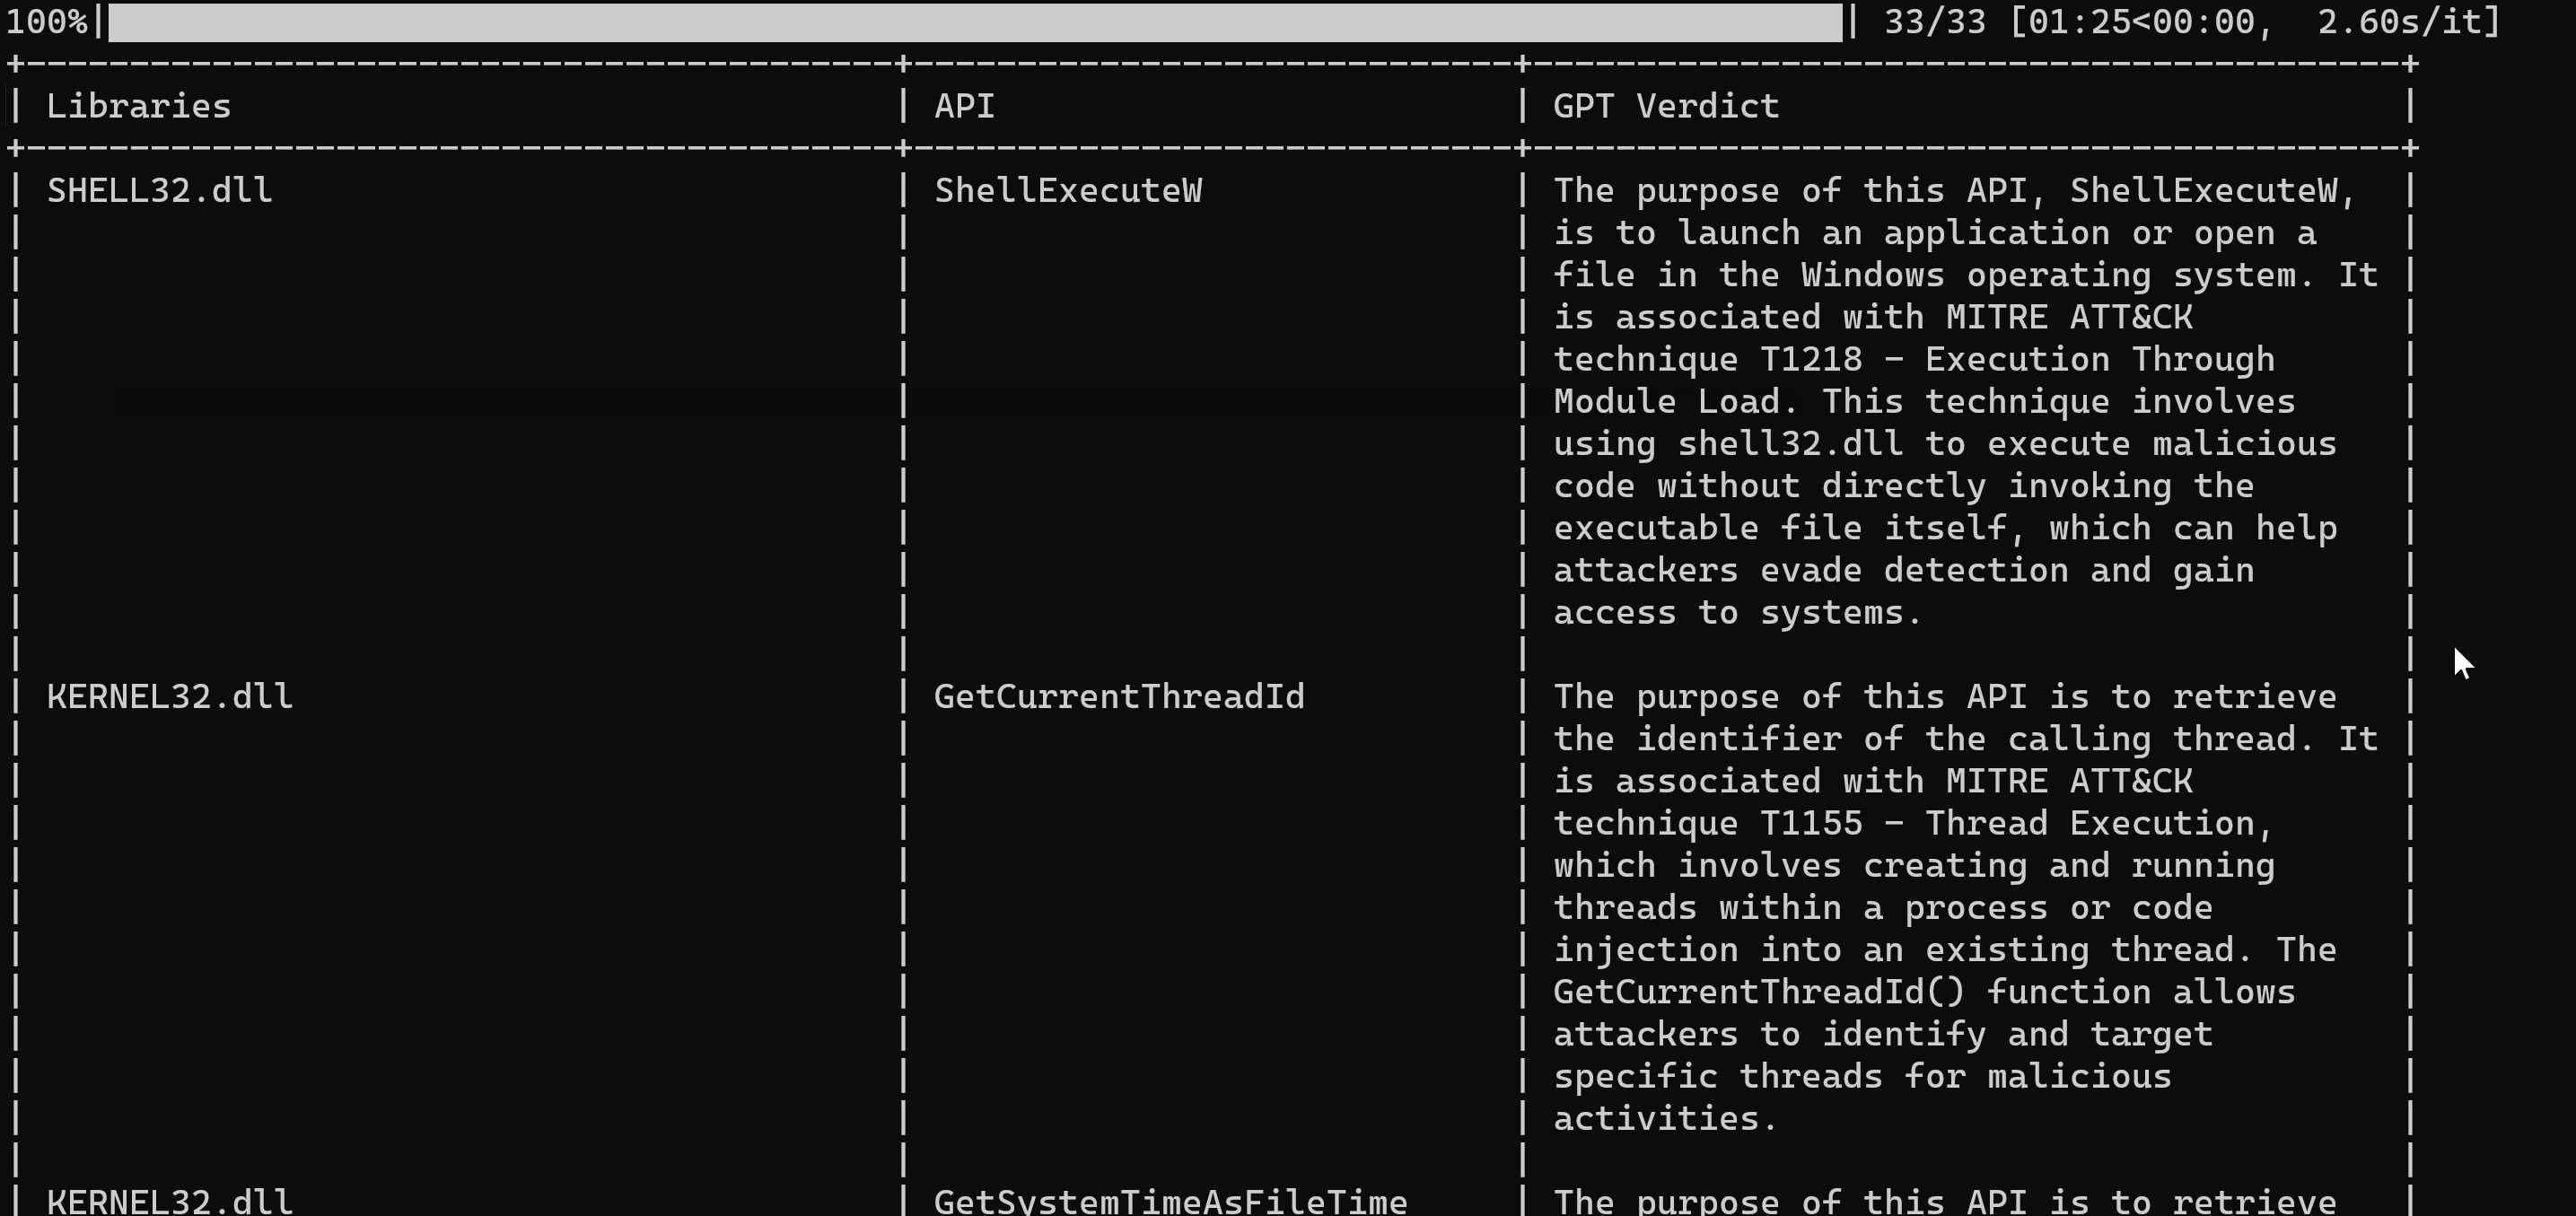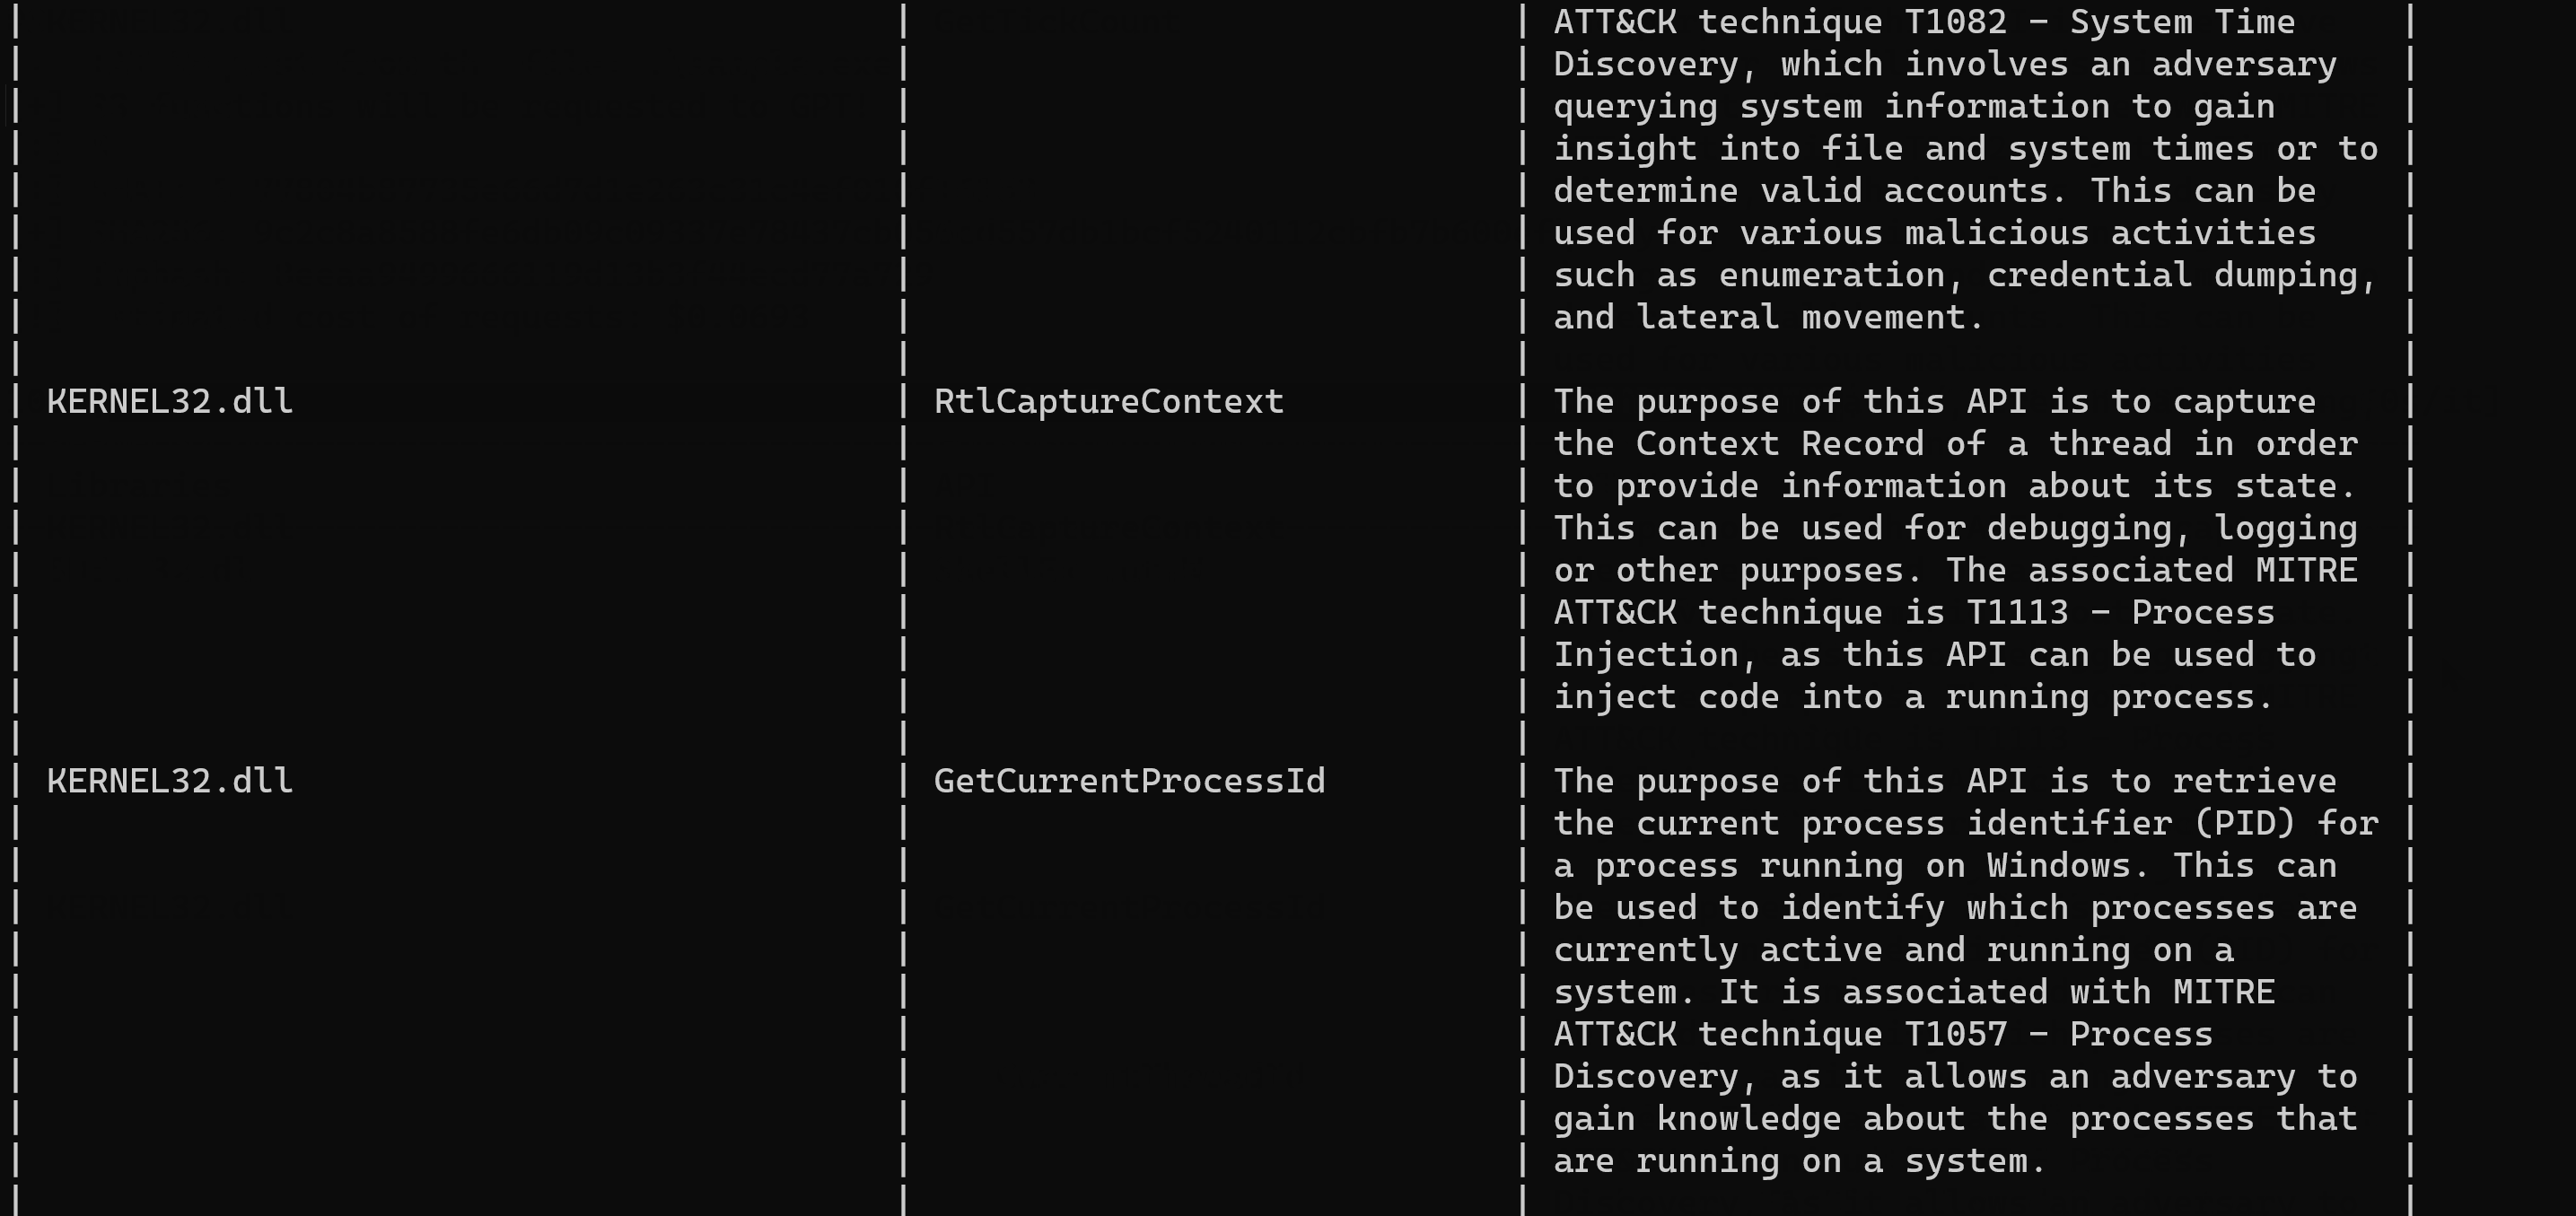
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…

ai-assisted-reversingbinary-analysismalware-analysis+3
3853 years ago
Shelltropy preview

Shelltropy

GitHubkleiton0x00/shelltropy

A technique of hiding malicious shellcode via Shannon encoding.

exploitationmalware-analysispayload-development+1
2693 years ago
POC-of-CVE-2022-36271 preview

POC-of-CVE-2022-36271

GitHubsaumyajeetdas/poc-of-cve-2022-36271

This is working POC of CVE-2022-36271

binary-exploitationexploitationmalware-analysis+3
94 years ago
Get-PDInvokeImports preview

Get-PDInvokeImports

GitHubdump-guy/get-pdinvokeimports

PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
binary-analysismalware-analysisreverse-engineering+1
544 years ago
cuckooautoinstall preview

cuckooautoinstall

GitHubbuguroo/cuckooautoinstall

Auto Installer Script for Cuckoo Sandbox
dynamic-analysis-sandboxingmalware-analysisscripting-automation+1
1648 years ago
Santoku-Linux preview

Santoku-Linux

GitHubsantoku/santoku-linux

Linux Distro for Mobile Security, Malware Analysis, and Forensics

android-securitydigital-forensicseducation+6
20712 years ago
Previous12Next