
Archived
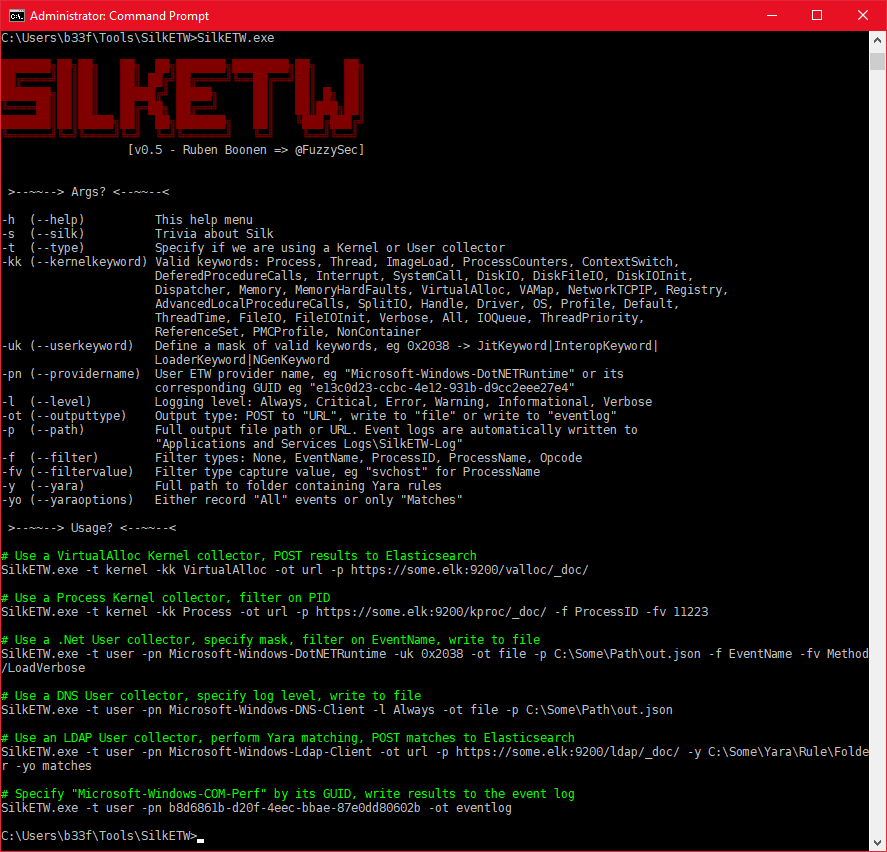
SilkETW
 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
anomaly-detectiondefensive-toolsdigital-forensics+8
 mindcrypt/stegowiper
A powerful and flexible tool to apply active attacks for disrupting stegomalware