

kunglao-agent
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
ai-assisted-reversingandroid-securitybinary-analysis+8
51
amd2g2zz/kunglao-agentThe reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
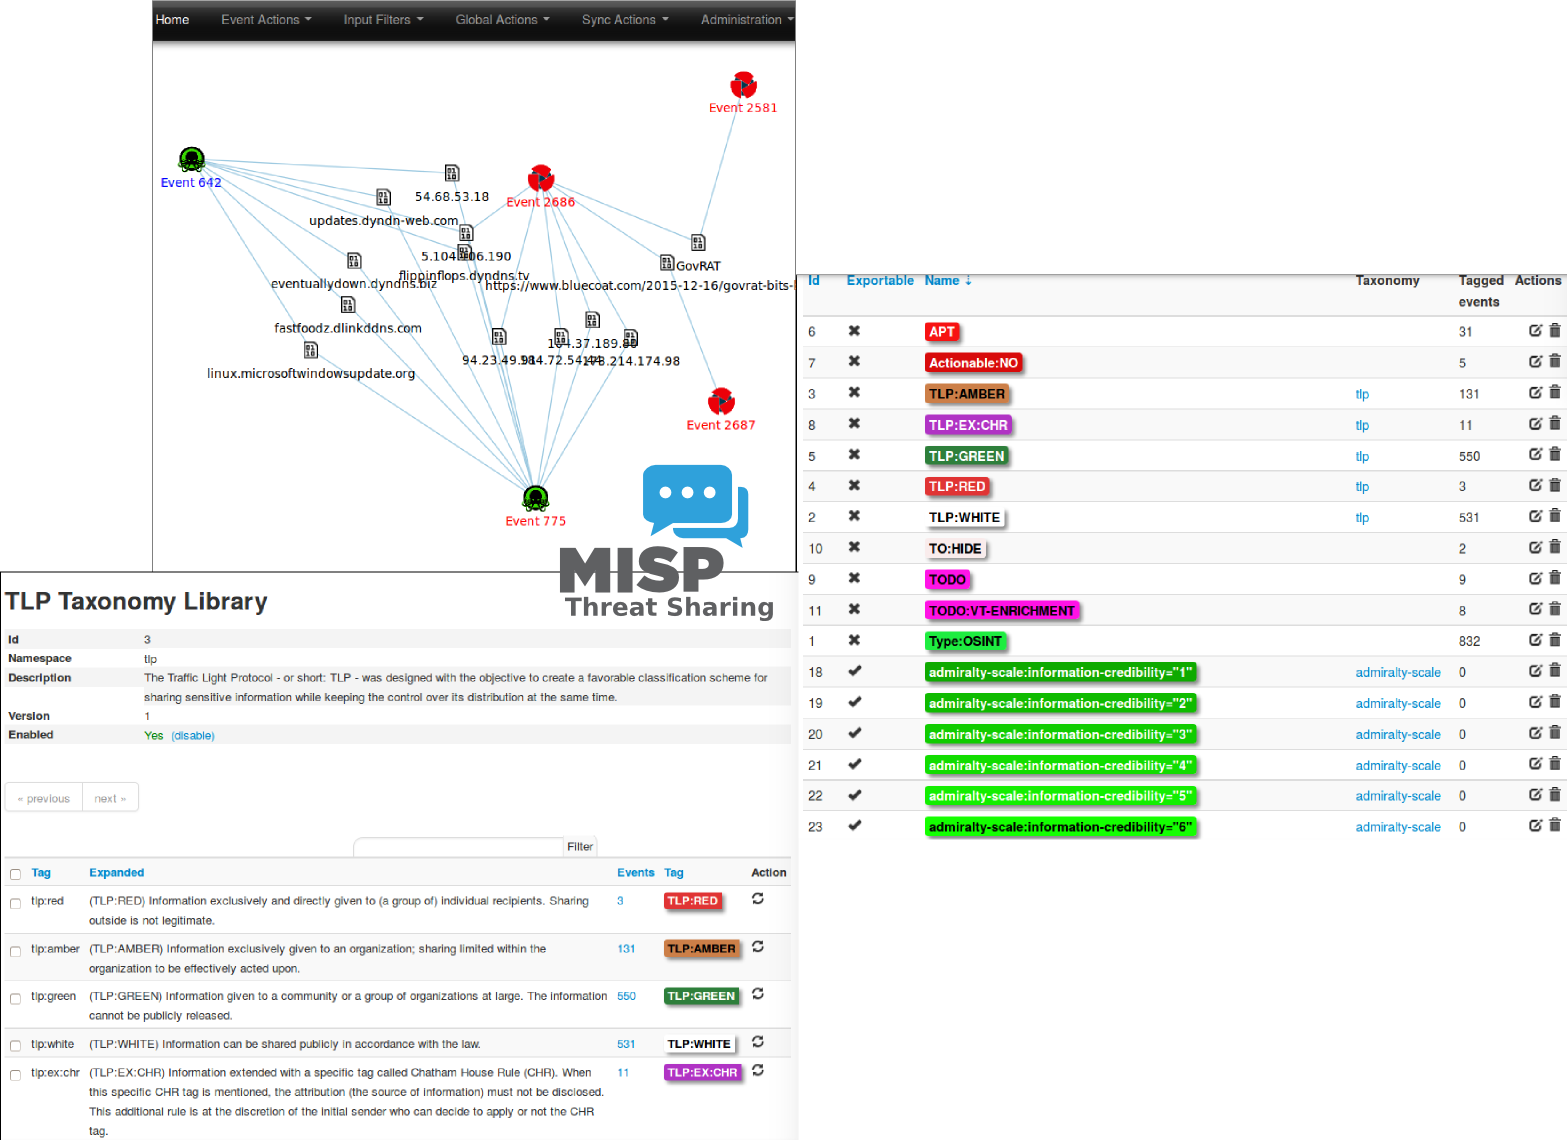 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
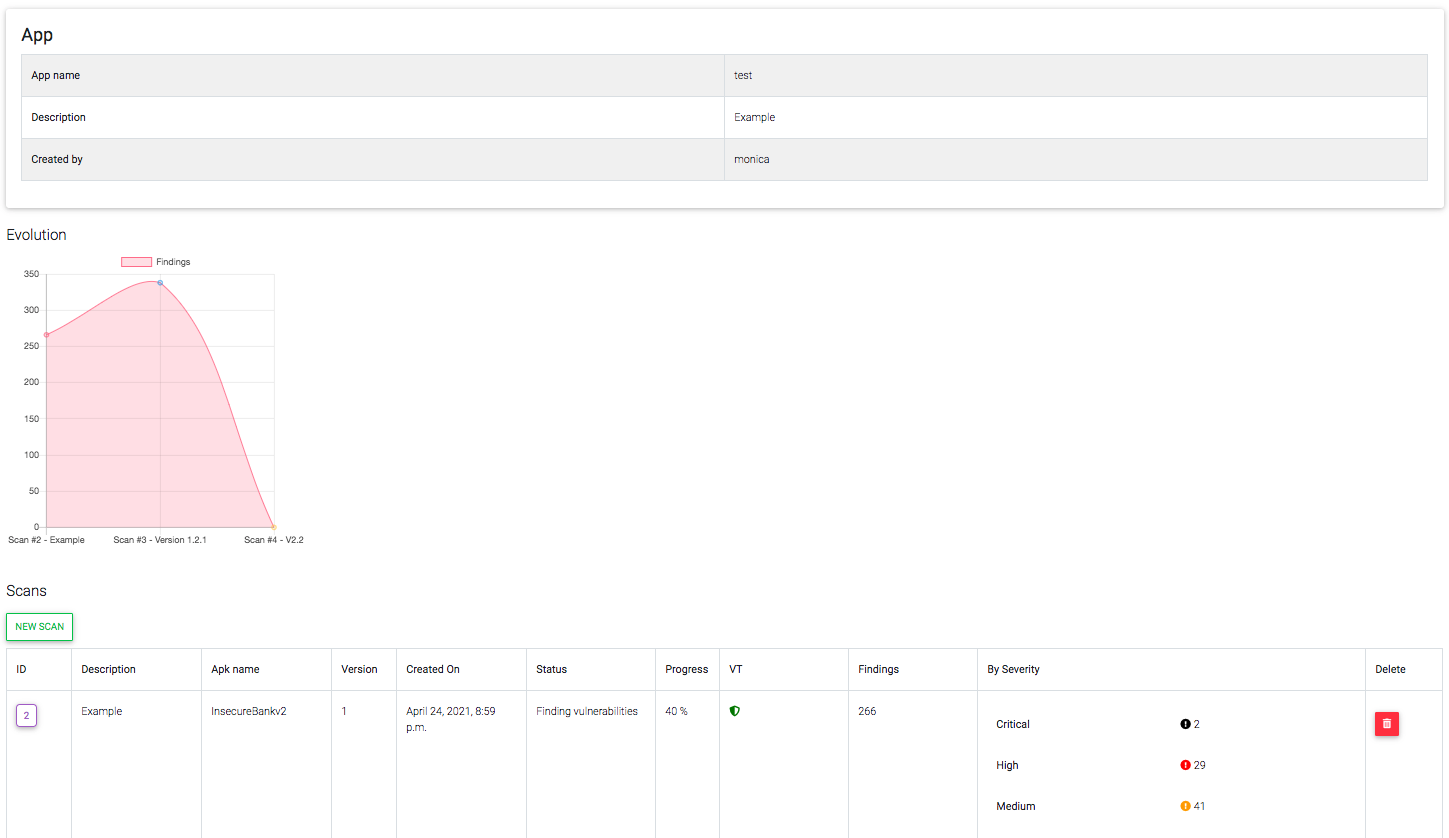 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
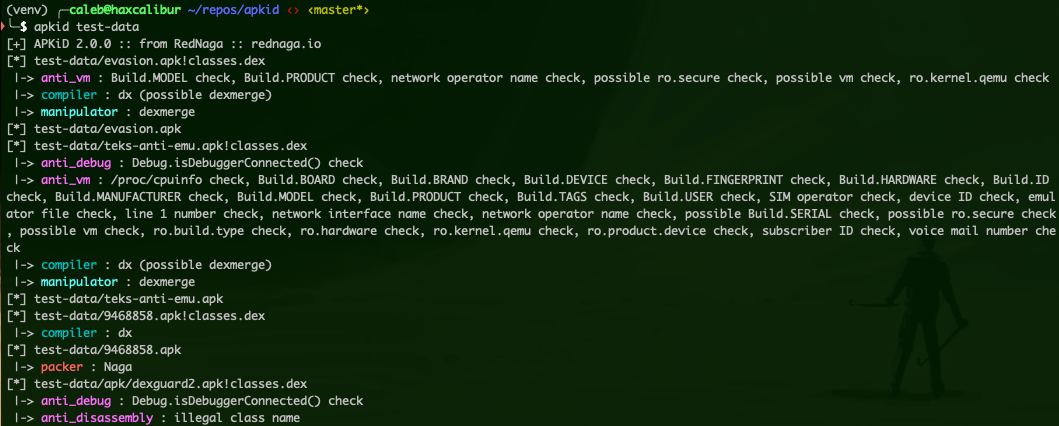 rednaga/apkid
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
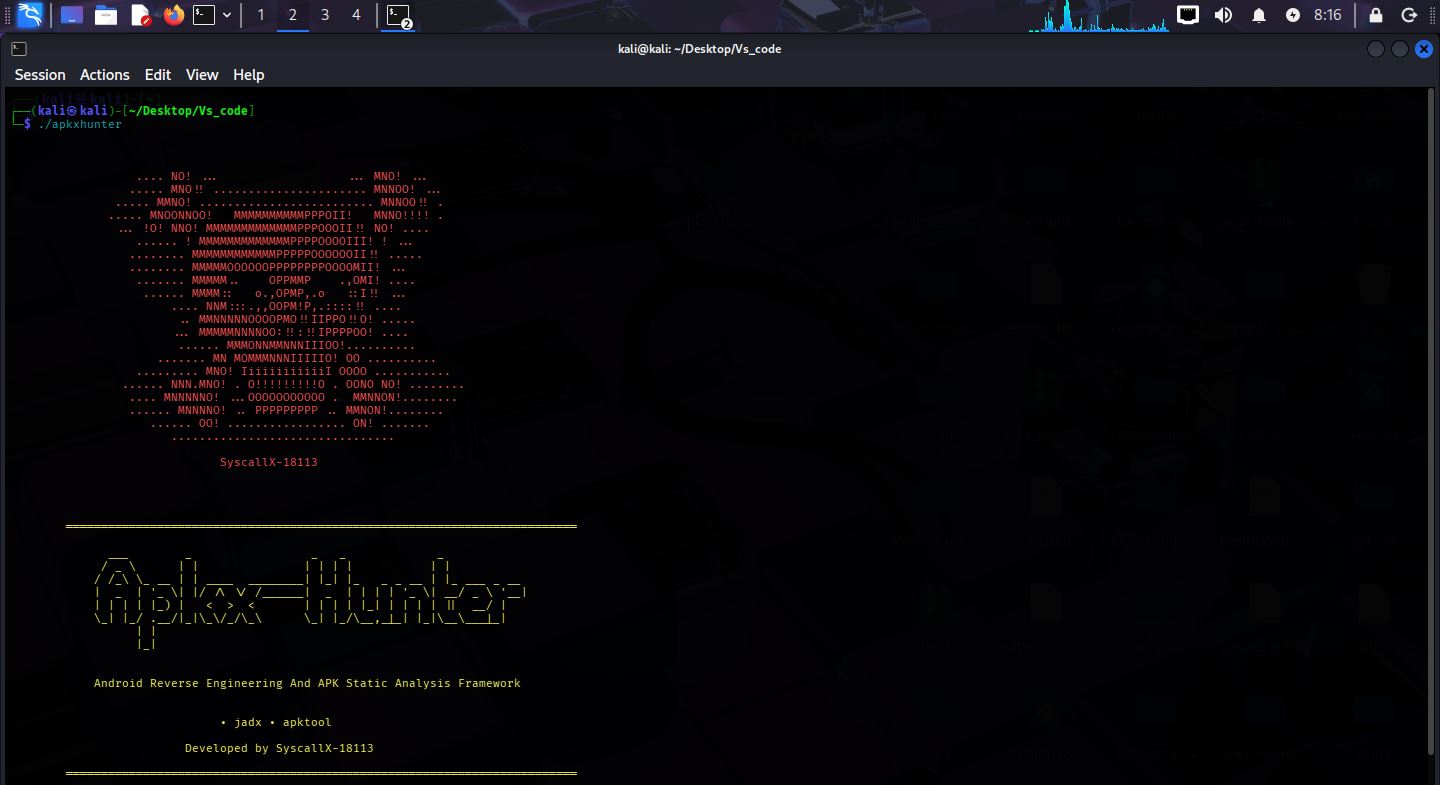 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…