Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent

Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…

Real-time Windows clipboard hijack detector that monitors clipboard changes, restores replaced BTC, ETH, SOL, and USDT addresses, and alerts users to…

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…

Batch-mode checker for Shadowhammer malware indicators, scanning local or provided MAC addresses against known malicious hashes, with offline support…

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…

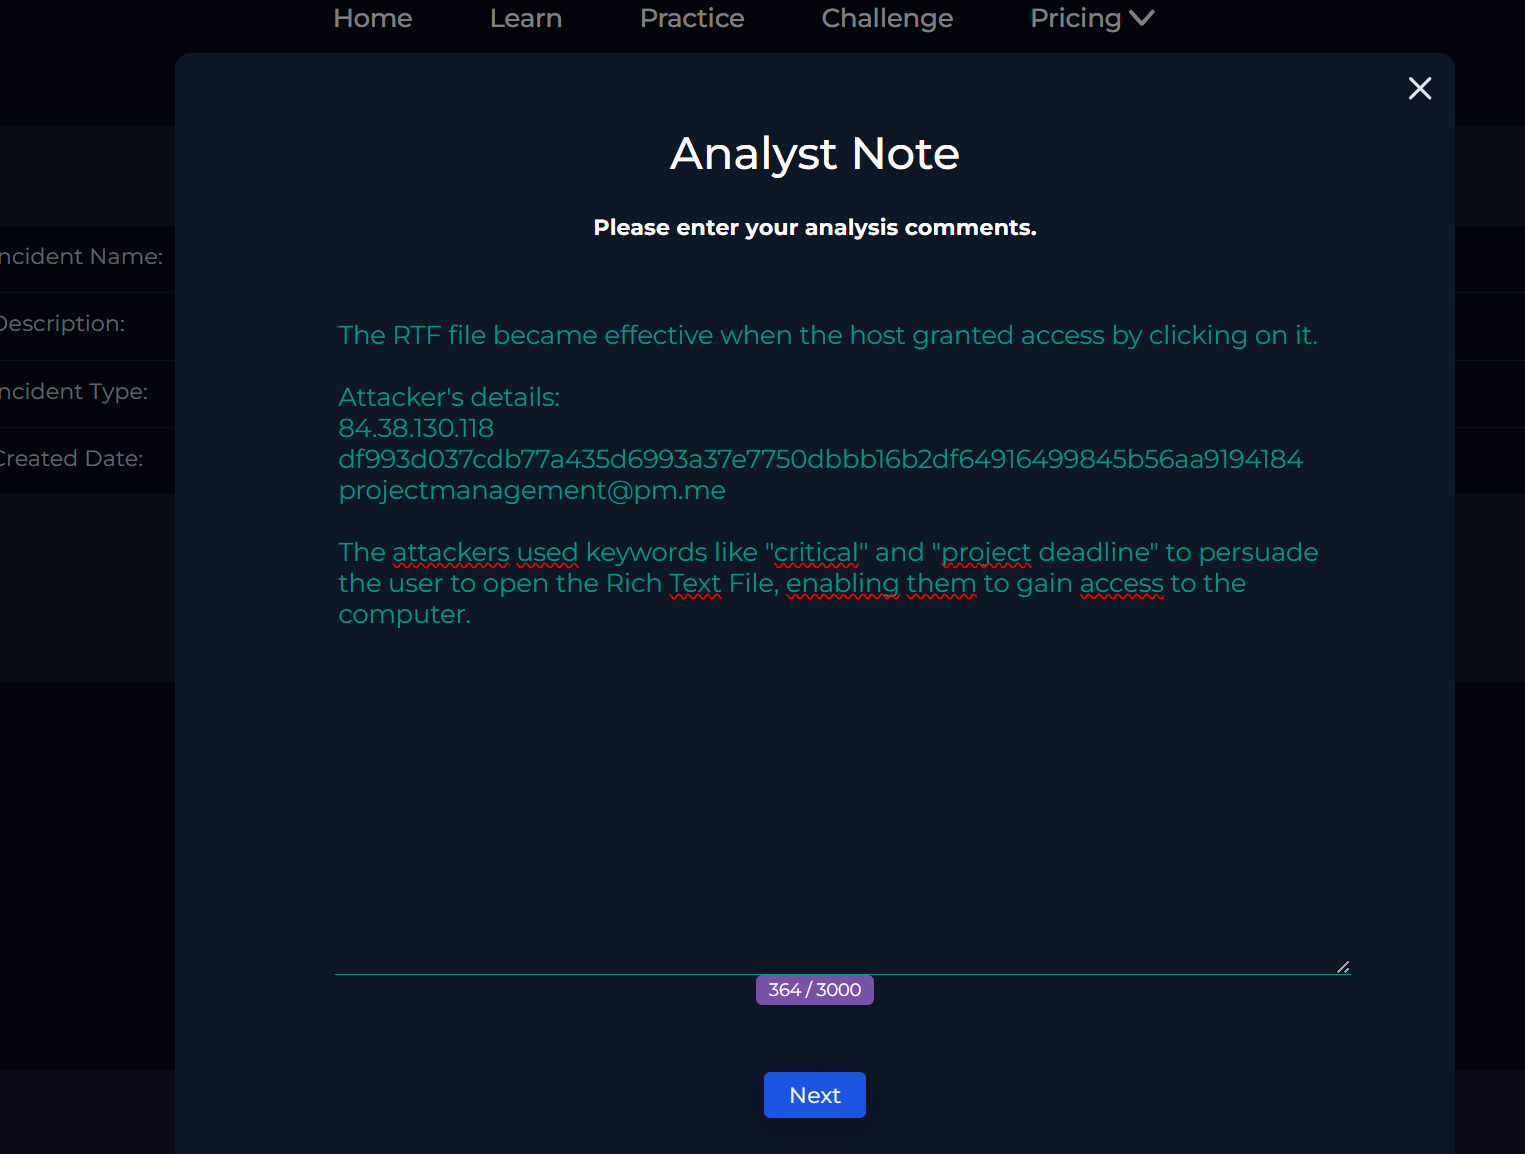
We are expected to investigate a critical alert reporting a Windows OLE zero-click RCE exploitation (CVE-2025-21298) delivered via a malicious RTF…

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…

Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.

A repository to share publicly available Velociraptor detection content

A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…