

 google/bindiff
Quickly find differences and similarities in disassembled code
 google/magika
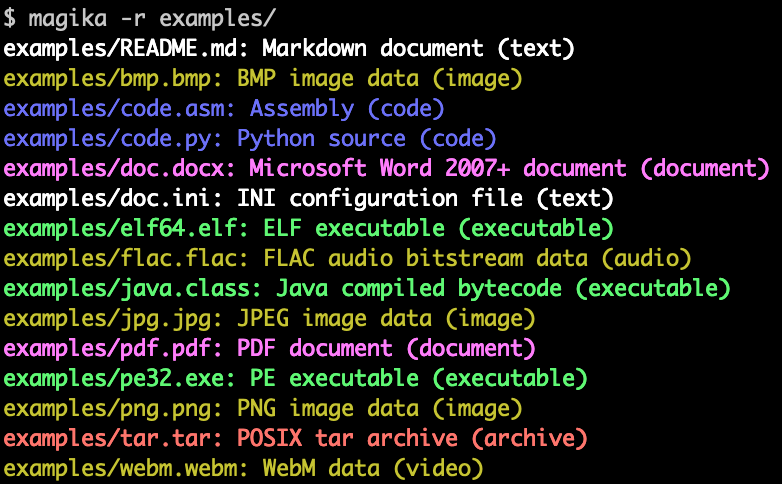
Fast and accurate AI powered file content types detection
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
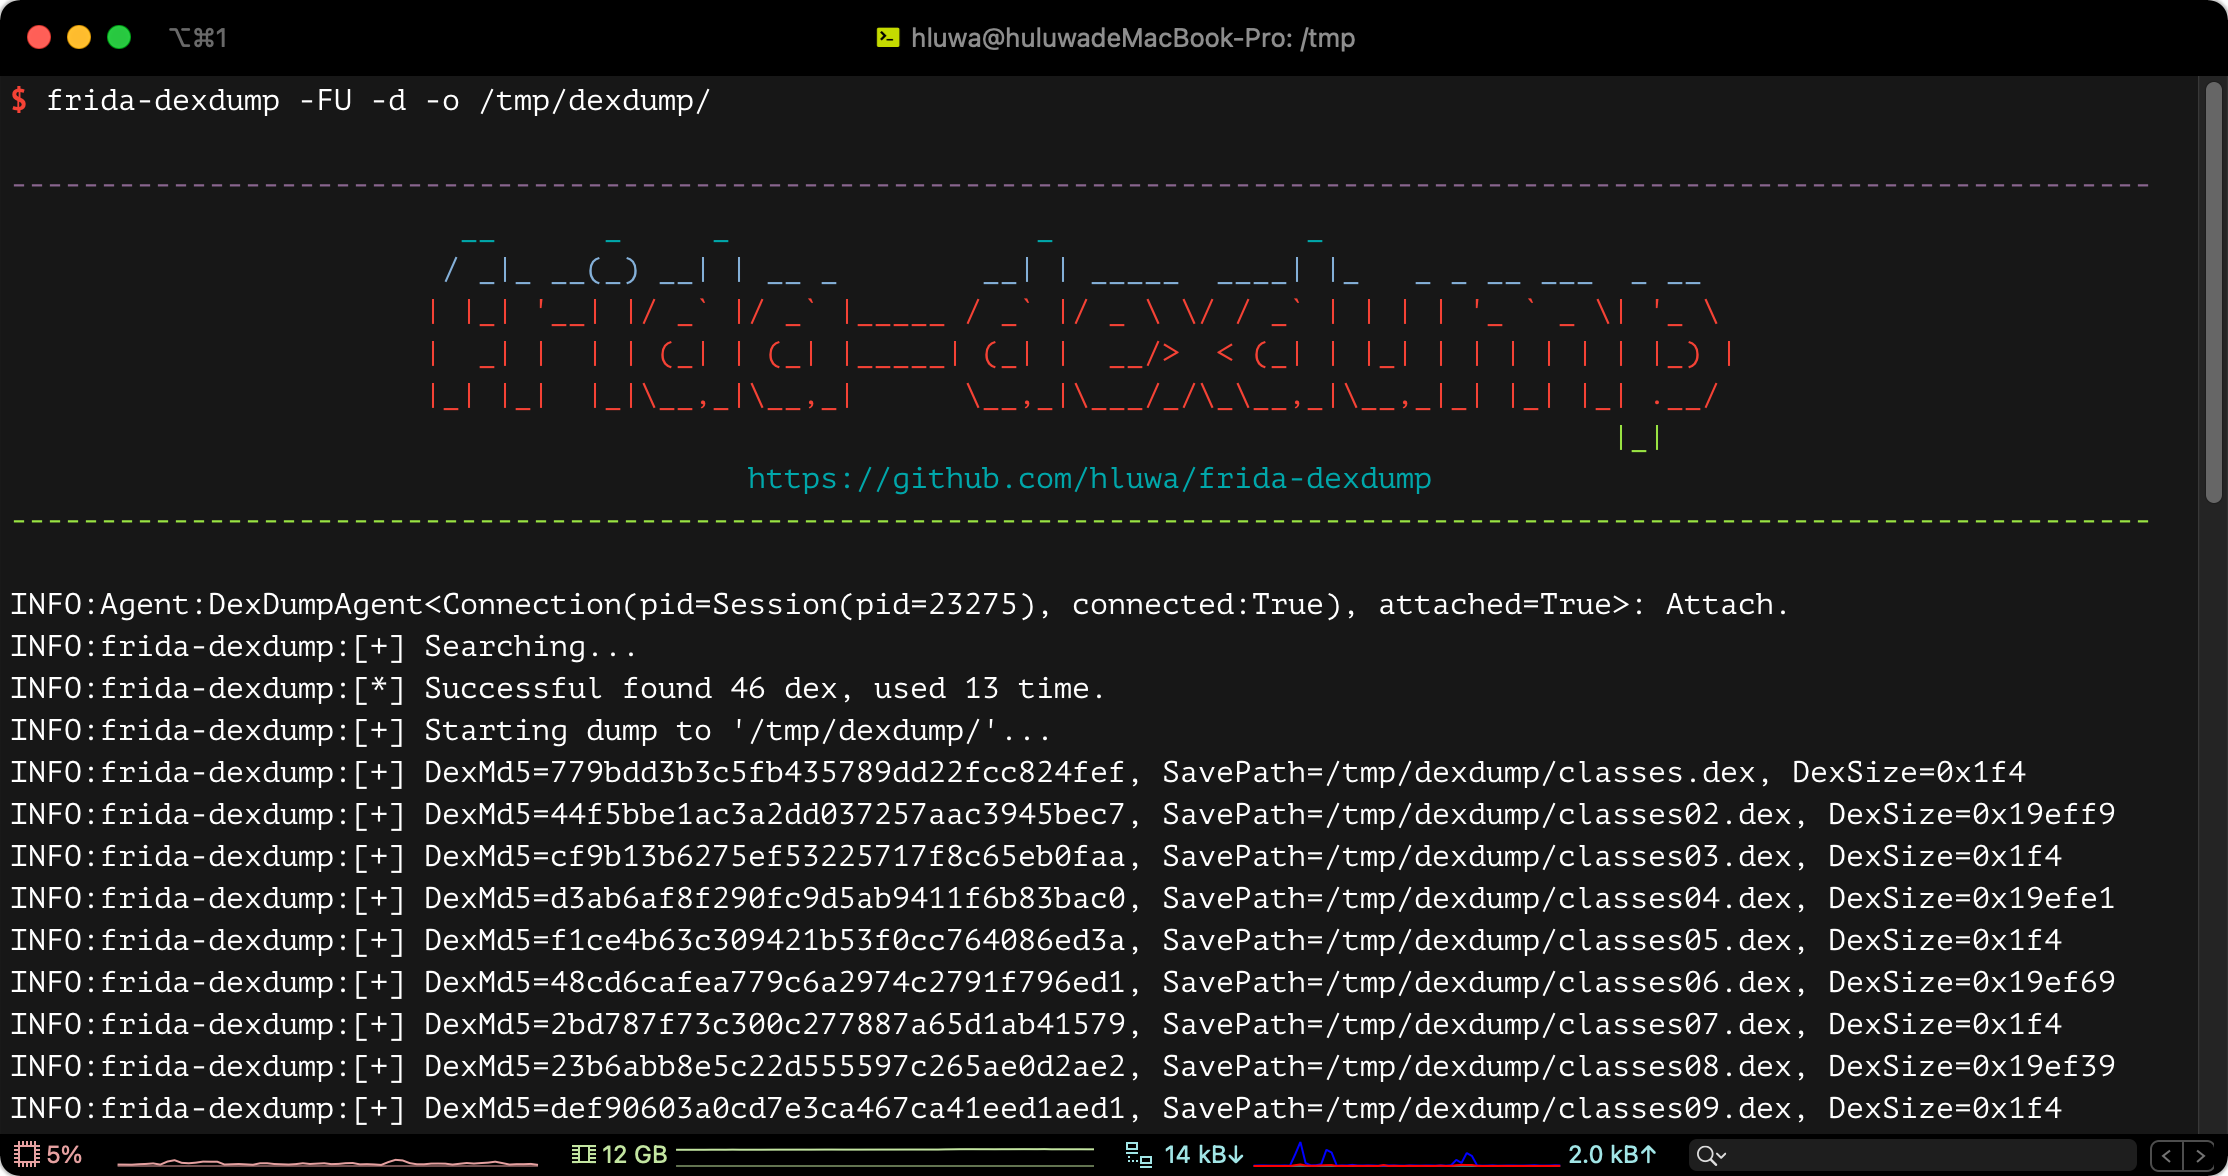 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data